题:抄错的字符
题目作者: Aman
题目描述:老师让小明抄写一段话,结果粗心的小明把部分数字抄成了字母,还因为强迫症把所有字母都换成大写。你能帮小明恢复并解开答案吗:QWIHBLGZZXJSXZNVBZW
分析:
- 数字和字符可能的转换:l-1, s-5, b-6, z-2, B-8, G-9
1 : l(小写L)、I(大写i)
2 : Z/z
5 : S/s
8 : B
9 : g
0 : O/o
尝试还原字符串,进行base64解码
python
from base64 import b64decode
from string import printable

# 字母数字对应表
Numlist = {'i': '1', 'l': '1', 'z': '2', 's': '5', 'g': '9', 'o': '0'}


# 分割字符串
def cut(obj, sec):
    return [obj[i:i + sec] for i in range(0, len(obj), sec)]


# 使用递归将字符串还原回所有可能的结果
def decode(str):
    res = []
    if len(str) > 1:
        relist = decode(str[1:])
        Rlist = decode(str[0])
        for i in Rlist:
            for j in relist:
                res.append(i + j)
    else:
        res.append(str[0].lower())
        res.append(str[0].upper())
        if str[0].lower() in Numlist:
            res.append(Numlist[str[0].lower()])
    return res


# 判断base解码后是否是正常的字符
def isbase(str):
    res = b64decode(str)
    for i in res:
        if i not in printable.encode():
            return False
    return True


if __name__ == '__main__':
    enstr = 'QWIHBLGZZXJSXZNVBZW'
    # base64可以切片分别解码,减少运算数量
    enlist = cut(enstr, 4)
    flag = []
    for i in enlist:
        delist = decode(i)
        f = []
        for base in delist:
            base += '=' * (4 - len(base))  # 填充=
            if isbase(base):
                # print(base, end=',')
                f.append(b64decode(base).decode())
        flag.append(f)
        print(f)
所以结合作者的名字,flag{Aman_very_cool}
题:/.-
题目描述: ...-./.-.../.-/--./----.--/-.../...--/...-./-.-./-.../...-./.----/--.../...-./----./...--/----./----./.../-----/...-/-----.-
分析:
点横推测是摩斯密码
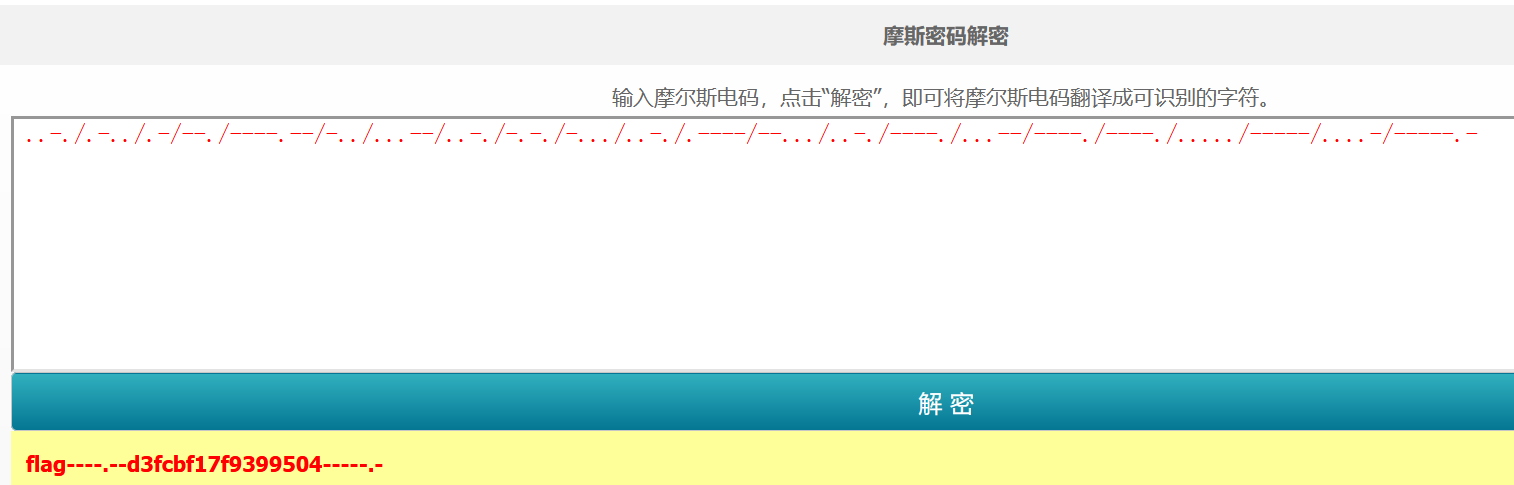 得到flag{d3fcbf17f9399504}
题:聪明的小羊
题目描述:一只小羊翻过了2个栅栏 fa{fe13f590lg6d46d0d0}
分析:
根据提示为栅栏密码

代码为:
python
import sys
def fence_Passwd_burst(secret):
    res = [step for step in range(2, len(secret)) if len(secret)%step == 0]
    for step in res:
        flag = ''#获取解密结果,以step栏进行遍历获取解密后的flag
        for i in range(step):flag += secret[i::step]
        print('第%s栏: 解密结果:%s' %(str(step), flag))
if(__name__ == '__main__'):
    secret ="fa{fe13f590lg6d46d0d0}"
    fence_Passwd_burst(secret)
得到flag{6fde4163df05d900}
题:ok
描述: Ook.
附件里面全是该字符:
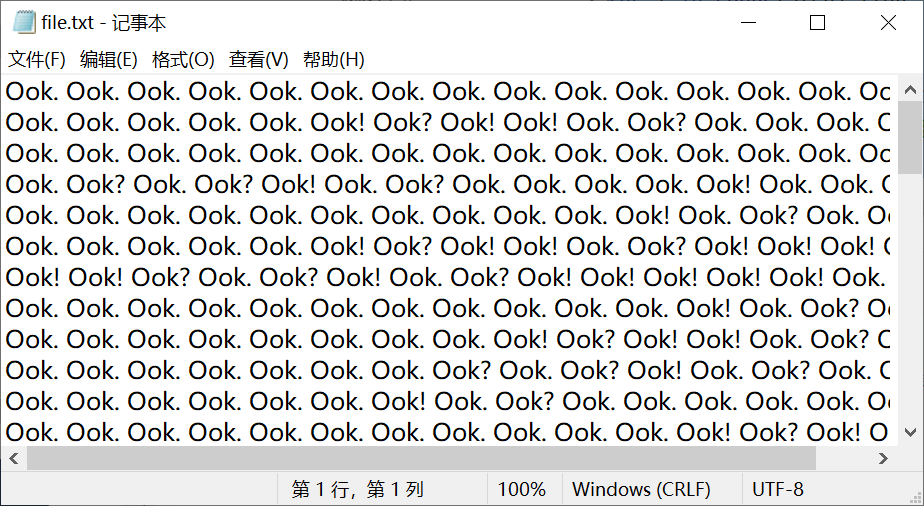
使用在线工具解密:https://www.splitbrain.org/services/ook

题:±\<\>
题目描述: +++++ +++++ -\>++ +++++ +++\< >++.+ +++++ .<+++ -\>-- -\<>- -.+++ +++.< ++++ -\>+++ +\<>+ +++.< +++++ +++- \>---- ----\< >--- ----- ---.< +++++ ++-\> +++++ ++\<> +++.< +++++ +-\>- ----- \<>-- ----- -.--. ----. --.++ +++++ +.<++ ++++ -\>+++ +++\< >++++ +.++. <++++ ++-\> ----- -\<>- ----- ----. -.<++ +++++ -\>++ +++++ \<>+. ----. ++++. <++++ +++- \>---- ---\< >---- .+.<+ +++++ ++-\> +++++ +++\< >++++ +++++ ++.<
使用在线工具解密:https://ctf.bugku.com/tool/brainfuck
