Summary
- CVE-2024-47176 | cups-browsed <= 2.0.1 binds on UDP INADDR_ANY:631 trusting any packet from any source to trigger a IPP request to an attacker controlled URL.
Get-Printer-Attributes - CVE-2024-47076 | libcupsfilters <= 2.1b1 does not validate or sanitize the IPP attributes returned from an IPP server, providing attacker controlled data to the rest of the CUPS system.
cfGetPrinterAttributes5 - CVE-2024-47175 | libppd <= 2.1b1 does not validate or sanitize the IPP attributes when writing them to a temporary PPD file, allowing the injection of attacker controlled data in the resulting PPD.
ppdCreatePPDFromIPP2 - CVE-2024-47177 | cups-filters <= 2.0.1 allows arbitrary command execution via the PPD parameter.
foomatic-rip``FoomaticRIPCommandLine
(can you already see where this is going? :D)
Plus a couple of other bugs that will be mentioned and that are arguably security issues but have been pretty much ignored during the conversation with the developers and the CERT. They are still there, along with several other bugs that are more or less exploitable.
Impact
A remote unauthenticated attacker can silently replace existing printers' (or install new ones) IPP urls with a malicious one, resulting in arbitrary command execution (on the computer) when a print job is started (from that computer).
Entry Points
- WAN / public internet : a remote attacker sends an UDP packet to port 631. No authentication whatsoever.
- LAN: a local attacker can spoof zeroconf / mDNS / DNS-SD advertisements (we will talk more about this in the next writeup ) and achieve the same code path leading to RCE.
总结
- CVE-2024-47176 漏洞 |cups-browsed <= 2.0.1 在 UDP INADDR_ANY:631 上绑定,信任来自任何来源的任何数据包,以触发对攻击者控制的 URL 的 IPP 请求。
Get-Printer-Attributes - CVE-2024-47076 漏洞 |libcups过滤器 <= 2.1b1 不会验证或清理从 IPP 服务器返回的 IPP 属性,从而向 CUPS 系统的其余部分提供攻击者控制的数据。
cfGetPrinterAttributes5 - CVE-2024-47175 漏洞 |libppd <= 2.1b1 在将 IPP 属性写入临时 PPD 文件时不验证或清理 IPP 属性,从而允许在生成的 PPD 中注入攻击者控制的数据。
ppdCreatePPDFromIPP2 - CVE-2024-47177 漏洞 |cups-filters <= 2.0.1 允许通过 PPD 参数执行任意命令。
foomatic-rip``FoomaticRIPCommandLine
此外,还有一些其他错误,这些错误可以说是安全问题,但在与开发人员和 CERT 的对话中几乎被忽略了。它们仍然存在,还有其他几个或多或少可利用的 bug。
冲击
未经身份验证的远程攻击者可以静默地将现有打印机(或安装新打印机)的 IPP URL 替换为恶意 IPP URL,从而导致在启动打印作业(从该计算机)时(在计算机上)执行任意命令。
入场点
- WAN/公共互联网 :远程攻击者向端口 631 发送 UDP 数据包。无需任何身份验证。
- LAN:本地攻击者可以欺骗 zeroconf / mDNS / DNS-SD 广告(我们将在下一篇文章 中详细讨论这一点)并实现导致 RCE 的相同代码路径。
本地复现
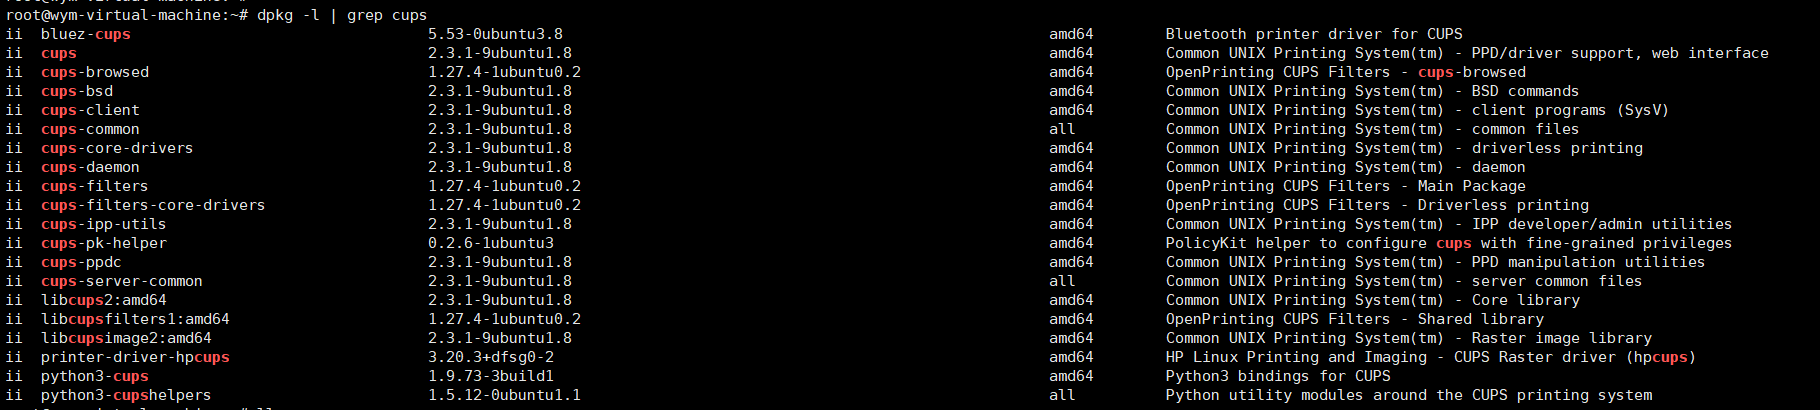
打开自己的ubuntu虚拟机,看到是有cups(通用Unix打印系统)的
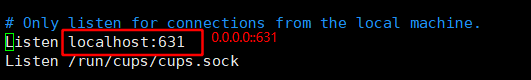
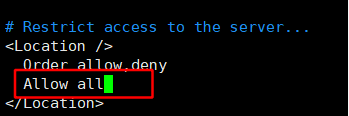
配置cups的配置文件/etc/cups/cupsd.conf使其可以访问
关闭防火墙
systemctl stop ufw
systemctl status ufw
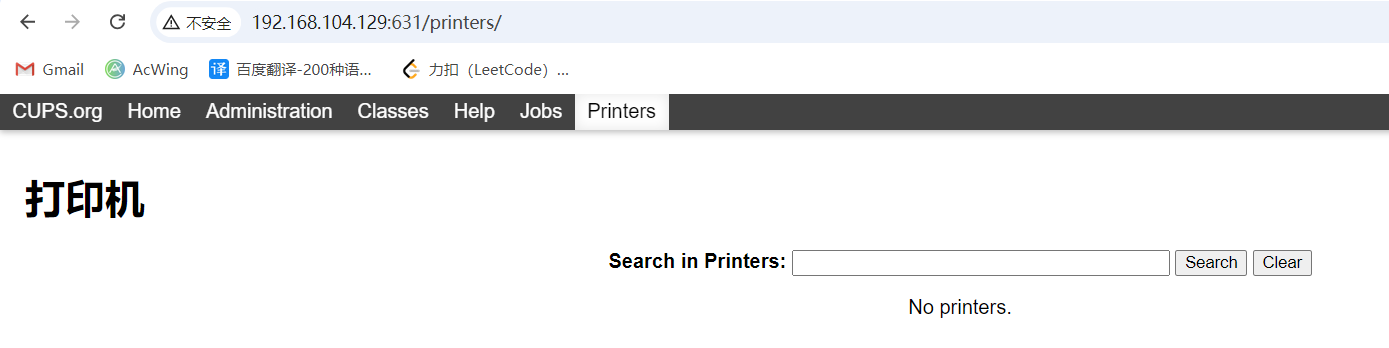
此时的打印机服务是可以使用网页访问的
查看侦听的tcp和udp端口,可以看到确实有631的udp端口在侦听
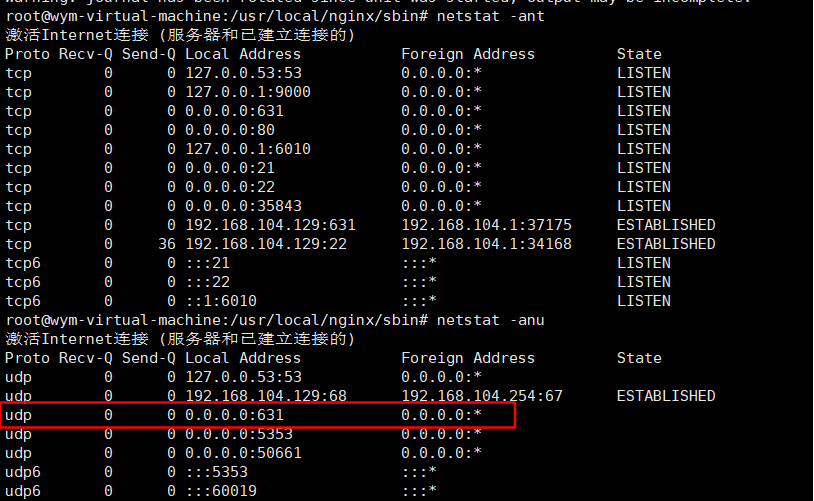
该udp监听端口是此进程以 root 身份运行的
ps aux | grep "cups-brow"
cups-browsed ,它的作用主要是发现新打印机并自动将它们添加到系统中
使用poc.py文件向运行了cups的服务器

然后转头在服务器的631端口查看一下,可以看到它将我们当成了新打印机并添加到系统中了
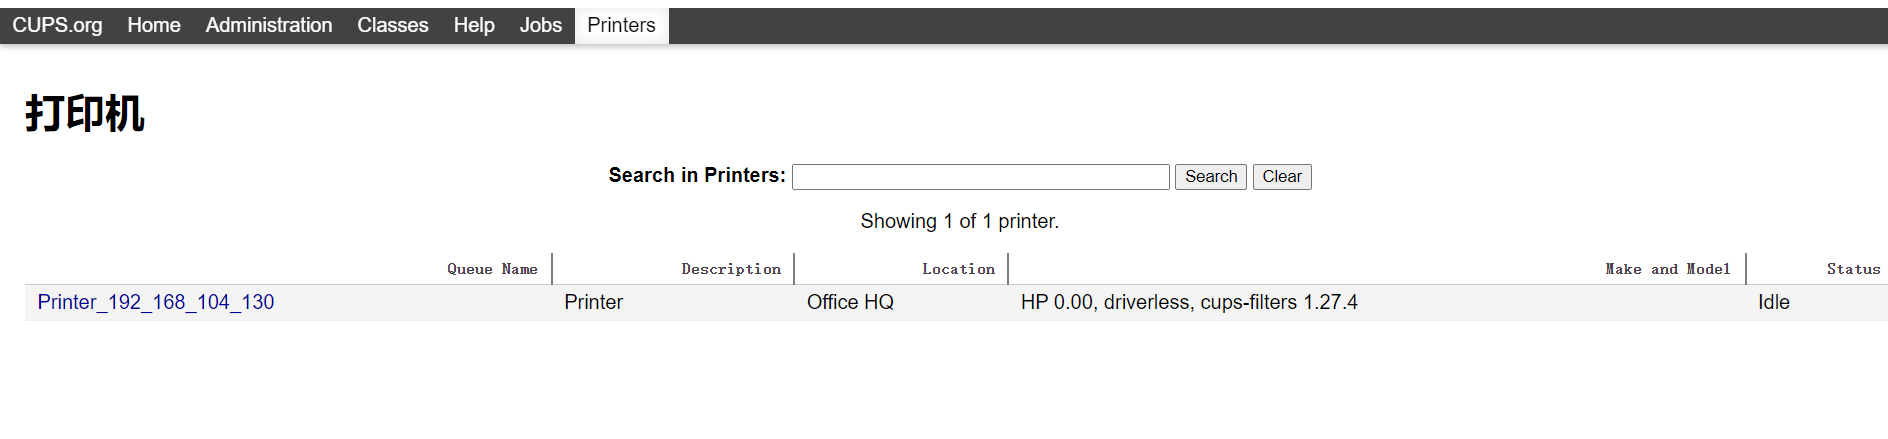
但是没有打印任务
公网复现
直接使用公网地址去执行,会报错
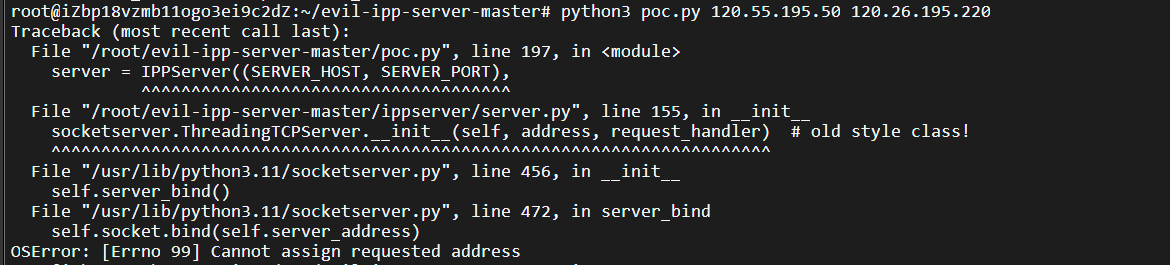
查看ip addr发现没有公网的网卡
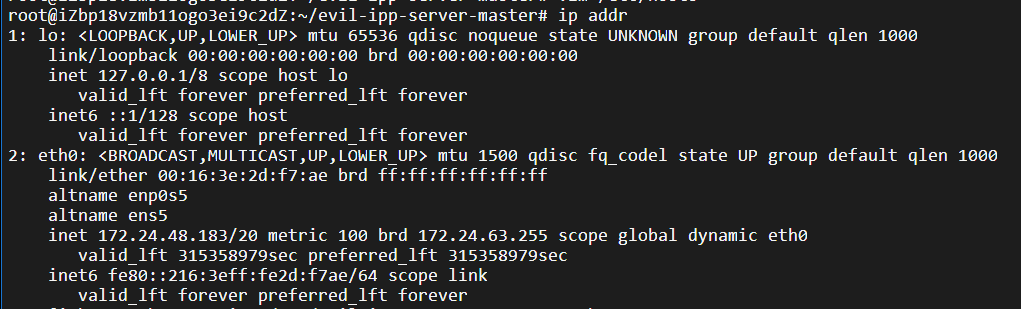
猜测是使用公网地址的话没有公网网卡,导致无法绑定ip,所以使用私网地址

但是公网cups服务器没有侦听udp631端口
