创建目录存放签证
[root@server100 ~]# mkdir /etc/nginx/certs
[root@server100 ~]# openssl req -newkey rsa:2048 -nodes -sha256 -keyout /etc/nginx/certs/timinglee.org.key -x509 -days 365 -out /etc/nginx/certs/timinglee.org.crt
..........+......+......+......+...+....+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++*....+.+..+...+....+..+...+......+.+...+........+...+.......+...+..+....+.........+...............+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++*.+.......+.....+.........+.......+...+..............+.......+.........+.....+....+..+.+...+..+.........+......+...+.+......+..............................+........+.+...+.....+..........+..+.+........+..........+......+........+.............+.....+...+......+....+......+.....+.+..+...+......................+...+...+...............+..+.......+..+....+.....+.+......+...+..+...+....+..+.+..+.+....................+......+......+.........+......+.......+......+..+.............+......+........+...+....+....................+....+............+........+.+....................+...+.......+...+.....+.+.....+.......+..+.......+.....+...+......+.........+..........+.....+.......+...........+...............+.........+....+....................+....+......+.....+......+....+......+...+..+...+...+..........+..............+.+..+...............+.+.....+....+...+..+......+.+...+...+..+.......+........+......+.+......+.....+...+.+.....+.+..............+...+.+..+.........+...+.............+.....+.........+..........+.........+.....+......+...+..........+..+.+........................+........+.+............+..+...+....+......+...+...............+..+...+......+.............+..+.+..................+......+...+...........+.+...+........+...................+.....+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
........+..+.........+....+.....+.+.................+....+......+..+......+.+.........+.....+.+........+.+.........+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++*...+...+..+.+........+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++*....+..+...+....+...+..+...+...............+..................+...+.+......+.................+............+.........+...................+......+.....+......+.........+....+...+.....+...+.+++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
-----
You are about to be asked to enter information that will be incorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Name or a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [XX]:CN
State or Province Name (full name) []:Shanxi
Locality Name (eg, city) [Default City]:Xi'an
Organization Name (eg, company) [Default Company Ltd]:timinglee
Organizational Unit Name (eg, section) []:webserver
Common Name (eg, your name or your server's hostname) []:www.timinglee.org
Email Address []:admin@timinlee.org
进行查看
[root@server100 ~]# ls /etc/nginx/certs/
timinglee.org.crt timinglee.org.key[root@server100 ~]# vim /etc/nginx/conf.d/vhosts.conf
server {
listen 443 ssl;
server_name login.timinglee.org;
ssl_certificate "/etc/nginx/certs/timinglee.org.crt";
ssl_certificate_key "/etc/nginx/certs/timinglee.org.key";
root /usr/share/nginx/virtual/login;
index index.html;
}
[root@server100 ~]# mkdir -p /usr/share/nginx/virtual/login
[root@server100 ~]# echo login.timinglee.org > /usr/share/nginx/virtual/login/index.html
[root@server100 ~]# nginx -t
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
[root@server100 ~]# systemctl restart nginx.service最后在windows里面测试,效果明显
首先在windows里面也要做解析
C:\Windows\System32\drivers\etc这个目录下的hosts里面,添加172.25.254.100 login.timinglee.org
然后在浏览器里面进行访问
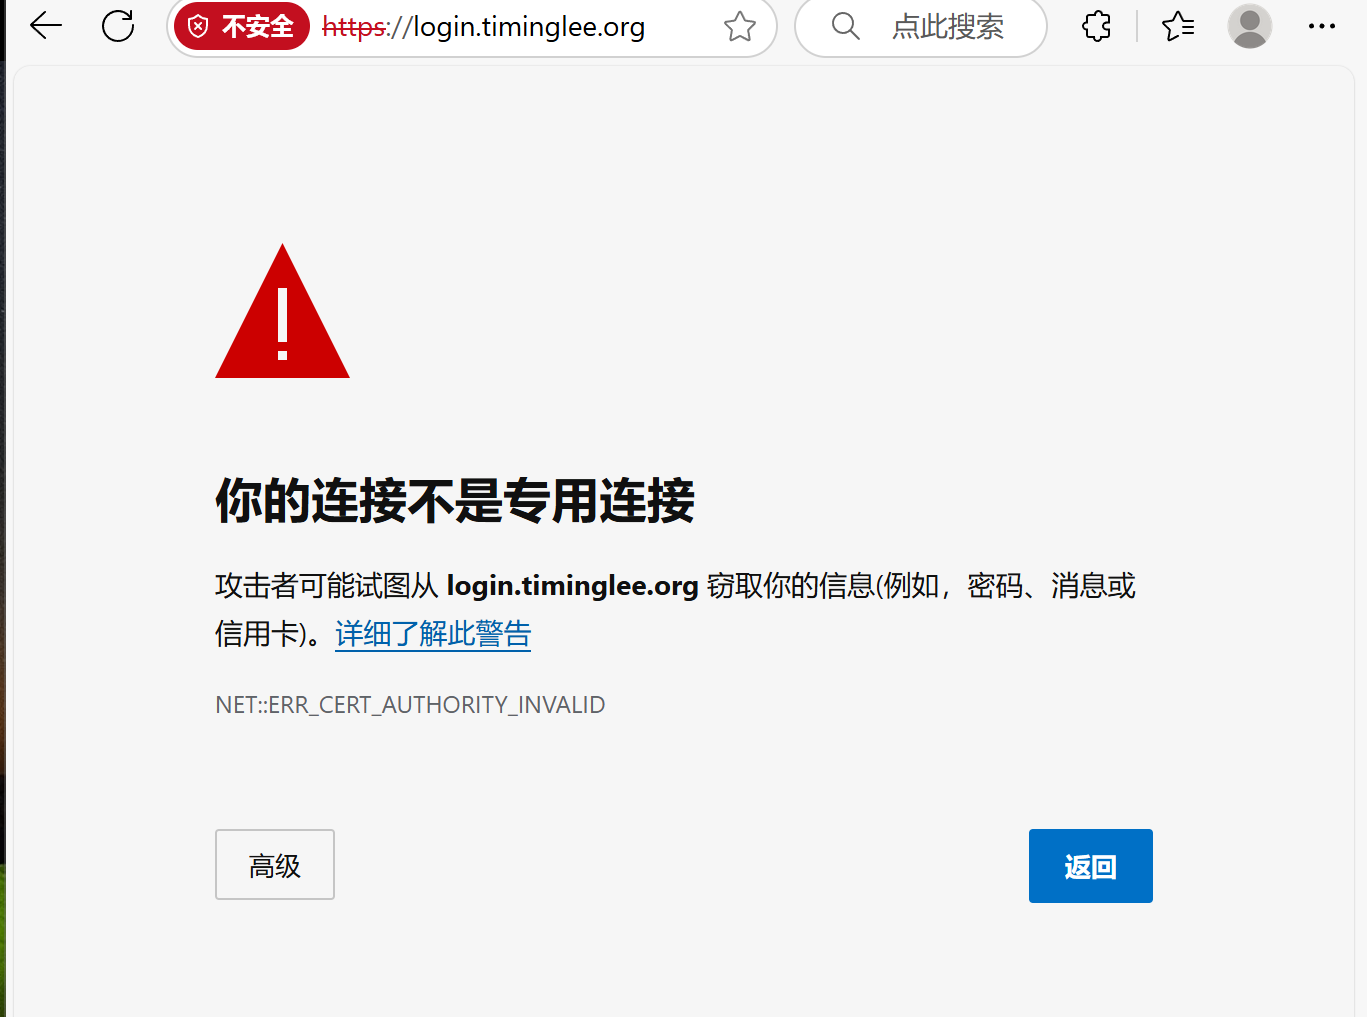
选择高级,继续查看
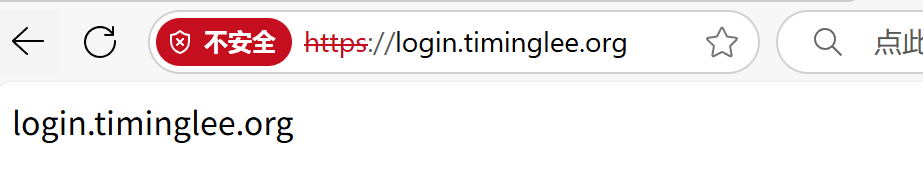
强制走加密
root@server100 \~# vim /etc/nginx/conf.d/vhosts.conf
在443上面添加
server {
listen 80;
server_name login.timinglee.org;
rewrite ^/(.*) https://login.timinglee.org/1 permanent;
}
同样也需要做本地解析
root@server100 \~# curl -I login.timinglee.org/hehe
HTTP/1.1 301 Moved Permanently
Server: nginx/1.20.1
Date: Thu, 29 May 2025 09:31:06 GMT
Content-Type: text/html
Content-Length: 169
Connection: keep-alive
Location: https://login.timinglee.org/hehe