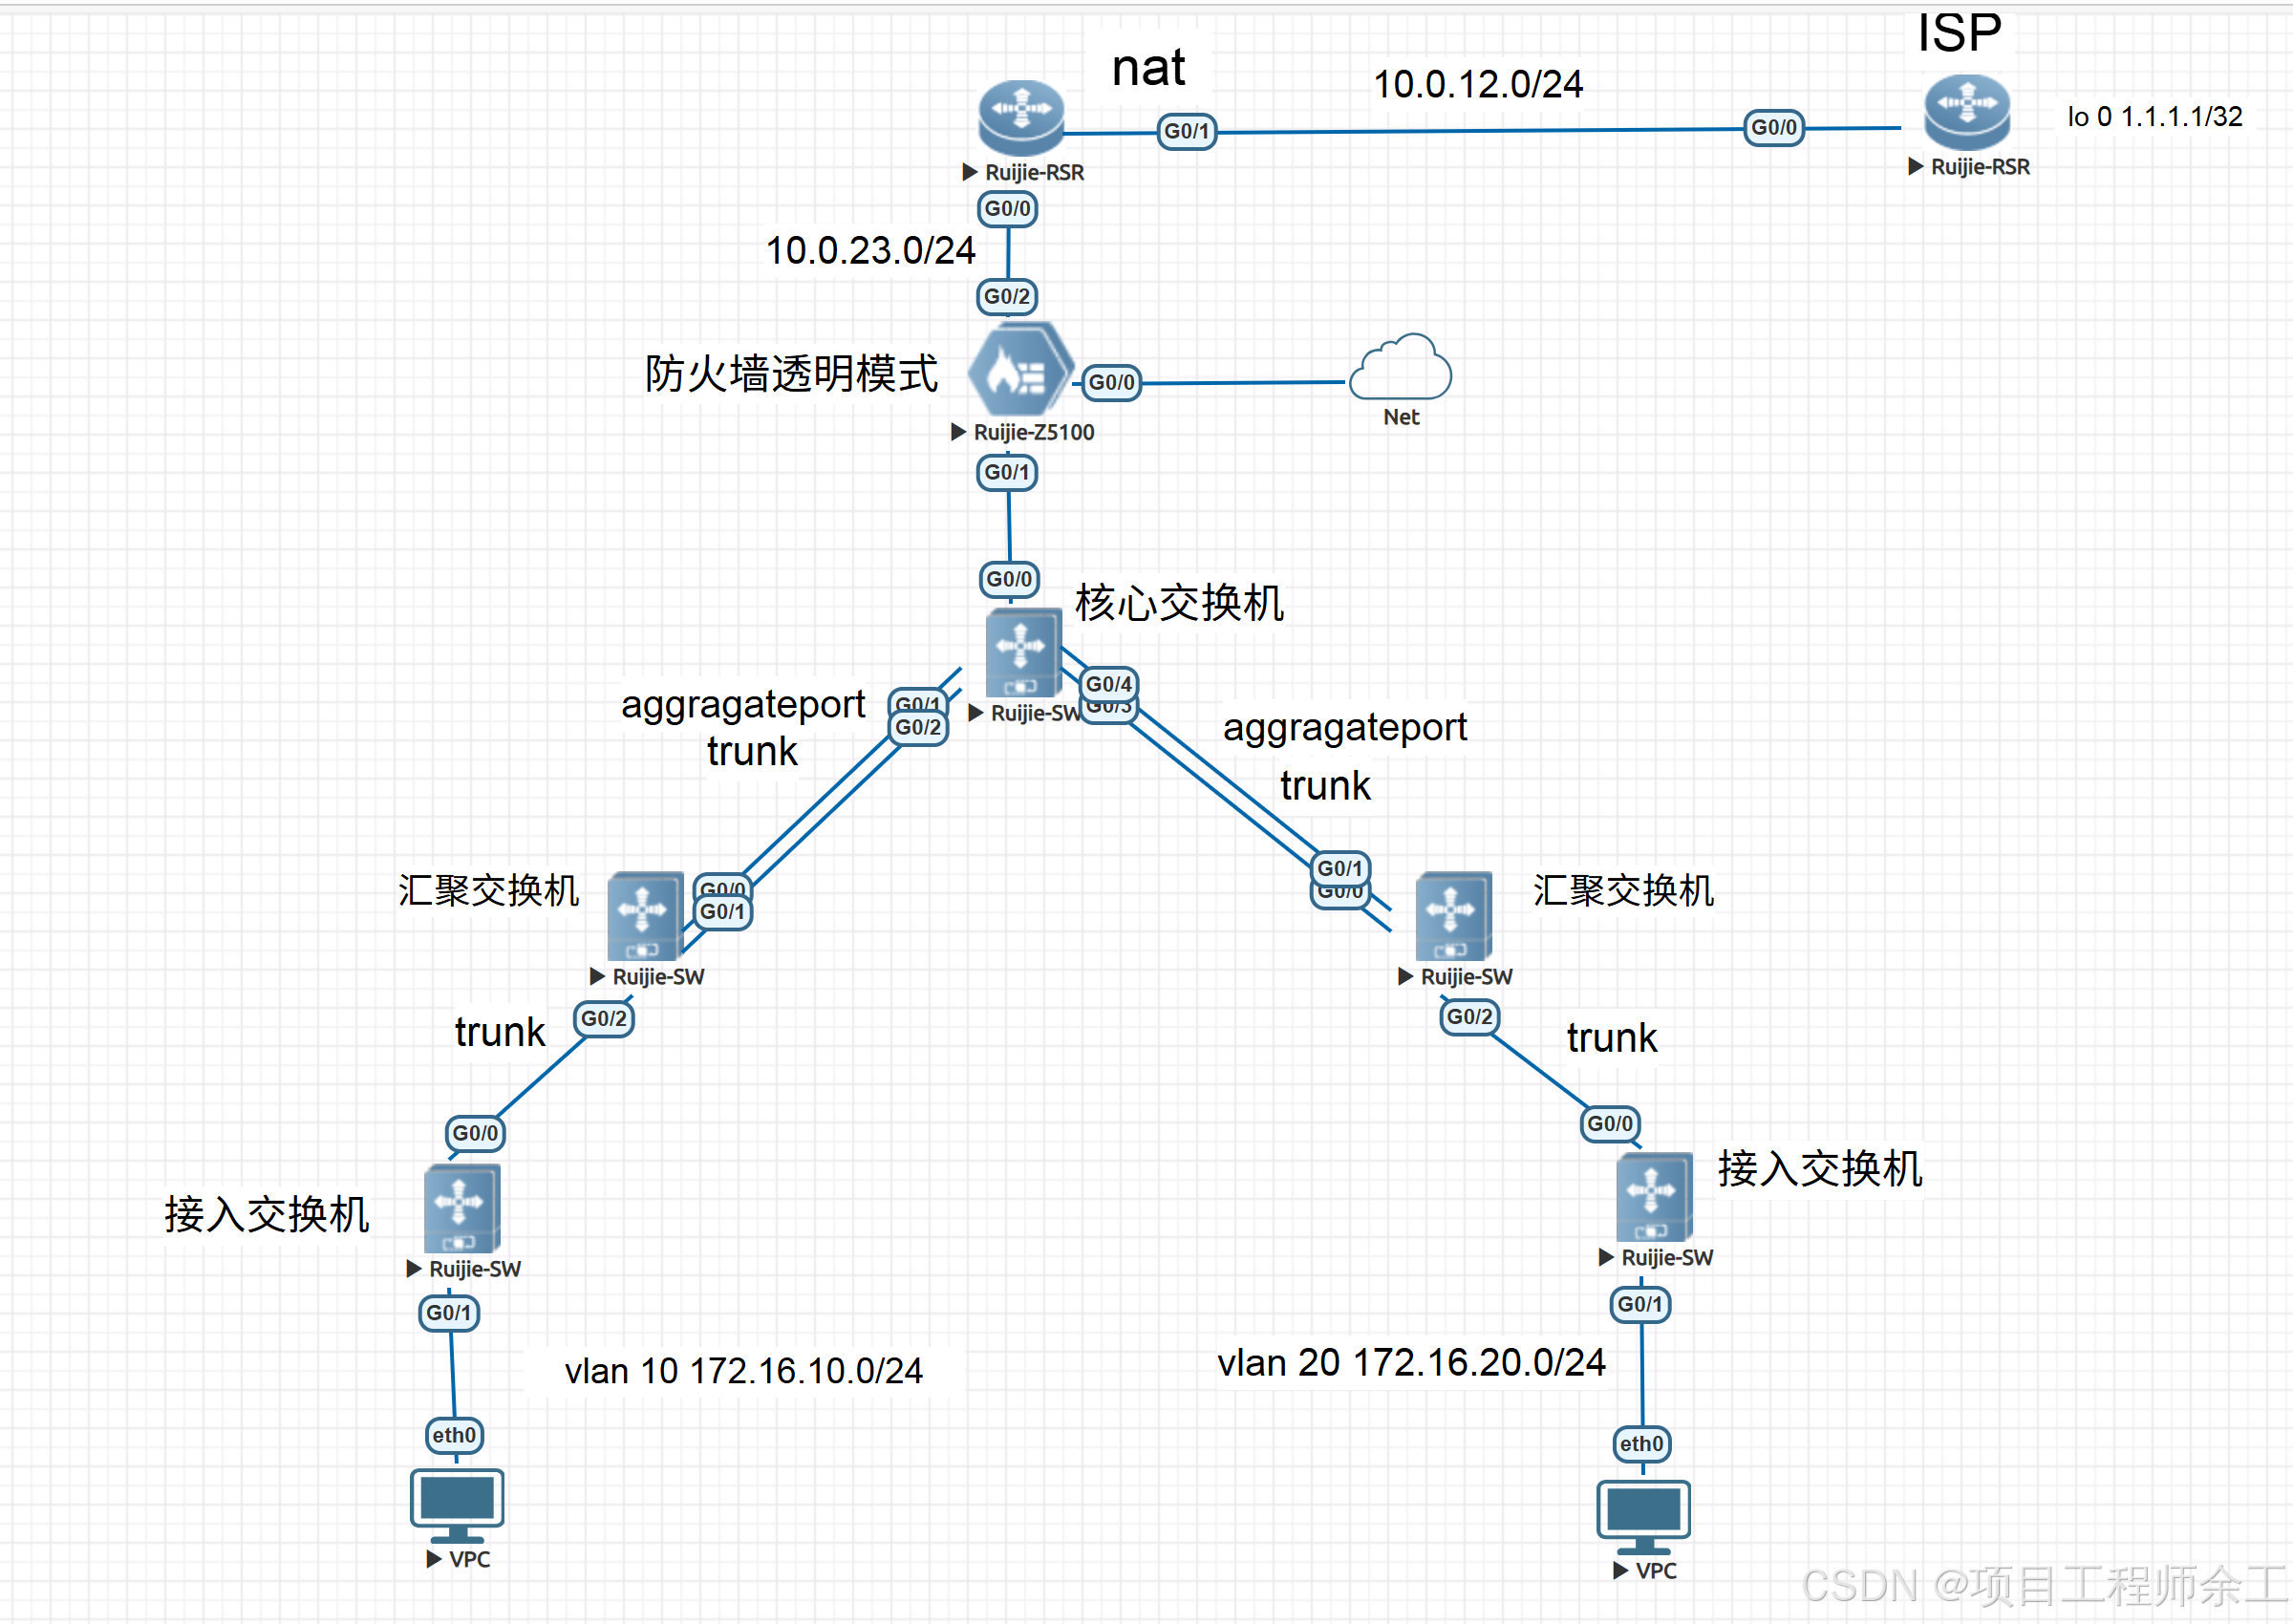
网络规划设计
1、防火墙做透明模式用web配置,其它设备用命令行配置
2、路由上做nat,并和核心起ospf,并下发默认路由,路由器配置远程telnet用户名密码的方式登陆
3、核心上ospf配静默接口,和汇聚用聚合跑trunk
4、所有交换机跑rstp生成树,核心配为全网根桥权限最高
5、接入交换机配边缘端口及bpdu保护,并配dhcp snooping防私接小路由
6、pc使用dhcp自动分配地址,dhcp放在核心上
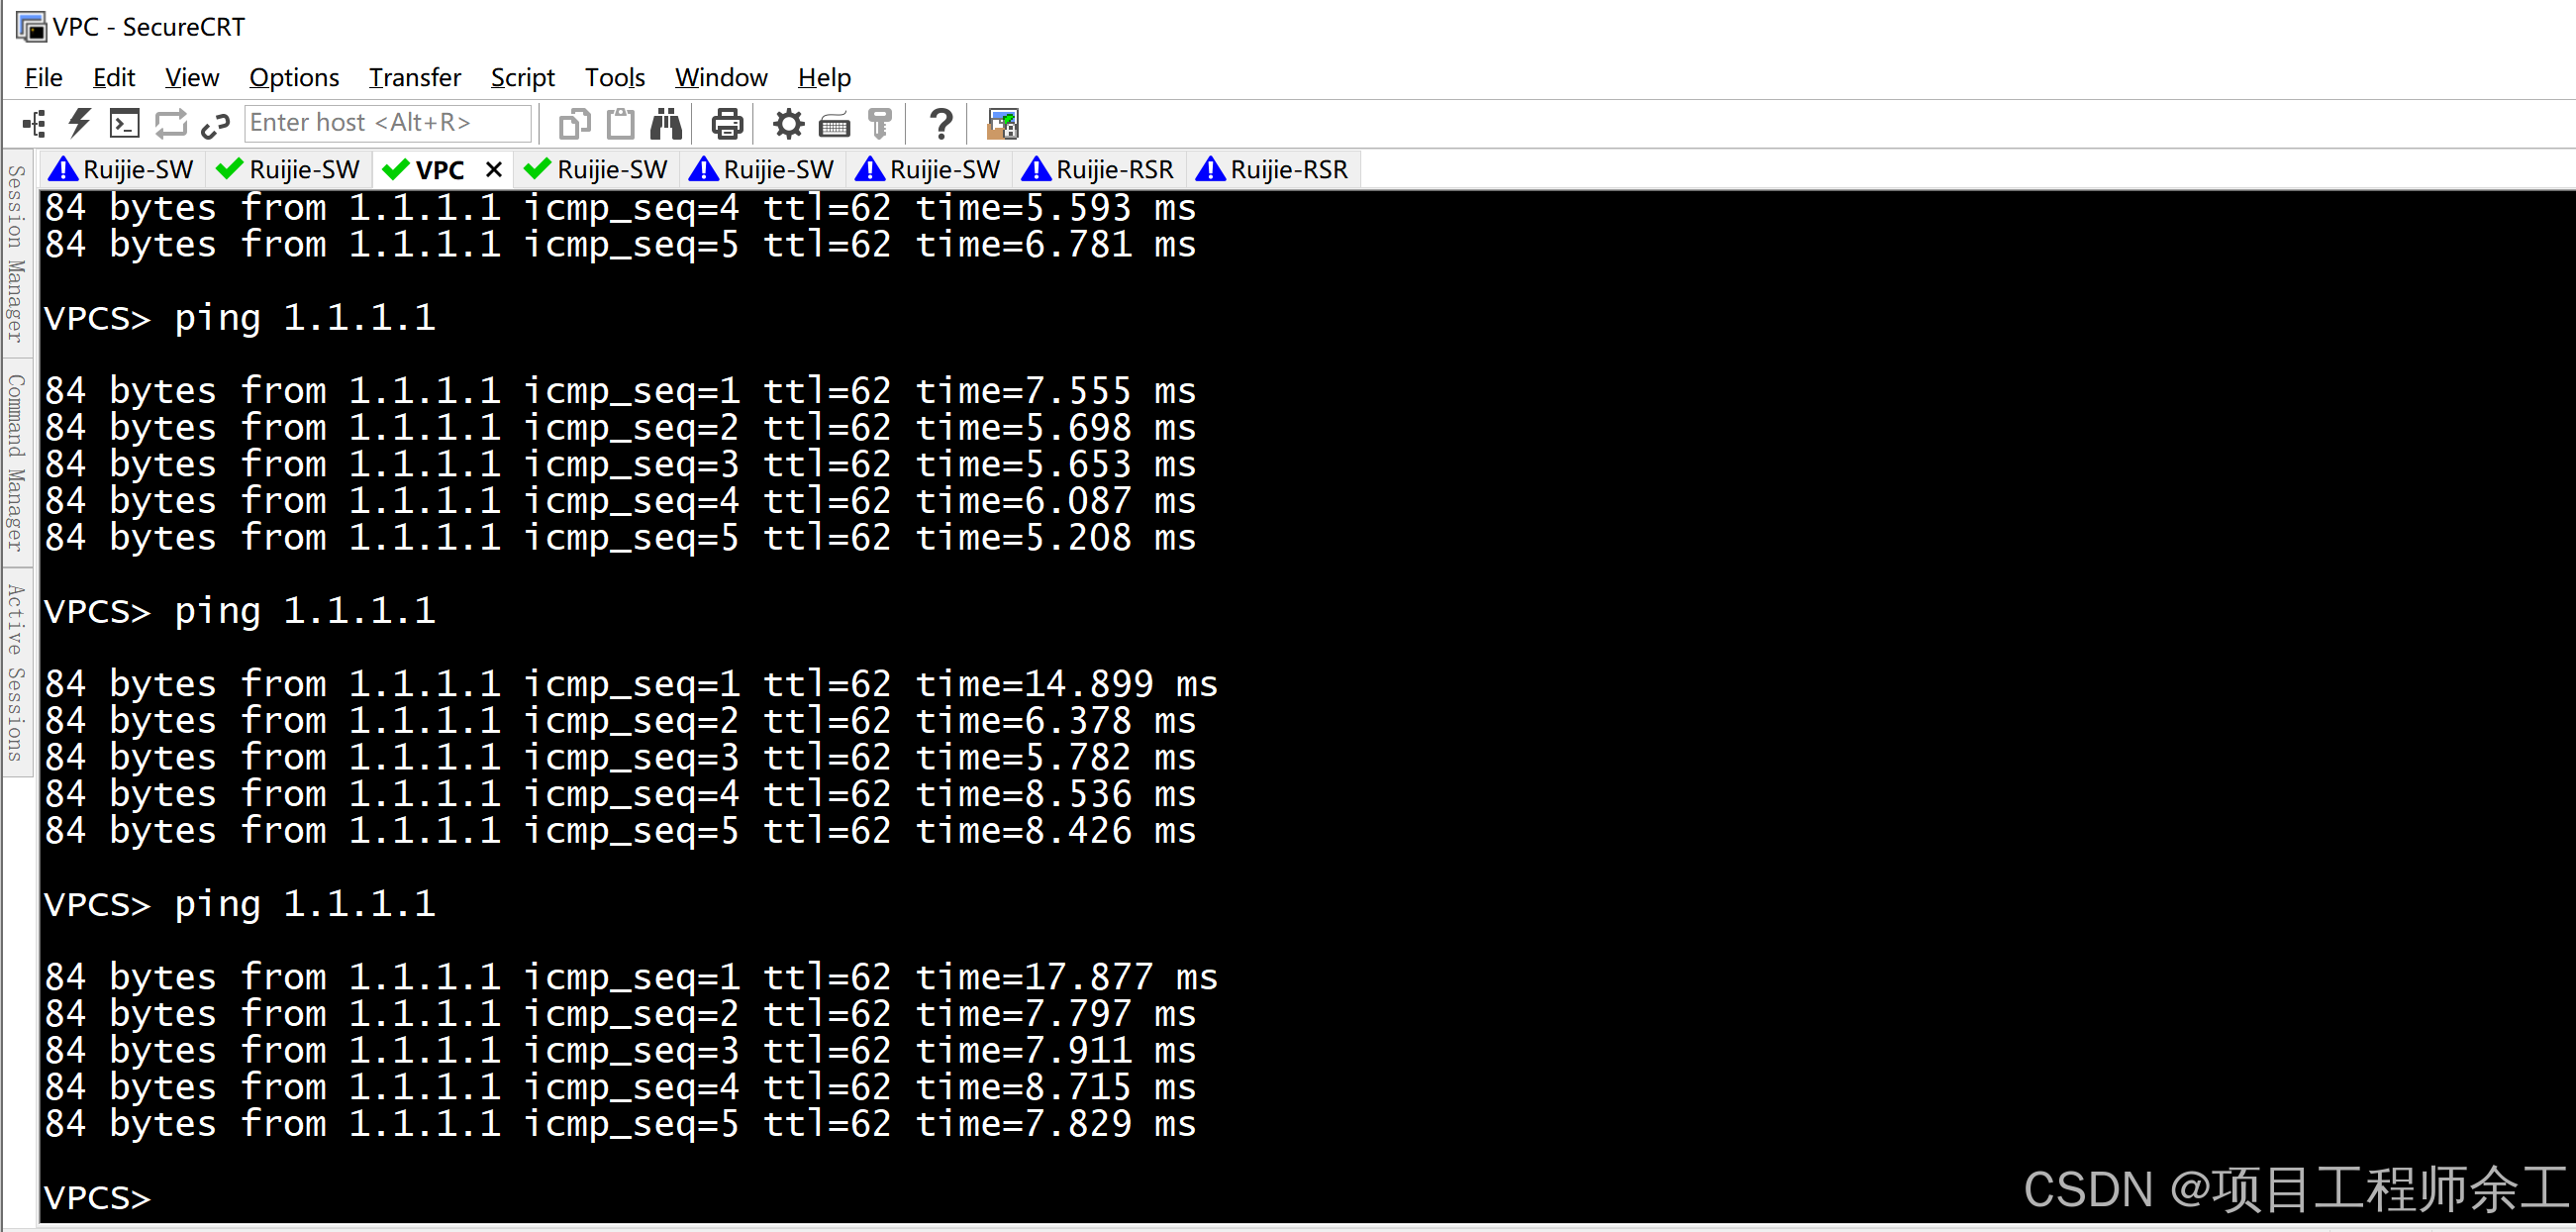
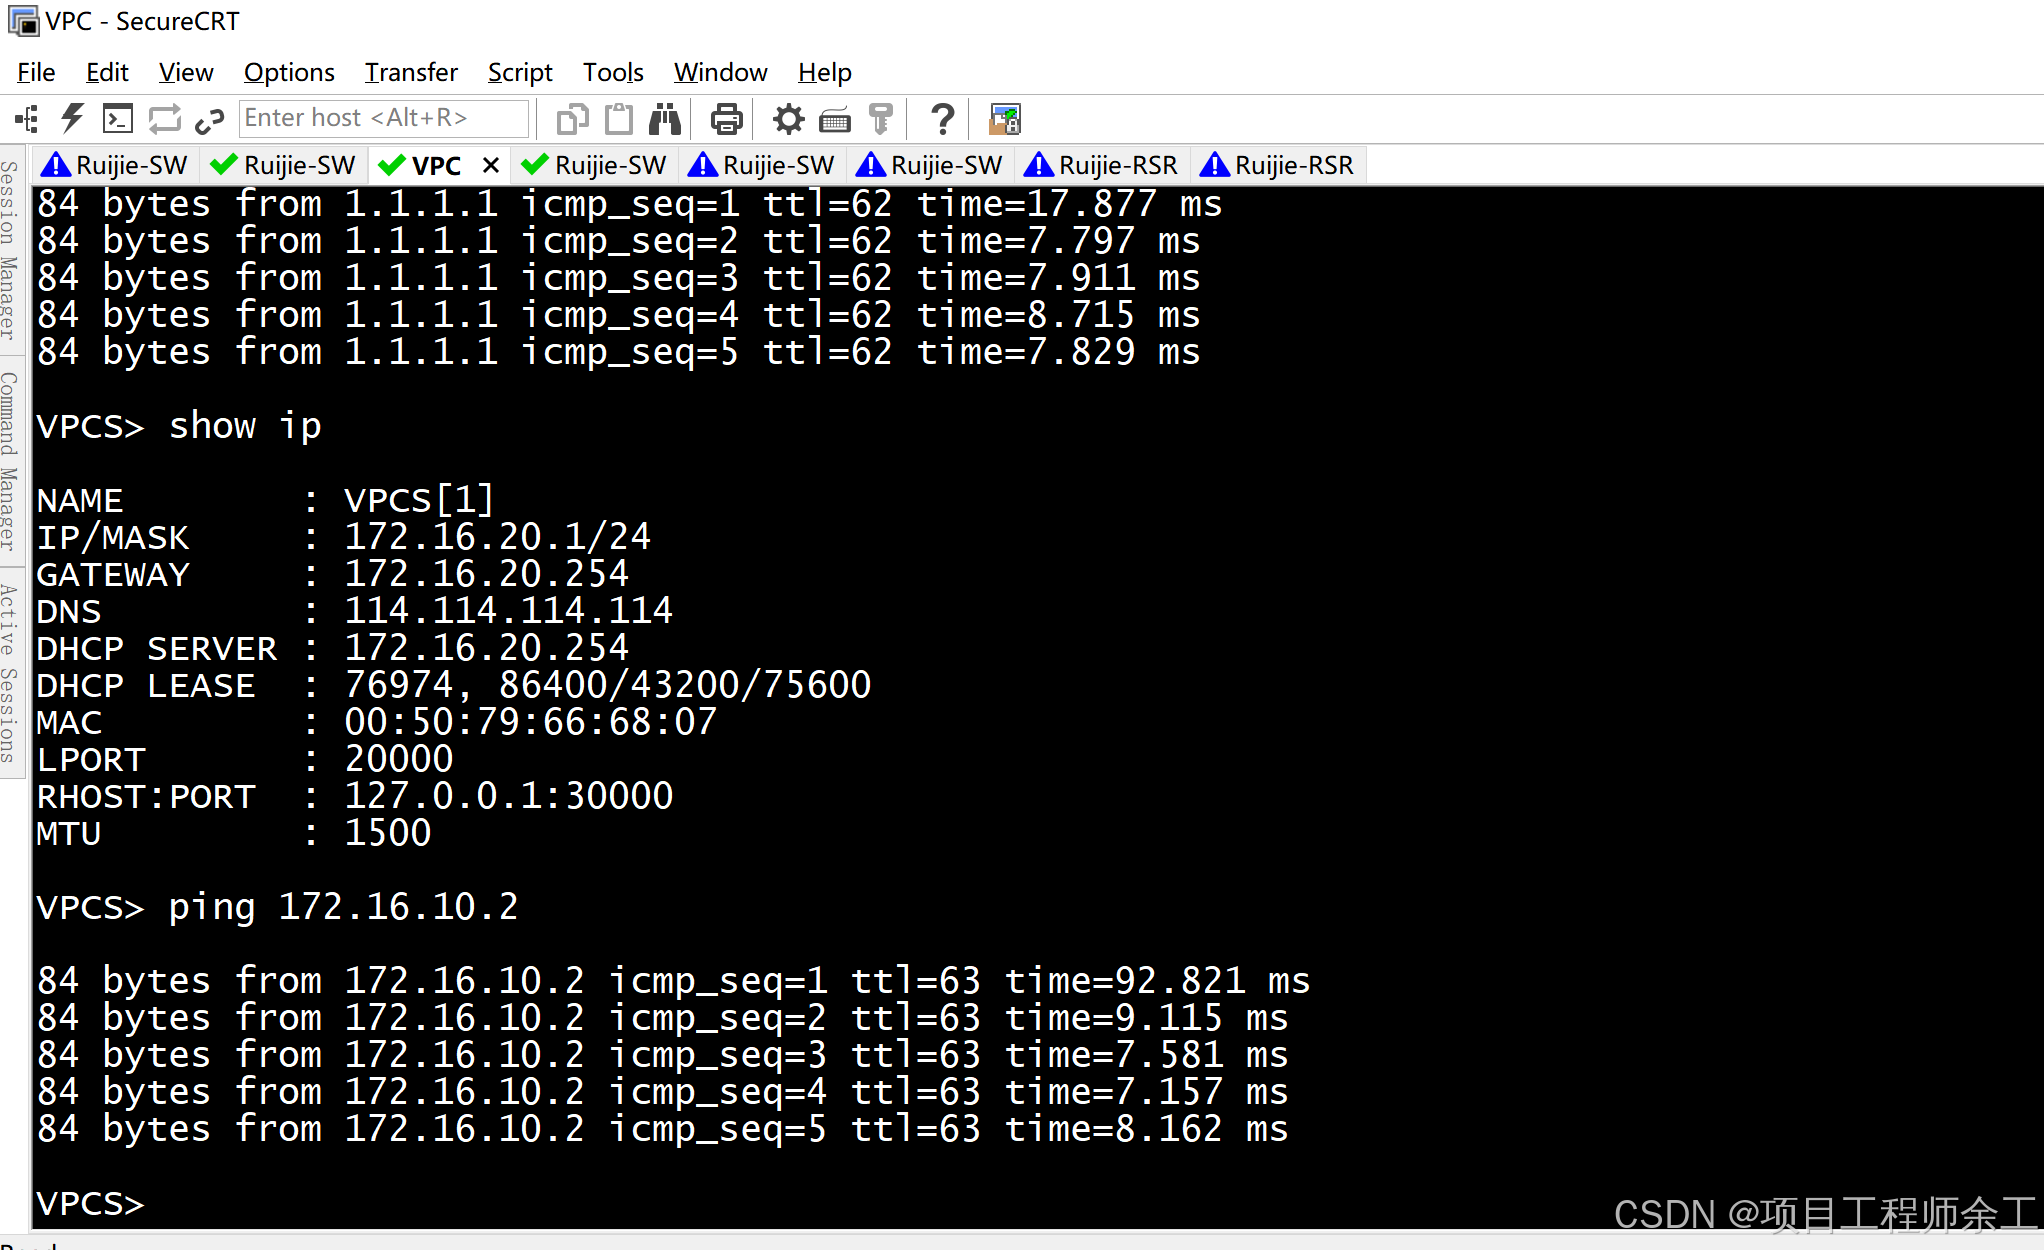
7、isp用回环接口模拟,内网两台pc互通,且可以nat访问isp的回环口1.1.1.1
各设备配置
isp配置
r2#show run
r2#show running-config
Building configuration...
Current configuration: 775 bytes
version RG-NSE-Route(V1.06)
hostname r2
!
interface GigabitEthernet 0/0
ip address 10.0.12.1 255.255.255.0
!
!
interface Loopback 0 模拟公网终端
ip address 1.1.1.1 255.255.255.255
end
出口路由配置
r1#show running-config
Building configuration...
Current configuration: 1323 bytes
version RG-NSE-Route(V1.06)
hostname r1
!
ip access-list standard 1 //访问控制列表,要上公网的网段
20 permit 172.16.10.0 0.0.0.255
30 permit 172.16.20.0 0.0.0.255
!
username admin password Huawei@123 配置telnet用户名密码的方式连接
!
enable password Huawei@123 配置全局登陆密码
!
vlan 1
!
interface GigabitEthernet 0/0
ip address 10.0.23.2 255.255.255.0
ip nat inside //nat配置
!
interface GigabitEthernet 0/1
ip address 10.0.12.2 255.255.255.0
ip nat outside //nat配置
!
interface AggregatePort 2
switchport mode trunk
switchport trunk allowed vlan only 20
!
router ospf 1
router-id 1.1.1.1
graceful-restart
network 10.0.23.2 0.0.0.0 area 0
default-information originate //下发默认路由
!
ip nat pool p1 10.0.12.2 10.0.12.2 netmask 255.255.255.0 //nat上网配置
ip nat inside source list 1 pool p1 overload //nat上网配置
!
ip route 0.0.0.0 0.0.0.0 10.0.12.1 //默认路由
!
line console 0
logging synchronous
line vty 0 4
logging synchronous
login local //使用本地用户名密码telnet登陆
!
end
核心交换机配置
hx#show run
hx#show running-config
Building configuration...
Current configuration: 1718 bytes
version RG-NSE-Switch(V1.06)
hostname hx
!
spanning-tree mode rstp //开生成树rstp
spanning-tree mst 0 priority 0 //设置为全网根桥
spanning-tree //开生成树
!
!
service dhcp //开dhcp 服务
!
ip dhcp pool vlan10 //dhcp池配置
network 172.16.10.0 255.255.255.0
dns-server 114.114.114.114
default-router 172.16.10.254
!
ip dhcp pool vlan20
network 172.16.20.0 255.255.255.0
dns-server 114.114.114.114
default-router 172.16.20.254
!
vlan range 1,10,20,100
!
interface GigabitEthernet 0/0
switchport access vlan 100 //和对端路由连接,中间过透明防火墙
!
interface GigabitEthernet 0/1
port-group 1 //加入聚合口1
!
interface GigabitEthernet 0/2
port-group 1
!
interface GigabitEthernet 0/3
port-group 2
!
interface GigabitEthernet 0/4
port-group 2
!
interface AggregatePort 1
switchport mode trunk
switchport trunk allowed vlan only 10 //只放vlan 10
!
interface AggregatePort 2
switchport mode trunk
switchport trunk allowed vlan only 20
!
interface VLAN 10 //三层vlanif配置
ip address 172.16.10.254 255.255.255.0
!
interface VLAN 20
ip address 172.16.20.254 255.255.255.0
!
interface VLAN 100
ip address 10.0.23.3 255.255.255.0
!
router ospf 1
router-id 2.2.2.2
graceful-restart
passive-interface VLAN 10 //静默接口
passive-interface VLAN 20
network 10.0.23.3 0.0.0.0 area 0
network 172.16.10.0 0.0.0.255 area 0
network 172.16.20.0 0.0.0.255 area 0
!
end
汇聚交换机1
hj1#show run
hj1#show running-config
Building configuration...
Current configuration: 918 bytes
version RG-NSE-Switch(V1.06)
hostname hj1
!
spanning-tree mode rstp
spanning-tree
!
vpdn limit_rate 15
!
vlan range 1,10
!
interface GigabitEthernet 0/0
port-group 1
!
interface GigabitEthernet 0/1
port-group 1
!
interface GigabitEthernet 0/2
switchport mode trunk
switchport trunk allowed vlan only 10
!
!
interface AggregatePort 1
switchport mode trunk
switchport trunk allowed vlan only 10
!
end
汇聚交换机2
hj2#show run
hj2#show running-config
Building configuration...
Current configuration: 918 bytes
version RG-NSE-Switch(V1.06)
hostname hj2
!
spanning-tree mode rstp
spanning-tree
!
!
vpdn limit_rate 15
!
vlan range 1,20
!
interface GigabitEthernet 0/0
port-group 1
!
interface GigabitEthernet 0/1
port-group 1
!
interface GigabitEthernet 0/2
switchport mode trunk
switchport trunk allowed vlan only 20
!
!
interface AggregatePort 1
switchport mode trunk
switchport trunk allowed vlan only 20
!
line console 0
logging synchronous
line vty 0 4
logging synchronous
login
!
end
接入交换机1
jr1#show run
jr1#show running-config
Building configuration...
Current configuration: 952 bytes
version RG-NSE-Switch(V1.06)
hostname jr1
!
spanning-tree portfast bpduguard default //开bpdu保护
spanning-tree mode rstp
spanning-tree
!
ip dhcp snooping //开snooping防私接小路
!
no cwmp
!
service dhcp //开dhcp
!
vlan range 1,10
!
interface GigabitEthernet 0/0
switchport mode trunk
switchport trunk allowed vlan only 10
ip dhcp snooping trust //上联信任口
!
interface GigabitEthernet 0/1
switchport access vlan 10
spanning-tree portfast //边缘端口
!
!
end
接入交换机2
jr2>en
jr2#show run
jr2#show running-config
Building configuration...
Current configuration: 952 bytes
version RG-NSE-Switch(V1.06)
hostname jr2
!
spanning-tree portfast bpduguard default
spanning-tree mode rstp
spanning-tree
!
ip dhcp snooping
!
no cwmp
!
service dhcp
!
vlan range 1,20
!
interface GigabitEthernet 0/0
switchport mode trunk
switchport trunk allowed vlan only 20
ip dhcp snooping trust
!
interface GigabitEthernet 0/1
switchport access vlan 20
spanning-tree portfast
!
line console 0
logging synchronous
line vty 0 4
logging synchronous
login
!
end
防火墙配置
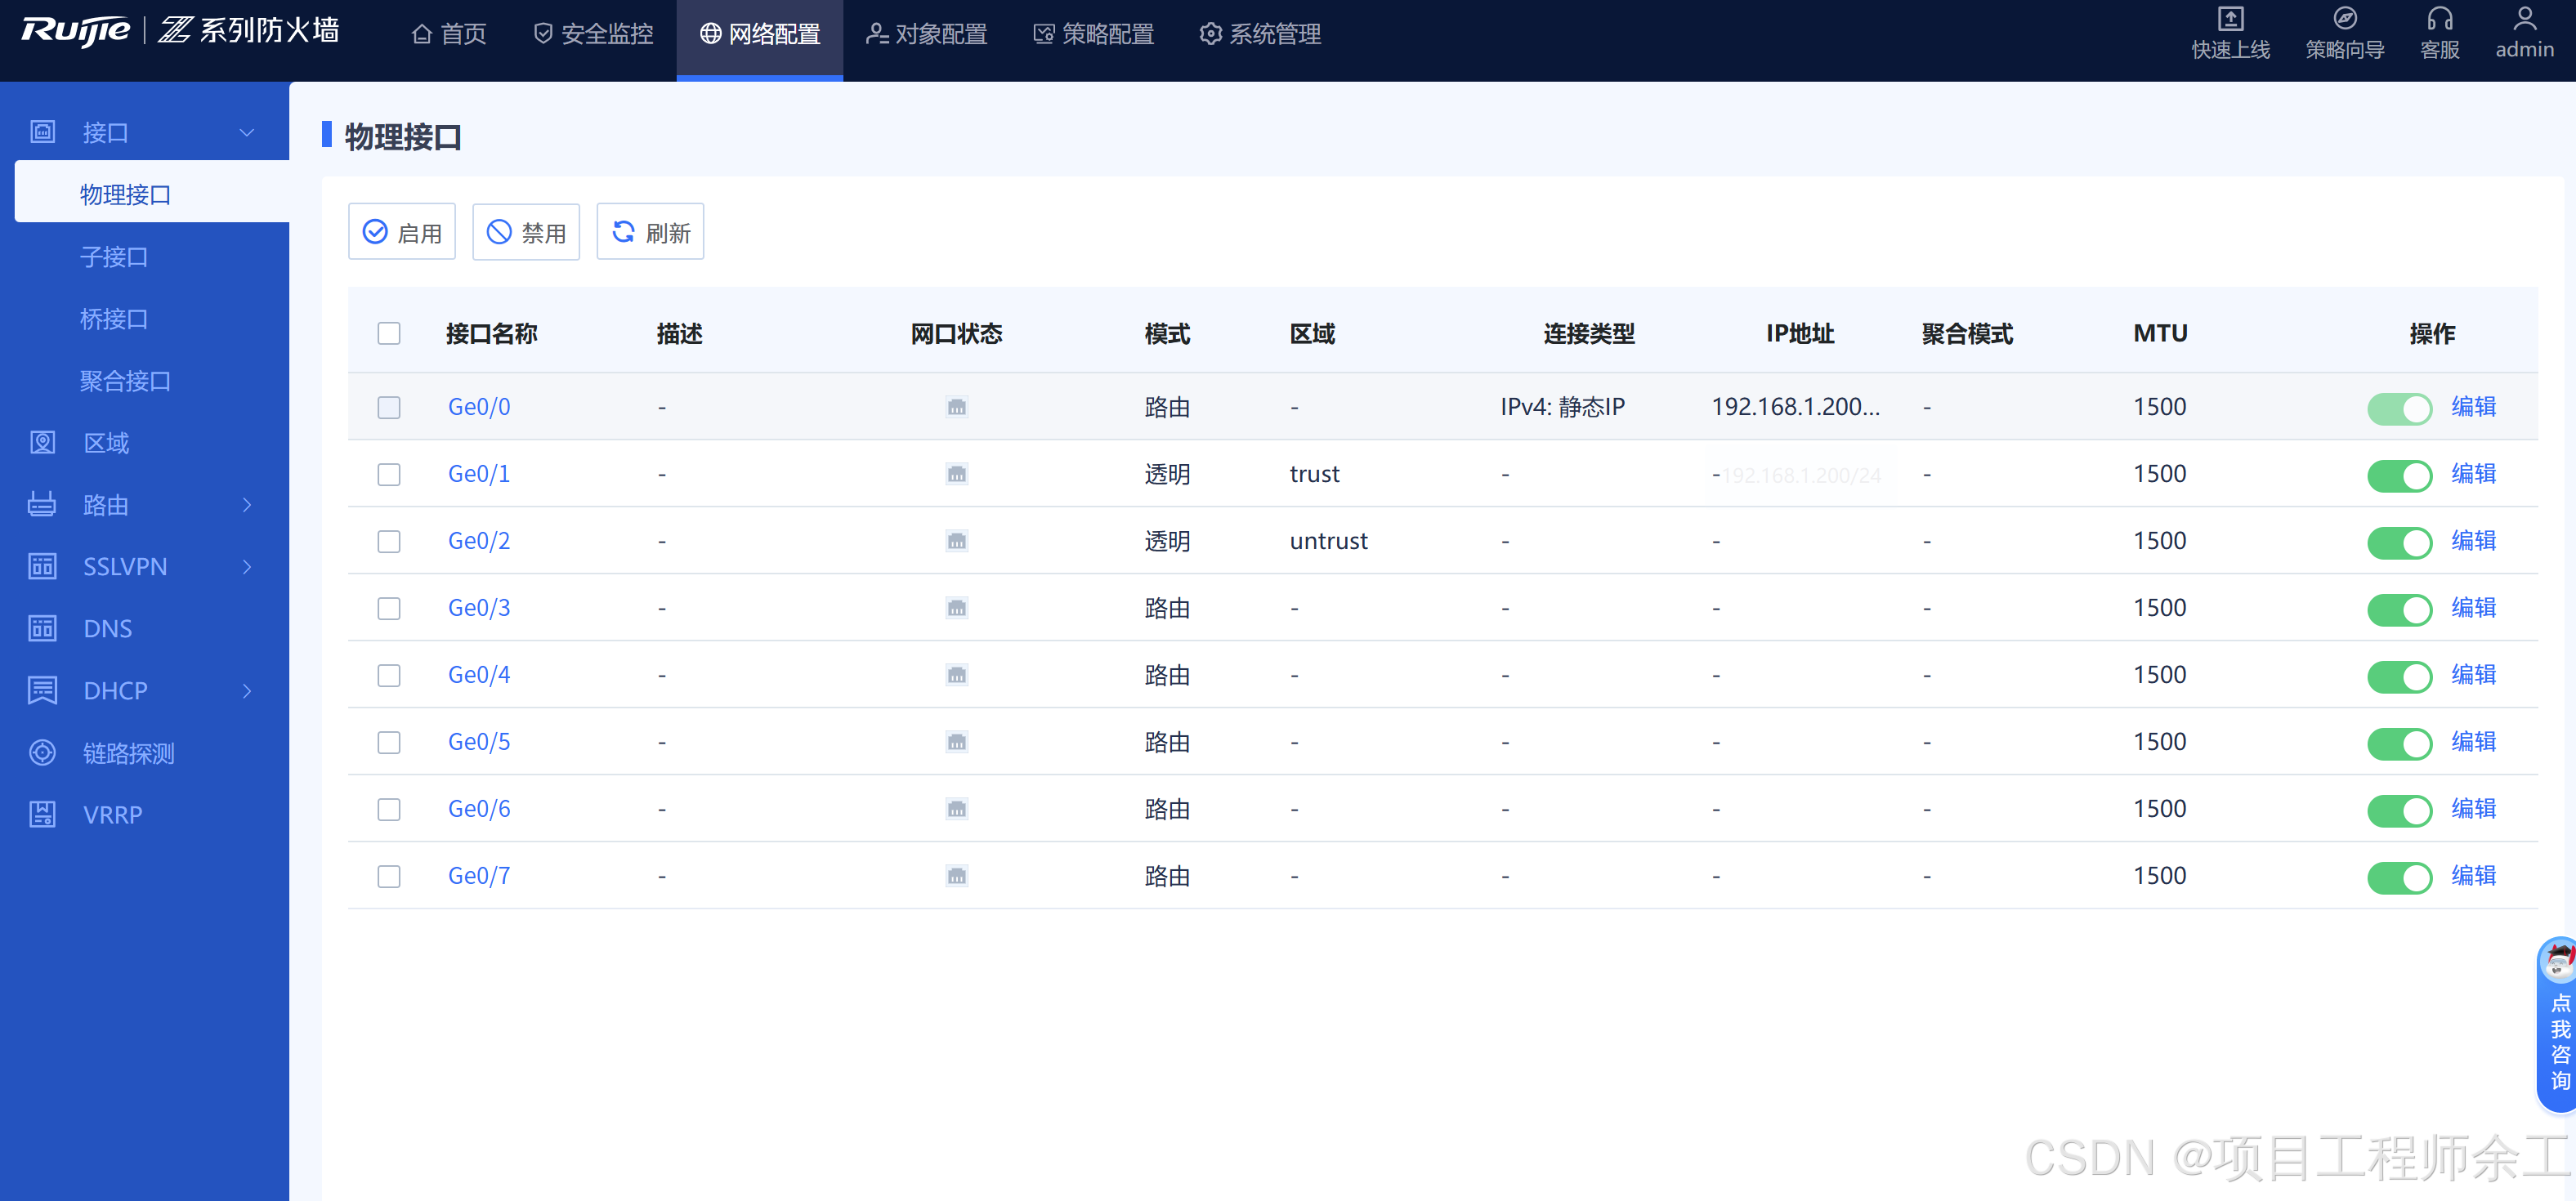
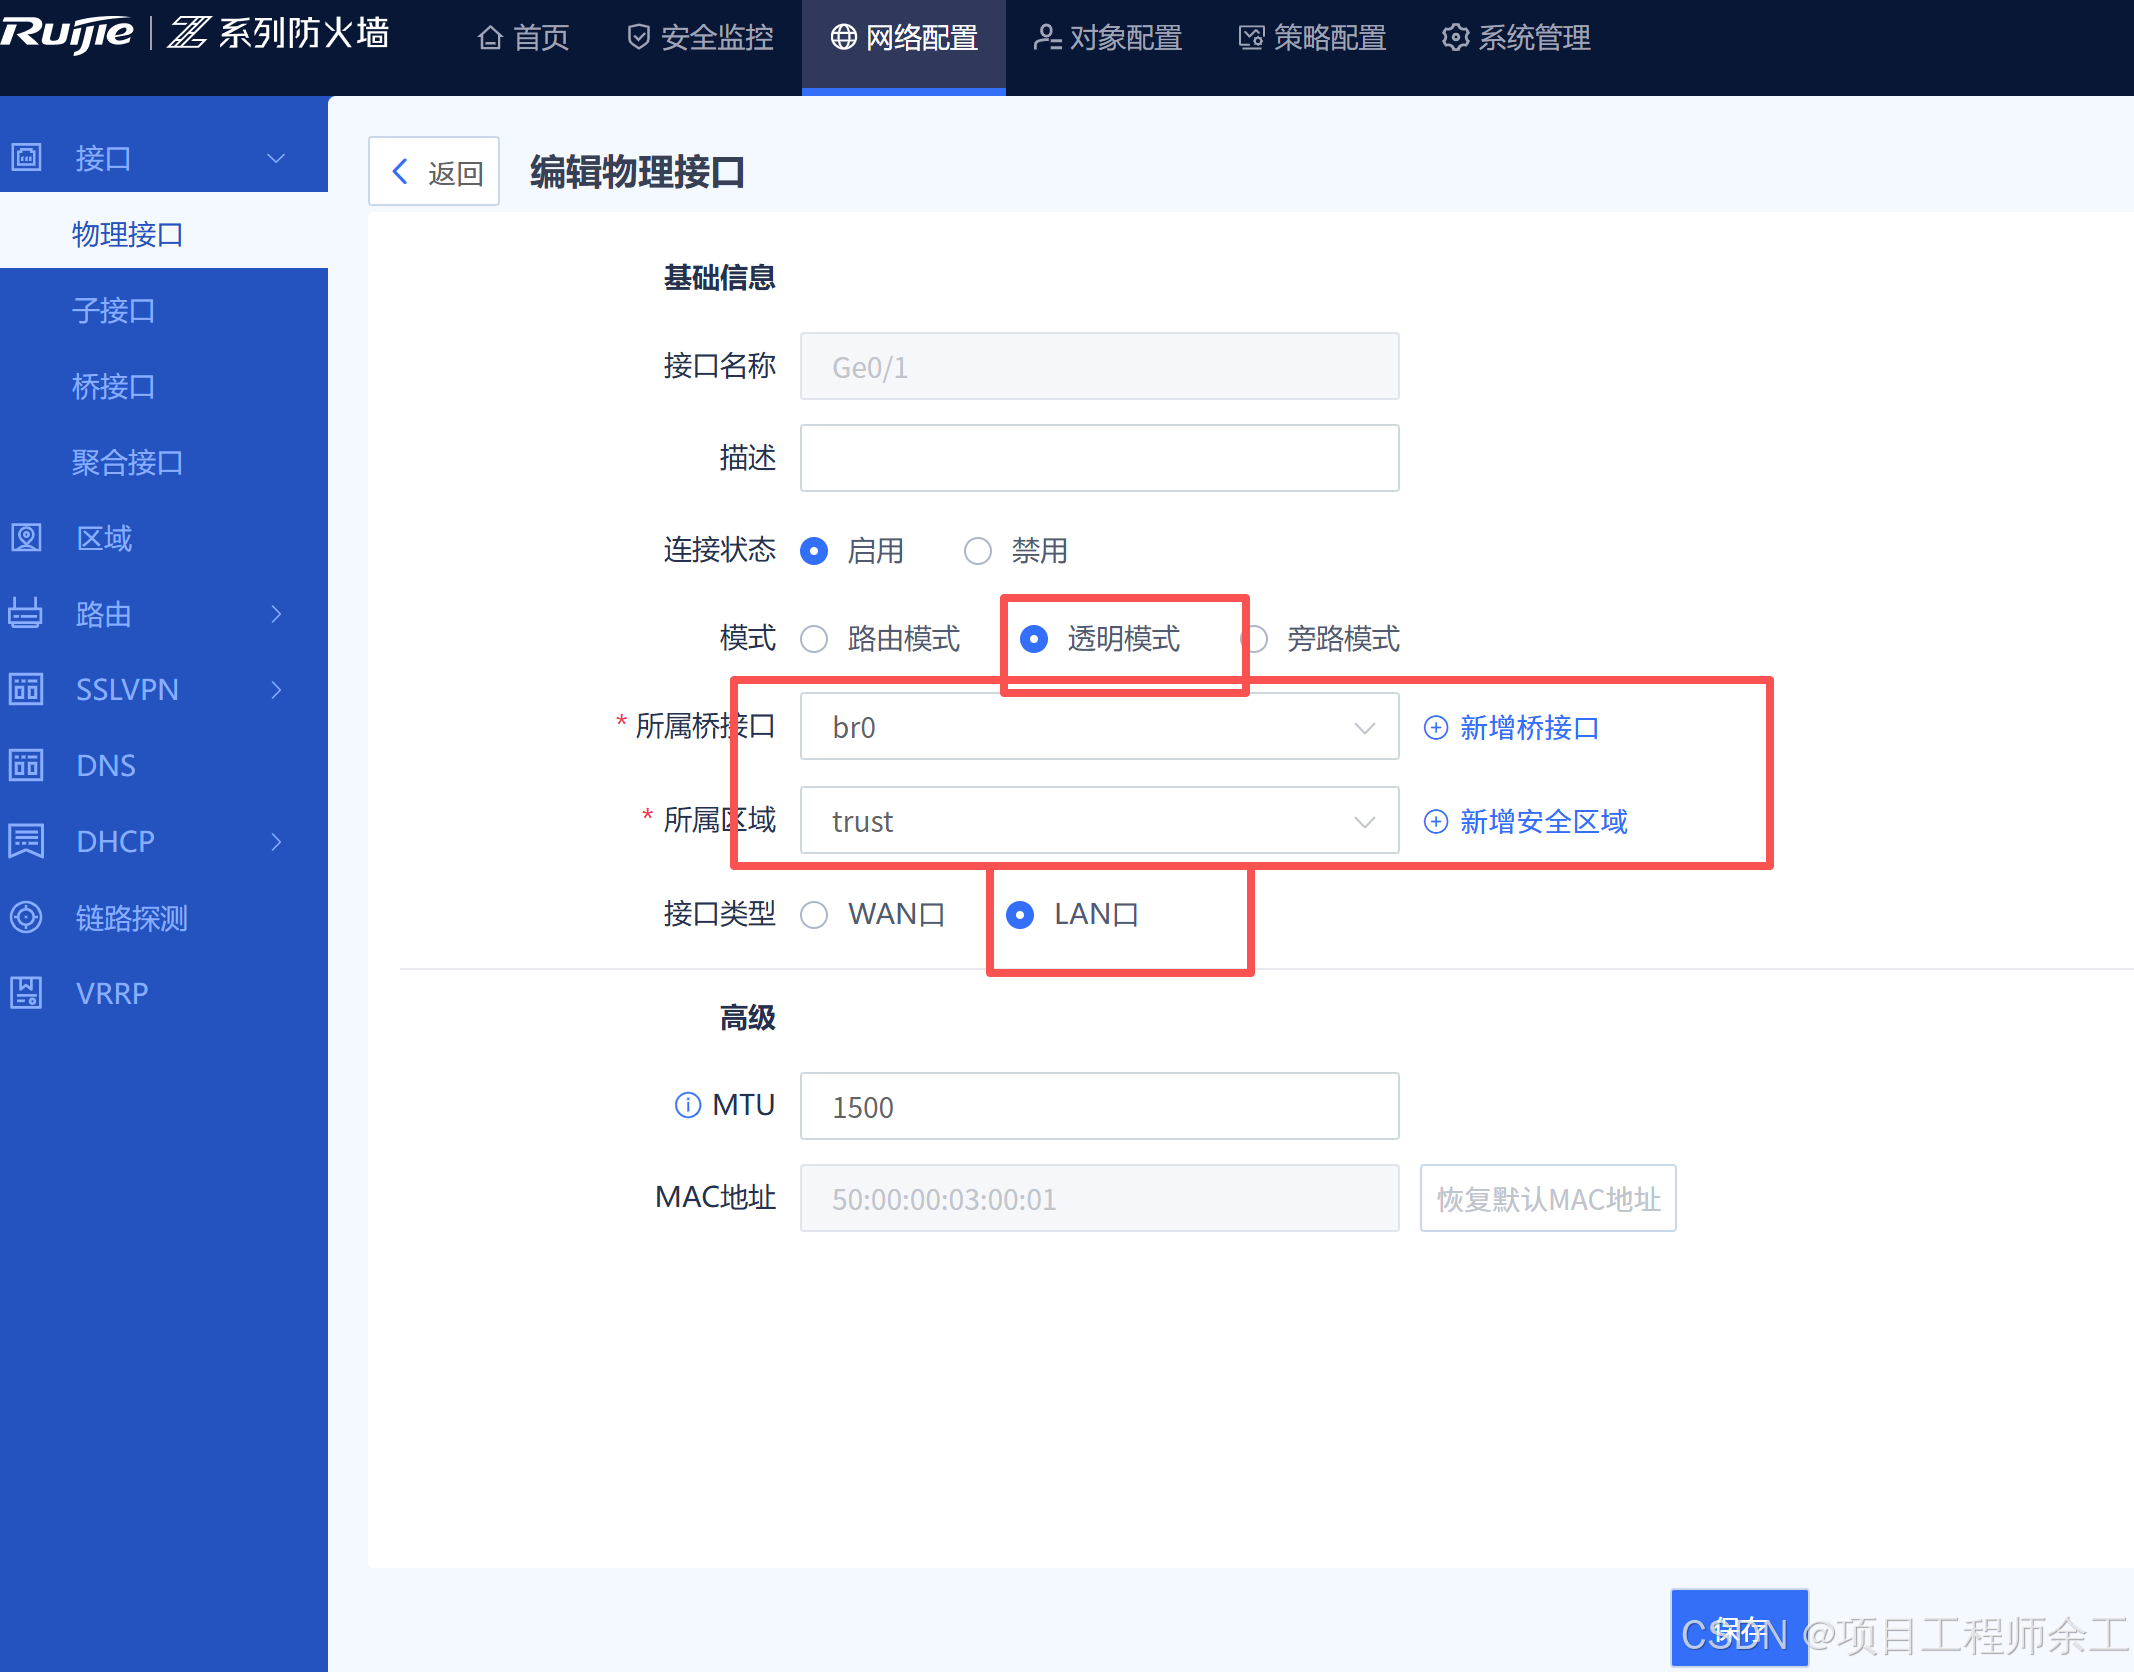
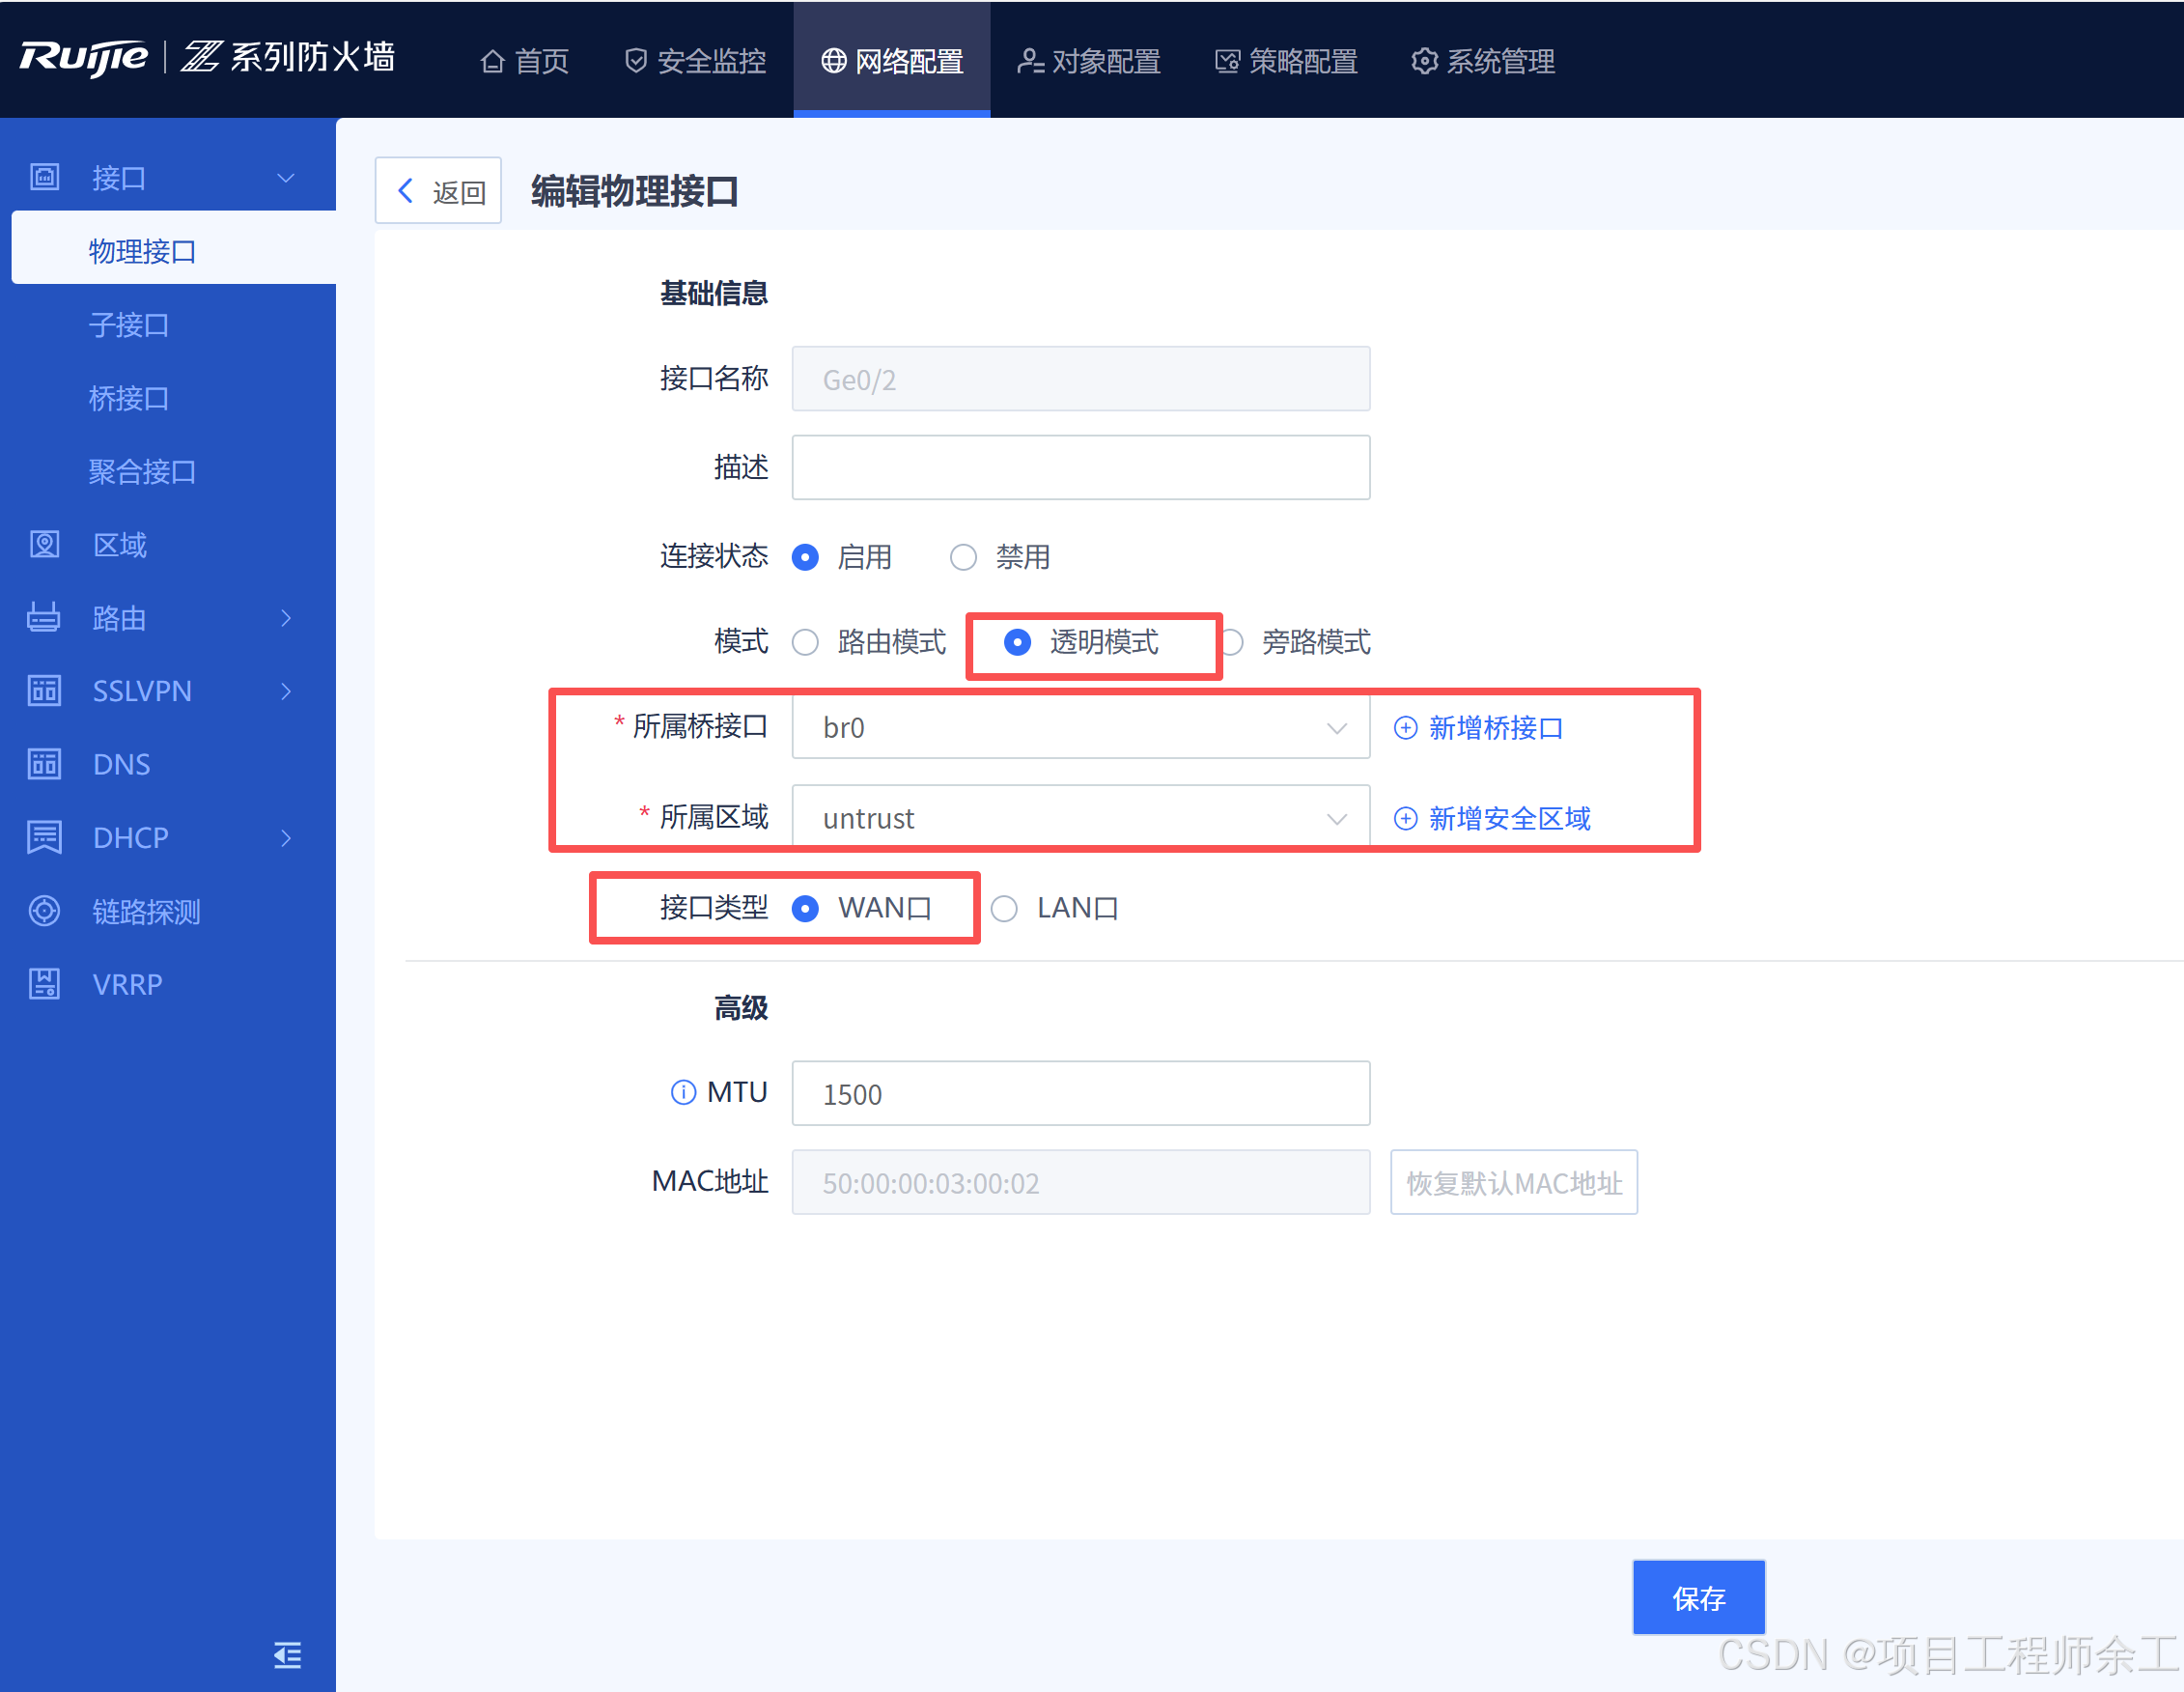
测试发现和华为防火墙一样ospf策略也是默认放行的
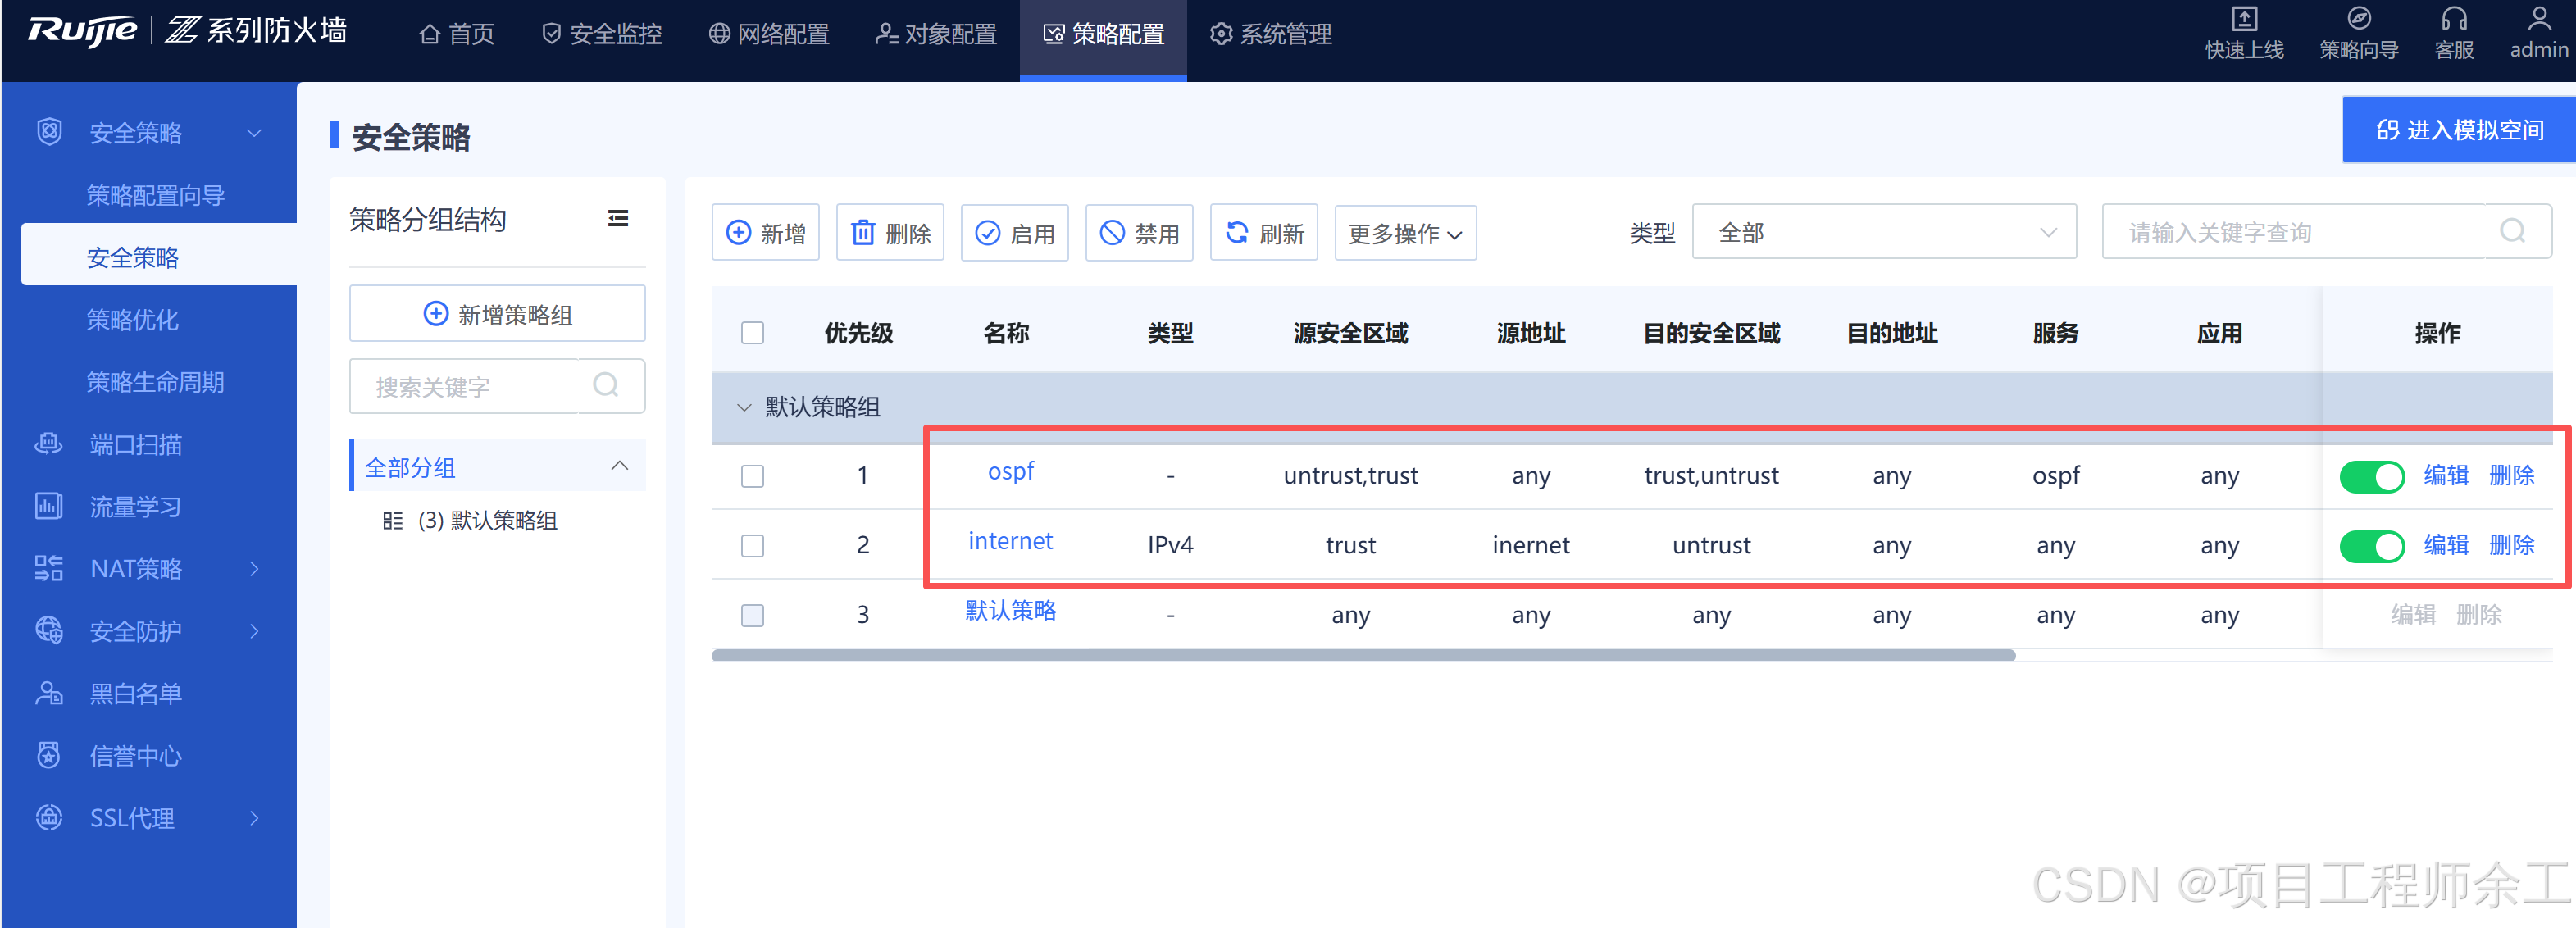
联通性测试