一、实验环境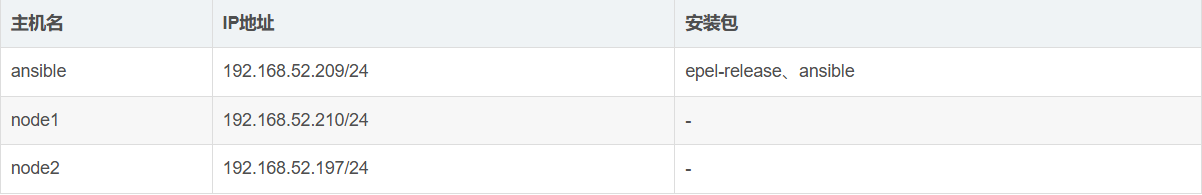
二、实验步骤
安装ansible
bash
[root@localhost ~]# hostnamectl set-hostname ansible
[root@localhost ~]# bash
[root@ansible ~]# yum install epel-release -y
[root@ansible ~]# yum install ansible -y
添加主机清单
bash
[root@ansible ~]# cd /etc/ansible/
[root@ansible ansible]# ls
ansible.cfg  hosts  roles
[root@ansible ansible]# vim hosts

[webservers]        ##添加到最后一行
192.168.52.209
192.168.52.197
配置公私钥
bash
[root@ansible ~]# ssh-keygen
Generating public/private rsa key pair.
Enter file in which to save the key (/root/.ssh/id_rsa):
Created directory '/root/.ssh'.
Enter passphrase (empty for no passphrase):
Enter same passphrase again:
Your identification has been saved in /root/.ssh/id_rsa.
Your public key has been saved in /root/.ssh/id_rsa.pub.
The key fingerprint is:
SHA256:LPYTI56Y4SDp+SC6GkYrMoXCx1PhftoIvs3AM6iwtc4 root@localhost.localdomain
The key's randomart image is:
+---[RSA 2048]----+
|     .           |
|    . .          |
|     o           |
|.o. o  .         |
|=oo=..+.S        |
|+oBoo*== o       |
|BB.*+oo.o        |
|O*o.B    .       |
|BoEo o           |
+----[SHA256]-----+
[root@ansible ~]# ssh-copy-id root@192.168.52.210
/usr/bin/ssh-copy-id: INFO: Source of key(s) to be installed: "/root/.ssh/id_rsa.pub"
The authenticity of host '192.168.52.210 (192.168.52.210)' can't be established.
ECDSA key fingerprint is SHA256:nryK+/NCYC3BMKWWs5x2gbYTOXHh1XQfrA1hIak57bQ.
ECDSA key fingerprint is MD5:b4:f5:03:a7:f0:2c:48:5e:c8:26:b0:eb:c2:c3:37:45.
Are you sure you want to continue connecting (yes/no)? yes
/usr/bin/ssh-copy-id: INFO: attempting to log in with the new key(s), to filter out any that are already installed
/usr/bin/ssh-copy-id: INFO: 1 key(s) remain to be installed -- if you are prompted now it is to install the new keys
root@192.168.115.109's password:
Number of key(s) added: 1
Now try logging into the machine, with:   "ssh 'root@192.168.52.210'"
and check to make sure that only the key(s) you wanted were added.
[root@ansible ~]# ssh-copy-id root@192.168.52.210
/usr/bin/ssh-copy-id: INFO: Source of key(s) to be installed: "/root/.ssh/id_rsa.pub"
The authenticity of host '192.168.52.210 (192.168.52.210)' can't be established.
ECDSA key fingerprint is SHA256:Nc4WQ6E4MwaQD/67ALzZ36hjNRigxQSUiDa2ZP5ZT+o.
ECDSA key fingerprint is MD5:f7:33:08:60:92:d5:99:2c:9e:fe:47:5a:63:c8:e5:a8.
Are you sure you want to continue connecting (yes/no)? yes
/usr/bin/ssh-copy-id: INFO: attempting to log in with the new key(s), to filter out any that are already installed
/usr/bin/ssh-copy-id: INFO: 1 key(s) remain to be installed -- if you are prompted now it is to install the new keys
root@192.168.52.210's password:
Number of key(s) added: 1
Now try logging into the machine, with:   "ssh 'root@192.168.52.210'"
and check to make sure that only the key(s) you wanted were added.
下载Nginx源码
-
使用
get_url模块从Nginx官网下载源码包到目标主机的临时目录(如/tmp)。bash- name: download nginx get_url: url: "http://nginx.org/download/nginx-1.18.0.tar.gz" # 可替换为最新版本URL dest: /tmp/nginx-1.18.0.tar.gz # 指定下载路径
此步骤确保源码包被安全下载
安装编译依赖包
使用yum模块安装必需的工具链,包括编译器(gcc)和库(openssl-devel、pcre-devel)。
bash
- name: install gcc and dependencies
  yum:
    name: "{{ packages }}"
    state: present
  vars:
    packages:
      - openssl-devel
      - pcre-devel
      - gcc
解压源码包
使用shell模块解压下载的源码包到临时目录。
bash
- name: extract nginx tarball
  shell: |
    cd /tmp
tar -xf nginx-1.18.0.tar.gz解压后源码位于/tmp/nginx-1.18.0
创建Nginx系统用户
为安全运行Nginx,使用user模块创建专用用户(无登录权限)
bash
- name: create nginx user
  user:
    name: nginx
    state: present
    shell: /sbin/nologin  # 禁止登录
编译并安装Nginx
使用shell模块执行configure、make和make install。此处添加常用编译选项(如状态模块)
bash
- name: compile and install nginx
  shell: |
    cd /tmp/nginx-1.18.0
    ./configure \
      --prefix=/usr/local/nginx \
      --user=nginx \
      --group=nginx \
      --with-http_stub_status_module  # 启用状态监控
    make
make install此步骤将Nginx安装到/usr/local/nginx
配置Systemd服务
创建systemd服务文件(确保Nginx开机自启),使用copy模块生成文件
bash
- name: create nginx systemd service
  copy:
    dest: /etc/systemd/system/nginx.service  # 服务文件路径
    content: |
      [Unit]
      Description=The nginx HTTP and reverse proxy server
      After=network.target
      [Service]
      Type=forking
      ExecStart=/usr/local/nginx/sbin/nginx  # 启动命令
      ExecReload=/usr/local/nginx/sbin/nginx -s reload
      ExecStop=/usr/local/nginx/sbin/nginx -s quit
      PrivateTmp=true
      [Install]
      WantedBy=multi-user.target
启用并启动Nginx服务
重载systemd配置,并启用服务。
bash
- name: reload systemd daemon
  command: systemctl daemon-reload
  become: yes  # 需要root权限
- name: enable and start nginx
  service:
    name: nginx
    state: started
    enabled: yes
三、创建playbook
创建剧本
bash
vim nginx.yaml添加
bash
- hosts: webservers  # 目标主机组,需在Ansible清单中定义
  become: yes  # 使用root权限
  tasks:
    - name: download nginx
      get_url:
        url: "http://nginx.org/download/nginx-1.18.0.tar.gz"
        dest: /tmp/nginx-1.18.0.tar.gz

    - name: install gcc and dependencies
      yum:
        name: "{{ packages }}"
        state: present
      vars:
        packages:
          - openssl-devel
          - pcre-devel
          - gcc

    - name: extract nginx tarball
      shell: |
        cd /tmp
        tar -xf nginx-1.18.0.tar.gz

    - name: create nginx user
      user:
        name: nginx
        state: present
        shell: /sbin/nologin

    - name: compile and install nginx
      shell: |
        cd /tmp/nginx-1.18.0
        ./configure \
          --prefix=/usr/local/nginx \
          --user=nginx \
          --group=nginx \
          --with-http_stub_status_module
        make
        make install

    - name: create nginx systemd service
      copy:
        dest: /etc/systemd/system/nginx.service
        content: |
          [Unit]
          Description=The nginx HTTP and reverse proxy server
          After=network.target
          [Service]
          Type=forking
          ExecStart=/usr/local/nginx/sbin/nginx
          ExecReload=/usr/local/nginx/sbin/nginx -s reload
          ExecStop=/usr/local/nginx/sbin/nginx -s quit
          PrivateTmp=true
          [Install]
          WantedBy=multi-user.target

    - name: reload systemd daemon
      command: systemctl daemon-reload

    - name: enable and start nginx
      service:
        name: nginx
        state: started
        enabled: yes