CTF类题目复现总结-hashcat 1

一、题目地址

matlab 复制代码
https://buuoj.cn/challenges#hashcat

二、复现步骤

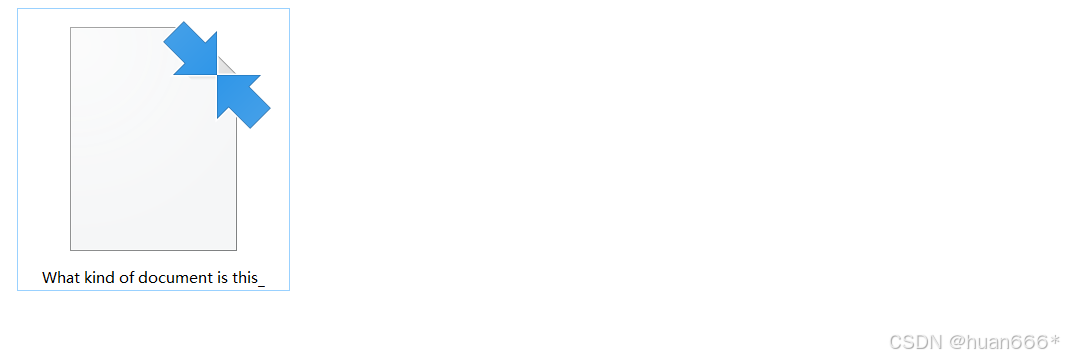
1、下载附件,解压得到What kind of document is this_文件;
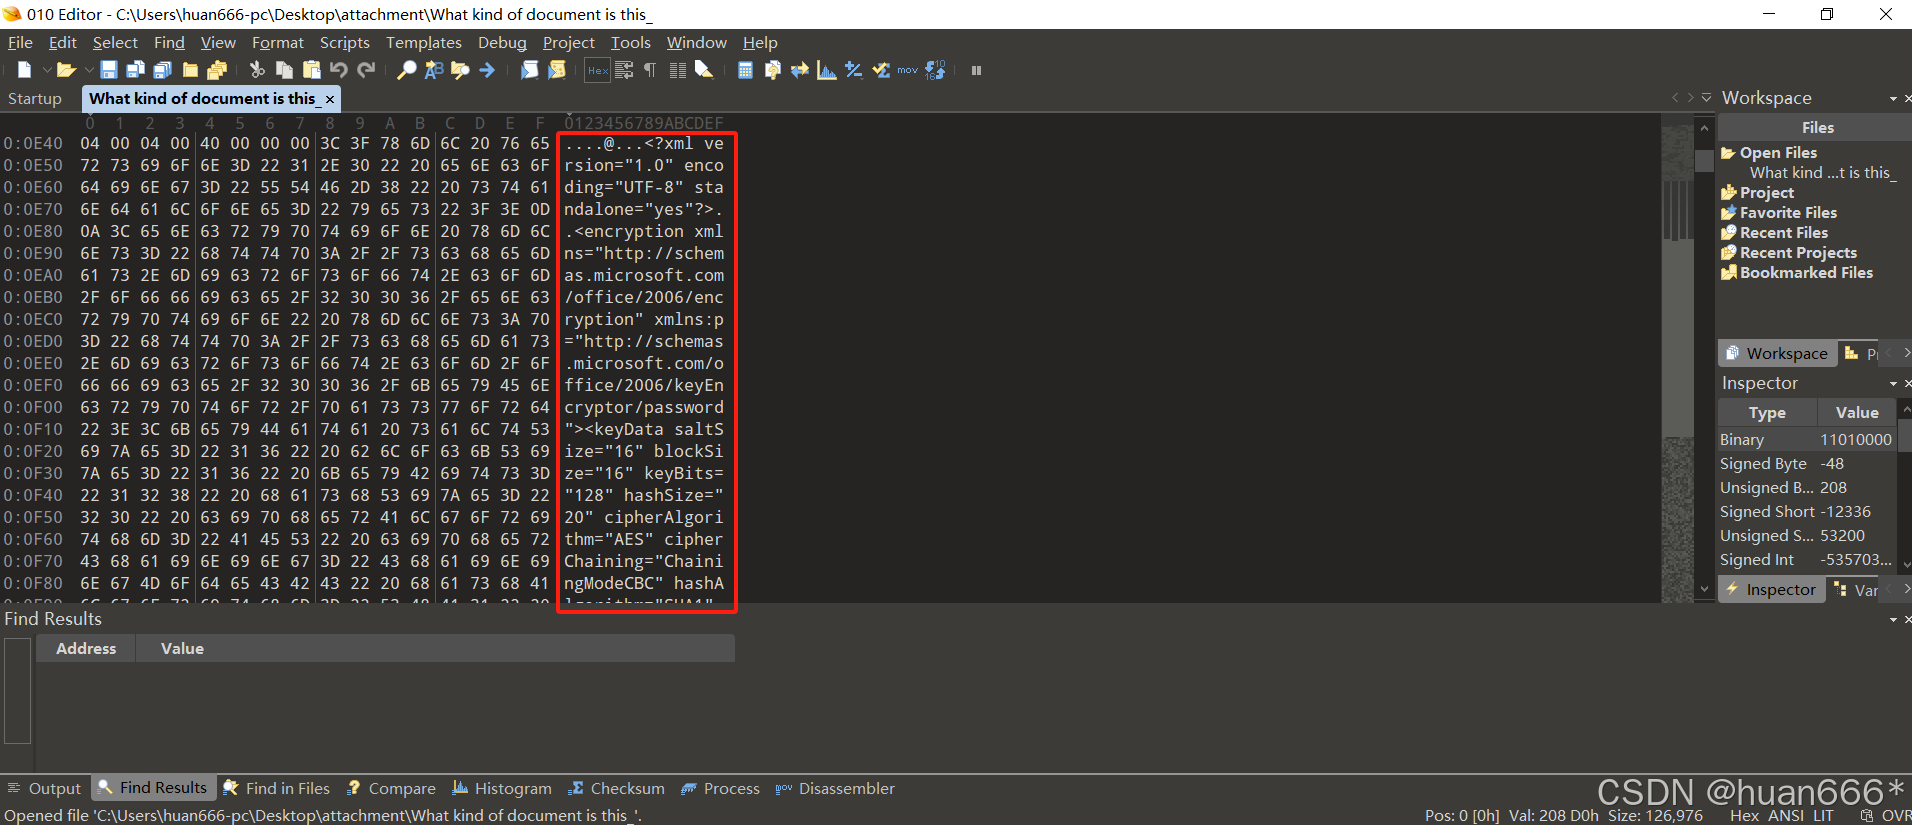
2、用010 Editor打开What kind of document is this_文件,发现是office文件;
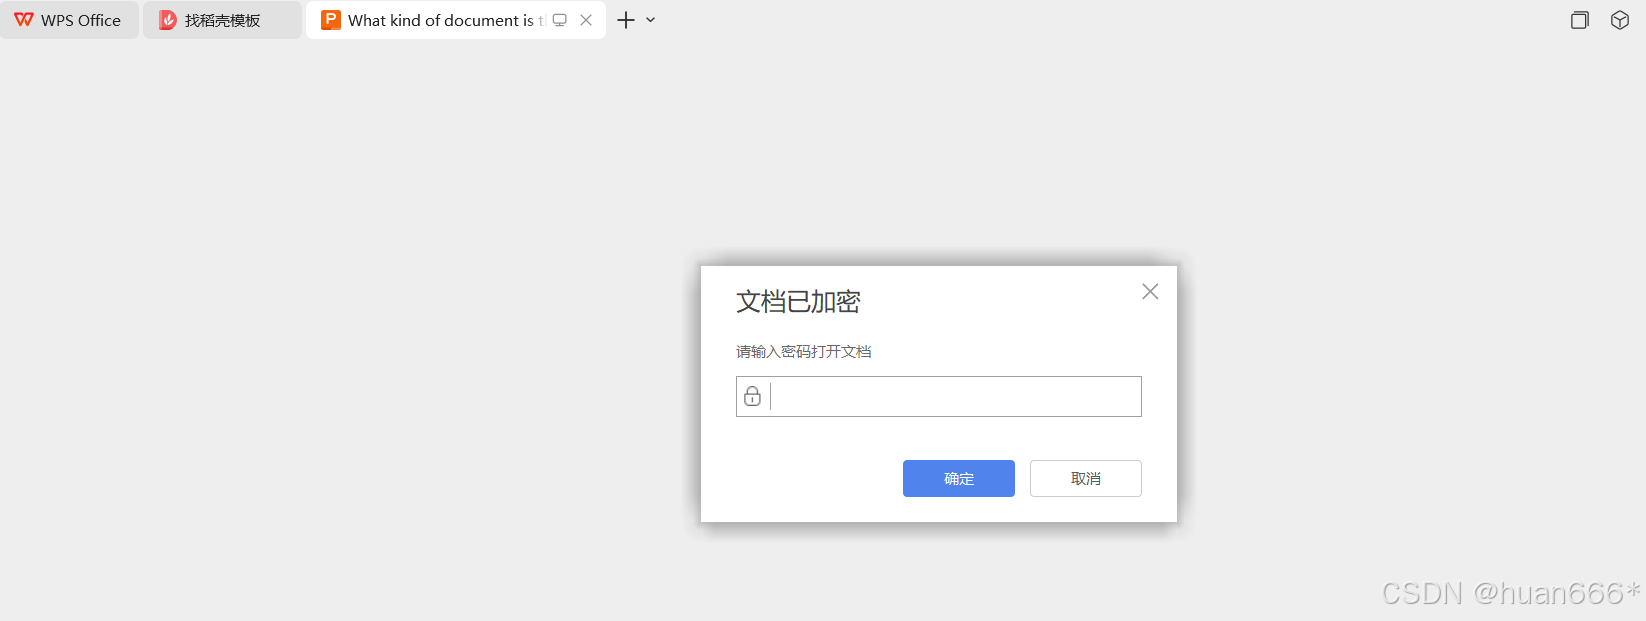
3、将后缀名改为ppt时,能打开,但是需要密码;
4、通过破解得到密码为 9919,详细破解方法参考:密码学专栏-->利用john crack 文档密码 ;

5、利用密码成功打开ppt文件,在第七页,将字体改为红色,得到flag;
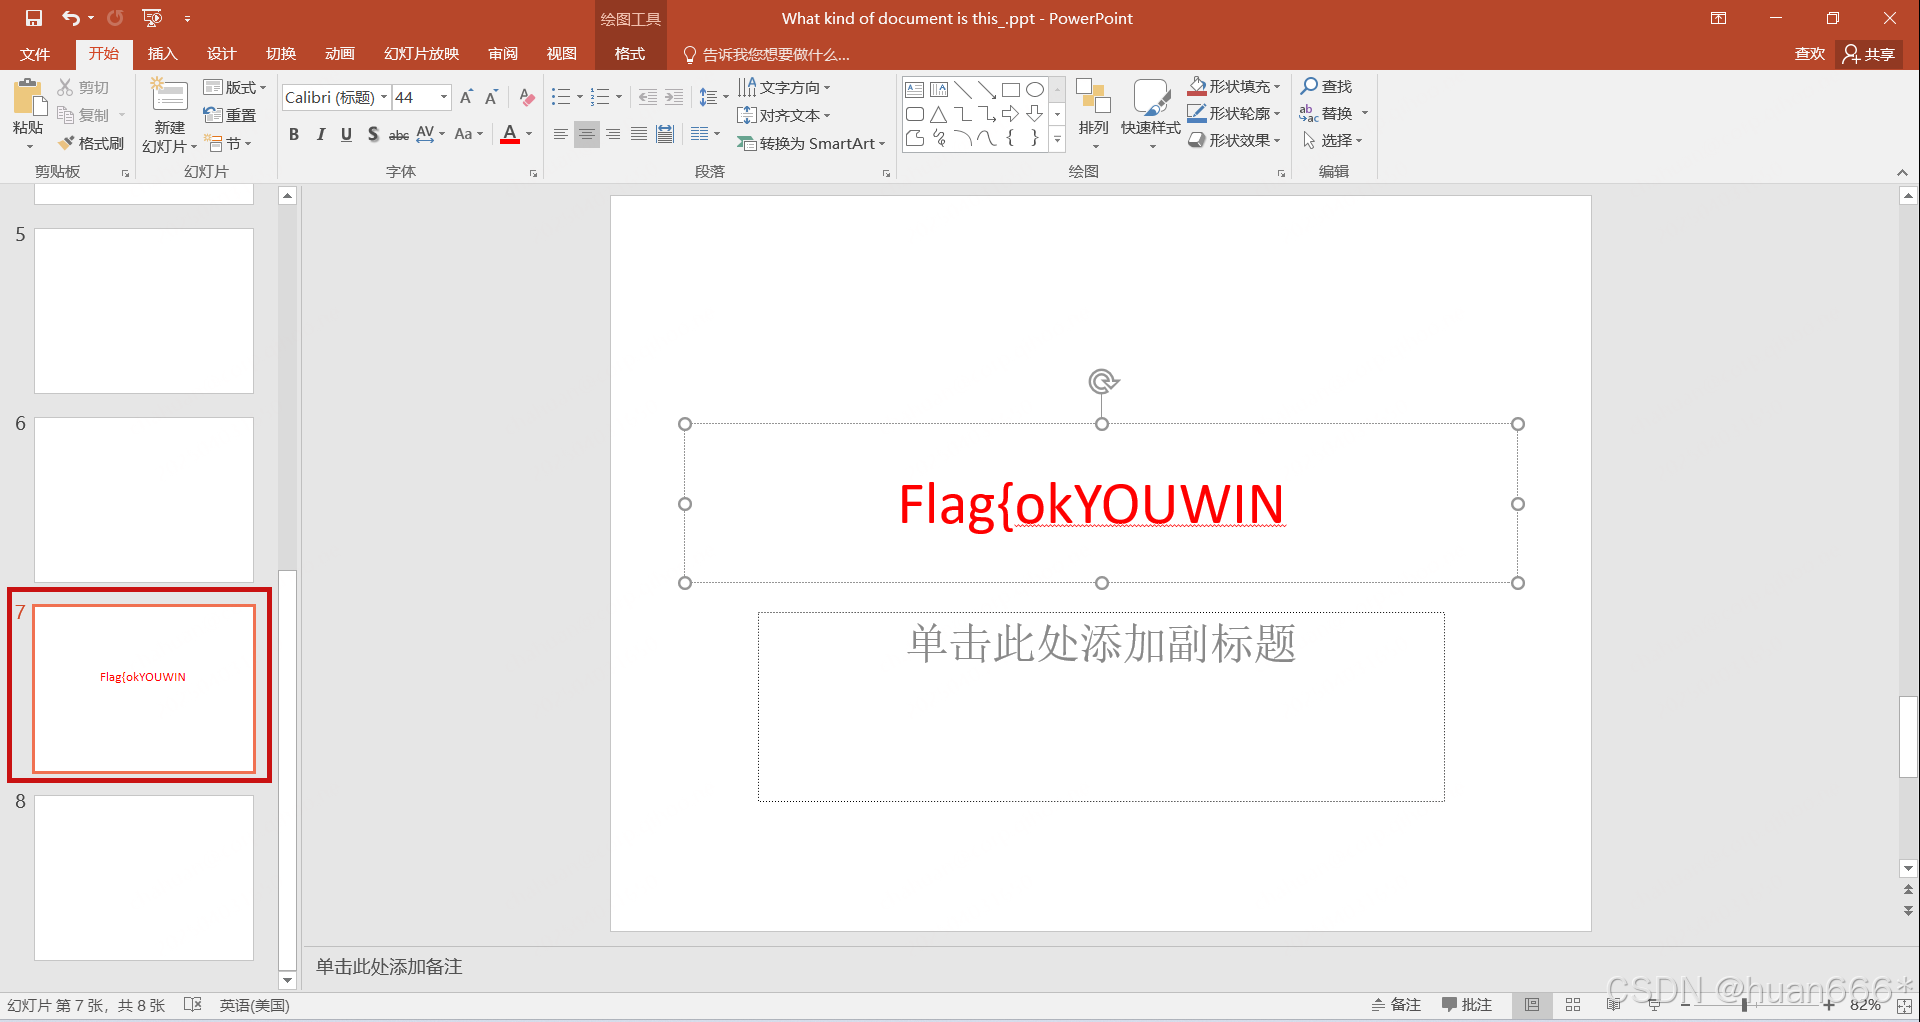
matlab 复制代码
flag{okYOUWIN}
相关推荐
kingx38 小时前
Bugku 326 Baby-heap1 题解:glibc 2.23 堆溢出到 FSOP 劫持 _IO_list_all(附完整 exp)
pwn·ctf·glibc·堆溢出·fsop
hengdonghui1 天前
Writeup 4 0xGame 2021 · command (WEB)
web·ctf·rce(远程代码执行)
0xBADCODE1 天前
2026 强网杯 Web 题 cwp · 全链路复盘
前端·安全·web安全·网络安全·系统安全·ctf
kingx34 天前
Bugku WEB 题解总集:文件包含 / SQLi / 反序列化 / SSTI / 反爬 / 组件漏洞
web安全·网络安全·ctf·bugku
kingx34 天前
Bugku Reverse 与 Android 题解总集:APK / native / PE / IPA
android·逆向·ctf·bugku
hengdonghui9 天前
Writeup 4 NUAACTF 2020 Wireshark 流量分析题
wireshark·ctf·misc·流量分析
hengdonghui10 天前
Writeup 4 0xGame 2021 - robot
web·ctf·信息泄露·robots.txt
hengdonghui13 天前
Writeup 4 Speak Softly Love
ctf·misc·osint(开源情报搜集)
其实防守也摸鱼15 天前
Cylab在线靶场——CTF中的通用技能
linux·数据库·学习·算法·靶场·ctf·学习网络安全
hengdonghui17 天前
Writeup 4 CTFHub injection
web·ctf·sql注入·整数型联合查询注入(有回显)