Conference:Network and Distributed System Security Symposium (NDSS)
CCF level:CCF A
Year:2026
Title:
CtPhishCapture: Uncovering Credential-Theft-Based Phishing Scams Targeting Cryptocurrency Wallets
CtPhishCapture:揭露针对加密货币钱包的基于凭证窃取的网络钓鱼诈骗
Authors:****
Abstract:****
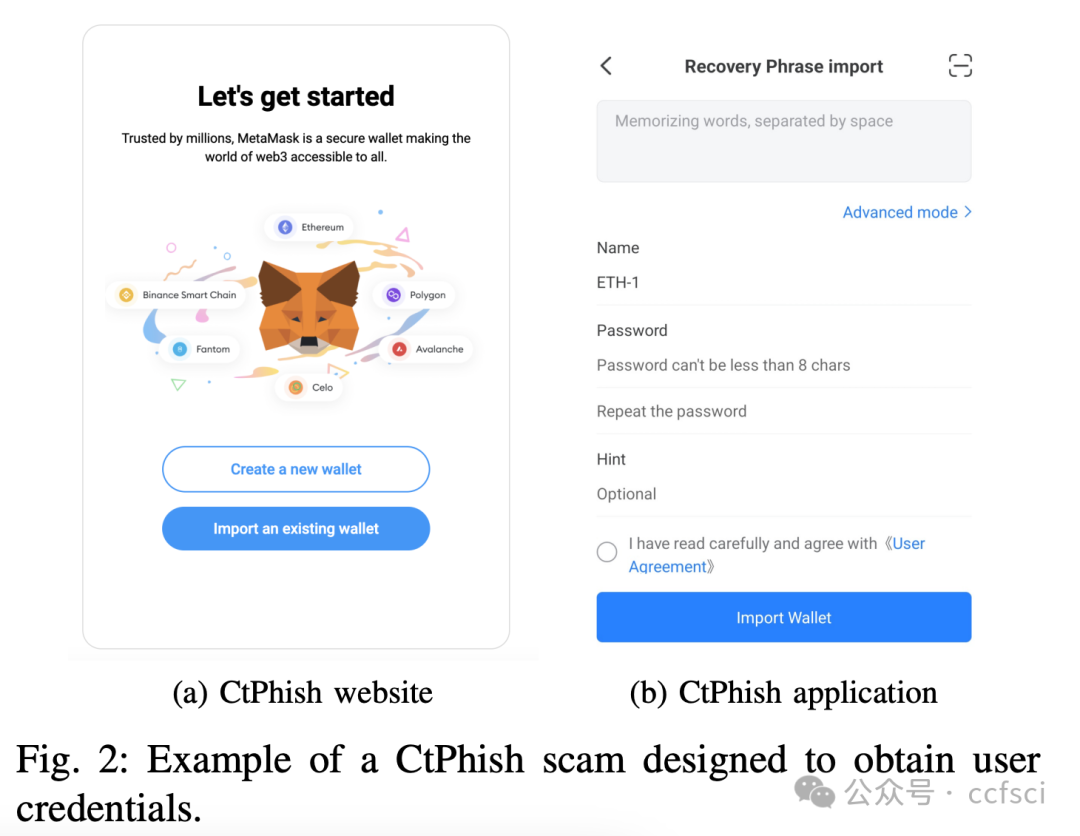
Due to the substantial financial incentives involved, credential-theft-based cryptocurrency wallet phishing (CtPhish) scams have emerged as one of the most prevalent malicious activities in the cryptocurrency ecosystem. In these attacks, victims are lured into visiting CtPhish websites or applications and deceived into disclosing their credentials, allowing attackers to steal their cryptocurrency assets. Although several phishing detection approaches exist, they are either inapplicable to CtPhish or suffer from significant limitations.
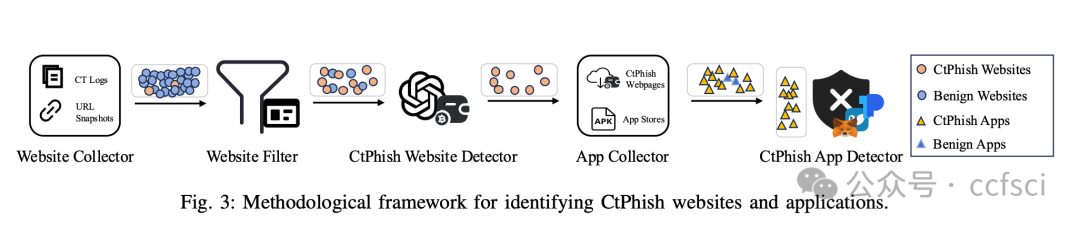
To bridge this gap, we propose CtPhishCapture, a large-scale detection system targeting CtPhish websites and applications. CtPhishCapture visits suspicious websites, employs large language model (LLM)-based detection methods to identify CtPhish websites, and attempts to download and analyze potential CtPhish applications for further detection. Over a six-month deployment, CtPhishCapture identifies 5,138 CtPhish websites and 10,612 CtPhish applications. Notably, only 17% of the websites and 21% of the applications were previously reported by the community, indicating that CtPhishCapture newly discovers 83% of the websites and 79% of the applications, making it the largest known detection system for CtPhish to date.
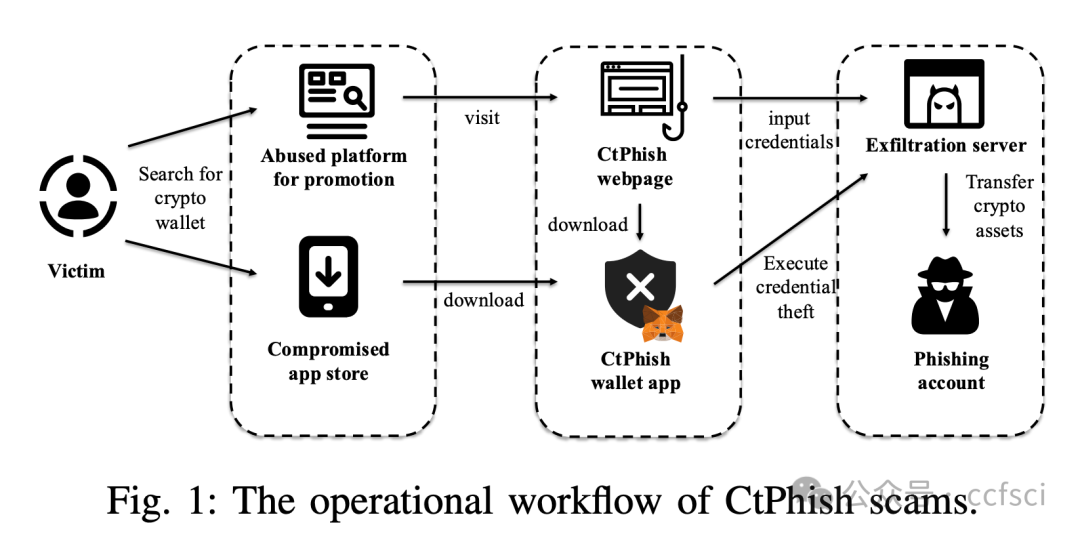
Leveraging the collected dataset, we conduct a comprehensive end-to-end measurement and analysis of the CtPhish ecosystem. Our analysis examines how attackers attract victims to CtPhish websites and apps, how they gain users' trust, and ultimately how they exfiltrate victims' cryptocurrency assets. Additionally, we provide in-depth measurements of the associated websites and applications, including their characteristics, evasion techniques, and estimated financial losses. Finally, we deploy CtPhishCapture in collaboration with a leading search engine provider. By integrating CtPhishCapture's detection results, the weekly user complaints about CtPhish are reduced by a factor of 5.8.
由于涉及巨额经济利益,基于凭证窃取的加密货币钱包网络钓鱼(CtPhish)诈骗已成为加密货币生态系统中最普遍的恶意活动之一。在这些攻击中,受害者被诱骗访问 CtPhish 网站或应用程序,并被骗泄露凭证,从而使攻击者能够窃取其加密货币资产。尽管存在多种网络钓鱼检测方法,但它们要么不适用于 CtPhish,要么存在重大局限性。
为了弥补这一不足,我们提出了 CtPhishCapture,一个针对 CtPhish 网站和应用程序的大规模检测系统。CtPhishCapture 会访问可疑网站,采用基于大型语言模型(LLM)的检测方法来识别 CtPhish 网站,并尝试下载和分析潜在的 CtPhish 应用程序以进行进一步检测。在为期六个月的部署中,CtPhishCapture 识别出了 5,138 个 CtPhish 网站和 10,612 个 CtPhish 应用程序。值得注意的是,此前社区仅报告过 17% 的网站和 21% 的应用程序,这意味着 CtPhishCapture 首次发现了 83% 的网站和 79% 的应用程序,使其成为迄今为止已知最大的 CtPhish 检测系统。
利用收集到的数据集,我们对 CtPhish 生态系统进行了全面的端到端测量和分析。我们的分析考察了攻击者如何吸引受害者访问 CtPhish 网站和应用程序,如何获取用户信任,以及最终如何窃取受害者的加密货币资产。此外,我们还对相关的网站和应用程序进行了深入测量,包括它们的特征、规避技术和预估的经济损失。最后,我们与一家领先的搜索引擎提供商合作部署了 CtPhishCapture。通过整合 CtPhishCapture 的检测结果,每周用户对 CtPhish 的投诉减少了 5.8 倍。
Pdf:
https://www.ndss-symposium.org/wp-content/uploads/2026-f2854-paper.pdf