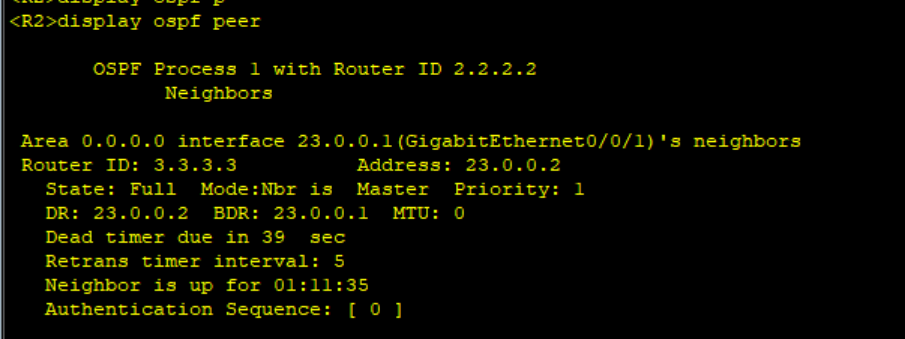
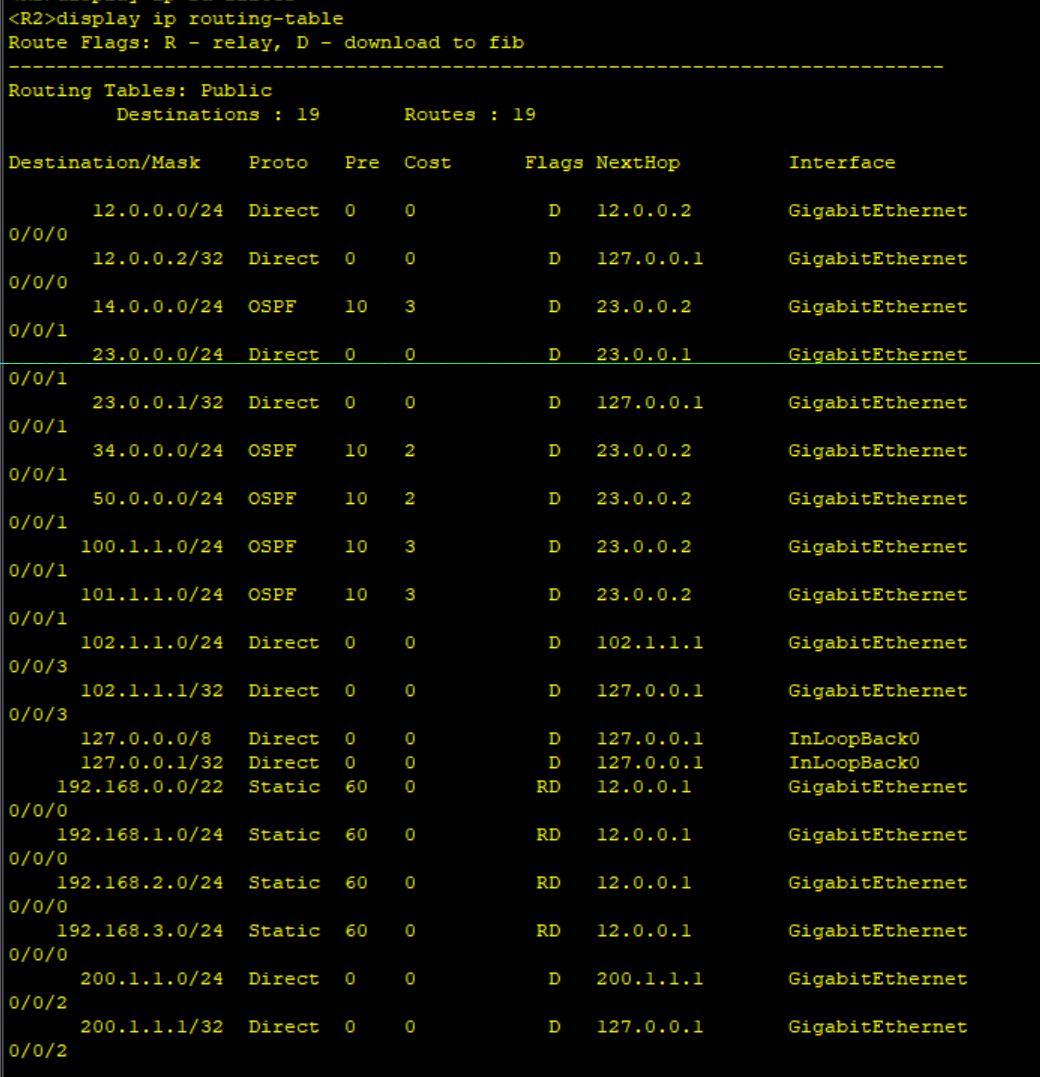
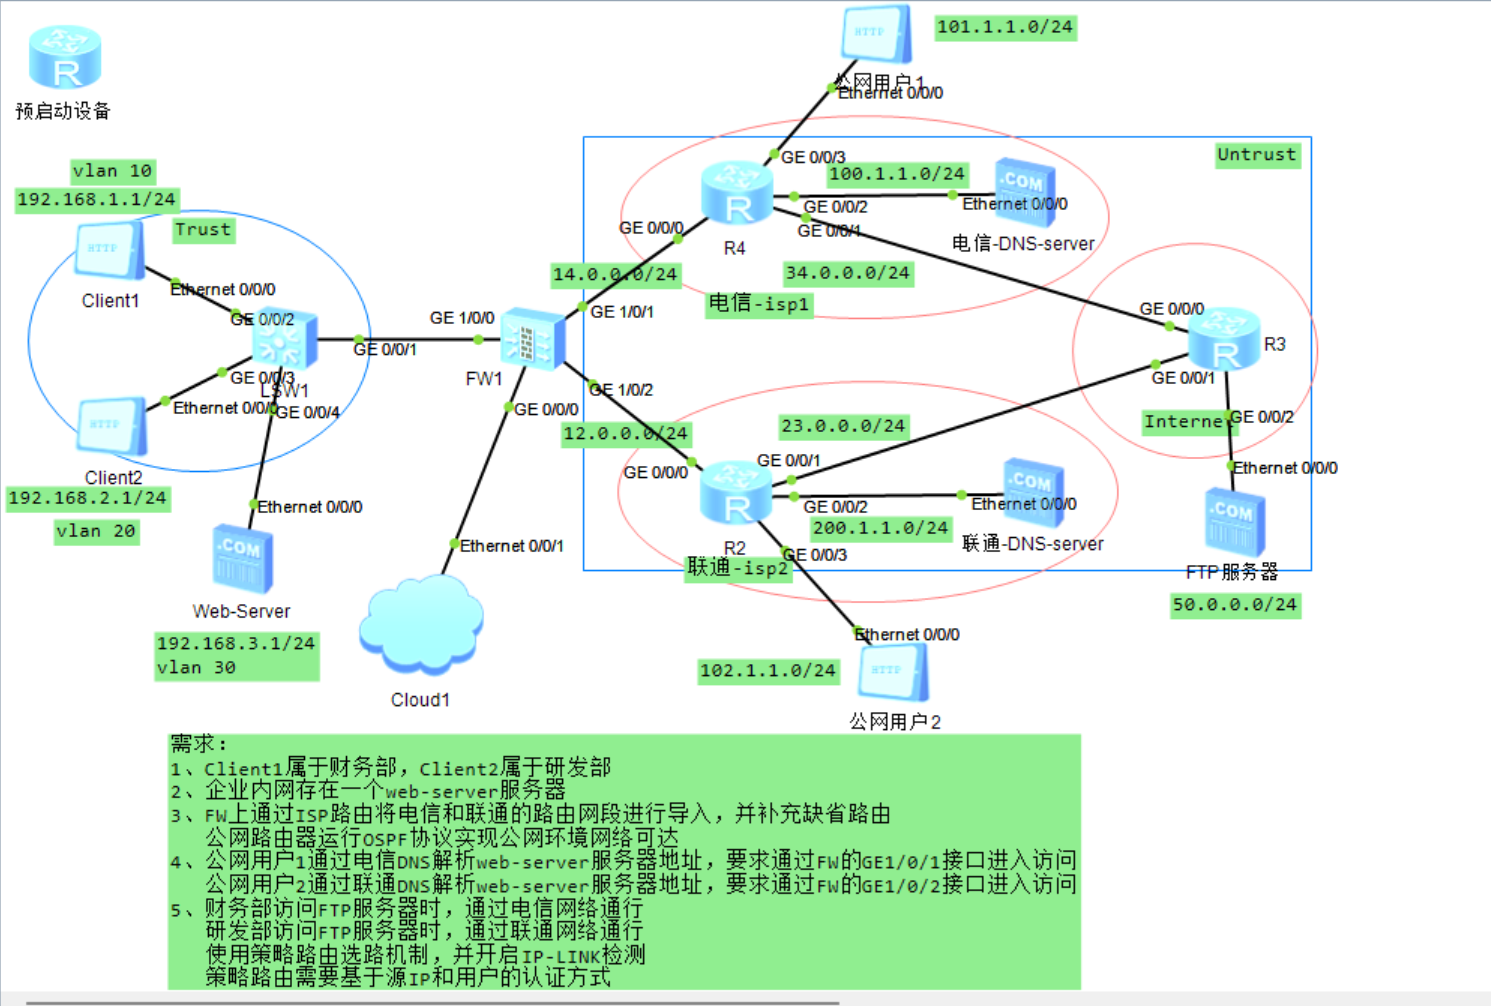
拓扑图及需求
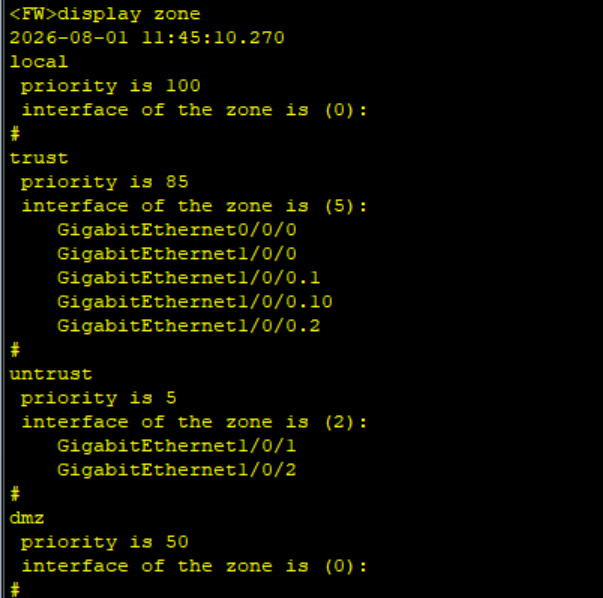
FW接口IP与安全区域配置
# ========== 子接口==========
interface GigabitEthernet1/0/0.10
 vlan-type dot1q 10
 ip address 192.168.1.254 255.255.255.0
 service-manage ping permit
#
interface GigabitEthernet1/0/0.1
 vlan-type dot1q 1
 ip address 192.168.2.254 255.255.255.0
 service-manage ping permit
#
interface GigabitEthernet1/0/0.2
 vlan-type dot1q 2
 ip address 192.168.3.254 255.255.255.0
 service-manage ping permit

# ========== 外网物理接口配置 ==========
interface GigabitEthernet1/0/1
 ip address 14.0.0.1 255.255.255.0
 service-manage ping permit
#
interface GigabitEthernet1/0/2
 ip address 12.0.0.1 255.255.255.0
 service-manage ping permit

# ========== 安全区域划分 ==========
firewall zone trust
 add interface GigabitEthernet1/0/0.10
 add interface GigabitEthernet1/0/0.1
 add interface GigabitEthernet1/0/0.2
#
firewall zone untrust
 add interface GigabitEthernet1/0/1
 add interface GigabitEthernet1/0/2
SW交换机VLAN与接口配置
# ========== 创建VLAN ==========
vlan batch 10 1 2

# ========== 连接FW的接口配置为Trunk ==========
interface GigabitEthernet0/0/1
 port link-type trunk
 port trunk allow-pass vlan 10 1 2

# ========== 连接Client1(财务部)的接口 ==========
interface GigabitEthernet0/0/2
 port link-type access
 port default vlan 10

# ========== 连接Client2(研发部)的接口 ==========
interface GigabitEthernet0/0/3
 port link-type access
 port default vlan 1

# ========== 连接Web-Server的接口 ==========
interface GigabitEthernet0/0/4
 port link-type access
 port default vlan 2
地址对象、用户组与认证配置
# ========== 地址对象(eNSP USG6000V语法)==========
address 财务部
 net-address 192.168.1.0 mask 24
#
address 研发部
 net-address 192.168.2.0 mask 24
#
address Web服务器
 host-address 192.168.3.10
#
address FTP服务器
 host-address 200.0.0.10

# ========== 用户组 ==========
user-group 财务部组
user-group 研发部组

# ========== 认证策略:财务部免认证,研发部匿名认证 ==========
authentication
 access-type free user-group 财务部组
 access-type anonymous user-group 研发部组
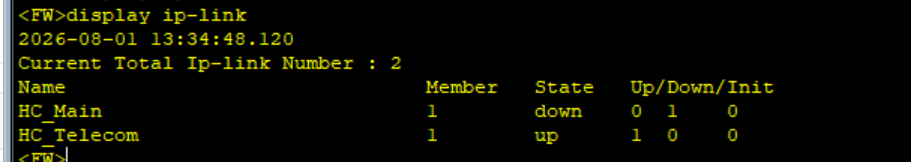
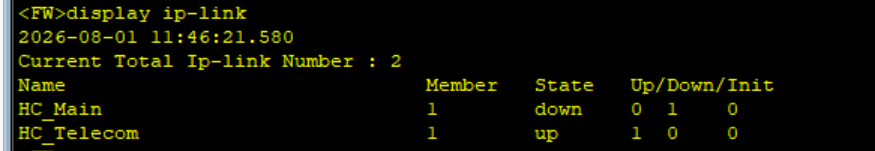
IP-Link链路探测配置
ip-link check enable
#
ip-link 1
 destination 14.0.0.2 interface GigabitEthernet1/0/1
#
ip-link 2
 destination 12.0.0.2 interface GigabitEthernet1/0/2
策略路由PBR配置
# ========== 定义ACL匹配不同部门访问FTP的流量 ==========
acl 3000
 rule 5 permit ip source 192.168.1.0 0.0.0.255 destination 200.0.0.10 0
#
acl 3001
 rule 5 permit ip source 192.168.2.0 0.0.0.255 destination 200.0.0.10 0

# ========== 定义流分类(匹配ACL)==========
traffic classifier finance_ftp
 if-match acl 3000
#
traffic classifier rd_ftp
 if-match acl 3001

# ========== 定义流行为(重定向下一跳+IP-Link联动)==========
traffic behavior to_telecom
 redirect ip-nexthop 14.0.0.2 track ip-link 1
#
traffic behavior to_unicom
 redirect ip-nexthop 12.0.0.2 track ip-link 2

# ========== 定义流策略(绑定分类与行为)==========
traffic policy PBR
 classifier finance_ftp behavior to_telecom
 classifier rd_ftp behavior to_unicom

# ========== 在内网子接口入方向应用策略路由 ==========
interface GigabitEthernet1/0/0.10
 traffic-policy PBR inbound
#
interface GigabitEthernet1/0/0.1
 traffic-policy PBR inbound
NAT策略配置
# ========== 内网Easy-IP源NAT(出站)==========
nat-policy
 rule name trust_to_internet
  source-zone trust
  destination-zone untrust
  action source-nat easy-ip

# ========== NAT Server外网发布Web服务器(双线映射)==========
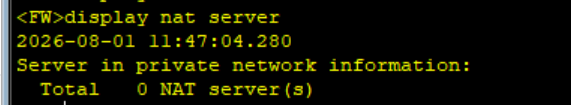
nat server Web_tele protocol tcp global 14.0.0.100 www inside 192.168.3.10 www
nat server Web_unicom protocol tcp global 12.0.0.100 www inside 192.168.3.10 www
路由配置
# ========== 导入电信、联通ISP网段明细路由 ==========
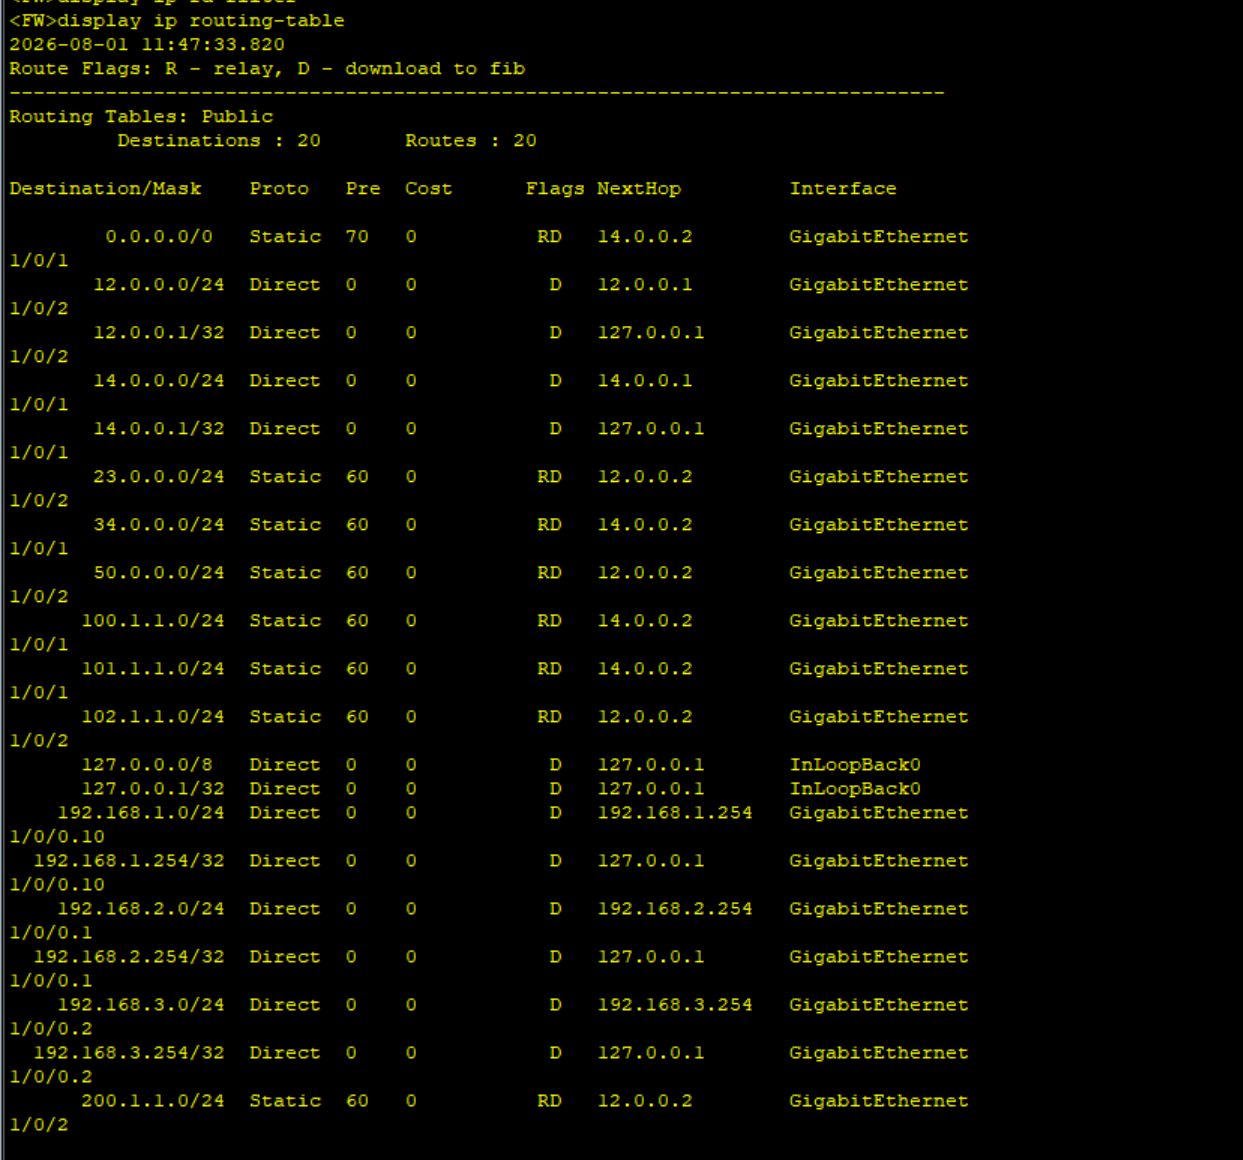
ip route-static 101.1.1.0 255.255.255.0 14.0.0.2
ip route-static 102.1.1.0 255.255.255.0 12.0.0.2

# ========== 双线缺省路由(主备模式 + IP-Link联动)==========
ip route-static 0.0.0.0 0.0.0.0 14.0.0.2 preference 70 track ip-link 1
ip route-static 0.0.0.0 0.0.0.0 12.0.0.2 preference 80
精准安全策略配置
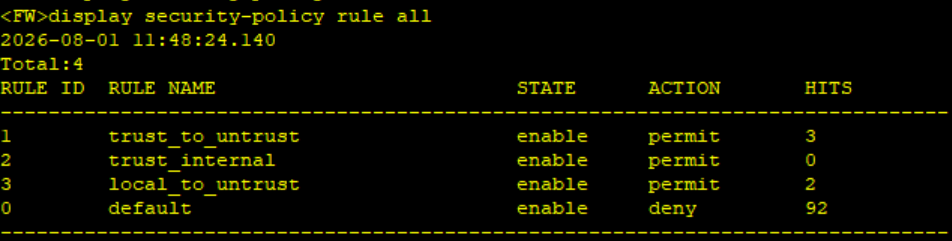
security-policy
 rule name finance_internet
  source-zone trust
  source-address 192.168.1.0 24
  destination-zone untrust
  action permit
#
 rule name rd_internet
  source-zone trust
  source-address 192.168.2.0 24
  destination-zone untrust
  authentication user-group 研发部组
  action permit
#
 rule name internet_to_web
  source-zone untrust
  destination-zone trust
  destination-address 192.168.3.10 32
  service http
  action permit
#
 rule name local_to_untrust
  source-zone local
  destination-zone untrust
  service icmp
  action permit
#
 rule name trust_internal
  source-zone trust
  destination-zone trust
  action permit
R4电信路由器完整配置
# ========== 接口IP配置 ==========
interface GigabitEthernet0/0/0
 ip address 14.0.0.2 255.255.255.0
 description TO-FW-GE1/0/1
#
interface GigabitEthernet0/0/1
 ip address 200.0.0.1 255.255.255.0
 description TO-公网FTP服务器方向
#
interface LoopBack0
 ip address 101.1.1.1 255.255.255.0
 description 电信ISP网段

# ========== OSPF协议配置 ==========
ospf 1 router-id 4.4.4.4
 area 0.0.0.0
  network 14.0.0.0 0.0.0.255
  network 101.1.1.0 0.0.0.255
  network 200.0.0.0 0.0.0.255

# ========== 回程路由指向内网 ==========
ip route-static 192.168.0.0 255.255.252.0 14.0.0.1
R2联通路由器完整配置
# ========== 接口IP配置 ==========
interface GigabitEthernet0/0/0
 ip address 12.0.0.2 255.255.255.0
 description TO-FW-GE1/0/2
#
interface GigabitEthernet0/0/1
 ip address 200.0.0.2 255.255.255.0
 description TO-公网FTP服务器方向
#
interface LoopBack0
 ip address 102.1.1.1 255.255.255.0
 description 联通ISP网段

# ========== OSPF协议配置 ==========
ospf 1 router-id 2.2.2.2
 area 0.0.0.0
  network 12.0.0.0 0.0.0.255
  network 102.1.1.0 0.0.0.255
  network 200.0.0.0 0.0.0.255

# ========== 回程路由指向内网 ==========
ip route-static 192.168.0.0 255.255.252.0 12.0.0.1
测试