1、实验目的
通过本实验可以掌握:
- IPv4 ACL工作方式和工作过程
- 定义编号和命名的标准IPv4 ACL的方法
- 接口和VTY下应用标准IPv4 ACL的方法
2、实验拓扑
配置IPv4 ACL的实验拓扑如图9-2所示
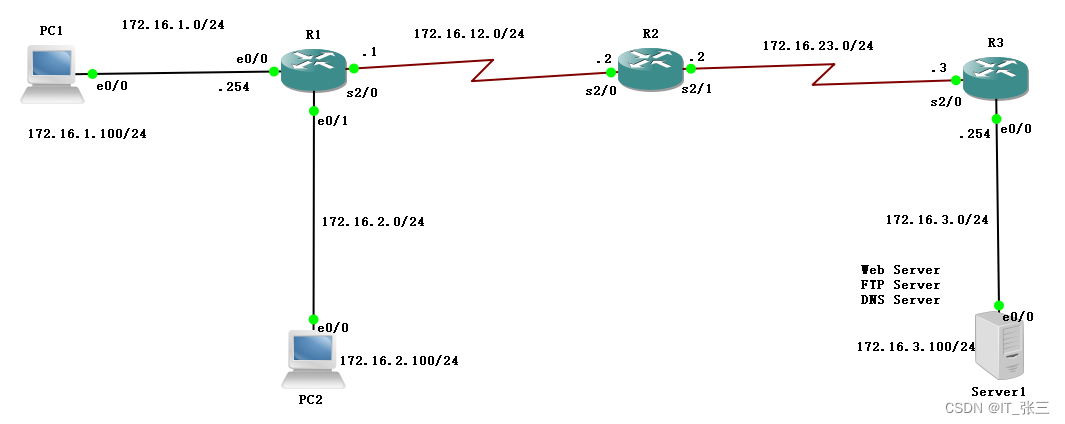
配置 ACL 实验拓扑如下图所示。本实验中,通过配置标准 ACL 实现拒绝 PC2 所在网段访问 Server1,同时只允许主机 PC1 访问路由器 R1、R2 和 R3 的 Telnet 服务,实现对路由器进行远程管理。整个网络配置RIPv2路由协议保证 IP 的连通性。
3、实验步骤
(1)配置路由器R1
R1(config)#router rip
R1(config-router)#version 2
R1(config-router)#no auto-summary
R1(config-router)#network 172.16.0.0
R1(config-router)#passive-interface ethernet 0/0
R1(config-router)#passive-interface ethernet 0/1
R1(config-router)#exit
R1(config)#access-list 2 remark ONLY HOST PC CAN TELNET
R1(config)#access-list 2 permit host 172.16.1.100
R1(config)#line vty 0 4
R1(config-line)#access-class 2 in
R1(config-line)#password cisco123
R1(config-line)#privilege level 15
R1(config-line)#login
R1(config-line)#exit
(2)配置路由器R2
R2(config)#router rip
R2(config-router)#version 2
R2(config-router)#no auto-summary
R2(config-router)#network 172.16.0.0
R2(config-router)#exit
R2(config)#access-list 2 remark ONLY HOST PC1 CAN TELENT
R2(config)#access-list 2 permit host 172.16.1.100
R2(config)#line vty 0 4
R2(config-line)#access-class 2 in
R2(config-line)#password cisco
R2(config-line)#privilege level 15
R2(config-line)#login
R2(config-line)#exit
(3)配置路由器R3
R3(config)#router rip
R3(config-router)#version 2
R3(config-router)#no auto-summary
R3(config-router)#network 172.16.0.0
R3(config-router)#passive-interface ethernet 0/0
R3(config-router)#exit
R3(config)#access-list 2 remark ONLY HOST PC1 CAN TELENT
R3(config)#access-list 2 permit host 172.16.1.100
R3(config)#access-list 1 remark DENY NETWORK 172.16.2.0 FROM R1
R3(config)#access-list 1 deny 172.16.2.0 0.0.0.255 log
R3(config)#access-list 1 permit any
R3(config)#interface ethernet 0/0
R3(config-if)#ip access-group 1 out
R3(config-if)#exit
R3(config)#line vty 0 4
R3(config-line)#access-class 2 in
R3(config-line)#password cisco
R3(config-line)#privilege level 15
R3(config-line)#login
R3(config-line)#exit
4、实验调试
(1)Telent测试
除了PC1主机上Telnet路由器的各个接口地址可以成功外,以其它地址为源Telnet各个路由器都不能成功,显示如如下
% Connection refused by remote host(2)ping测试
在路由器R1上ping主机172.16.3.100,结果如下
R1#ping 172.16.3.100
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 172.16.3.100, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 18/19/20 ms
##以上输出表明使用标准ping命令,可以ping通,因为标准ping命令是以路由器R1的s2/1接口发出的,没有被R3上的IPv4 ACL拒绝
R1#ping 172.16.3.100 source 172.16.1.254
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 172.16.3.100, timeout is 2 seconds:
Packet sent with a source address of 172.16.1.254
UUUU
(3)查看定义的IPv4 ACL及流量匹配情况
R3#show ip access-lists
Standard IP access list 1
    10 deny   172.16.2.0, wildcard bits 0.0.0.255 log
    20 permit any (10 matches)
Standard IP access list 2
    10 permit 172.16.1.100
(4)查看IPv4 ACL应用情况
R3#show ip interface ethernet 0/0
Ethernet0/0 is up, line protocol is up
  Internet address is 172.16.3.254/24
  Broadcast address is 255.255.255.255