一.Nginx的源码编译
1.下载软件
bash
[root@Nginx ~] wget https://nginx.org/download/nginx-1.28.1.tar.gz2.解压
bash
[root@Nginx ~] tar zxf nginx-1.28.1.tar.gz
[root@Nginx ~] cd nginx-1.28.1/
[root@Nginx nginx-1.28.1] ls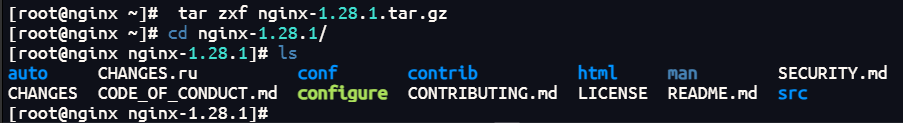
3.检测环境
bash
#安装依赖性
[root@Nginx ~] dnf install gcc openssl-devel.x86_64 pcre2-devel.x86_64 zlib-devel -y

[root@Nginx nginx-1.28.1] ./configure --prefix=/usr/local/nginx --user=nginx --group=nginx --with-http_ssl_module --with-http_v2_module --with-http_realip_module --with-http_stub_status_module --with-http_gzip_static_module --with-pcre --with-stream --with-stream_ssl_module --with-stream_realip_module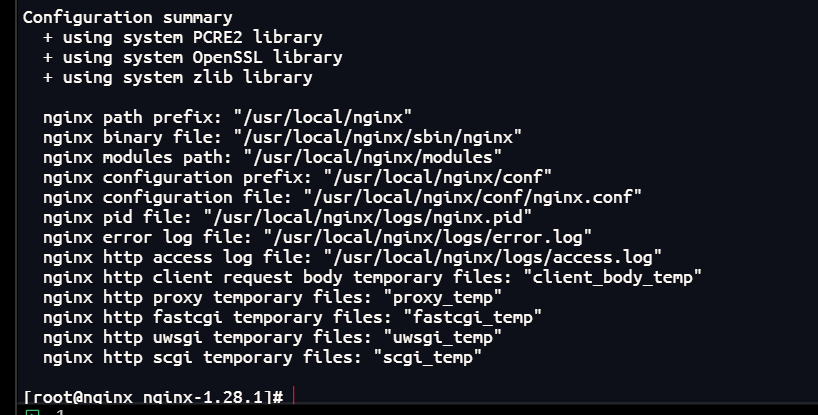
4.编译
bash
[root@Nginx nginx-1.28.1] make
[root@Nginx nginx-1.28.1] make install
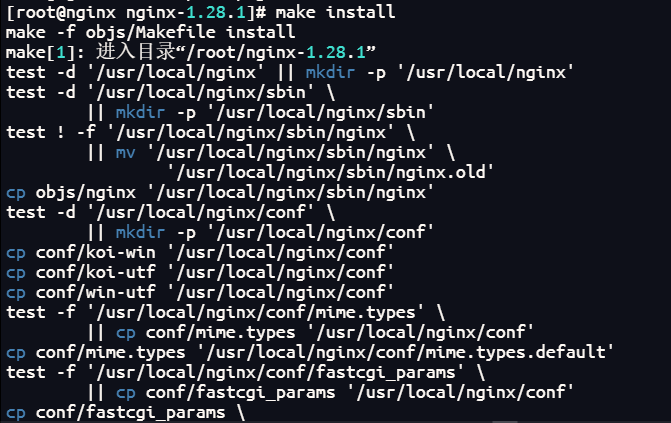
5.nginx启动
bash
#设定环境变量
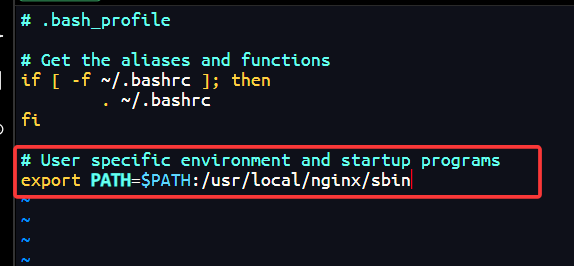
[root@Nginx sbin] vim  ~/.bash_profile
export PATH=$PATH:/usr/local/nginx/sbin

[root@Nginx sbin] source   ~/.bash_profile

[root@Nginx logs] useradd  -s /sbin/nologin -M nginx
[root@Nginx logs] nginx
[root@Nginx logs] ps aux | grep nginx
root       44012  0.0  0.1  14688  2356 ?        Ss   17:01   0:00 nginx: master process nginx
nginx      44013  0.0  0.2  14888  3892 ?        S    17:01   0:00 nginx: worker process
root       44015  0.0  0.1   6636  2176 pts/0    S+   17:01   0:00 grep --color=auto nginx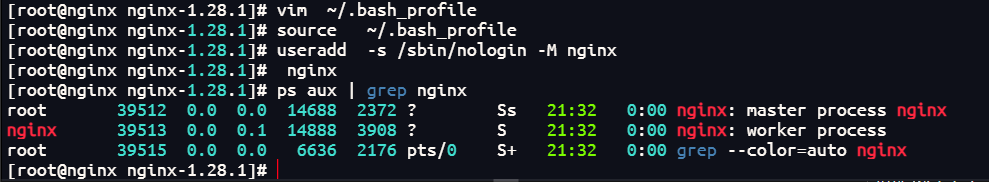
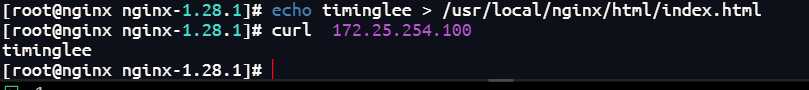
测试:
6.编写启动文件
bash
[root@Nginx ~] vim /lib/systemd/system/nginx.service
[Unit]
Description=The NGINX HTTP and reverse proxy server
After=syslog.target network-online.target remote-fs.target nss-lookup.target
Wants=network-online.target

[Service]
Type=forking
ExecStartPre=/usr/local/nginx/sbin/nginx -t
ExecStart=/usr/local/nginx/sbin/nginx
ExecReload=/usr/local/nginx/sbin/nginx -s reload
ExecStop=/bin/kill -s QUIT $MAINPID
PrivateTmp=true

[Install]
WantedBy=multi-user.target

[root@Nginx ~] systemctl daemon-reload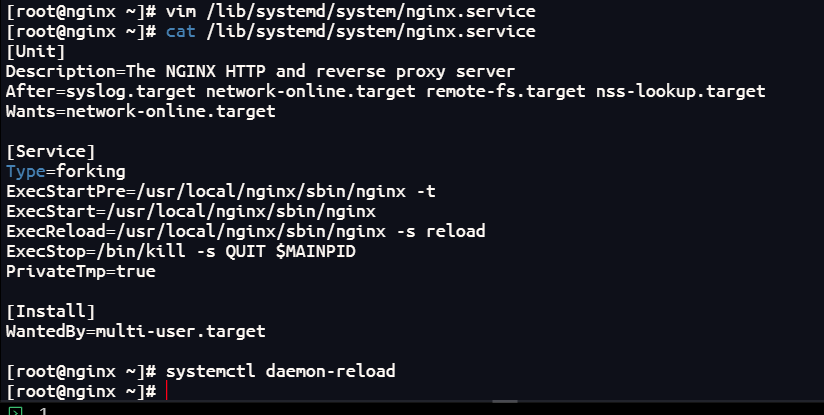
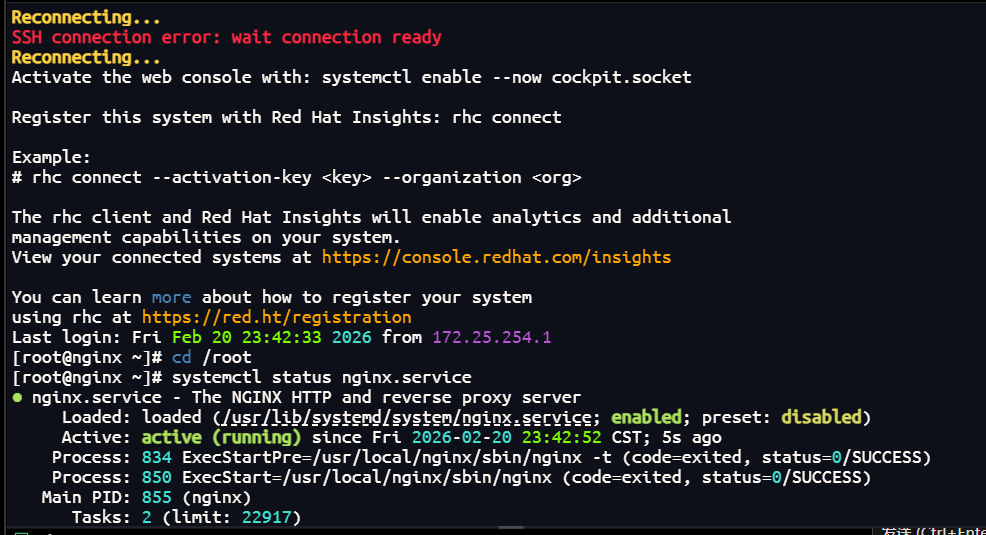
验证:
bash
[root@Nginx ~] reboot
[root@Nginx ~] systemctl status nginx.service
重启后自动启动服务;
二.Nginx的平滑升级及回滚
1.下载高版本的软件
bash
[root@Nginx ~] wget https://nginx.org/download/nginx-1.29.4.tar.gz2.对于新版本的软件进行源码编译并进行平滑升级
bash
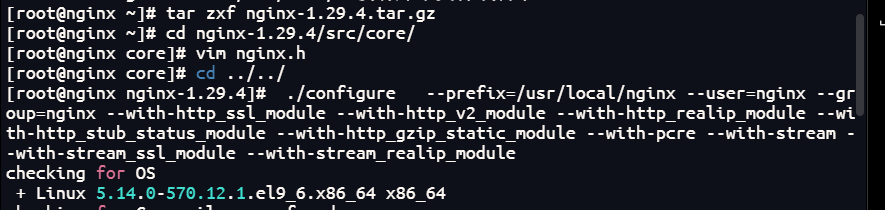
#编译nginx隐藏版本
[root@Nginx ~] tar zxf nginx-1.29.4.tar.gz
[root@Nginx ~] cd nginx-1.29.4/src/core/
[root@Nginx core]# vim nginx.h
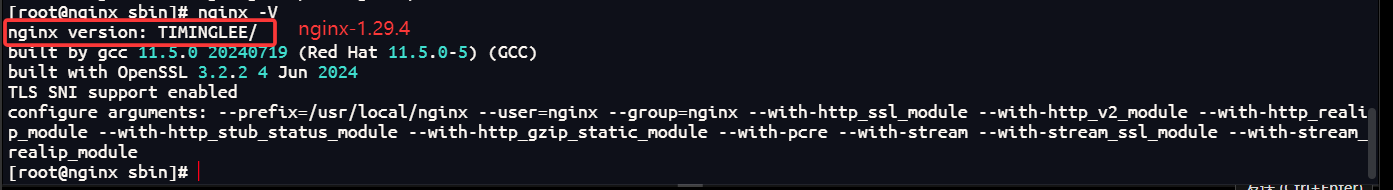
#define nginx_version      1029004
#define NGINX_VERSION      ""
#define NGINX_VER          "TIMINGLEE/" NGINX_VERSION
#文件编辑完成后进行源码编译即可

[root@Nginx core] cd ../../
[root@Nginx nginx-1.29.4] ./configure   --prefix=/usr/local/nginx --user=nginx --group=nginx --with-http_ssl_module --with-http_v2_module --with-http_realip_module --with-http_stub_status_module --with-http_gzip_static_module --with-pcre --with-stream --with-stream_ssl_module --with-stream_realip_module

[root@Nginx nginx-1.29.4] make
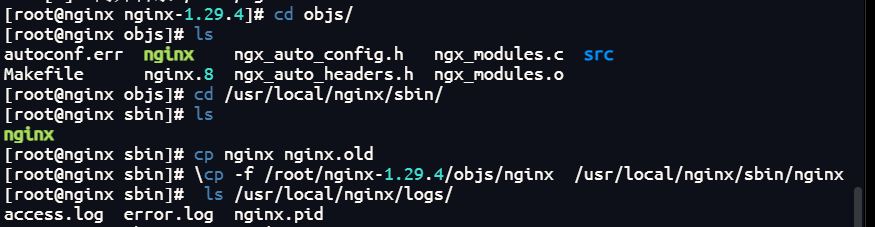
[root@Nginx nginx-1.29.4] cd objs/
[root@Nginx objs] ls
autoconf.err  nginx    ngx_auto_config.h   ngx_modules.c  src
Makefile      nginx.8  ngx_auto_headers.h  ngx_modules.o

[root@Nginx objs] cd /usr/local/nginx/sbin/
[root@Nginx sbin] ls
nginx
#备份旧版本
[root@nginx sbin]# cp nginx nginx.old

[root@Nginx sbin] \cp -f /root/nginx-1.29.4/objs/nginx  /usr/local/nginx/sbin/nginx

[root@Nginx sbin] ls /usr/local/nginx/logs/
access.log  error.log  nginx.pid

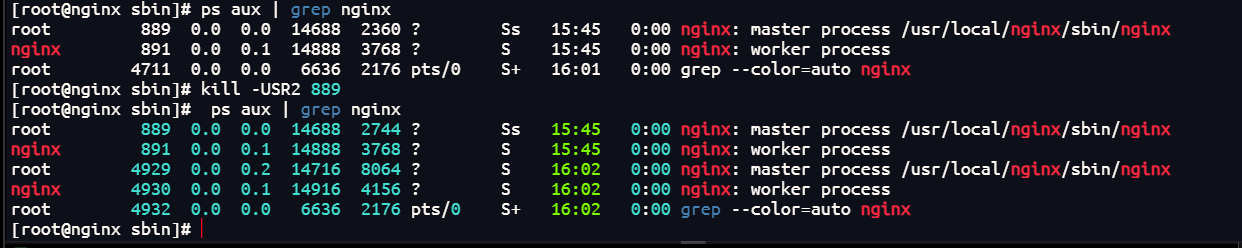
[root@Nginx sbin] ps aux | grep nginx
root        1643  0.0  0.1  14688  2360 ?        Ss   09:55   0:00 nginx: master process /usr/local/nginx/sbin/nginx
nginx       1644  0.0  0.2  14888  3896 ?        S    09:55   0:00 nginx: worker process

[root@Nginx sbin] kill -USR2 1643   #nginx master进程id

[root@Nginx sbin] ps aux | grep nginx
root        1643  0.0  0.1  14688  2744 ?        Ss   09:55   0:00 nginx: master process /usr/local/nginx/sbin/nginx
nginx       1644  0.0  0.2  14888  3896 ?        S    09:55   0:00 nginx: worker process
root        4919  0.0  0.4  14716  7936 ?        S    10:24   0:00 nginx: master process /usr/local/nginx/sbin/nginx
nginx       4921  0.0  0.2  14916  4156 ?        S    10:24   0:00 nginx: worker process
root        4923  0.0  0.1   6636  2176 pts/0    S+   10:25   0:00 grep --color=auto nginx

[root@Nginx sbin] ls /usr/local/nginx/logs/
access.log  error.log  nginx.pid  nginx.pid.oldbin
编译nginx隐藏版本:
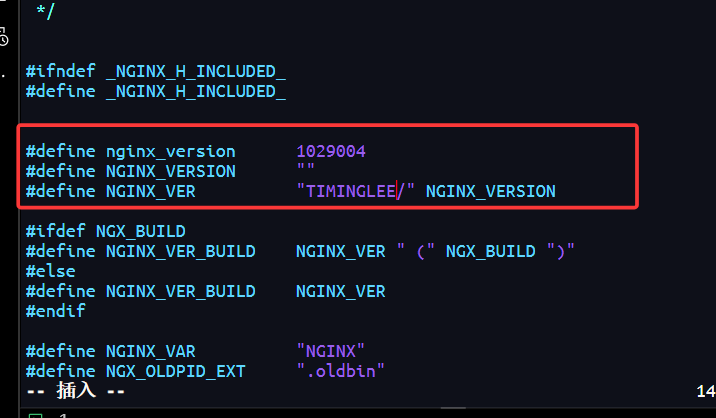
文件编辑完成后进行源码编译即可
关闭nginx master进程id
测试效果:
回收旧版本子进程:
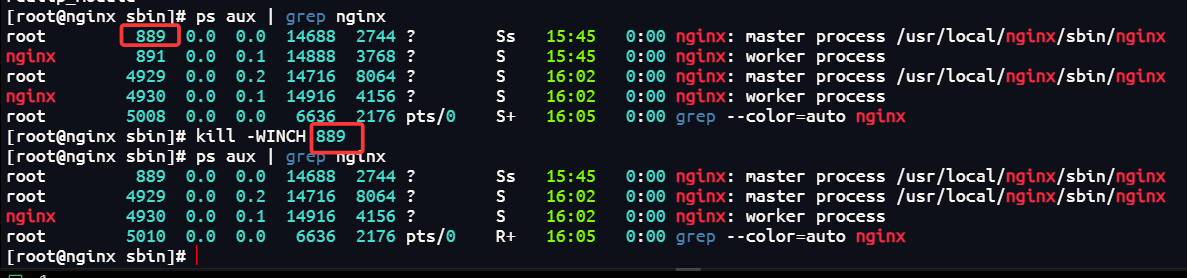
3.版本回退|版本回滚
bash
[root@Nginx sbin] cd /usr/local/nginx/sbin/
[root@Nginx sbin] cp nginx nginx.new -p
[root@Nginx sbin] \cp nginx.old  nginx -pf

[root@Nginx sbin]# kill -HUP 旧版本进程号
[root@Nginx sbin]# ps aux | grep nginx

[root@Nginx sbin]# nginx -V
nginx version: nginx/1.28.1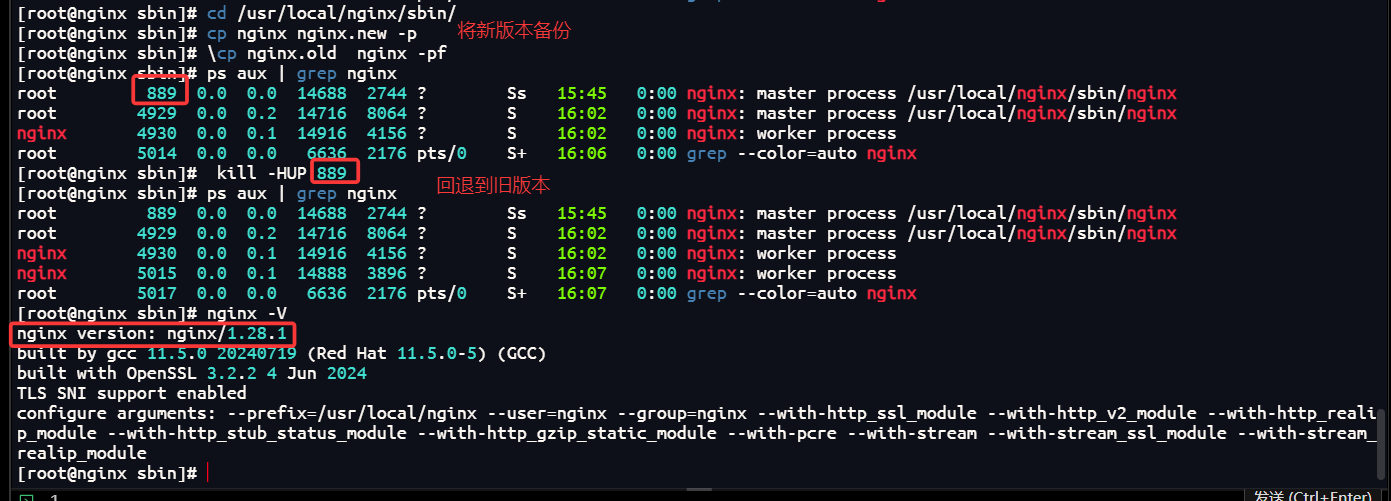
回收新版本进程:
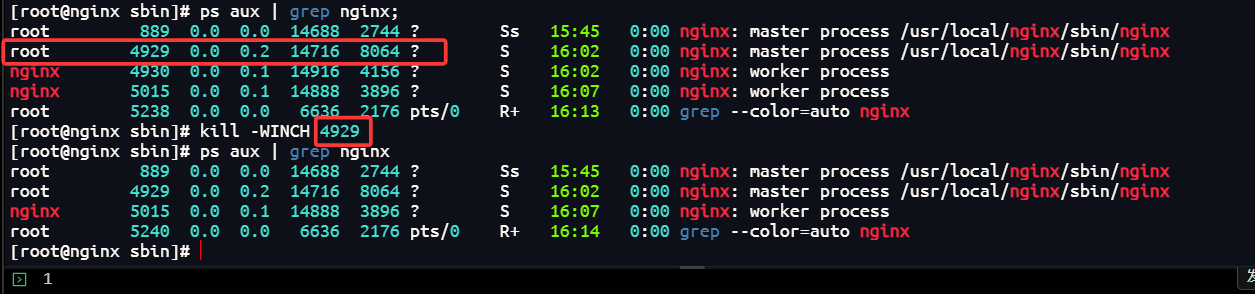
三.Nginx配置文件的管理及优化参数
添加nginx用户:
bash
[root@Nginx ~] vim /usr/local/nginx/conf/nginx.conf

user  nginx;

语法检测:
[root@Nginx ~] nginx  -t
nginx: the configuration file /usr/local/nginx/conf/nginx.conf syntax is ok
nginx: configuration file /usr/local/nginx/conf/nginx.conf test is successful
[root@Nginx ~] nginx -s reload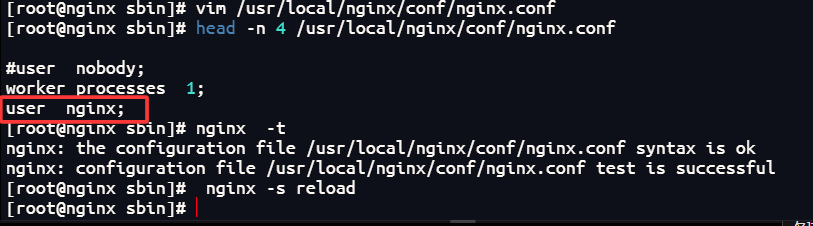
bash
[root@Nginx ~] vim /usr/local/nginx/conf/nginx.conf
worker_processes  2;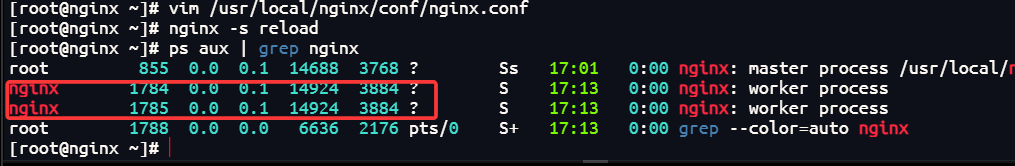
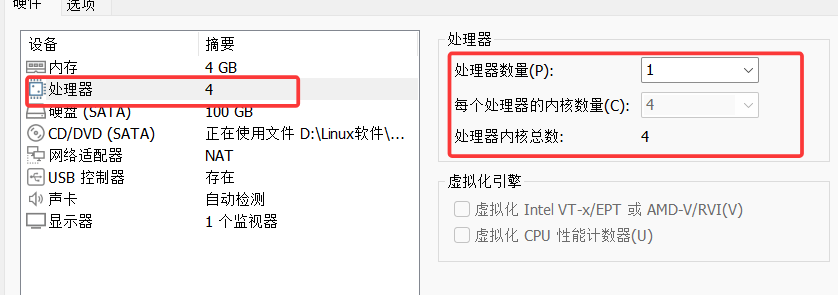
在vmware中更改硬件cpu核心个数,然后重启:
bash
[root@Nginx ~] vim /usr/local/nginx/conf/nginx.conf
worker_processes  auto;
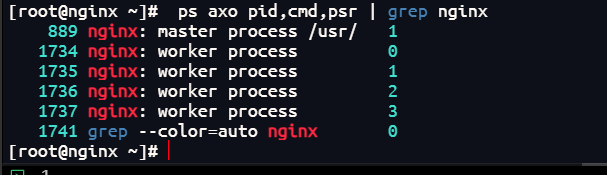
worker_cpu_affinity 0001 0010 0100 1000;

[root@Nginx ~] nginx -s reload
[root@Nginx ~] ps aux | grep nginx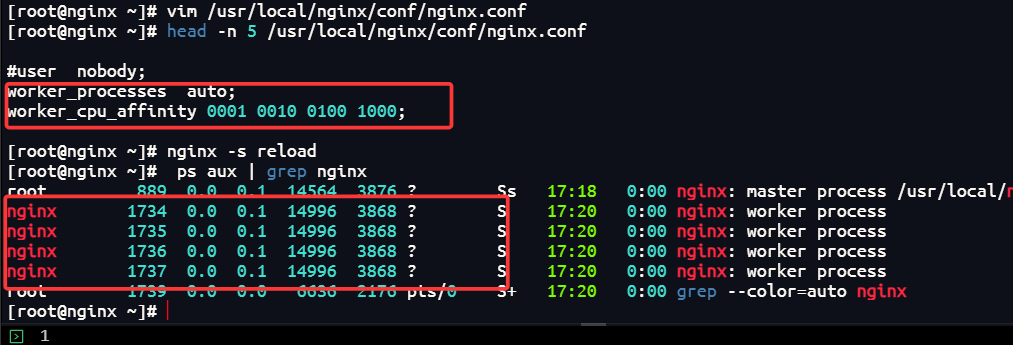
测试并发:
bash
[root@Nginx ~] vim /usr/local/nginx/conf/nginx.conf
events {
    worker_connections  10000;
    use epoll;
    accept_mutex on;
    multi_accept on;
}

[root@Nginx ~] nginx -s reload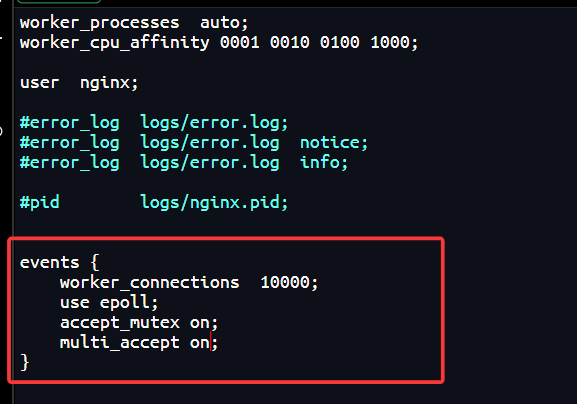
bash
[root@Nginx ~] dnf install httpd-tools -y
[root@Nginx ~] ab  -n 100000 -c5000 http://172.25.254.100/index.html

This is ApacheBench, Version 2.3 <$Revision: 1913912 $>
Copyright 1996 Adam Twiss, Zeus Technology Ltd, http://www.zeustech.net/
Licensed to The Apache Software Foundation, http://www.apache.org/

Benchmarking 172.25.254.100 (be patient)
socket: Too many open files (24)				#并发数量过多导致访问失败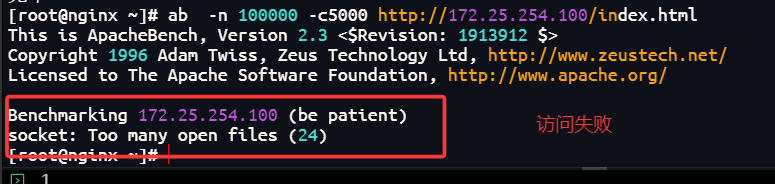
bash
#处理本地文件系统的并发文件数量
[root@Nginx ~] vim /etc/security/limits.conf
*               -       nofile          100000
*               -       noproc          100000
root			-		nofile			100000
#以 nginx 用户身份执行 ulimit -n,检查当前生效的最大文件句柄数。
[root@Nginx ~] sudo -u nginx ulimit -n
100000
#在当前 shell 会话中,临时将最大文件句柄数设置为 100000。
[root@Nginx ~] ulimit  -n 100000
100000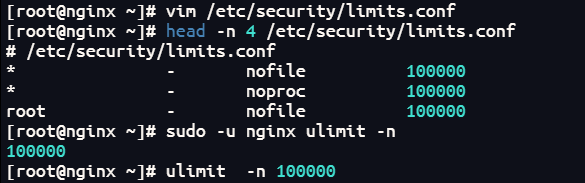
测试:
s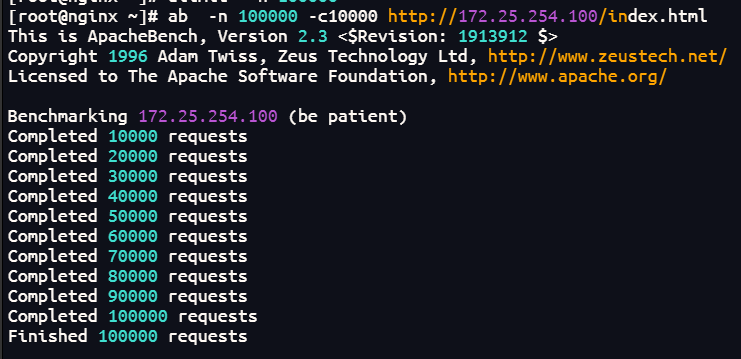
四.Nginx下构建PC站点
1.location中的root
bash
#设置子配置文件:
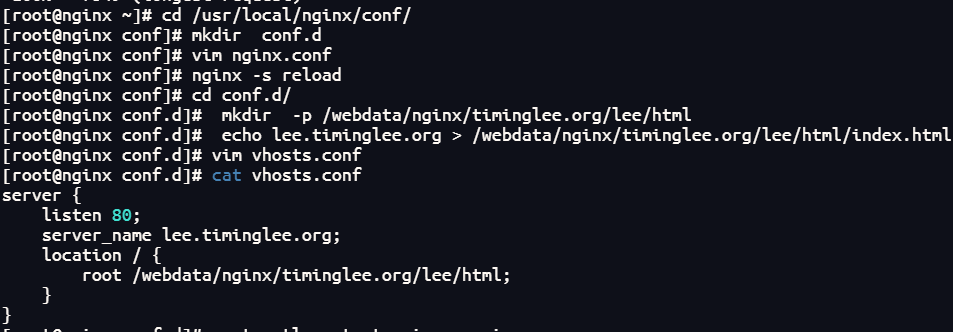
[root@Nginx conf] cd /usr/local/nginx/conf/
[root@Nginx conf] mkdir  conf.d
[root@Nginx conf] vim nginx.conf
82     include "/usr/local/nginx/conf/conf.d/*.conf";

[root@Nginx conf] nginx -s reload
[root@Nginx conf] cd conf.d/
#准备测试网站:
[root@Nginx ~] mkdir  -p /webdata/nginx/timinglee.org/lee/html
[root@Nginx ~] echo lee.timinglee.org > /webdata/nginx/timinglee.org/lee/html/index.html

[root@Nginx conf.d] vim vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    location / {
        root /webdata/nginx/timinglee.org/lee/html;
    }
}

root@Nginx conf.d] systemctl restart nginx.service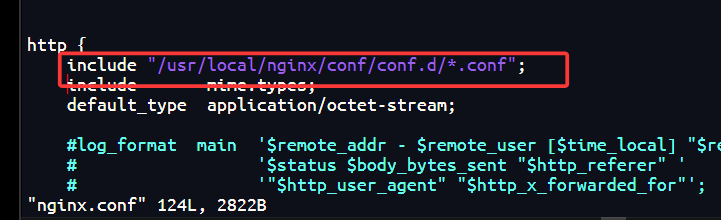
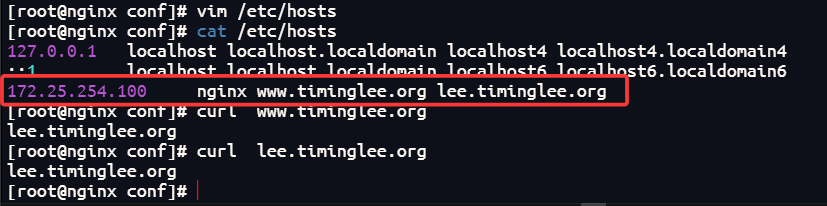
测试:
local示例需要访问lee.timinglee.org/lee/目录:
bash
[root@Nginx conf.d] vim vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    location / {
        root /webdata/nginx/timinglee.org/lee/html;
    }
    location /lee {			#lee标识location中的root值+location 后面指定的值代表目录的路径
        root /webdata/nginx/timinglee.org/lee/html;
    }

}
#重启服务
[root@Nginx conf.d] systemctl restart nginx.service
#准备要访问的目录
[root@Nginx conf.d] mkdir  -p /webdata/nginx/timinglee.org/lee/html/lee
[root@Nginx conf.d] echo lee > /webdata/nginx/timinglee.org/lee/html/lee/index.html
测试:
[root@Nginx conf.d] curl  lee.timinglee.org/lee/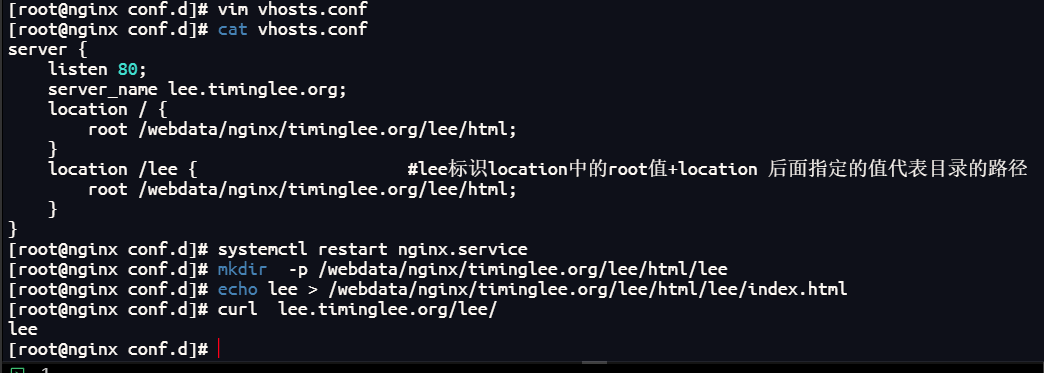
2.location中的alias
bash
[root@Nginx conf.d] vim vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;

    location /passwd {				#标识文件 访问/etc/passwd
        alias /etc/passwd;
    }


    location /passwd/ {				#表示目录 访问/mnt/index.html
        alias /mnt/;
    }

}

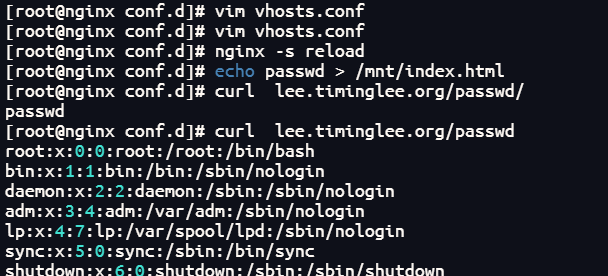
[root@Nginx conf.d] nginx -s reload
[root@Nginx conf.d] echo passwd > /mnt/index.html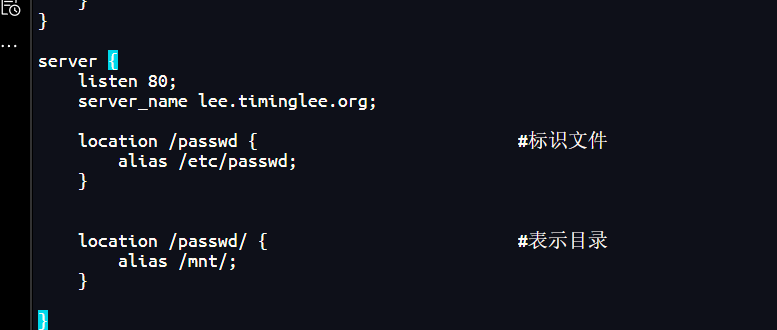
五.KeepAlived长链接优化
1.设定长链接时间
bash
[root@Nginx ~] vim /usr/local/nginx/conf/nginx.conf
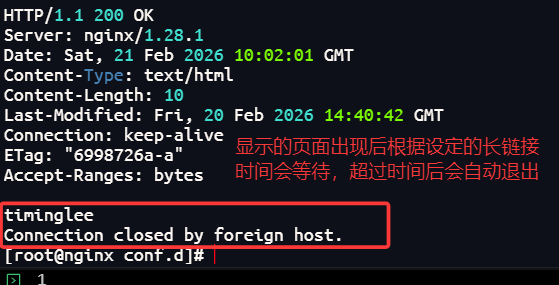
keepalive_timeout   5;
[root@Nginx ~] nginx -s reload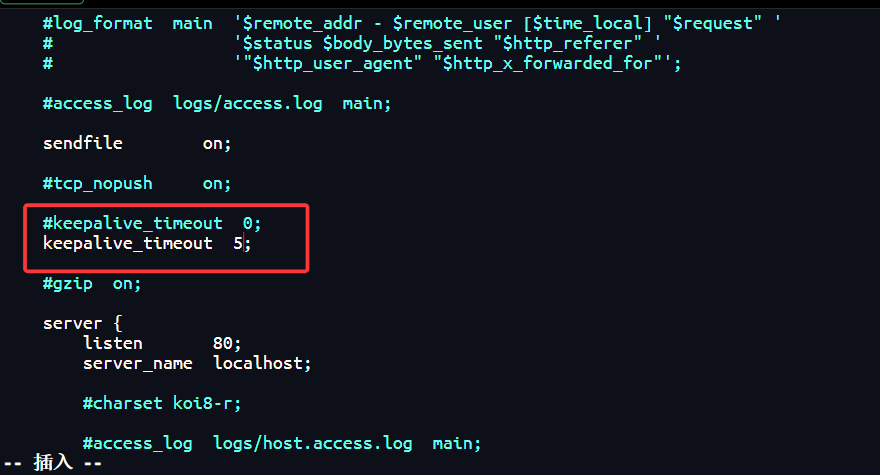
bash
#测试
[root@Nginx ~] dnf install telnet -y
[root@Nginx ~] telnet www.timinglee.org 80
Trying 172.25.254.100...
Connected to www.timinglee.org.
Escape character is '^]'.

输入以下内容:
GET / HTTP/1.1
Host: www.timinglee.org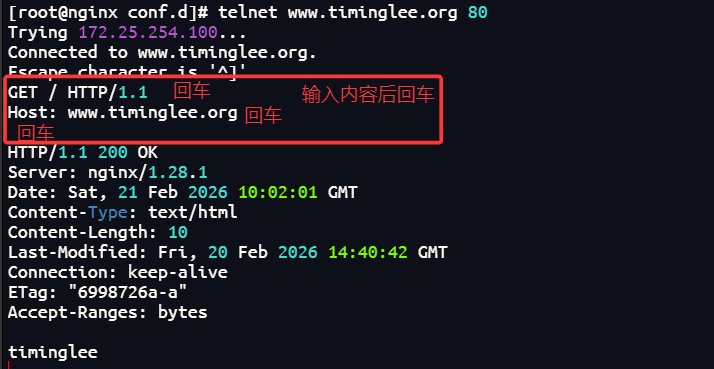
2.设定长链接次数
bash
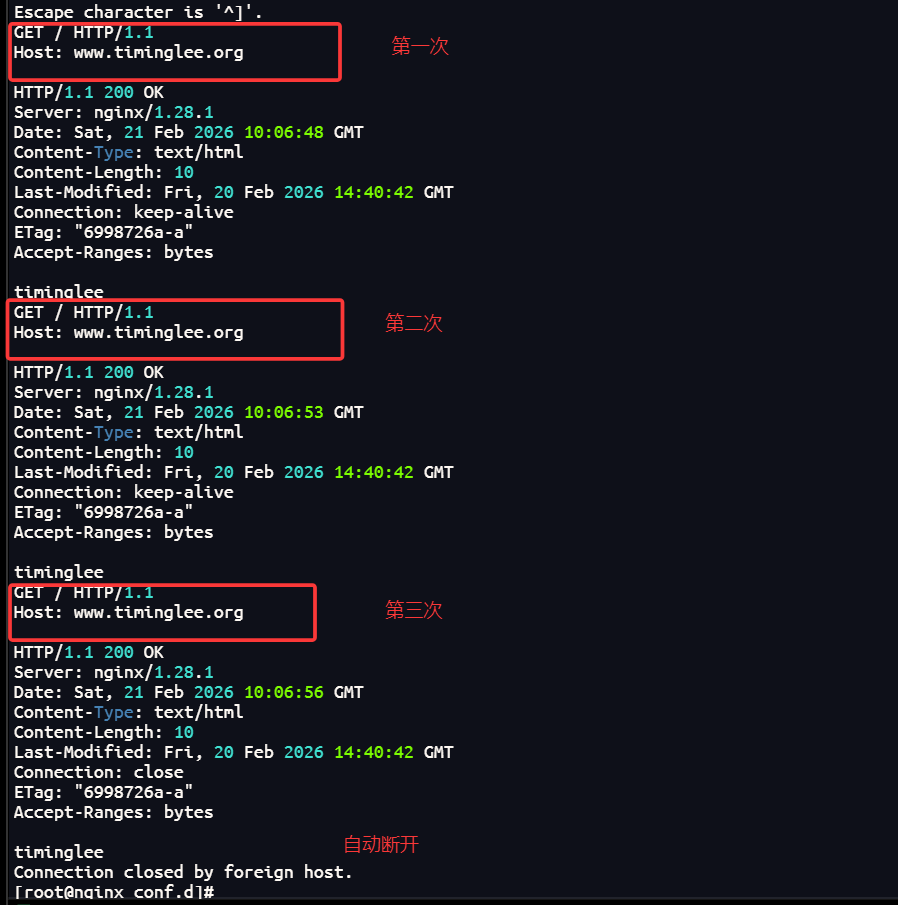
[root@Nginx ~] vim /usr/local/nginx/conf/nginx.conf
keepalive_requests 3;
[root@Nginx ~] nginx -s reload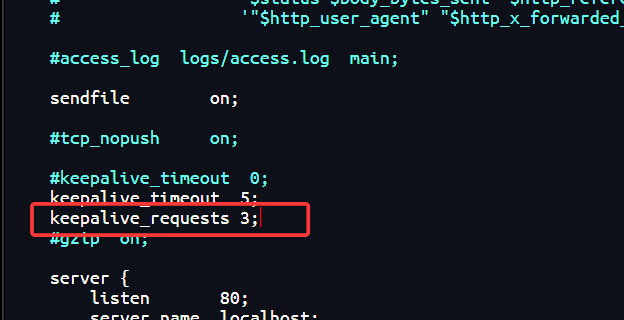
六.Location 字符匹配详解
1.Location后什么都不带直接指定目录
bash
[root@nginx conf.d] vim vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    location /null {
        return 200 "/null-1";
    }
}

[root@nginx conf.d] nginx -s reload
[root@nginx conf.d] curl lee.timinglee.org/null/
/null-1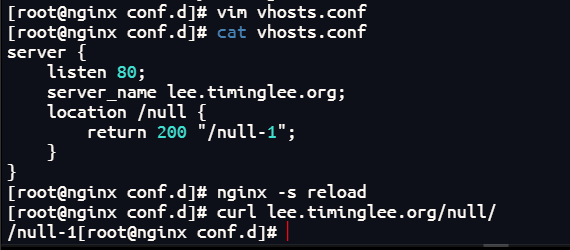
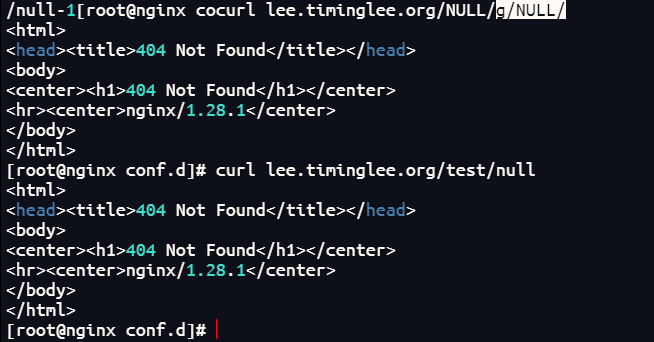
2.location 后用 =
精确匹配(优先级最高):
bash
[root@nginx conf.d] vim vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    location /null {
        return 200 "null-1";
    }

    location = /null {                          #精确匹配到此结束
        return 200 "null-2";
    }

    location ~ /null {
        return 200 "null-3";
    }

}
[root@nginx conf.d] nginx -s reload
[root@nginx conf.d] curl lee.timinglee.org/null
null-2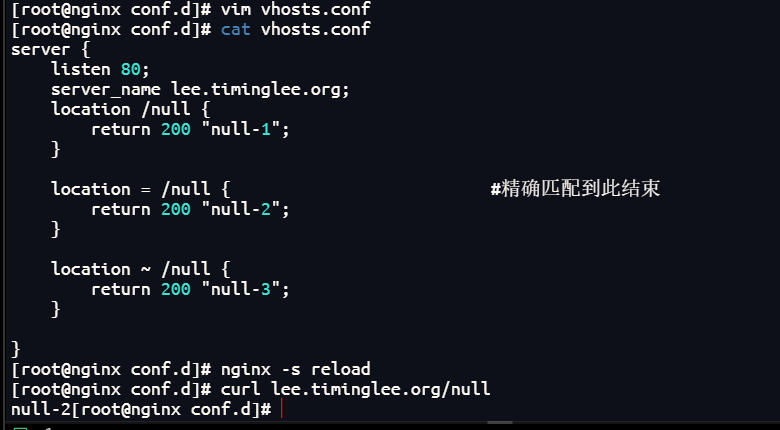
3.location 后用"^~"
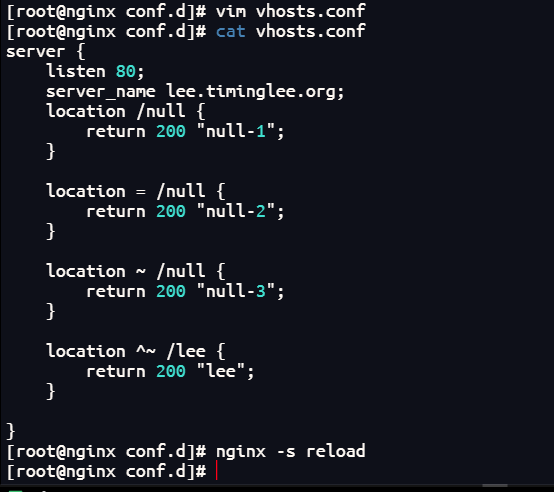
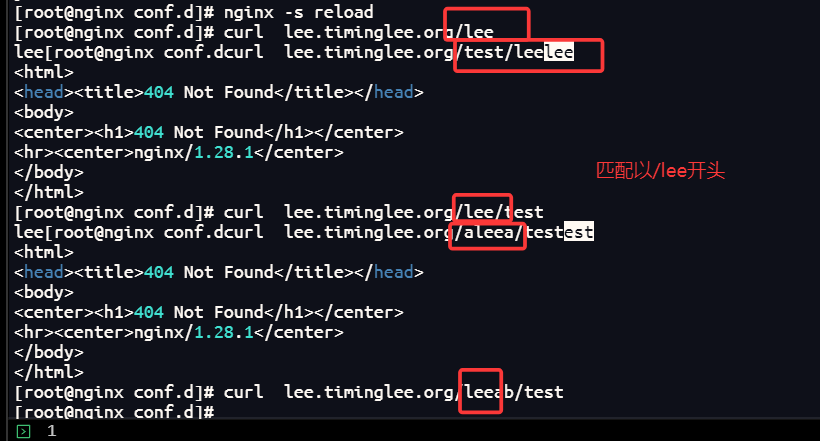
前缀优先匹配:
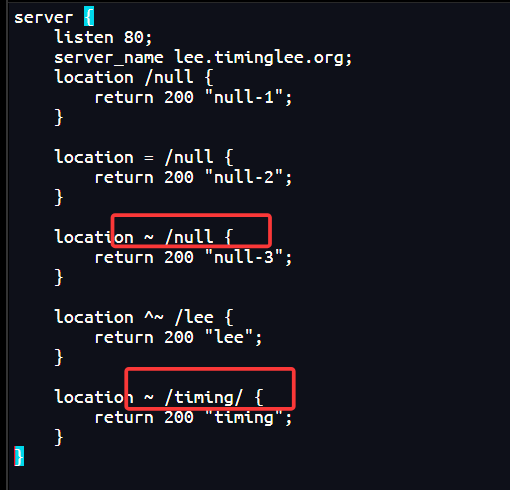
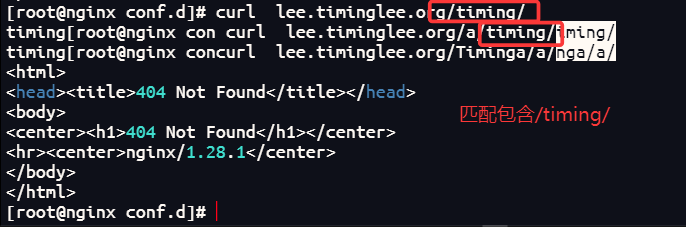
4.location 后用"~"
区分大小写的正则匹配:
5.location 后用"~*"
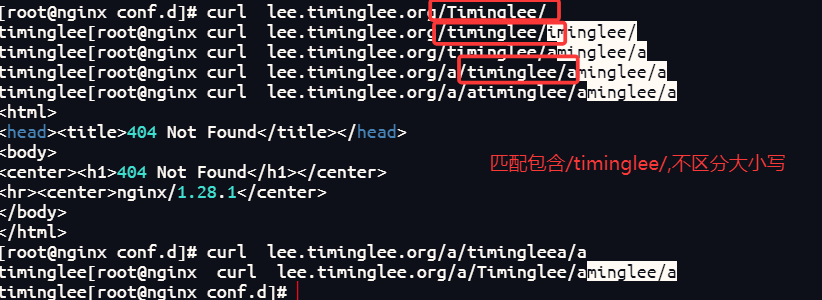
不区分大小写的正则匹配:
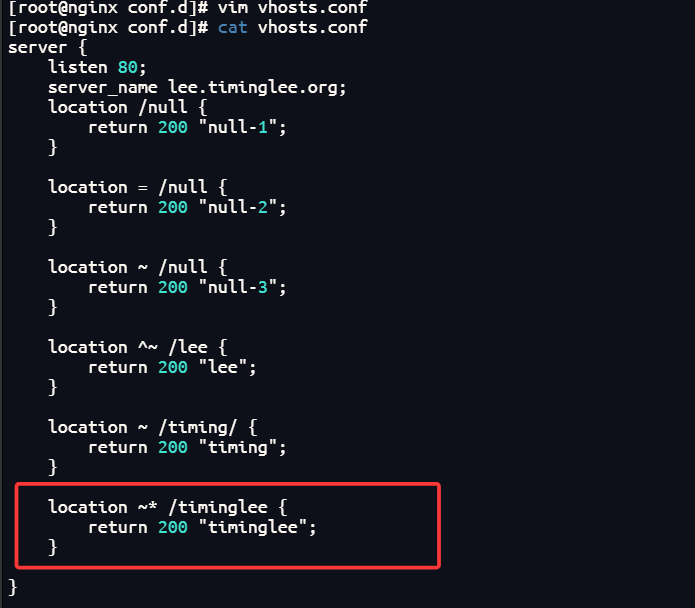
不区分大小写的正则匹配 ,只要 URI 中包含 timinglee 字符串就会触发
6.location 后用"\"
\后加正则表达式:
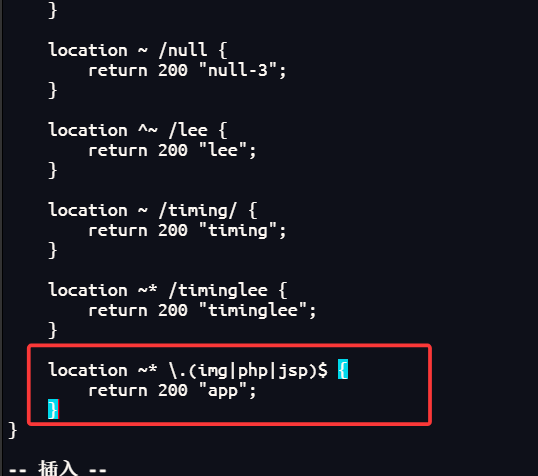
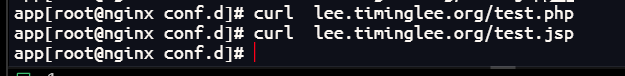
不区分大小写,匹配以.img,.php 或 .jsp 结尾
七.服务访问的用户认证
bash
#创建 .htpasswd 文件,并添加了用户 admin,密码为 lee
[root@Nginx ~] htpasswd  -cmb /usr/local/nginx/conf/.htpasswd admin  lee
Adding password for user admin

[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    location /admin {     #对/admin路径启用认证
        root /usr/local/nginx/html;
        auth_basic "login passwd";    #弹出浏览器认证框,提示文字为"Login passwd"
        # 指定密码文件路径,与 htpasswd 生成的文件对应
        auth_basic_user_file "/usr/local/nginx/conf/.htpasswd";
    }
}

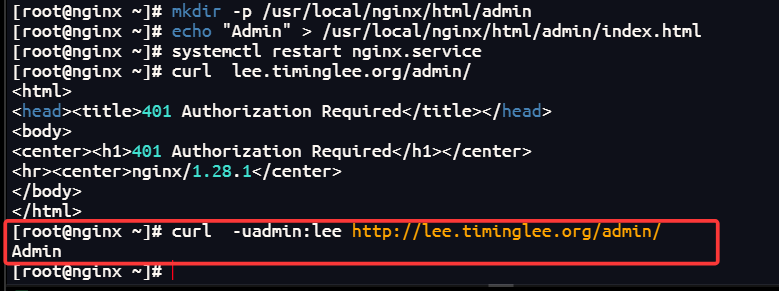
# 创建 admin 目录
mkdir -p /usr/local/nginx/html/admin
# 创建一个 index.html 文件
echo "Admin" > /usr/local/nginx/html/admin/index.html

[root@Nginx ~] systemctl restart nginx.service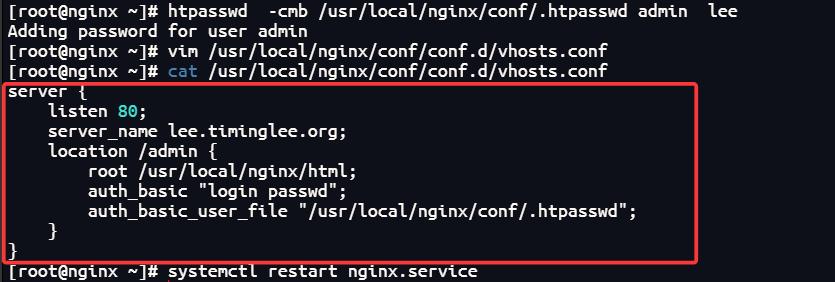
测试:
八.自定义错误日志
bash
[root@Nginx ~] mkdir  -p /usr/local/nginx/logs/timinglee.org/
#创建错误界面
[root@nginx ~] mkdir -p /usr/local/nginx/errorpage
[root@nginx ~] echo "<h1>页面不存在</h1>" > /usr/local/nginx/errorpage/errormessage

[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
	server {
    listen 80;
    server_name lee.timinglee.org;
    error_page 404 405 503 502 /error;
    error_log logs/timinglee.org/lee.error error;
    location /lee {
        root /usr/local/nginx/html;
    }
    #错误界面
    location /error {
        alias /usr/local/nginx/errorpage/errormessage;
    }
}

[root@Nginx ~] systemctl restart nginx.service
测试: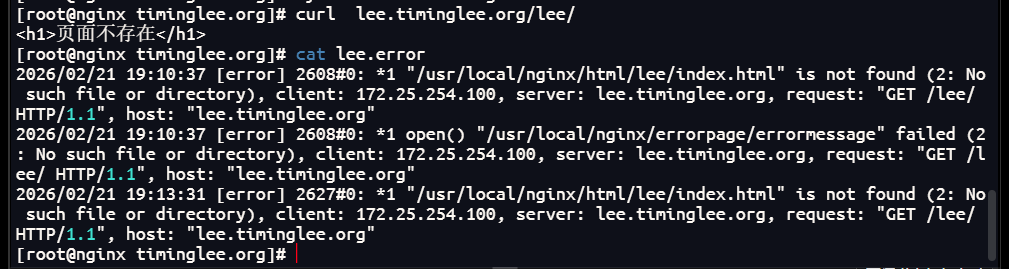
九.Nginx中建立下载服务器
环境准备:
bash
#准备下载文件
#创建了/usr/local/nginx/download/目录作为下载目录
[root@Nginx ~] mkdir  -p /usr/local/nginx/download
复制了系统文件passwd作为测试文件。
[root@Nginx ~] cp /etc/passwd  /usr/local/nginx/download/
#使用dd命令生成一个100MB的测试大文件 bigfile,用于测试大文件下载。
[root@Nginx ~] dd if=/dev/zero of=/usr/local/nginx/download/bigfile bs=1M count=100
记录了100+0 的读入
记录了100+0 的写出
104857600字节(105 MB,100 MiB)已复制,0.152409 s,688 MB/s

[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    error_page 404 405 503 502 /error;
    error_log logs/timinglee.org/lee.error error;
    location /lee {
        root /usr/local/nginx/html;
    }

    location /error {
        alias /usr/local/nginx/errorpage/errormessage;
    }

    location /download {
        root /usr/local/nginx;
    }
}
[root@Nginx ~] nginx -s reload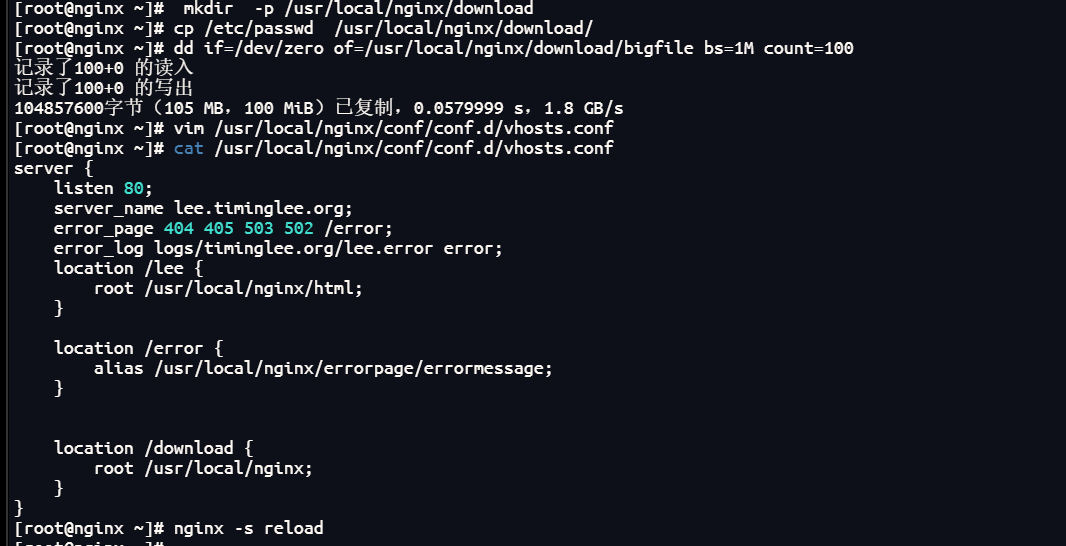
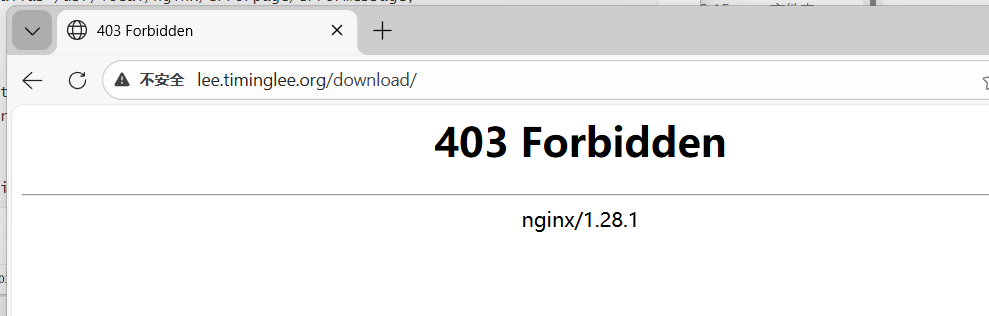
1.启用列表功能
bash
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    error_page 404 405 503 502 /error;
    error_log logs/timinglee.org/lee.error error;
    location /lee {
        root /usr/local/nginx/html;
    }

    location /error {
        alias /usr/local/nginx/errorpage/errormessage;
    }


    location /download {
        root /usr/local/nginx;
        #启用列表功能
        autoindex on;
    }
}
[root@Nginx ~] nginx -s reload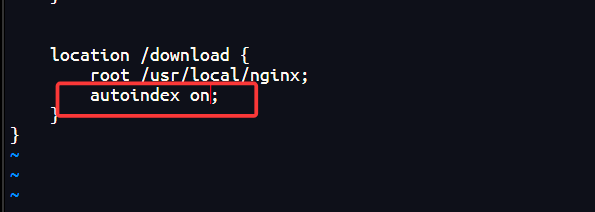
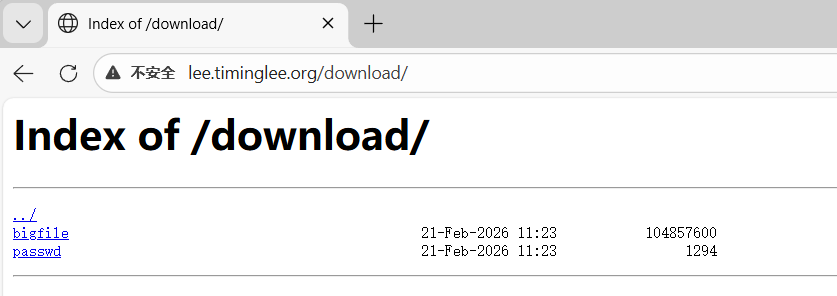
2.下载控速
bash
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    error_page 404 405 503 502 /error;
    error_log logs/timinglee.org/lee.error error;
    location /lee {
        root /usr/local/nginx/html;
    }

    location /error {
        alias /usr/local/nginx/errorpage/errormessage;
    }


    location /download {
        root /usr/local/nginx;
        autoindex on;
        #对 /download 路径下的所有文件下载进行限速。
        limit_rate 1024k;
    }
}
[root@Nginx ~] nginx -s reload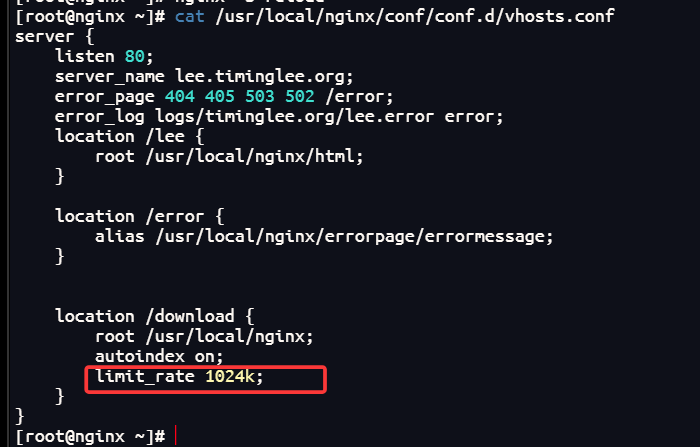
测试:
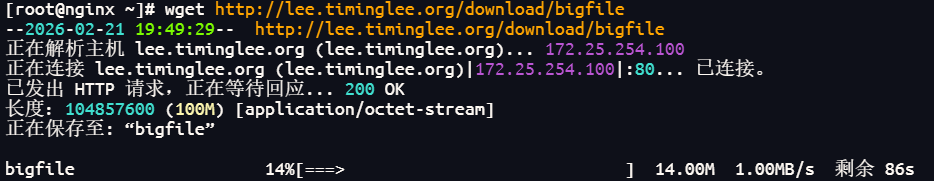
3.显示文件大小优化
bash
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    error_page 404 405 503 502 /error;
    error_log logs/timinglee.org/lee.error error;
    location /lee {
        root /usr/local/nginx/html;
    }

    location /error {
        alias /usr/local/nginx/errorpage/errormessage;
    }


    location /download {
        root /usr/local/nginx;
        autoindex on;
        limit_rate 1024k;
        autoindex_exact_size off;   #新增的优化配置
    }
}
[root@Nginx ~] nginx -s reload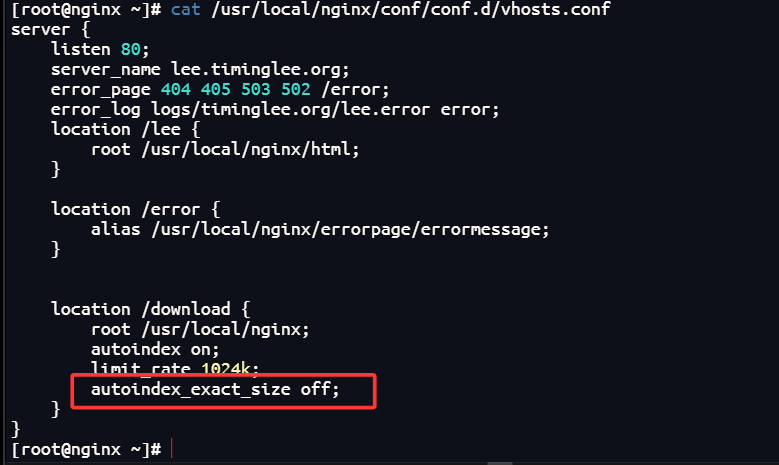
测试: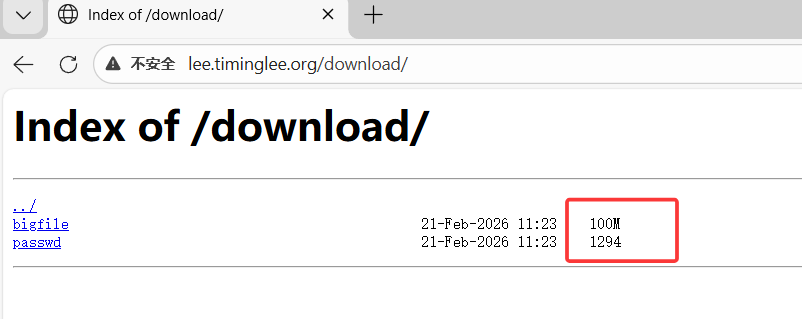
4.时间显示调整
bash
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    error_page 404 405 503 502 /error;
    error_log logs/timinglee.org/lee.error error;
    location /lee {
        root /usr/local/nginx/html;
    }

    location /error {
        alias /usr/local/nginx/errorpage/errormessage;
    }


    location /download {
        root /usr/local/nginx;
        autoindex on;
        limit_rate 1024k;
        autoindex_exact_size off;
        #时间显示调整
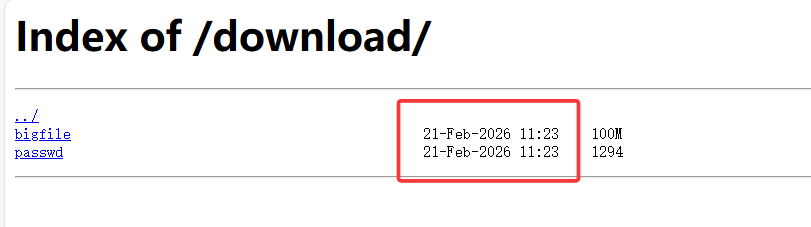
        autoindex_localtime on;
    }
}
[root@Nginx ~] nginx -s reload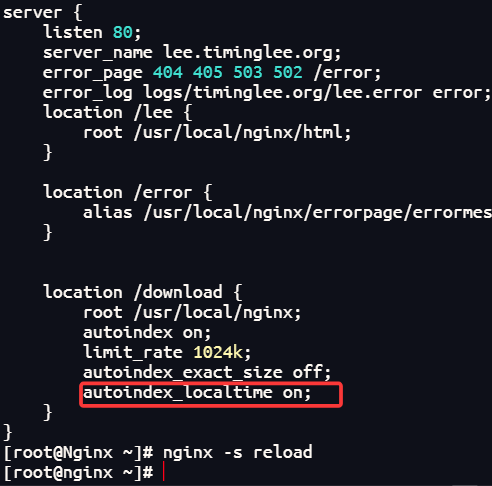
效果:
5.设定页面风格
bash
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    error_page 404 405 503 502 /error;
    error_log logs/timinglee.org/lee.error error;
    location /lee {
        root /usr/local/nginx/html;
    }

    location /error {
        alias /usr/local/nginx/errorpage/errormessage;
    }


    location /download {
        root /usr/local/nginx;
        autoindex on;
        limit_rate 1024k;
        autoindex_exact_size off;
        autoindex_localtime on;
        #页面风格,选择一个使用
        autoindex_format html | xml | json | jsonp;
    }
}
[root@Nginx ~] nginx -s reload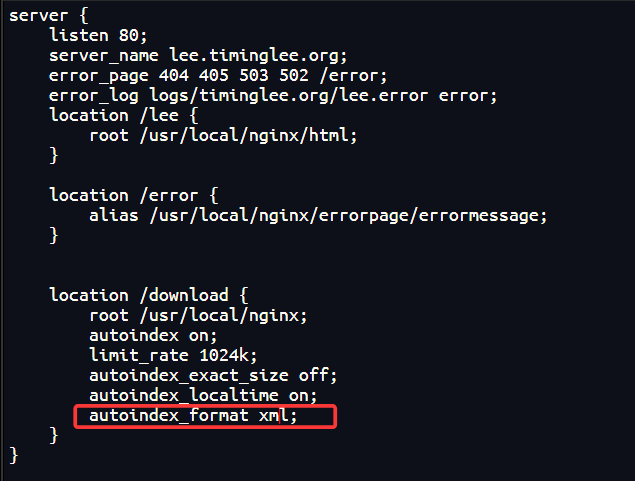
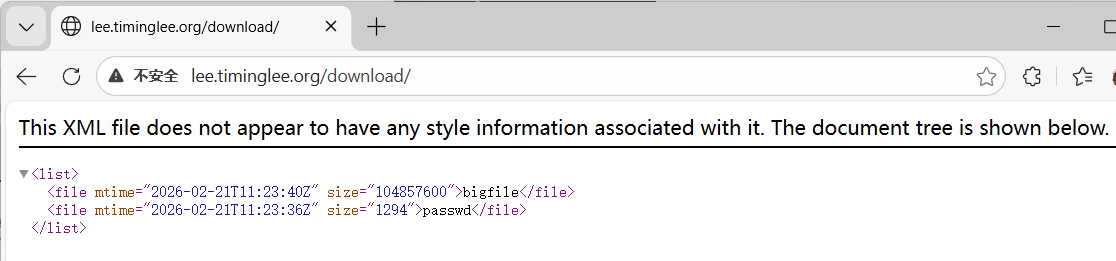
xml风格:
十.Nginx的文件检测
bash
[root@Nginx ~] echo default > /usr/local/nginx/errorpage/default.html
[root@Nginx ~] cat /usr/local/nginx/errorpage/default.html
default

[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    error_page 404 405 503 502 /error;
    error_log logs/timinglee.org/lee.error error;
    #所有文件查找都从这个目录开始。
    root /usr/local/nginx/errorpage;
    #依次尝试查找以下内容
    try_files $uri $uri.html $uri/index.html /default.html;
}

[root@Nginx ~] nginx -s reload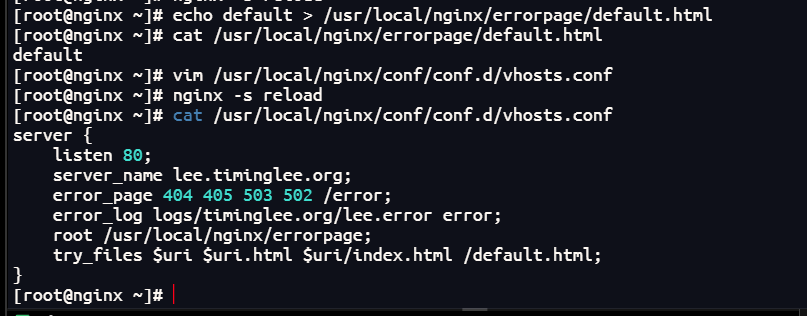
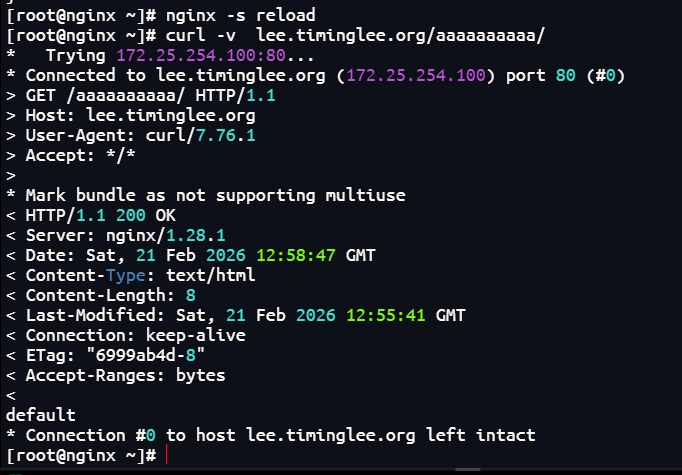
测试:
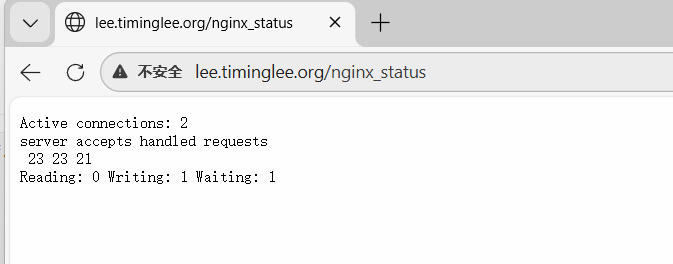
Nginx的状态页
bash
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;

    location /nginx_status{
        stub_status;  #启用状态页
        auth_basic "auth login";  #启用基础认证,提示语为"authlogin"
        auth_basic_user_file /usr/local/nginx/conf/.htpasswd;   #指定密码文件
        allow 172.25.254.0/24; #仅允许 172.25.254.0/24 网段访问
        deny all;    #拒绝所有其他IP访问
    }
}

[root@Nginx ~] nginx -s reload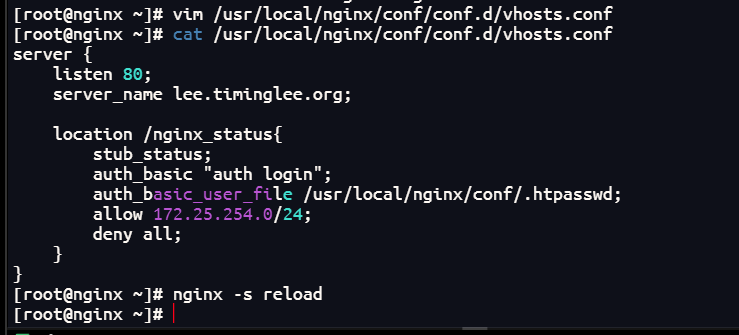
测试:
十一.Nginx的压缩功能:
bash
[root@Nginx ~]# mkdir  /usr/local/nginx/timinglee.org/lee/html -p
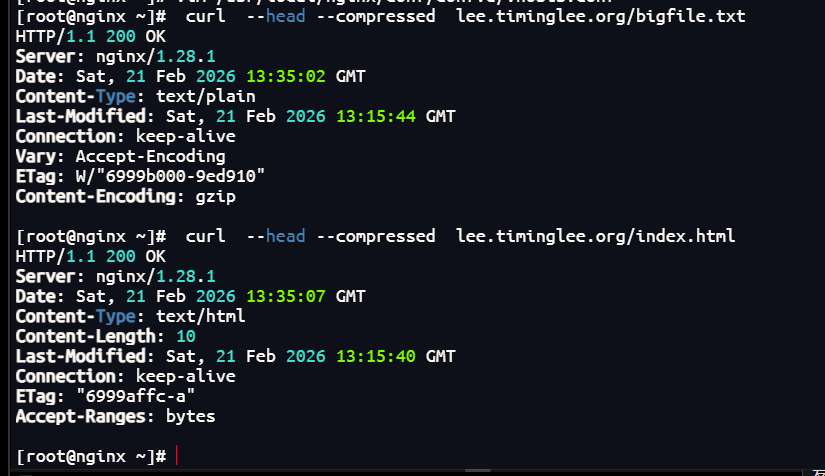
[root@Nginx ~]# echo  hello lee > /usr/local/nginx/timinglee.org/lee/html/index.html
[root@Nginx html]# cp /usr/local/nginx/logs/access.log /usr/local/nginx/timinglee.org/lee/html/bigfile.txt


[root@Nginx ~] vim /usr/local/nginx/conf/nginx.conf
    gzip  on;   #启用gzip压缩功能。
    gzip_comp_level 4;  #设置压缩级别为(范围 1-9。级别越高,压缩率越高,但消耗的CPU资源也越多。
    gzip_disable "MSIE [1-6]\.";
    gzip_min_length 1024k; #设置触发压缩的最小响应大小为1024KB。
    gzip_buffers 32 1024k;  #设置压缩缓冲区数量和大小:32 个缓冲区,每个 1024KB。用于存储压缩过程中的数据。
    gzip_types text/plain application/javascript application/x-javascript text/css  application/xml text/javascript application/x-httpd-php image/gif image/png; #指定需要进行压缩的 MIME 类型
    gzip_vary on;
    gzip_static on; #启用静态压缩。Nginx 会优先查找并返回 .gz 后缀的预压缩文件,而不是动态压缩,从而节省 CPU 资源


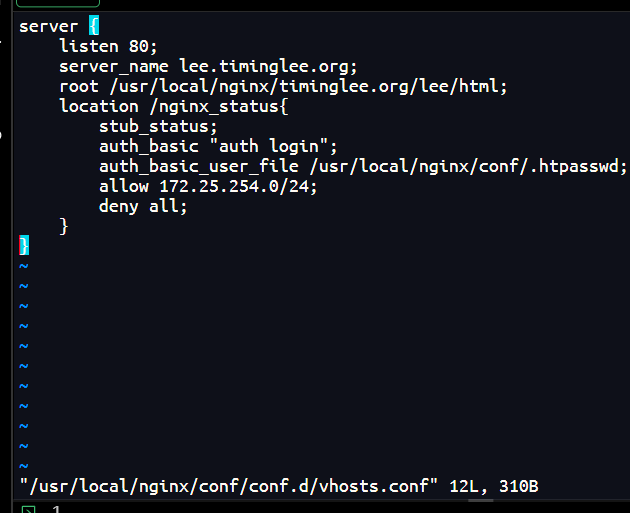
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    root /usr/local/nginx/timinglee.org/lee/html;
    location /nginx_status{
        stub_status;
        auth_basic "auth login";
        auth_basic_user_file /usr/local/nginx/conf/.htpasswd;
        allow 172.25.254.0/24;
        deny all;
    }
}

[root@Nginx ~] nginx -s reload
启动服务: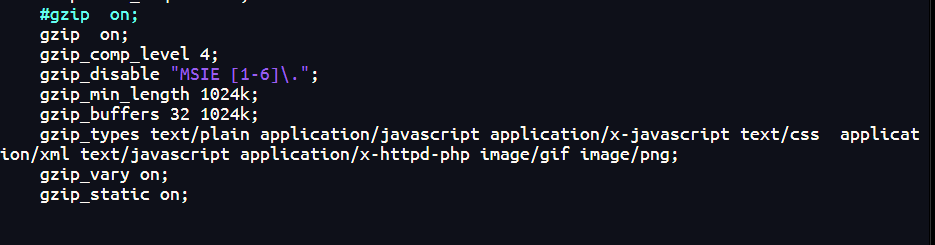
测试:
十二.Nginx 变量
1.升级Nginx支持echo
关闭nginx服务:
bash
[root@Nginx ~] systemctl stop nginx.service
[root@Nginx ~] ps aux | grep nginx
root        5193  0.0  0.1   6636  2176 pts/1    S+   16:08   0:00 grep --color=auto nginx
bash
[root@Nginx ~] tar zxf echo-nginx-module-0.64.tar.gz
[root@Nginx ~] cd nginx-1.28.1/

[root@Nginx nginx-1.28.1] make clean

[root@Nginx nginx-1.28.1] ./configure  --prefix=/usr/local/nginx --user=nginx --group=nginx --with-http_ssl_module --with-http_v2_module --with-http_realip_module --with-http_stub_status_module --with-http_gzip_static_module --with-pcre --with-stream --with-stream_ssl_module --with-stream_realip_module  --add-module=/root/echo-nginx-module-0.64

[root@Nginx nginx-1.28.1] make
[root@Nginx nginx-1.28.1] rm -rf /usr/local/nginx/sbin/nginx
[root@Nginx nginx-1.28.1] cp objs/nginx /usr/local/nginx/sbin/ -p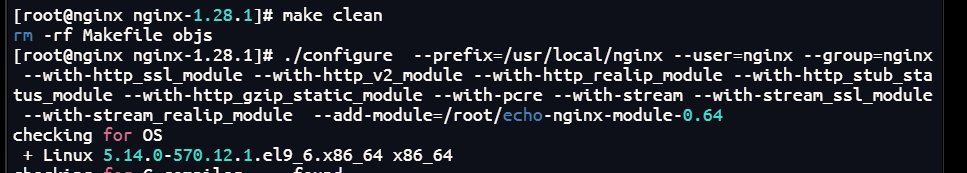
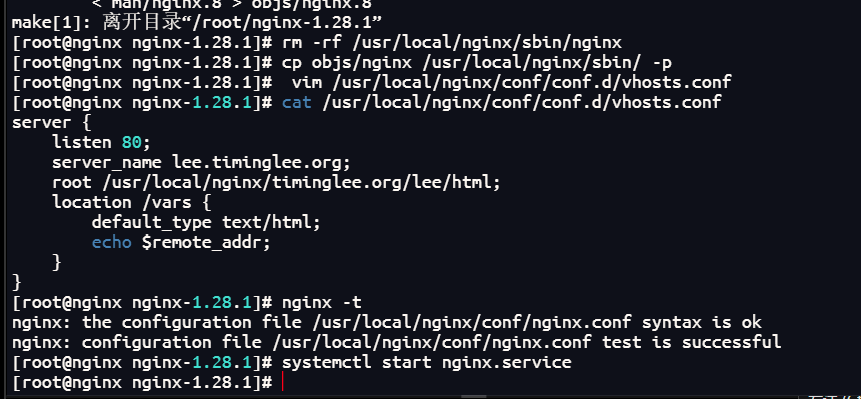
测试:
2.理解内建变量
准备环境:
bash
[root@Nginx nginx-1.28.1] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    root /usr/local/nginx/timinglee.org/lee/html;
    location /vars {
        default_type text/html;
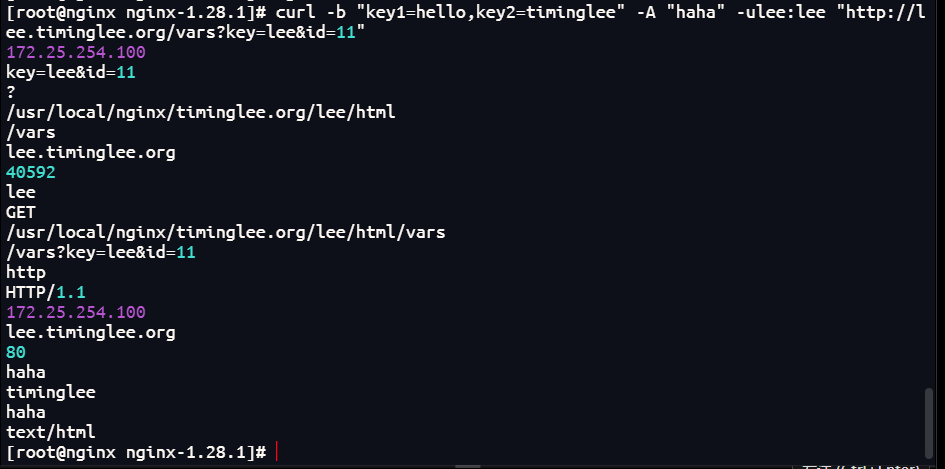
        echo $remote_addr;   #客户端 IP 地址
        echo $args;   #请求 URL 中的查询参数
        echo $is_args;
        echo $document_root;  #当前请求对应的根目录
        echo $document_uri;   #当前请求的 URI(不包含查询参数)
        echo $host;   #请求头中的 Host 字段
        echo $remote_port;   #客户端连接的端口
        echo $remote_user;   #经过 Basic Auth 认证的用户名
        echo $request_method;   #请求方法(GET/POST 等)
        echo $request_filename;   #映射到的本地文件路径
        echo $request_uri;   #完整的请求 URI(包含查询参数)
        echo $scheme;   #请求使用的协议(http/https)
        echo $server_protocol;   #服务器使用的协议(如 HTTP/1.1
        echo $server_addr;   #服务器 IP 地址
        echo $server_name;   #服务器名称(server_name 指令的值)
        echo $server_port;   #服务器监听的端口
        echo $http_user_agent;   #客户端的 User-Agent 信息
        echo $cookie_key2;   #名为 key2 的 Cookie 值
        echo $http_user_agent;   #客户端的 User-Agent 信息
        echo $sent_http_content_type;   #响应头中 Content-Type 的值
    }
}

[root@Nginx nginx-1.28.1] nginx -s reload
[root@Nginx nginx-1.28.1] curl -b "key1=hello,key2=timinglee" -A "haha" -ulee:lee "http://lee.timinglee.org/vars?key=lee&id=11"
测试:
3.自定义变量
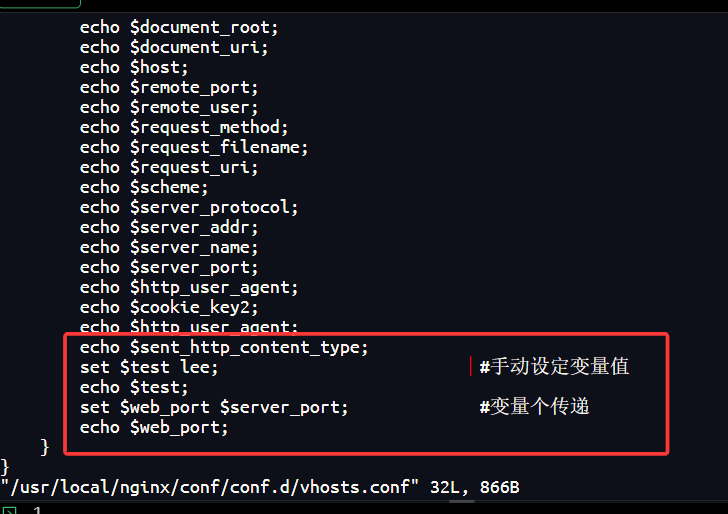
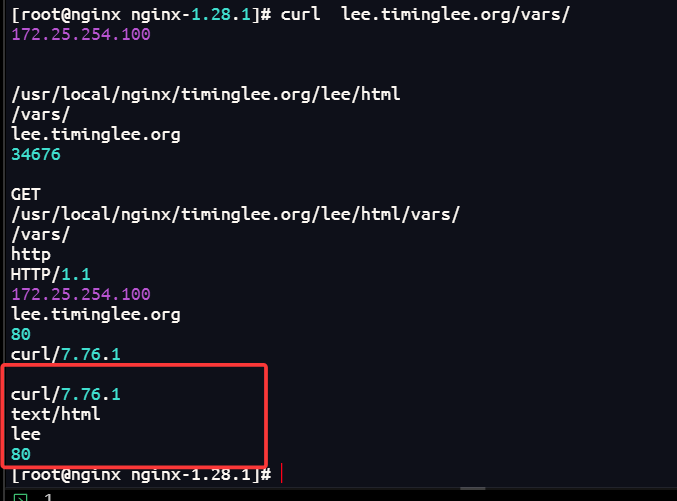
测试:
十三.网页从写
bash
#if
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    root /webdir/timinglee.org/lee/html;
    location /vars {
        echo $remote_user;
        echo $request_method;
        echo $request_filename;
        echo $request_uri;
        echo $scheme;
    }

    location / {
        #当条件满足时,执行return,直接返回状态码 200 和文本内容
        if ( $http_user_agent ~* firefox ) {
            return 200 "test if messages";
        }
    }
}

[root@Nginx ~] nginx -s reload
#普通访问:curl lee.timinglee.org;User-Agent 是 curl/7.76.1,不匹配 firefox,因此执行默认逻辑,返回根目录下的 lee page
[root@Nginx ~] curl  lee.timinglee.org
lee page
#模拟 Firefox 访问:curl -A "firefox" lee.timinglee.org;通过 -A 参数指定 User-Agent 为 firefox,触发 if 条件,返回 test if messages。
[root@Nginx ~] curl  -A "firefox" lee.timinglee.org
test if messages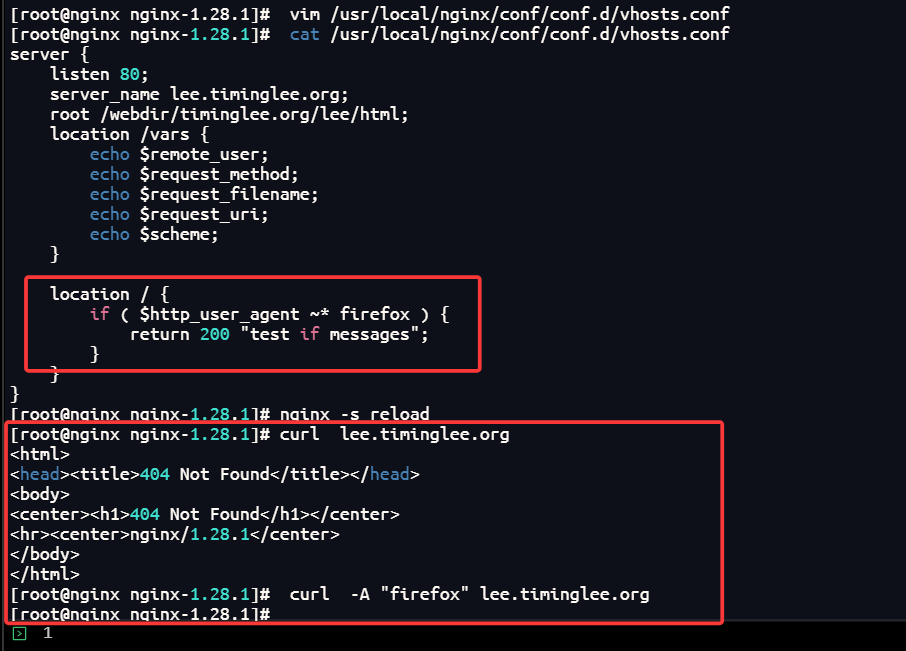
bash
#set
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    root /webdir/timinglee.org/lee/html;
    location /vars {
        echo $remote_user;
        echo $request_method;
        echo $request_filename;
        echo $request_uri;
        echo $scheme;
    }

    location / {
        #定义一个名为 $testname 的自定义变量,并将其值设为字符串 timinglee 。
        set $testname timinglee;
        #echo $testname;:使用 echo 模块将这个变量的值直接输出到响应体中。
        echo $testname;
    }
}

[root@Nginx ~] nginx -s reload

[root@Nginx ~] curl  lee.timinglee.org
timinglee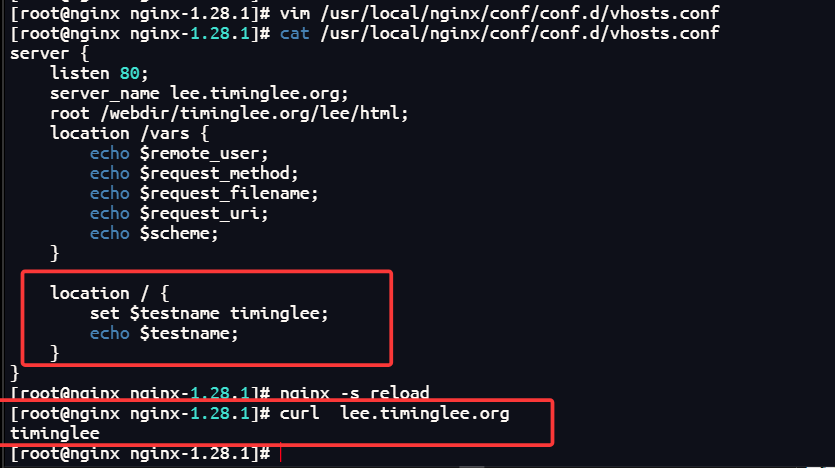
bash
#break
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    root /webdir/timinglee.org/lee/html;
    location /vars {
        echo $remote_user;
        echo $request_method;
        echo $request_filename;
        echo $request_uri;
        echo $scheme;
    }

    location / {
        set $test1 lee1;
        set $test2 lee2;
        if ($http_user_agent = firefox){
            break;  # 条件满足时,中断后续指令
        }
        set $test3 lee3;
        echo $test1 $test2 $test3;
    }
}
[root@Nginx ~] nginx -s reload

[root@Nginx ~] curl  lee.timinglee.org
lee1 lee2 lee3
[root@Nginx ~] curl -A "firefox" lee.timinglee.org
lee1 lee2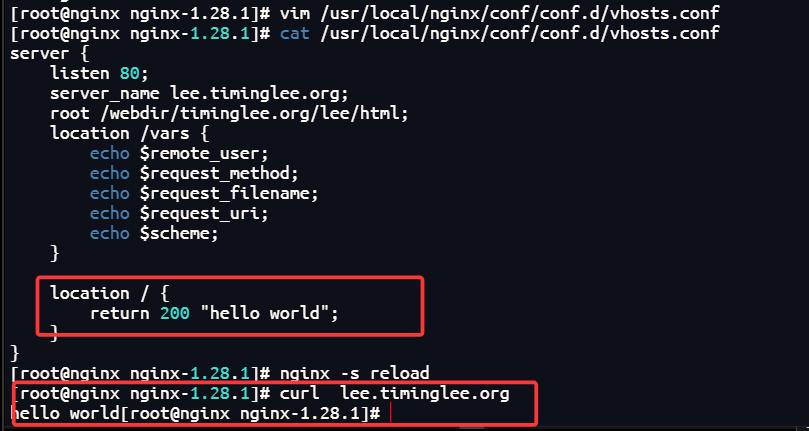
bash
#return
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    root /webdir/timinglee.org/lee/html;
    location /vars {
        echo $remote_user;
        echo $request_method;
        echo $request_filename;
        echo $request_uri;
        echo $scheme;
    }

    location / {
        #直接返回 HTTP 状态码 200,表示请求成功。
        return 200 "hello world";
    }
}
[root@Nginx ~] nginx -s reload
[root@Nginx ~] curl  lee.timinglee.org
hello world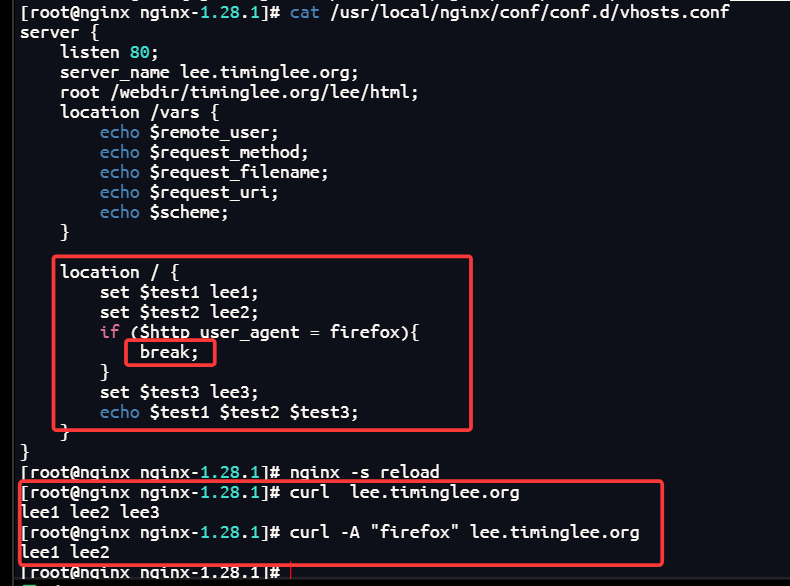
十四.Nginx反向代理
1.实验环境
bash
#172.25.254.10 RS1	172.25.254.20 RS2


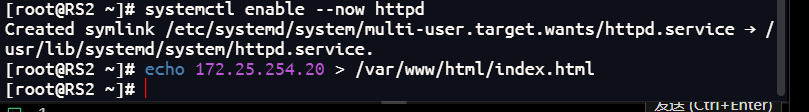
[root@RSX ~] dnf install httpd -y
[root@RSX ~] systemctl enable --now httpd
[root@RSX ~] echo 172.25.254.20 > /var/www/html/index.html


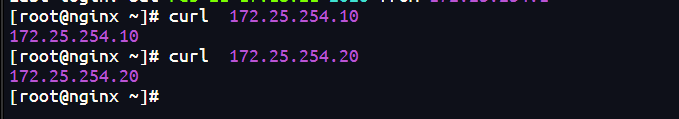
#测试 在Nginx主机中
[root@Nginx ~] curl  172.25.254.10
172.25.254.10
[root@Nginx ~] curl  172.25.254.20
172.25.254.20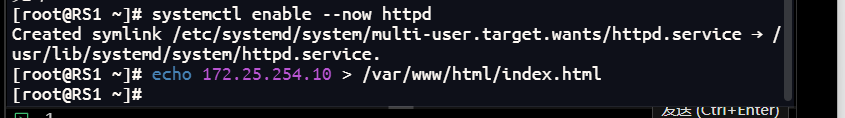
2.简单的代理方法
bash
[root@RS2 ~] mkdir -p /var/www/html/web
[root@RS2 ~] echo 172.25.254.20 web > /var/www/html/web/index.html


[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;

    #所有访问 lee.timinglee.org 的根路径请求,都会被代理到 172.25.254.10
    location / {
        proxy_pass http://172.25.254.10:80;
    }

    #所有访问 lee.timinglee.org/web 的请求,都会被代理到 172.25.254.20
    location /web {
        proxy_pass http://172.25.254.20:80;
    }

}

[root@Nginx ~] nginx -s reload
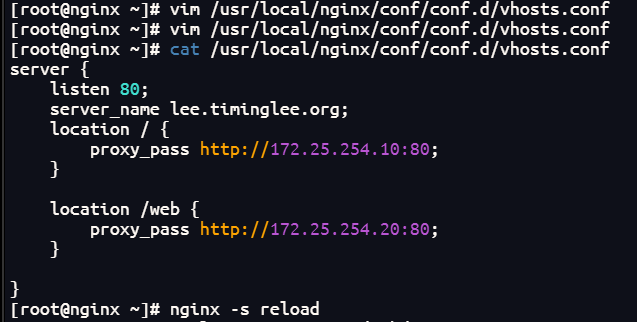
测试:
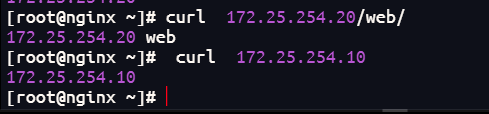
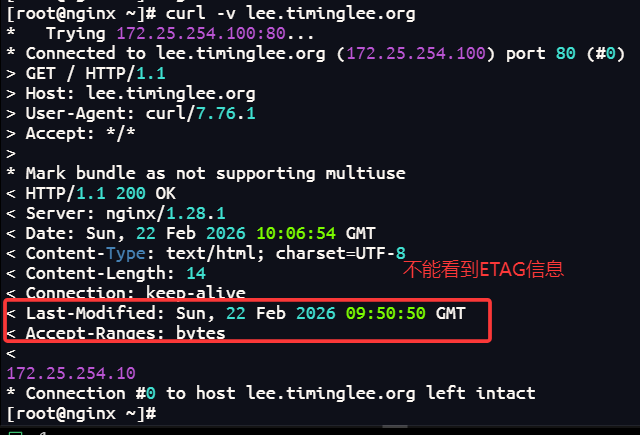
3.proxy_hide_header filed
proxy_hide_header:用于隐藏从上游服务器(后端)传递给客户端的 HTTP 响应头。
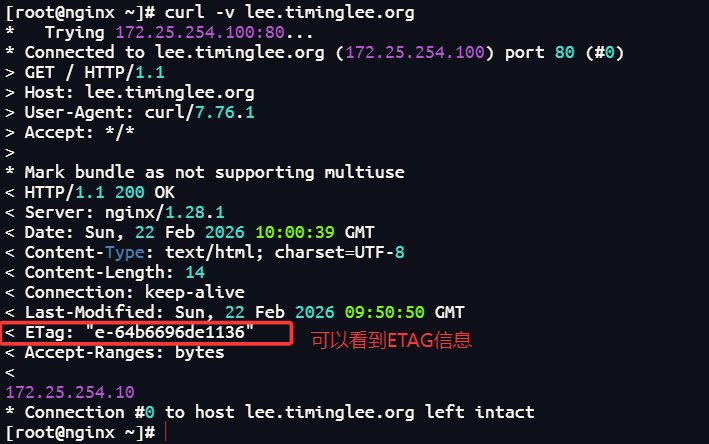
bash
[root@nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf

    server {
    listen 80;
    server_name lee.timinglee.org;
    location / {
        proxy_pass http://172.25.254.10:80;
        proxy_hide_header ETag;
    }

    location /web {
        proxy_pass http://172.25.254.20:80;
    }

}

[root@nginx ~] nginx -s reload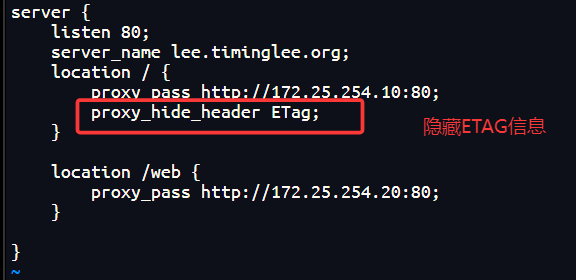
测试:
4.proxy_pass_header
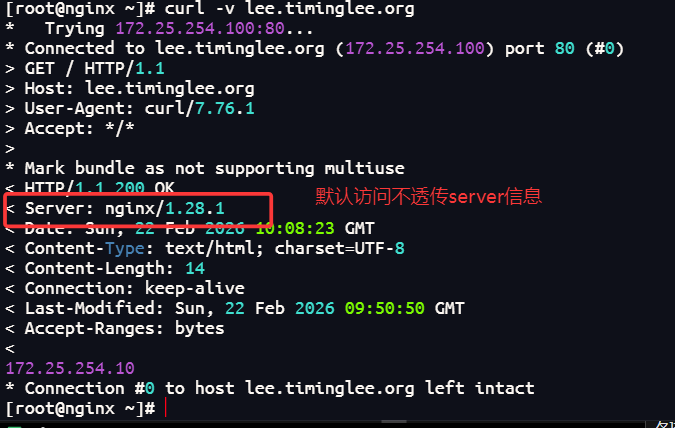
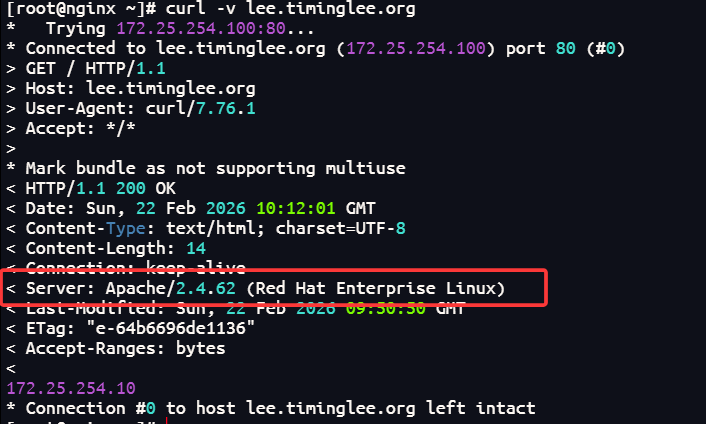
强制制 Nginx 将后端服务器返回的 Server 响应头,原封不动地透传给客户端:
bash
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    location / {
        proxy_pass http://172.25.254.10:80;
        #透传后端 Apache 服务器的信息。
        proxy_pass_header Server;
    }

    location /web {
        proxy_pass http://172.25.254.20:80;
    }

}

[root@Nginx ~] nginx -s reload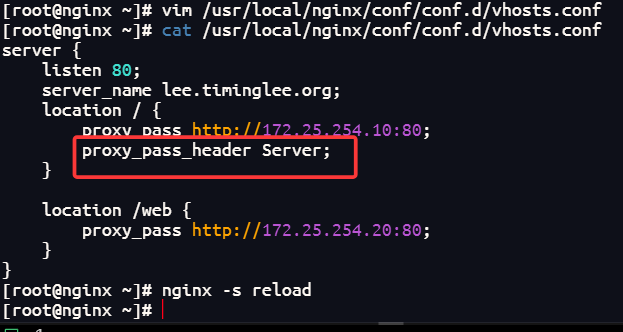
测试:
5.透传信息
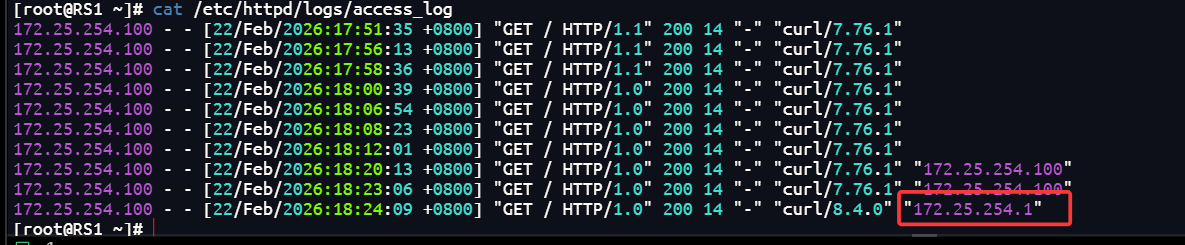
通过 X-Forwarded-For 头透传真实客户端 IP 地址到后端 Apache 服务器。
bash
#修改日志格式,在日志中增加 %{X-Forwarded-For}i 字段,
#用于记录从 Nginx 透传过来的真实客户端 IP。
[root@RS1 ~] vim /etc/httpd/conf/httpd.conf
    LogFormat "%h %l %u %t \"%r\" %>s %b \"%{Referer}i\" \"%{User-Agent}i\" \"%{X-Forwarded-For}i\"" combined

[root@RS1 ~] systemctl restart httpd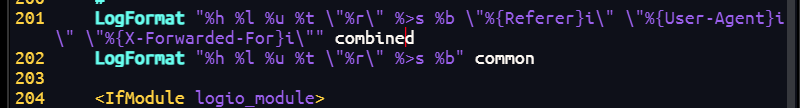
bash
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    location / {
        proxy_pass http://172.25.254.10:80;
    #将 Nginx 收到的客户端真实IP($remote_addr),通过X-Forwarded-For请求头发送给后端服务器。
        proxy_set_header X-Forwarded-For $remote_addr;

    }

    location /web {
        proxy_pass http://172.25.254.20:80;
    }
}

[root@Nginx ~] nginx -s reload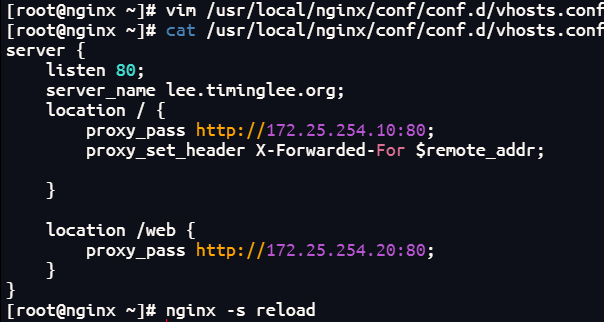
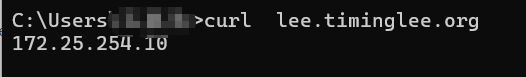
测试:
6.利用反向代理实现动静分离
环境配置:
bash
#在10中
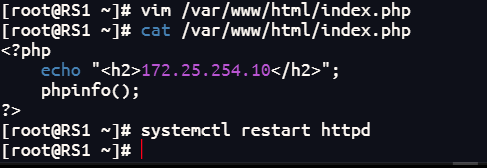
[root@RS1 ~] dnf install php -y
[root@RS1 ~] systemctl restart httpd

[root@RS1 ~] vim /var/www/html/index.php
<?php
    echo "<h2>172.25.254.10</h2>";
    phpinfo();
?>
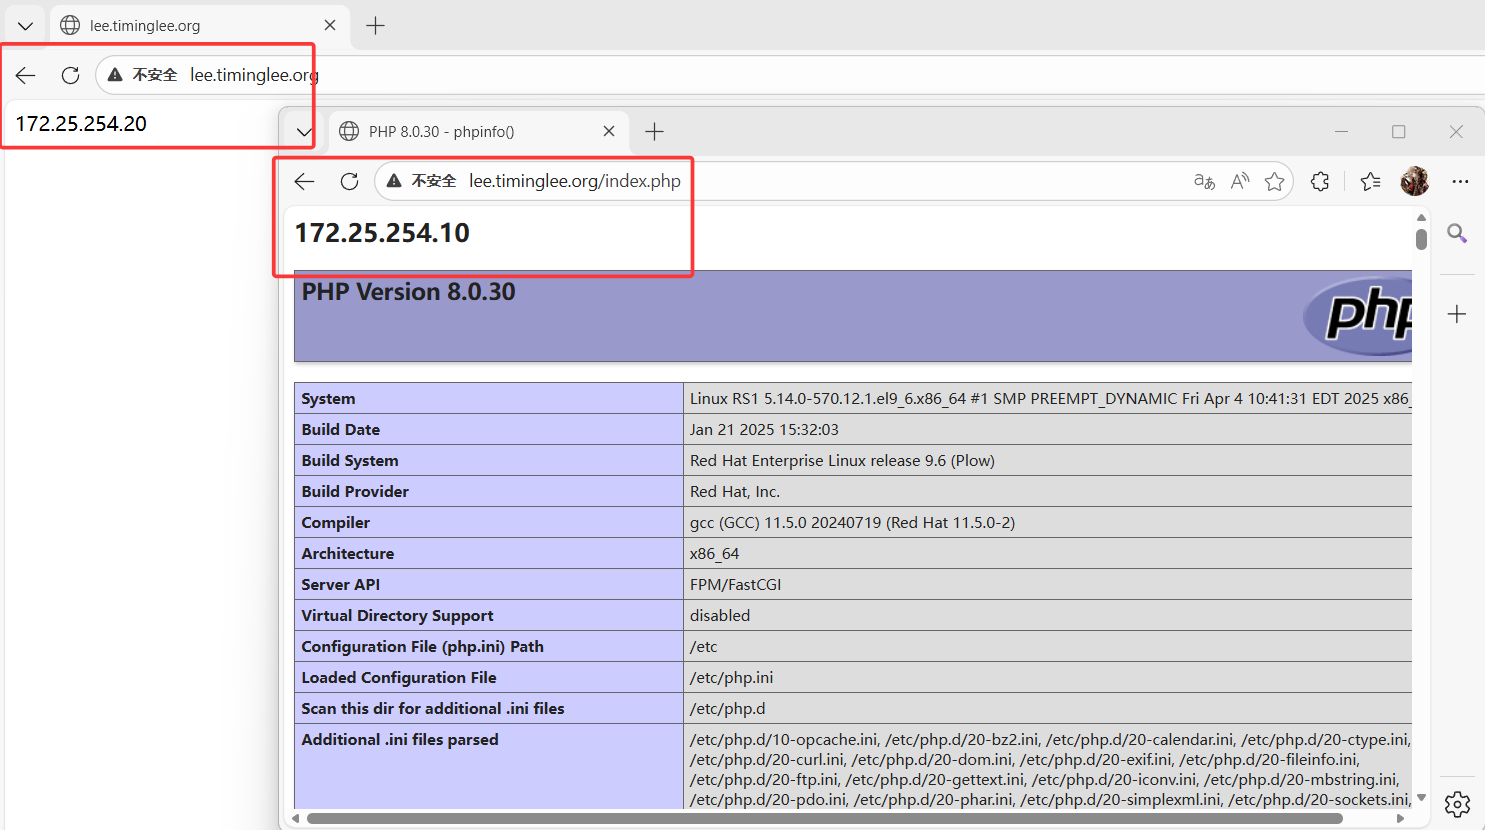
动静分离的实现:
bash
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 80;
    server_name lee.timinglee.org;
    location / {
        proxy_pass http://172.25.254.20:80;

    }

    location ~* \.(php|js)$ {
        proxy_pass http://172.25.254.10:80;
    }

}
[root@Nginx ~] nginx -s reload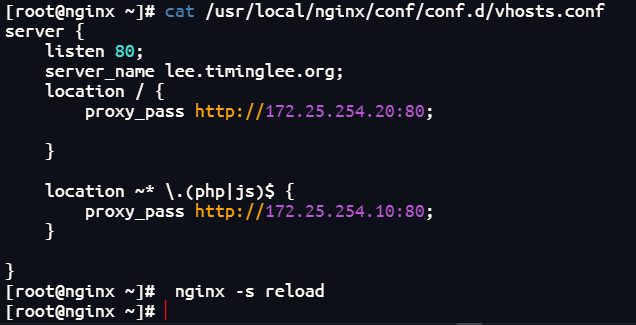
测试:
十五.缓存加速
1.当未启用缓存时进行压测
bash
[root@nginx ~] ab -n 10000 -c 50 lee.timinglee.org/index.php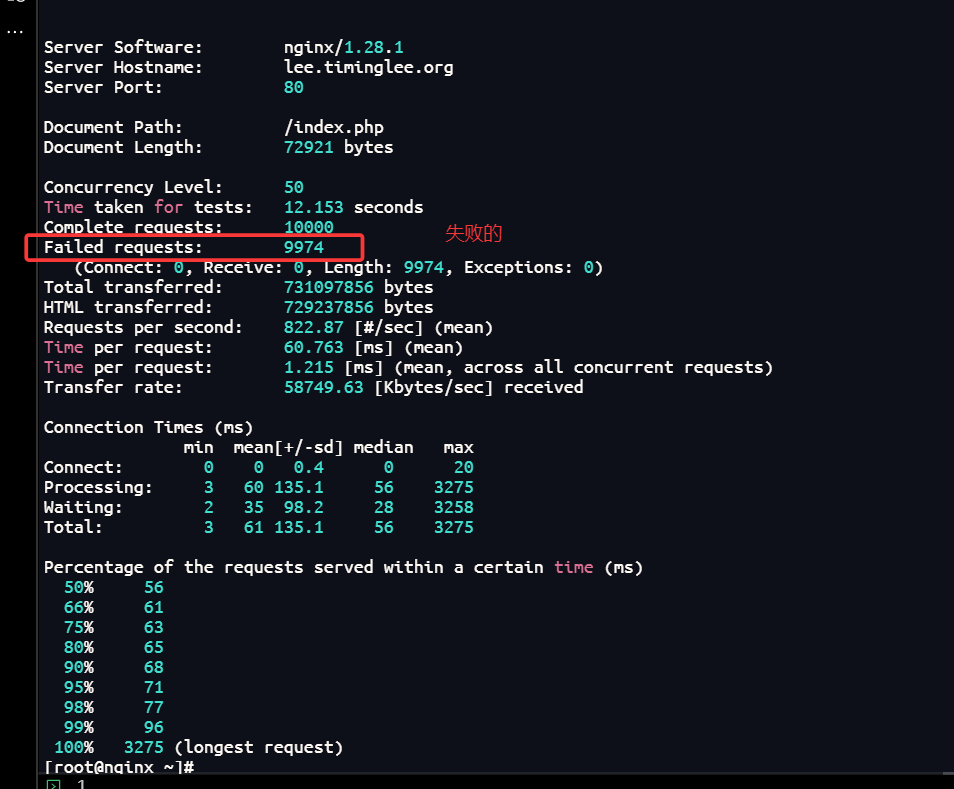
2.设定缓存加速
bash
[root@Nginx ~] vim /usr/local/nginx/conf/nginx.conf
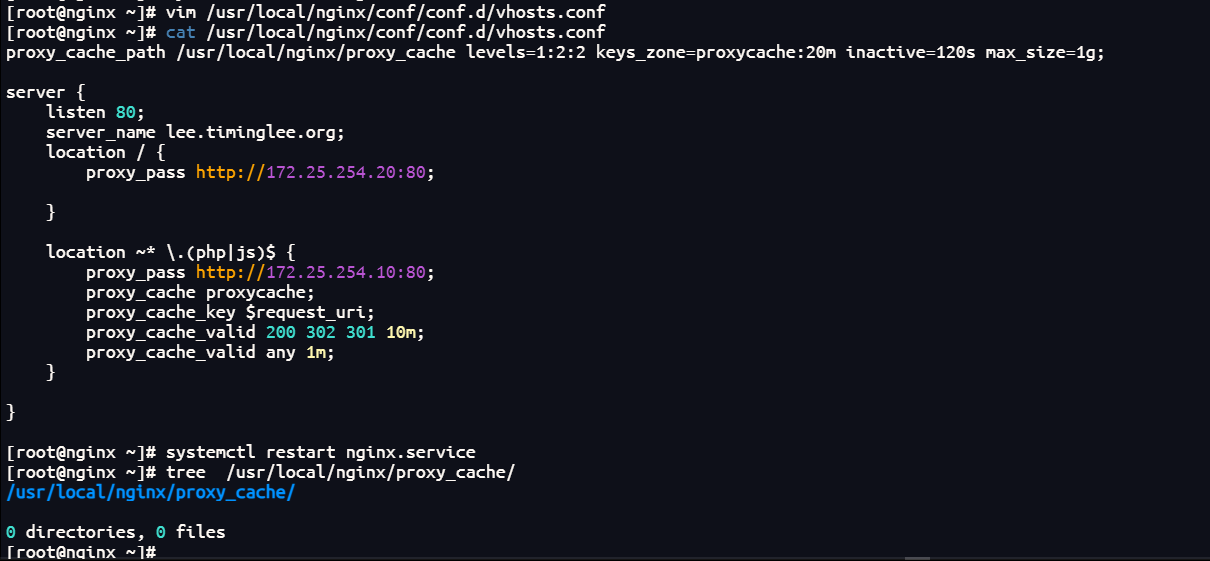
proxy_cache_path /usr/local/nginx/proxy_cache levels=1:2:2 keys_zone=proxycache:20m inactive=120s max_size=1g;

server {
    listen 80;
    server_name lee.timinglee.org;
    location / {
        proxy_pass http://172.25.254.20:80;

    }

    location ~* \.(php|js)$ {
        proxy_pass http://172.25.254.10:80;
        proxy_cache proxycache;  #引用全局定义的 proxycache 缓存区。
        proxy_cache_key $request_uri;  #以请求 URI 作为缓存键,相同 URI 的请求会命中缓存。
        proxy_cache_valid 200 302 301 10m;  #对 200、302、301 状态码的响应缓存 10 分钟。
        proxy_cache_valid any 1m;  #对其他所有状态码的响应缓存 1 分钟。
    }

}
测试:
bash
[root@nginx ~] ab -n 10000 -c 50 lee.timinglee.org/index.php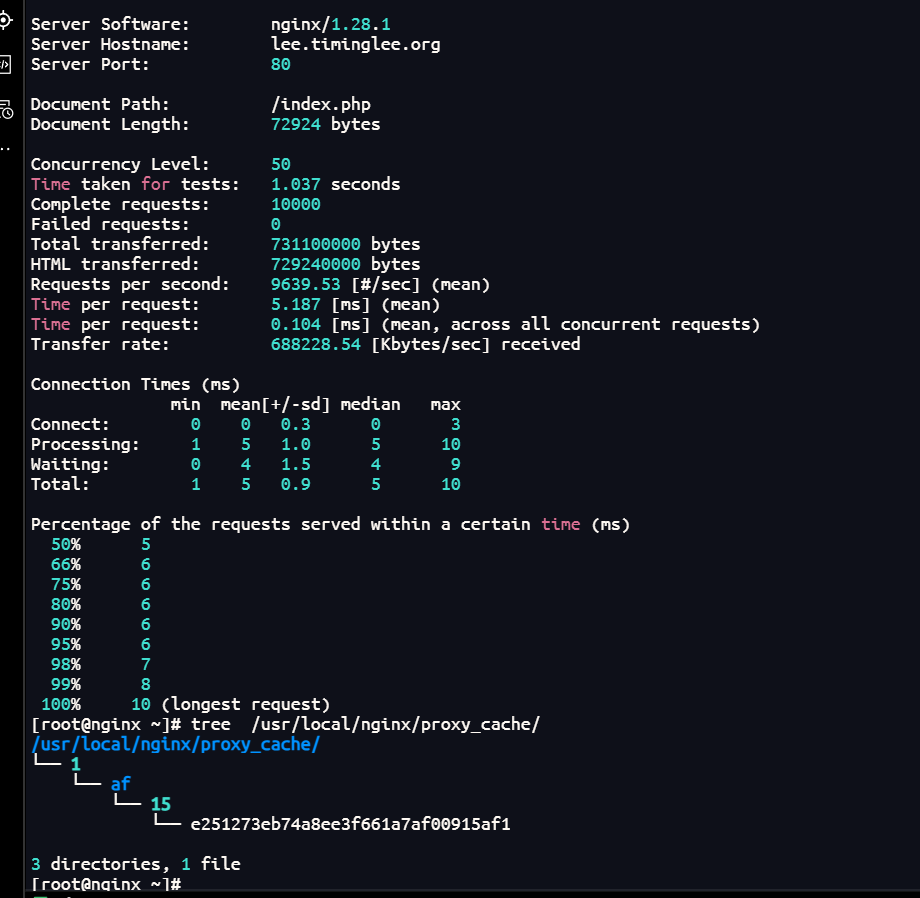
十六.反向代理负载均衡
bash
[root@Nginx ~] mkdir  /usr/local/nginx/conf/upstream/
[root@Nginx ~] vim /usr/local/nginx/conf/nginx.conf
events {
    worker_connections  10000;
    use epoll;
    accept_mutex on;
    multi_accept on;
}

http {
    include       mime.types;
    default_type  application/octet-stream;
	include "/usr/local/nginx/conf/upstream/*.conf";		#子配置目录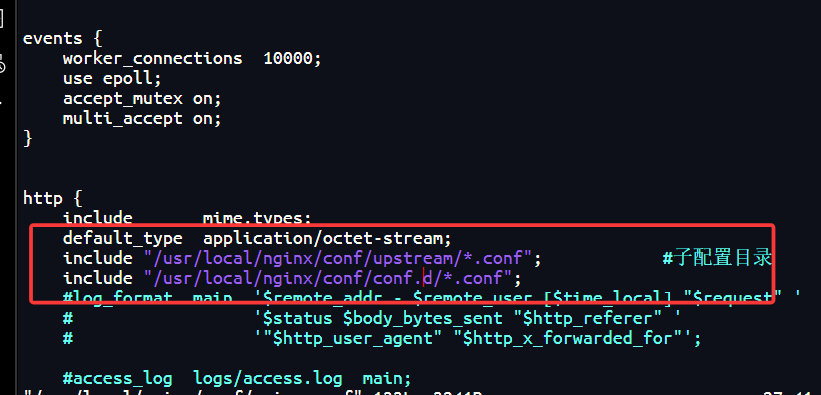
bash
[root@Nginx ~] vim /usr/local/nginx/conf/upstream/loadbalance.conf

#定义了一个名为 webserver 的服务器组,用于负载均衡
#weight=1:两台主服务器的权重相同,默认使用轮询策略分发请求。
#fail_timeout=15s max_fails=3:如果在 15 秒内连续 3 次请求失败,Nginx 会认为该服务器不可用,并暂时将其从负载均衡池中移除。
#backup:172.25.254.100:8888 被标记为备用服务器,只有当所有主服务器都不可用时,才会启用它
upstream webserver {
    server 172.25.254.10:80 weight=1 fail_timeout=15s max_fails=3;
    server 172.25.254.20:80 weight=1 fail_timeout=15s max_fails=3;
    server 172.25.254.100:8888 backup;

}
server {
    listen 80;
    server_name www.timinglee.org;

    location ~ / {
        proxy_pass http://webserver;
    }
}

[root@Nginx ~] mkdir  /webdir/timinglee.org/error/html -p
[root@Nginx ~] echo error > /webdir/timinglee.org/error/html/index.html

#配置了一个监听 8888 端口的站点,作为故障转移时的 "错误页面" 或 "维护页面"。
[root@Nginx ~] vim /usr/local/nginx/conf/conf.d/vhosts.conf
server {
    listen 8888;
    root /webdir/timinglee.org/error/html;
}

[root@nginx ~] systemctl restart nginx.service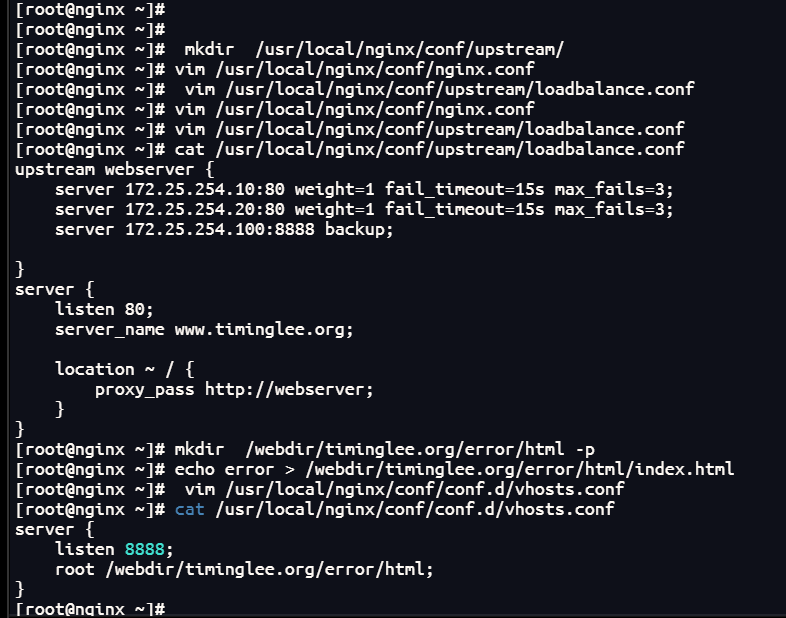
测试:
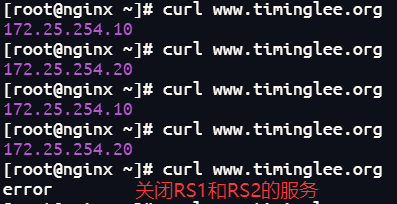
十七.PHP的源码编译
1.下载源码包
bash
[root@Nginx ~] wget https://www.php.net/distributions/php-8.3.30.tar.gz
[root@Nginx ~] wget https://mirrors.aliyun.com/rockylinux/9.7/devel/x86_64/os/Packages/o/oniguruma-devel-6.9.6-1.el9.6.x86_64.rpm     #依赖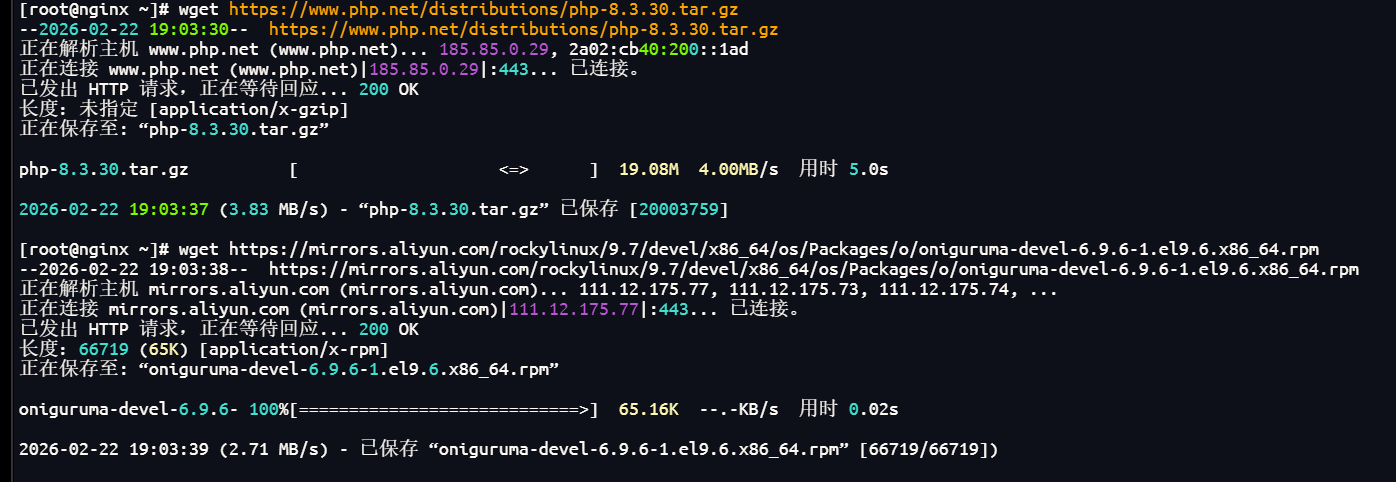
2.解压
bash
[root@Nginx ~] tar zxf php-8.3.30.tar.gz
[root@Nginx ~] ls
[root@Nginx ~] cd php-8.3.30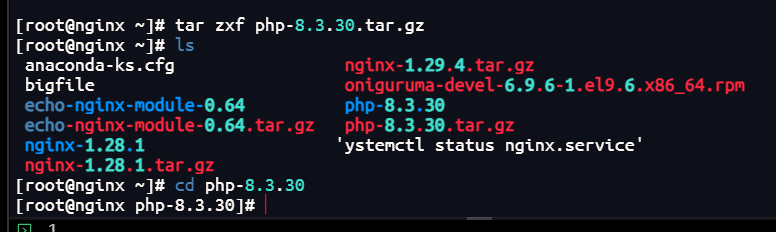
3.源码编译
bash
[root@Nginx ~] dnf install gcc systemd-devel-252-51.el9.x86_64 libxml2-devel.x86_64 sqlite-devel.x86_64  libcurl-devel.x86_64  libpng-devel.x86_64 oniguruma-devel-6.9.6-1.el9.6.x86_64.rpm -y

[root@Nginx ~] cd php-8.3.30/
[root@Nginx php-8.3.30] ./configure \
--prefix=/usr/local/php \		#安装路径
--with-config-file-path=/usr/local/php/etc \	#指定配置路径
--enable-fpm  \			#用cgi方式启动程序
--with-fpm-user=nginx \	#指定运行用户身份
--with-fpm-group=nginx \
--with-curl \			#打开curl浏览器支持
--with-iconv \			#启用iconv函数,转换字符编码
--with-mhash \			#mhash加密方式扩展库
--with-zlib \			#支持zlib库,用于压缩http压缩传输
--with-openssl \		#支持ssl加密
--enable-mysqlnd \		#mysql数据库
--with-mysqli \
--with-pdo-mysql \
--disable-debug \		#关闭debug功能
--enable-sockets \		#支持套接字访问
--enable-soap \			#支持soap扩展协议
--enable-xml \			#支持xml
--enable-ftp \			#支持ftp
--enable-gd \			#支持gd库
--enable-exif \			#支持图片元数据
--enable-mbstring \		#支持多字节字符串
--enable-bcmath \		#打开图片大小调整,用到zabbix监控的时候用到了这个模块
--with-fpm-systemd		#支持systemctl 管理cgi

./configure --prefix=/usr/local/php --with-config-file-path=/usr/local/php/etc --enable-fpm --with-fpm-user=nginx --with-fpm-group=nginx --with-curl --with-iconv --with-mhash --with-zlib --with-openssl --enable-mysqlnd --with-mysqli --with-pdo-mysql --disable-debug --enable-sockets --enable-soap --enable-xml --enable-ftp --enable-gd --enable-exif --enable-mbstring --enable-bcmath --with-fpm-systemd

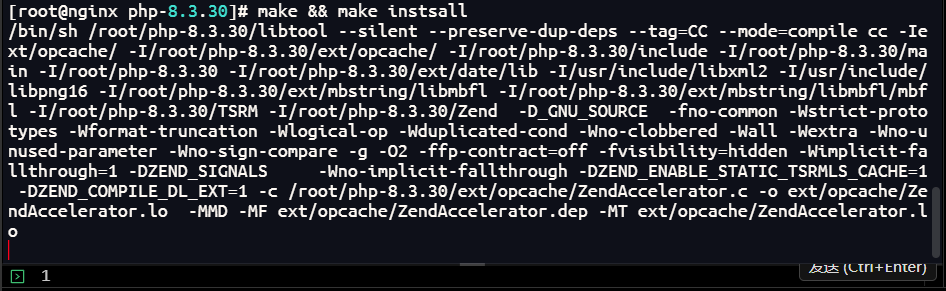
[root@Nginx php-8.3.30] make && make install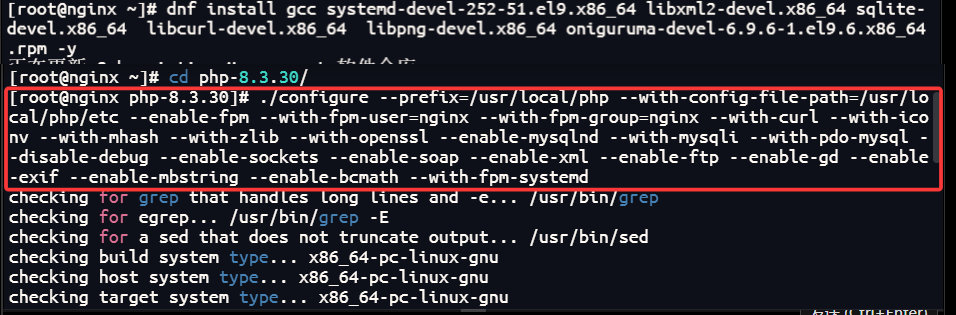
4.配置PHP
bash
[root@Nginx php-8.3.30] cd /usr/local/php/etc
[root@Nginx etc] cp -p php-fpm.conf.default  php-fpm.conf

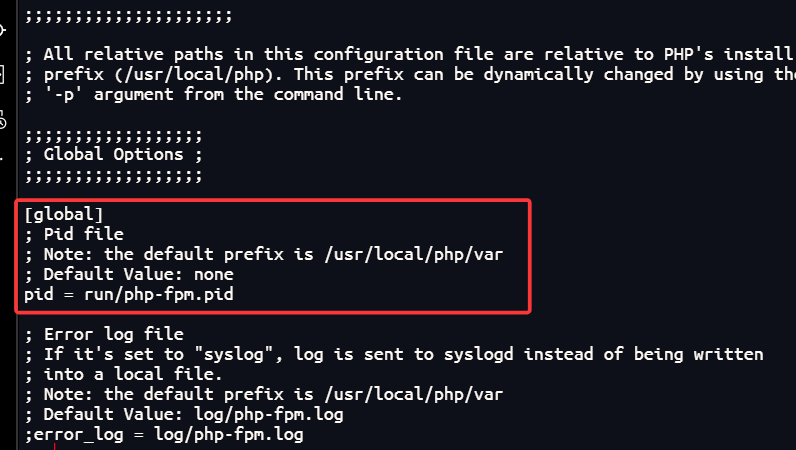
[root@Nginx etc] vim php-fpm.conf
[global]
; Pid file
; Note: the default prefix is /usr/local/php/var
; Default Value: none
#使得 PHP-FPM 监听在所有网卡的 9000 端口,允许其他服务器(如 Nginx)通过网络连接处理 PHP 请求。
pid = run/php-fpm.pid


[root@Nginx etc] cd php-fpm.d/
[root@Nginx php-fpm.d] cp www.conf.default www.conf
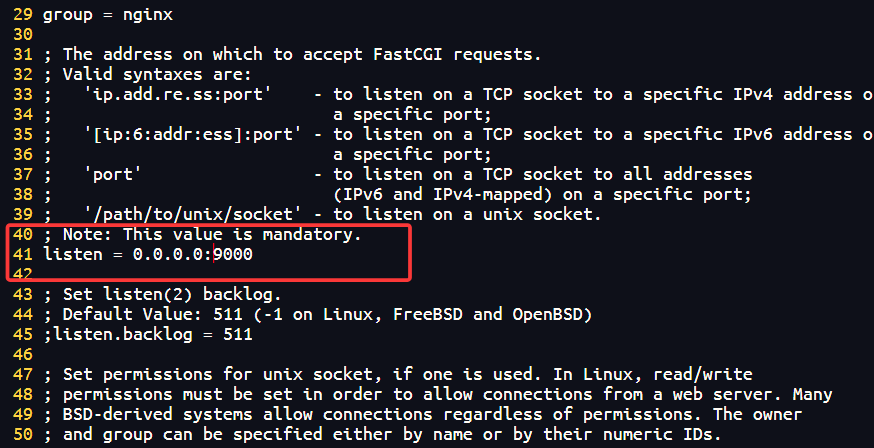
[root@Nginx php-fpm.d] vim www.conf
41 listen = 0.0.0.0:9000

[root@Nginx php-fpm.d] cp /root/php-8.3.30/php.ini-production  /usr/local/php/etc/php.ini

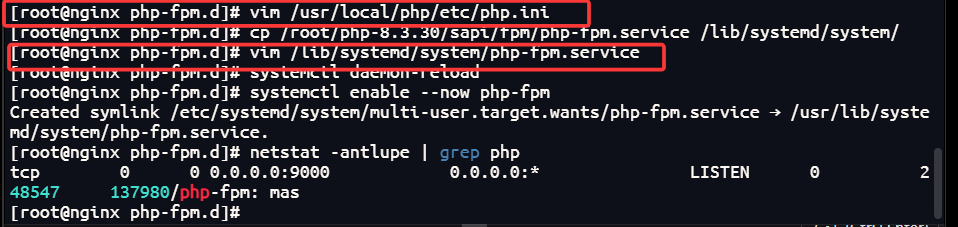
[root@Nginx php-fpm.d] vim /usr/local/php/etc/php.ini
#修改时区
989 date.timezone = Asia/Shangha

[root@Nginx ~] cp /root/php-8.3.30/sapi/fpm/php-fpm.service /lib/systemd/system/
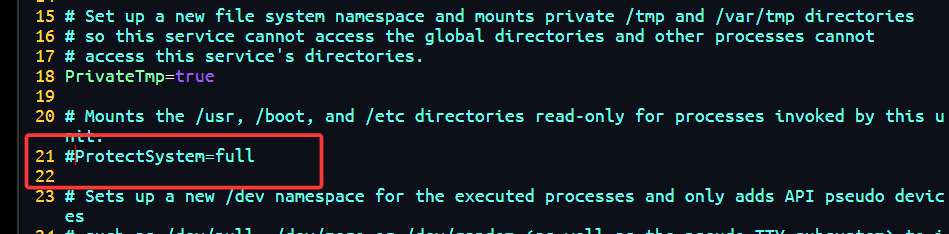
[root@Nginx ~] vim /lib/systemd/system/php-fpm.service

# Mounts the /usr, /boot, and /etc directories read-only for processes invoked by this unit.
#ProtectSystem=full		#注释此参数
[root@Nginx ~] systemctl daemon-reload
[root@Nginx ~] systemctl enable --now php-fpm

5.为php设定环境变量
bash
[root@Nginx ~] vim ~/.bash_profile
export PATH=$PATH:/usr/local/nginx/sbin:/usr/local/php/sbin:/usr/local/php/bin

[root@Nginx ~] source   ~/.bash_profile
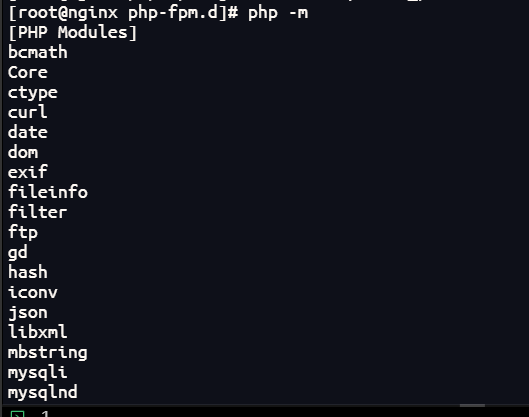
[root@Nginx ~] php -m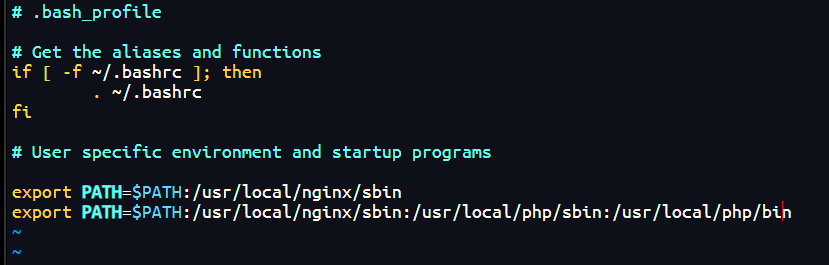
6.Nginx整合PHP
bash
[root@Nginx conf.d] mkdir  /webdir/timinglee.org/php/html -p
[root@Nginx conf.d] vim /webdir/timinglee.org/php/html/index.html
php.timinglee.org

[root@Nginx conf.d] vim /webdir/timinglee.org/php/html/index.php
<?php
  phpinfo();
?>

[root@Nginx ~] cd /usr/local/nginx/conf/conf.d/
[root@Nginx conf.d] vim php.conf
server {
  listen 80;
  server_name php.timinglee.org;
  root /webdir/timinglee.org/php/html;
  location ~ \.php$ {
    fastcgi_pass 127.0.0.1:9000;
    fastcgi_index index.php;
    include fastcgi.conf;
  }
}

[root@Nginx conf.d] nginx -s reload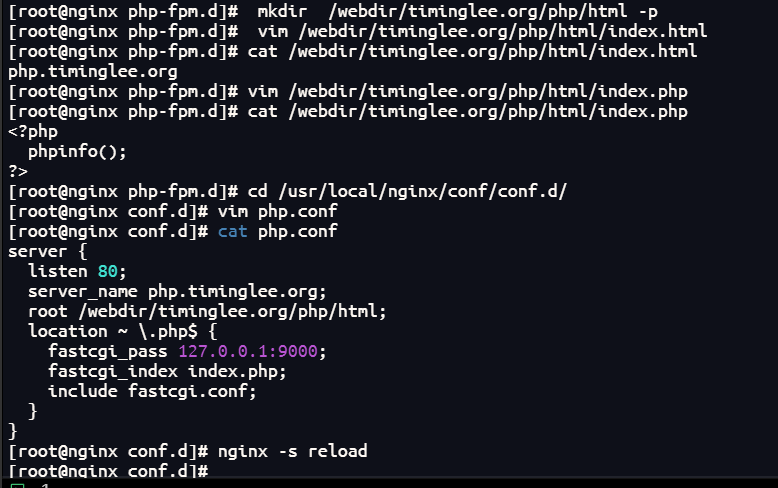
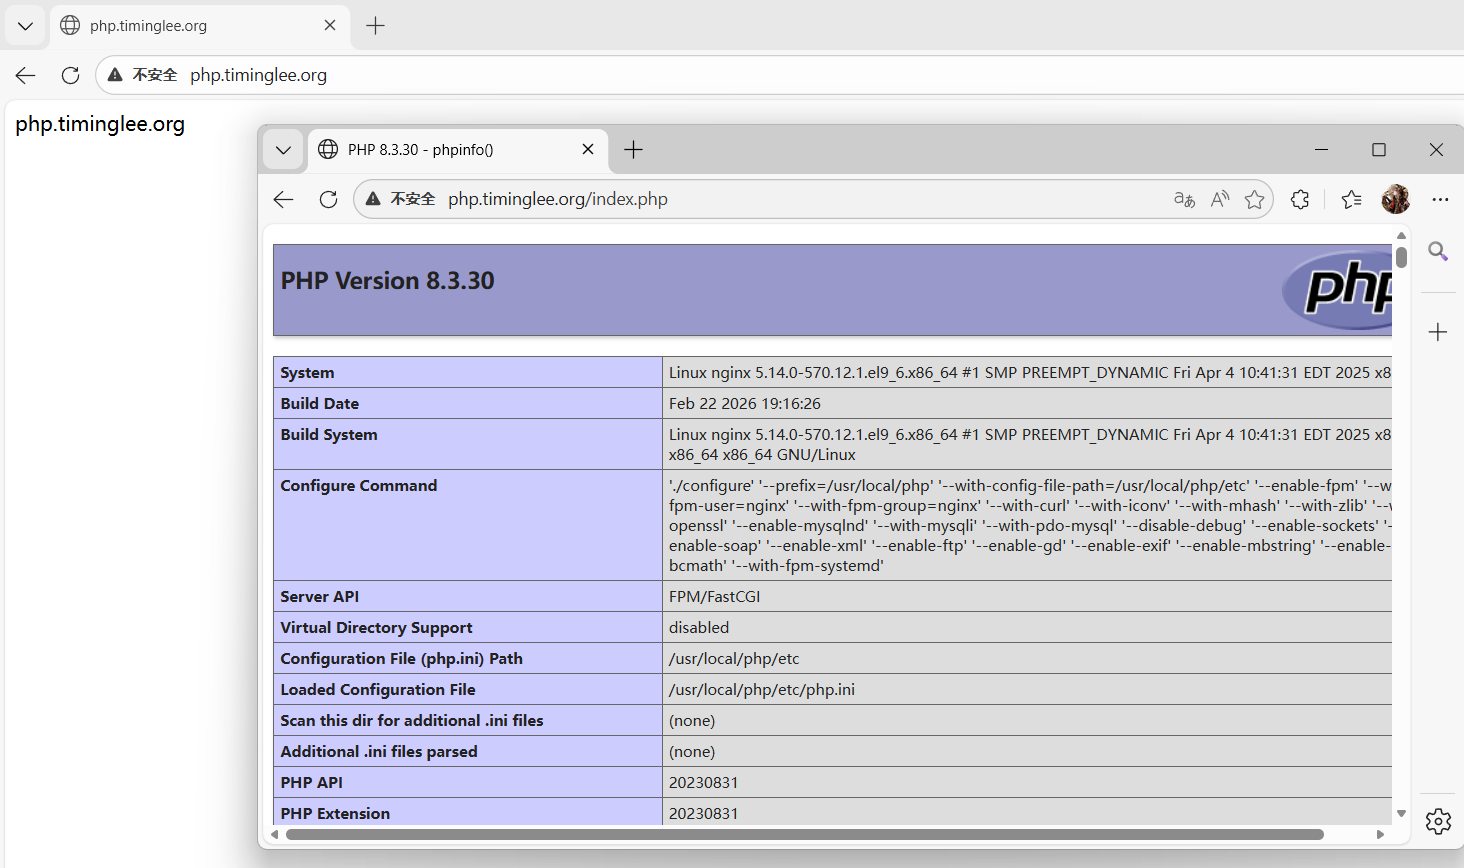
测试:
7.利用memcache实现php的缓存加速
1.安装memcache
bash
root@nginx conf.d] dnf install memcached.x86_64 -y
2.配置memcache
bash
[root@Nginx ~] vim /etc/sysconfig/memcached
PORT="11211"
USER="memcached"
MAXCONN="1024"
CACHESIZE="64"
OPTIONS="-l 0.0.0.0,::1"

[root@Nginx ~] systemctl enable --now memcached.service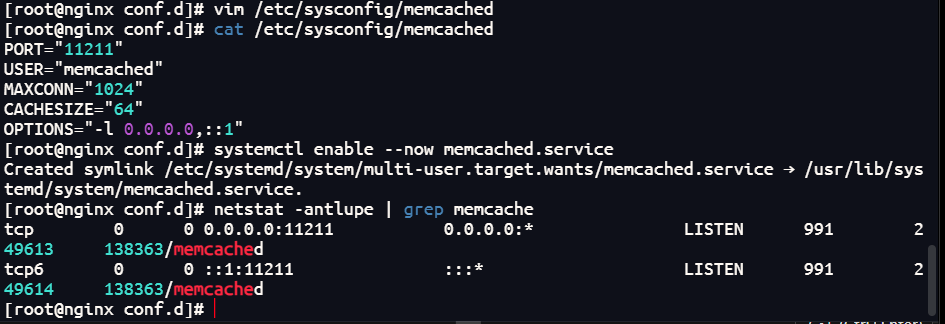
3.升级php对于memcache的支持
bash
[root@Nginx ~] php -m	#查看php支持的插件

[root@Nginx ~] tar zxf memcache-8.2.tgz
[root@Nginx ~] cd memcache-8.2/
[root@Nginx memcache-8.2] dnf install autoconf -y
[root@Nginx memcache-8.2] phpize
[root@Nginx memcache-8.2] ./configure  && make && make install

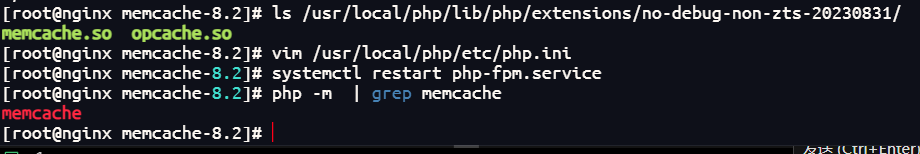
[root@Nginx memcache-8.2] ls /usr/local/php/lib/php/extensions/no-debug-non-zts-20230831/
memcache.so  opcache.so

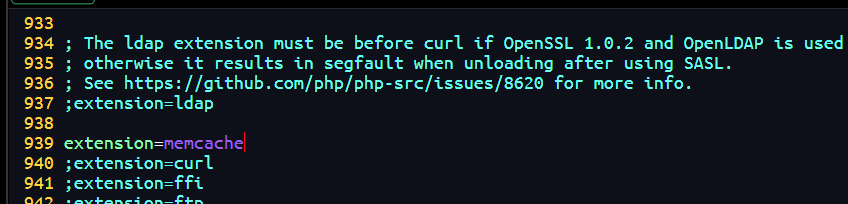
[root@Nginx memcache-8.2] vim /usr/local/php/etc/php.ini
939  extension=memcache

[root@Nginx memcache-8.2] systemctl restart php-fpm.service
[root@Nginx memcache-8.2] php -m  | grep memcache
memcache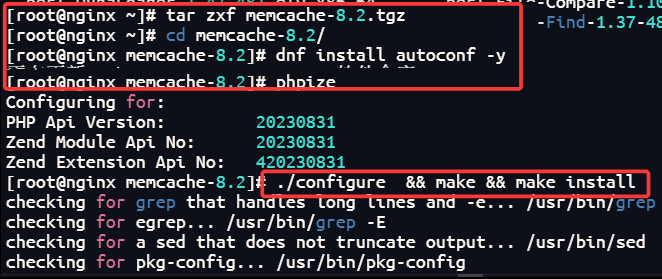
4.测试性能
bash
[root@Nginx memcache-8.2] vim memcache.php
define('ADMIN_USERNAME','admin');   // Admin Username
define('ADMIN_PASSWORD','lee');     // Admin Password
$MEMCACHE_SERVERS[] = '172.25.254.100:11211'; // add more as an array
#$MEMCACHE_SERVERS[] = 'mymemcache-server2:11211'; // add more as an array

[root@Nginx memcache-8.2] cp -p memcache.php  /webdir/timinglee.org/php/html/
[root@Nginx memcache-8.2] cp -p example.php /webdir/timinglee.org/php/html/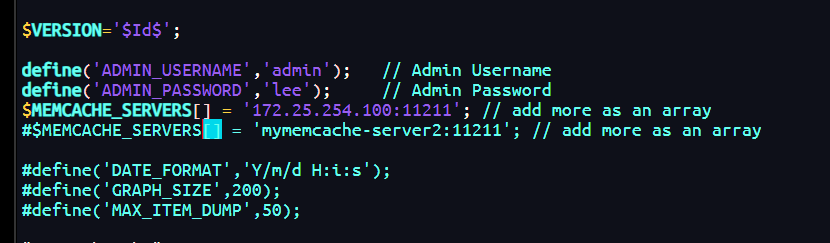
测试:
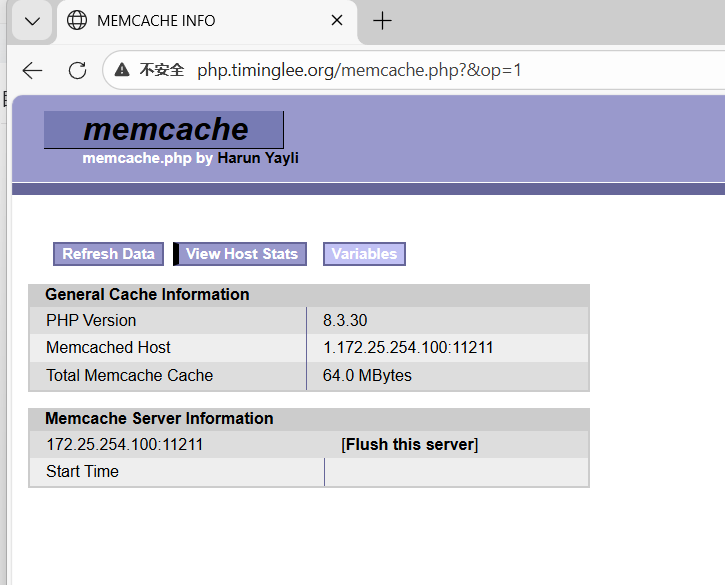
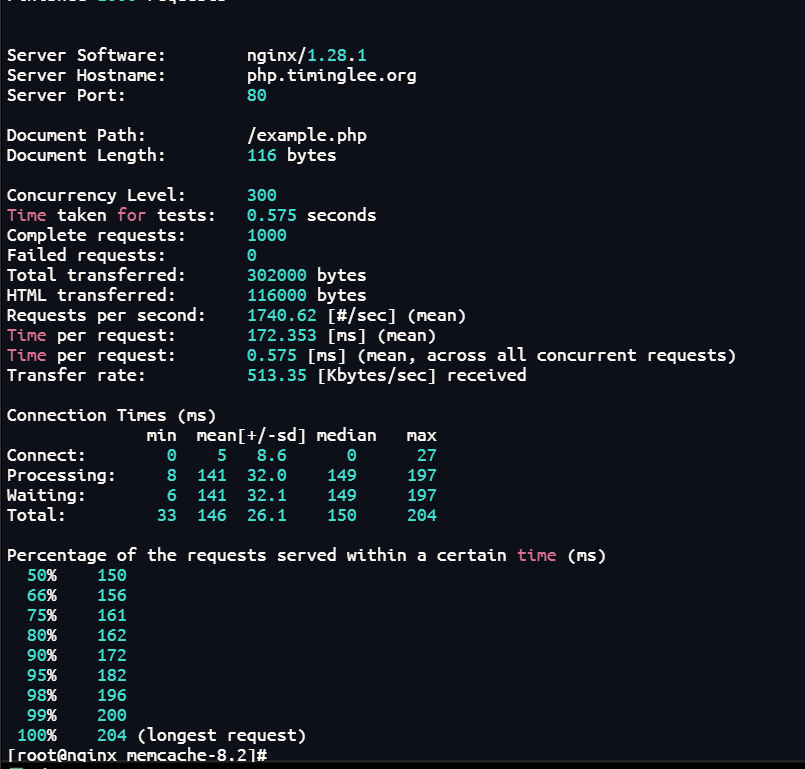
5.nginx+memcache实现高速缓存解
1.重新编译nginx
bash
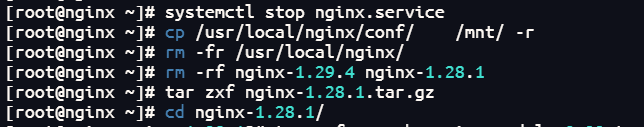
[root@Nginx ~] systemctl stop nginx.service
[root@Nginx ~] cp /usr/local/nginx/conf/    /mnt/ -r
[root@Nginx ~] rm -fr /usr/local/nginx/

[root@Nginx ~] rm -rf nginx-1.29.4 nginx-1.28.1

[root@Nginx ~] tar zxf nginx-1.28.1.tar.gz
[root@Nginx ~] cd nginx-1.28.1/

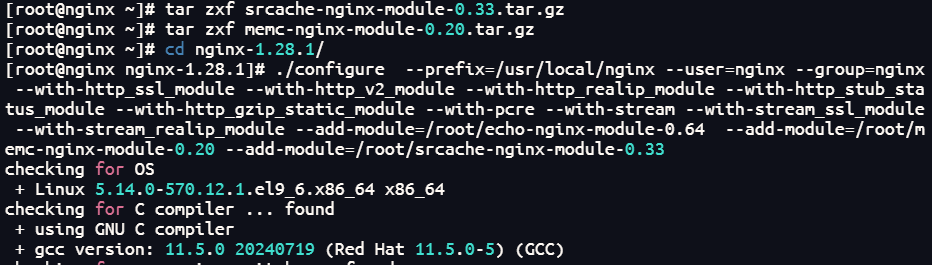
[root@Nginx ~] tar zxf srcache-nginx-module-0.33.tar.gz
[root@Nginx ~] tar zxf memc-nginx-module-0.20.tar.gz

[root@Nginx ~] cd nginx-1.28.1/
[root@Nginx nginx-1.28.1]# ./configure  --prefix=/usr/local/nginx --user=nginx --group=nginx --with-http_ssl_module --with-http_v2_module --with-http_realip_module --with-http_stub_status_module --with-http_gzip_static_module --with-pcre --with-stream --with-stream_ssl_module --with-stream_realip_module --add-module=/root/echo-nginx-module-0.64  --add-module=/root/memc-nginx-module-0.20 --add-module=/root/srcache-nginx-module-0.33
[root@Nginx nginx-1.28.1]# make && make install

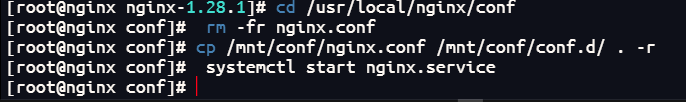
[root@Nginx ~] cd /usr/local/nginx/conf
[root@Nginx conf] rm -fr nginx.conf
[root@Nginx conf] cp /mnt/conf/nginx.conf /mnt/conf/conf.d/ . -r
[root@Nginx conf] systemctl start nginx.service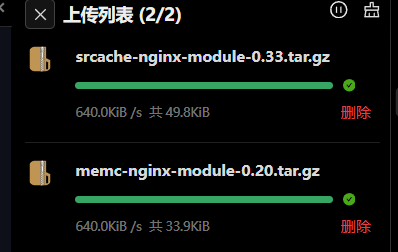
2.整合memcache
bash
[root@Nginx conf]# vim /usr/local/nginx/conf/conf.d/php.conf
upstream memcache {
   server 127.0.0.1:11211;
   keepalive 512;
}
server {
    listen 80;
    server_name php.timinglee.org;
    root /webdir/timinglee.org/php/html;
    index index.php index.html;

    location /memc {
        internal;
        memc_connect_timeout 100ms;
        memc_send_timeout 100ms;
        memc_read_timeout 100ms;
        set $memc_key $query_string;
        set $memc_exptime 300;
        memc_pass memcache;
    }
    location ~ \.php$ {
        set $key $uri$args;
        srcache_fetch GET /memc $key;
        srcache_store PUT /memc $key;
        fastcgi_pass 127.0.0.1:9000;
        fastcgi_index index.php;
        include fastcgi.conf;
  }
}

[root@Nginx conf] nginx  -s reload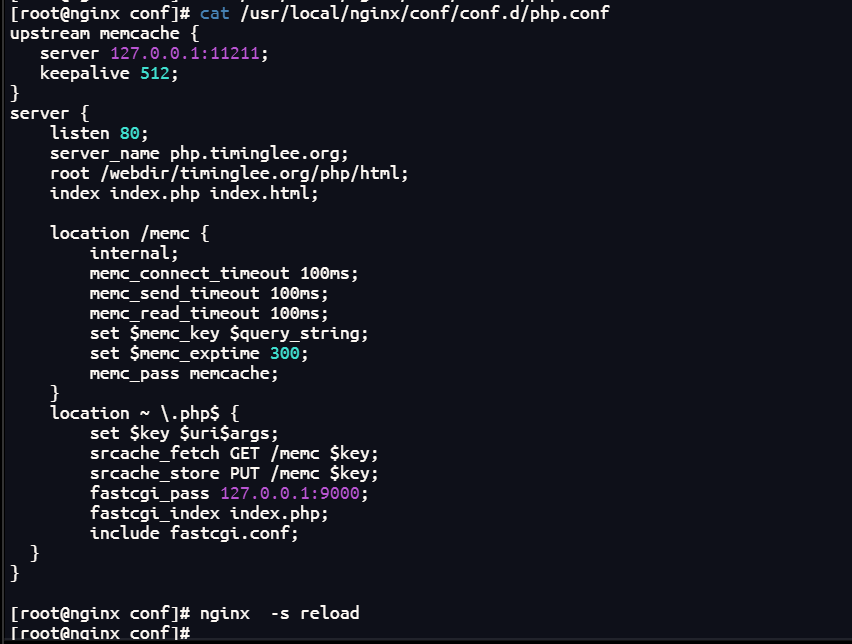
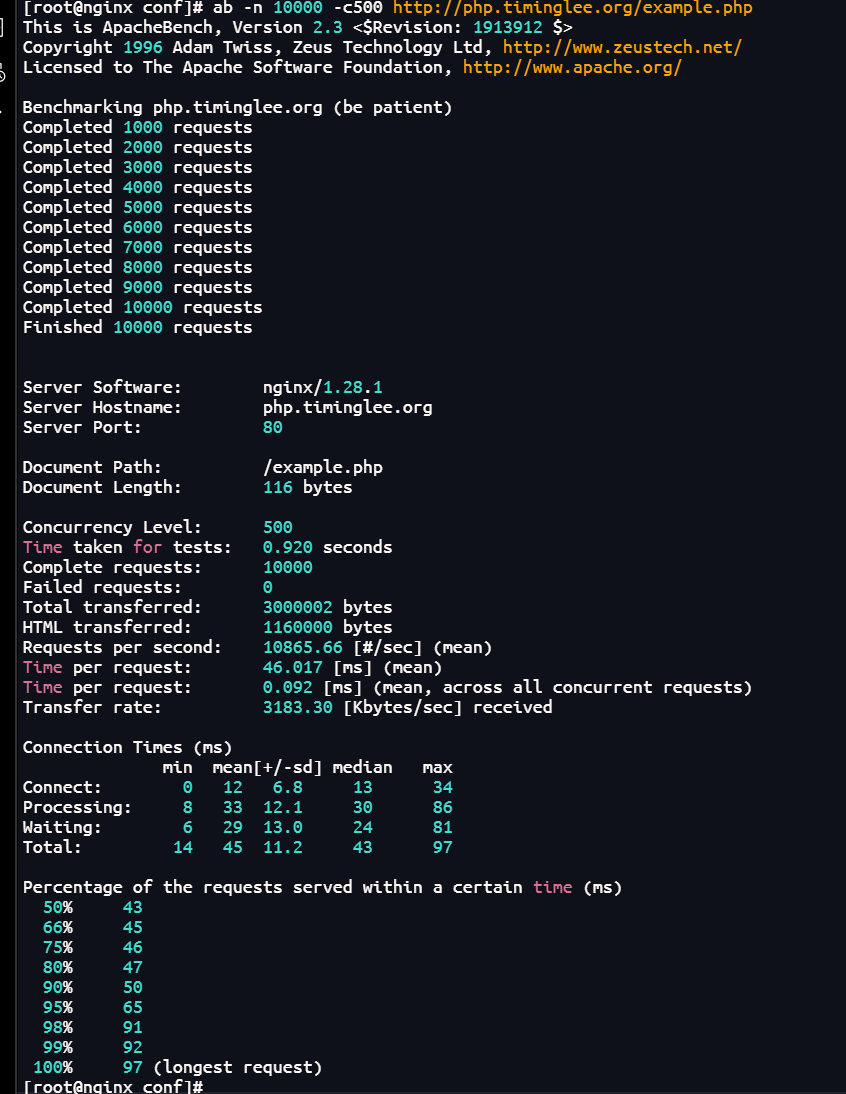
测试:
十八.Nginx的四层负载均衡代理
1.实验环境(Mysql)
bash
[root@RS1 ~] dnf install mariadb-server -y
[root@RS2 ~]  dnf install mariadb-server -y

[root@RS1 ~] vim /etc/my.cnf.d/mariadb-server.cnf
server-id=10

[root@RS2 ~] vim /etc/my.cnf.d/mariadb-server.cnf
server-id=20
[root@RS1 ~] systemctl enable --now mariadb
[root@RS2 ~] systemctl enable --now mariadb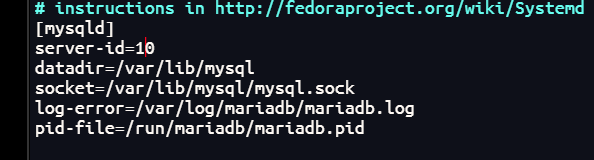
bash
[root@RS1 ~] mysql

MariaDB [(none)]> CREATE USER lee@'%' IDENTIFIED BY 'lee';
Query OK, 0 rows affected (0.001 sec)

MariaDB [(none)]> GRANT ALL ON *.* TO lee@'%';
Query OK, 0 rows affected (0.001 sec)

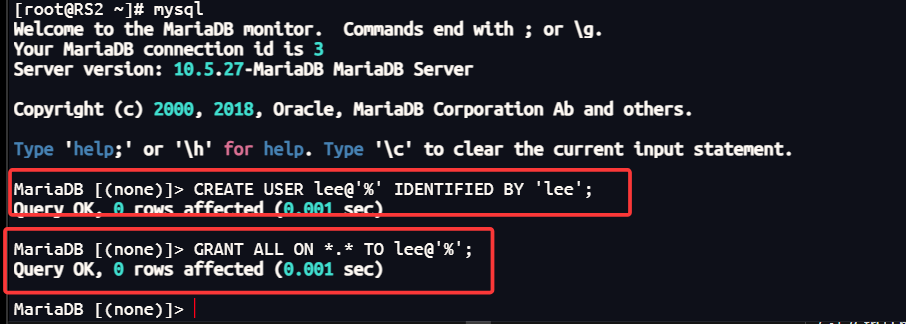
[root@RS2 ~] mysql

MariaDB [(none)]>  CREATE USER lee@'%' IDENTIFIED BY 'lee';
Query OK, 0 rows affected (0.001 sec)

MariaDB [(none)]> GRANT ALL ON *.* TO lee@'%';
Query OK, 0 rows affected (0.001 sec)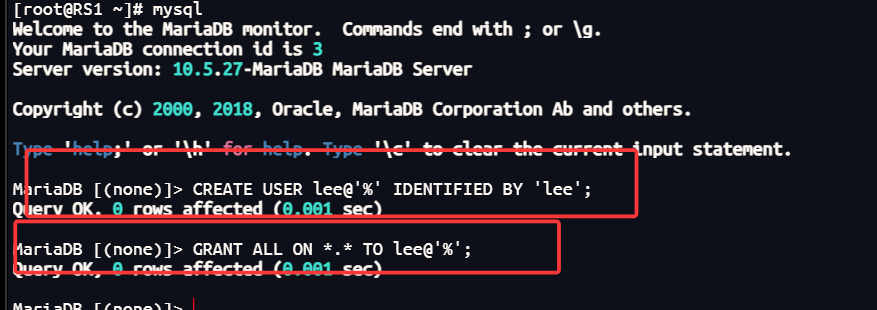
2.实验环境(dns)
bash
[root@RS1 ~]# dnf install bind -y
[root@RS2 ~]# dnf install bind -y

[root@RS1 ~]# vim /etc/named.conf
[root@RS2 ~]# vim /etc/named.conf

options {
//      listen-on port 53 { 127.0.0.1; };
//      listen-on-v6 port 53 { ::1; };
        directory       "/var/named";
        dump-file       "/var/named/data/cache_dump.db";
        statistics-file "/var/named/data/named_stats.txt";
        memstatistics-file "/var/named/data/named_mem_stats.txt";
        secroots-file   "/var/named/data/named.secroots";
        recursing-file  "/var/named/data/named.recursing";
//      allow-query     { localhost; };
        dnssec-validation no;

[root@RS1 ~]# vim /etc/named.rfc1912.zones
[root@RS2 ~]# vim /etc/named.rfc1912.zones

zone "timinglee.org" IN {
        type master;
        file "timinglee.org.zone";
        allow-update { none; };
};

[root@RS1 ~]# cd /var/named/
[root@RS2 ~]# cd /var/named/
[root@RS1 named]# cp -p named.localhost  timinglee.org.zone
[root@RS2 named]# cp -p named.localhost  timinglee.org.zone


[root@RS1 named]# vim timinglee.org.zone
$TTL 1D
@       IN SOA  dns.timingle.org. rname.invalid. (
                                        0       ; serial
                                        1D      ; refresh
                                        1H      ; retry
                                        1W      ; expire
                                        3H )    ; minimum
        NS      dns.timinglee.org.
dns     A       172.25.254.10

[root@RS2 named]# vim timinglee.org.zone
$TTL 1D
@       IN SOA  dns.timingle.org. rname.invalid. (
                                        0       ; serial
                                        1D      ; refresh
                                        1H      ; retry
                                        1W      ; expire
                                        3H )    ; minimum
        NS      dns.timinglee.org.
dns     A       172.25.254.20


[root@RS2 named]# systemctl enable --now named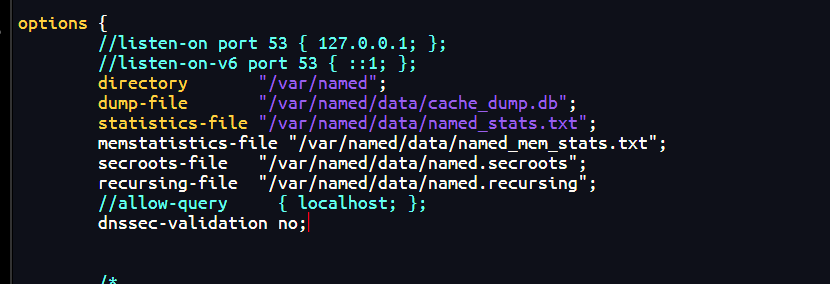
将重复配置删除或注释:
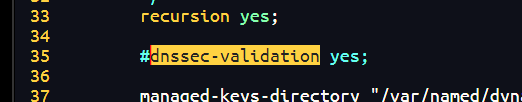
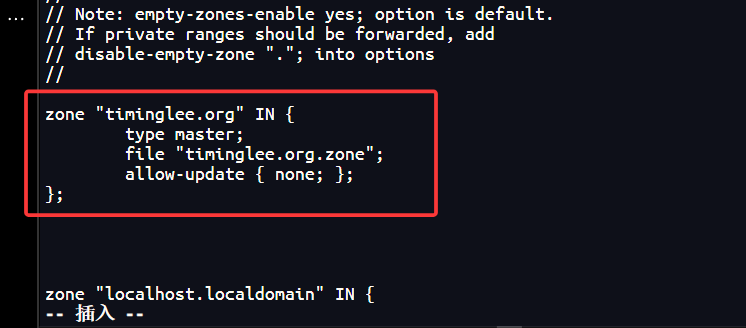
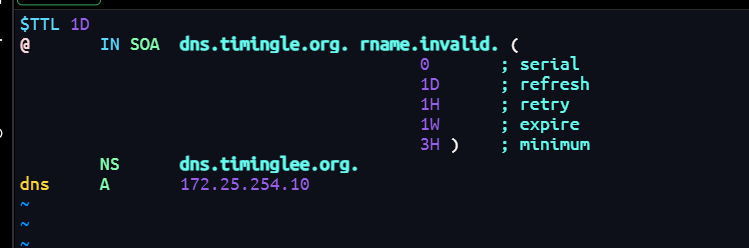
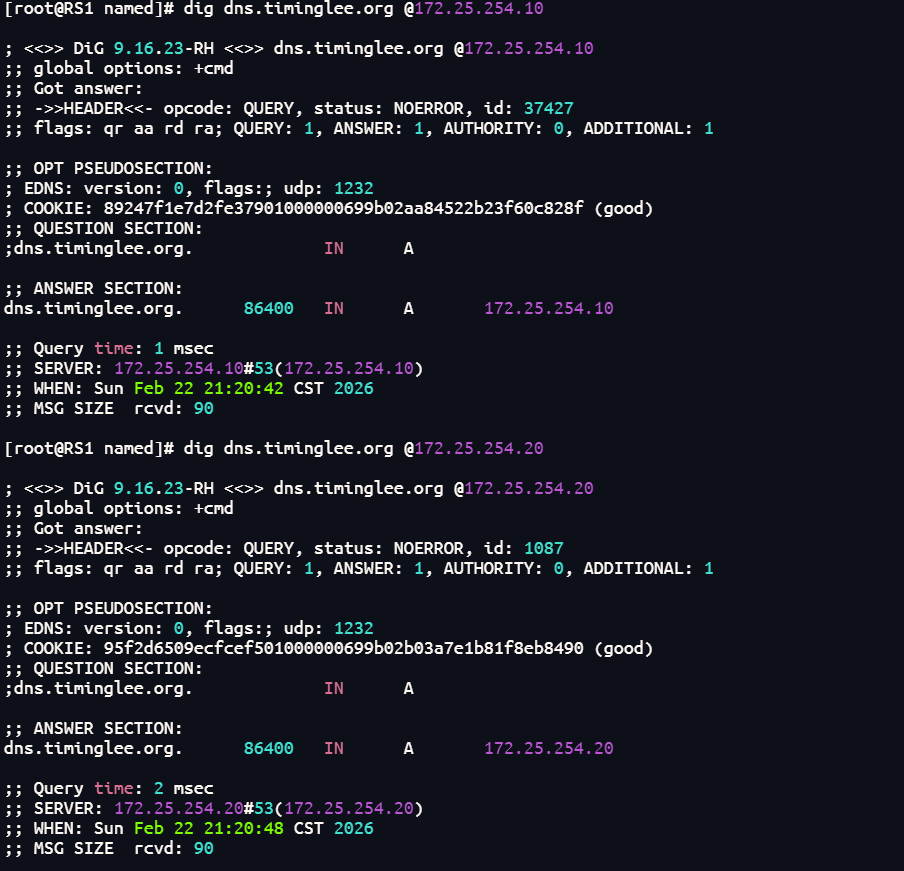
测试:
3.tcp四层负载
bash
[root@Nginx conf]# mkdir  /usr/local/nginx/conf/tcp -p
[root@Nginx conf]# mkdir  /usr/local/nginx/conf/udp -p
[root@Nginx conf]# vim /usr/local/nginx/conf/nginx.conf
include "/usr/local/nginx/conf/tcp/*.conf";

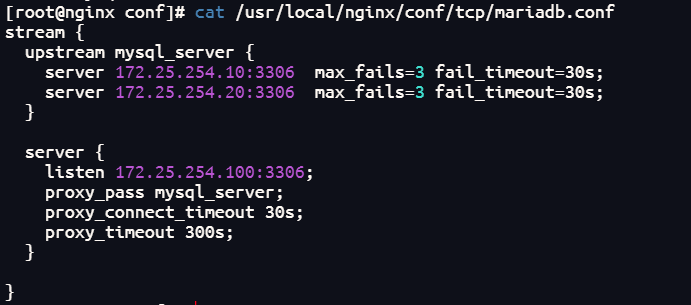
[root@Nginx conf]# vim /usr/local/nginx/conf/tcp/mariadb.conf
stream {
  upstream mysql_server {
    server 172.25.254.10:3306  max_fails=3 fail_timeout=30s;
    server 172.25.254.20:3306  max_fails=3 fail_timeout=30s;
  }

  server {
    listen 172.25.254.100:3306;
    proxy_pass mysql_server;
    proxy_connect_timeout 30s;
    proxy_timeout 300s;
  }

}
[root@Nginx conf]# nginx  -s reload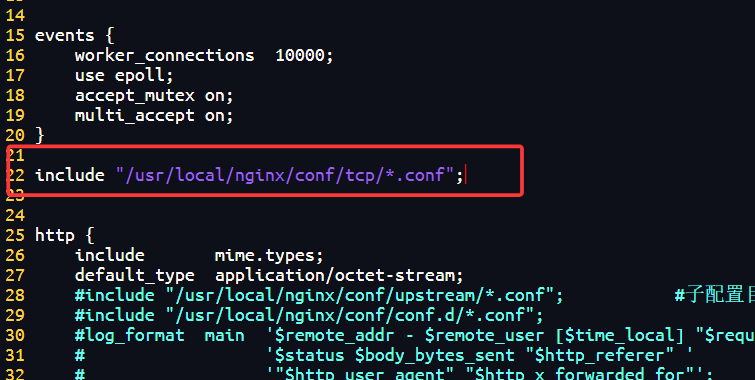
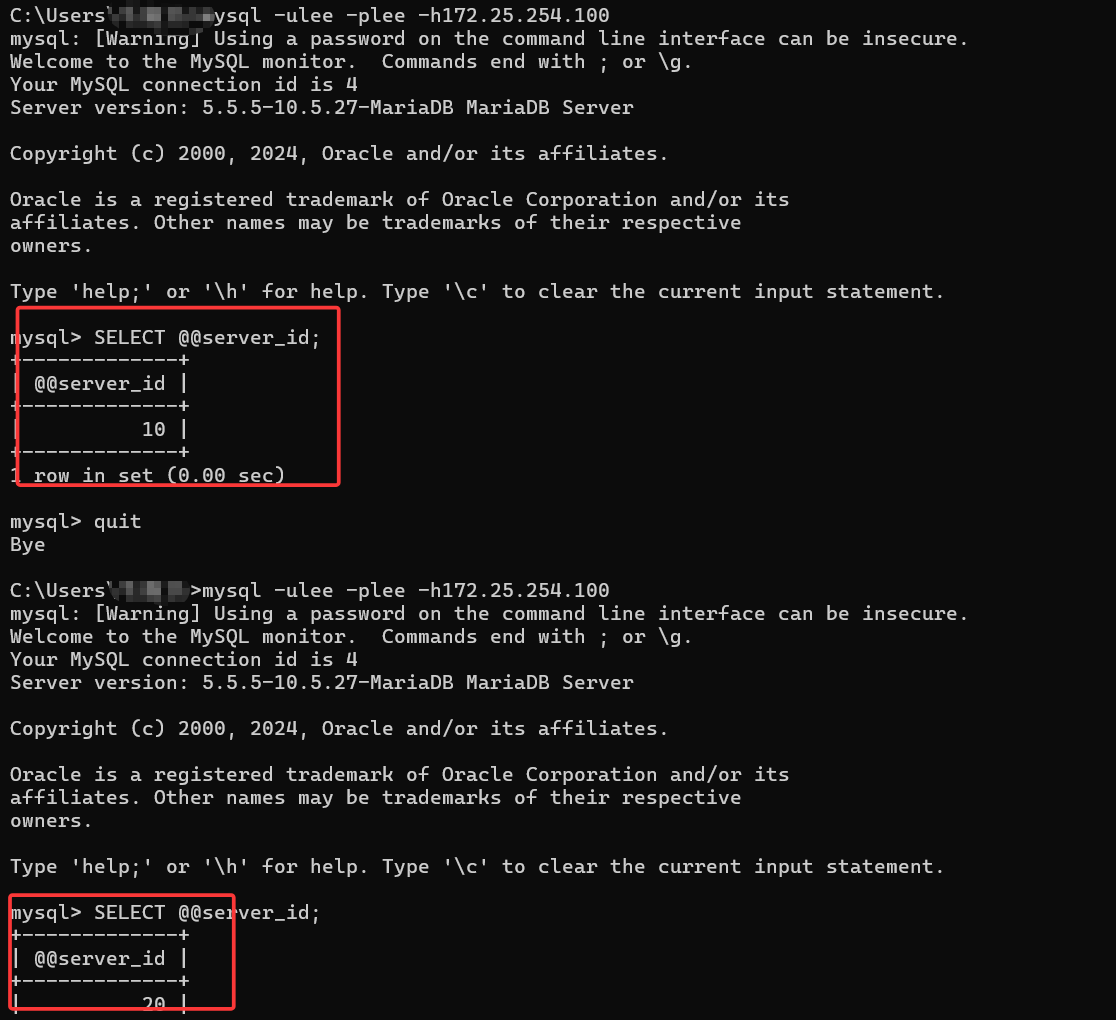
测试:
4.udp四层负载
bash
[root@Nginx ~]# vim /usr/local/nginx/conf/tcp/mariadb.conf
stream {
  upstream mysql_server {
    server 172.25.254.10:3306  max_fails=3 fail_timeout=30s;
    server 172.25.254.20:3306  max_fails=3 fail_timeout=30s;
  }

  upstream dns_server{
    server 172.25.254.10:53 max_fails=3 fail_timeout=30s;
    server 172.25.254.20:53 max_fails=3 fail_timeout=30s;
  }

  server {
    listen 172.25.254.100:3306;
    proxy_pass mysql_server;
    proxy_connect_timeout 30s;
    proxy_timeout 300s;
  }

  server {
        listen 172.25.254.100:53 udp;
        proxy_pass dns_server;
        proxy_timeout 1s;
        proxy_responses 1;
        error_log logs/dns.log;
    }
}
[root@Nginx ~]# nginx  -s reload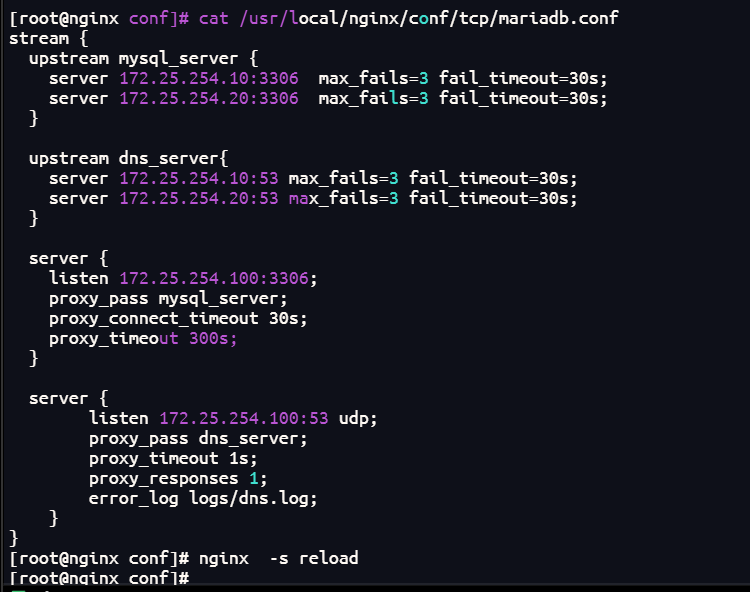
测试:
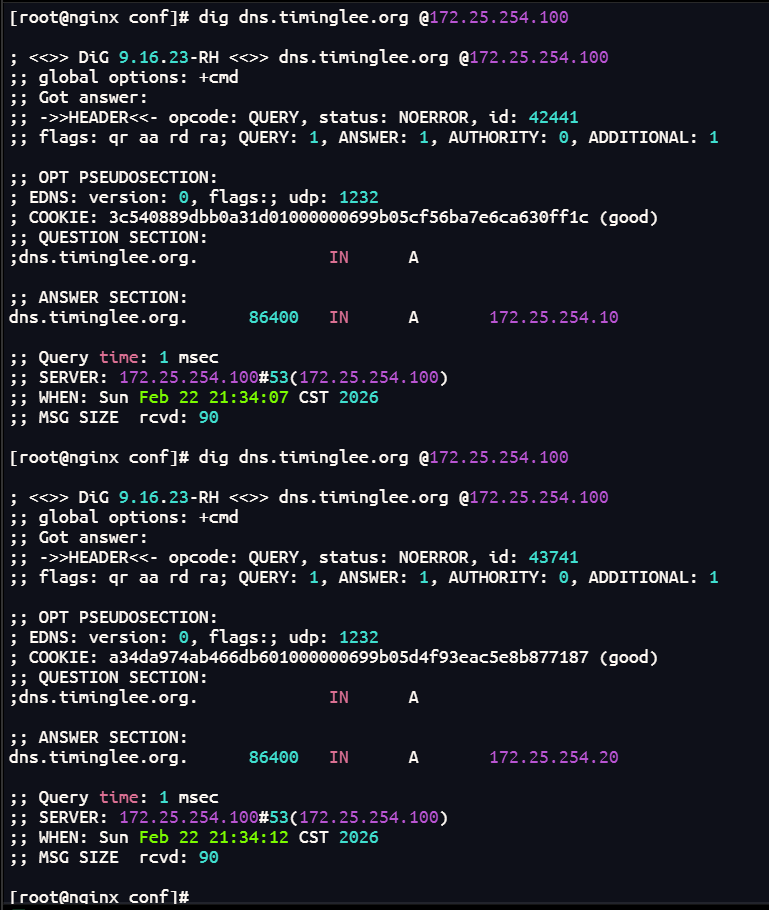
十九.编译安装 openresty
bash
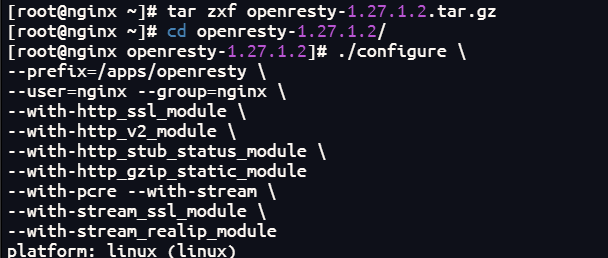
[root@Nginx src]#wget https://openresty.org/download/openresty-1.27.1.2.tar.gz
[root@Nginx ~]#dnf -yq install gcc pcre-devel openssl-devel perl zlib-devel
[root@Nginx ~]#useradd -r -s /sbin/nologin nginx
[root@Nginx ~]#tar zxf openresty-1.27.1.2
[root@webserver ~]# cd openresty-1.27.1.2/
[root@Nginx openresty-1.17.8.2]#./configure \
--prefix=/apps/openresty \
--user=nginx --group=nginx \
--with-http_ssl_module \
--with-http_v2_module \
--with-http_stub_status_module \
--with-http_gzip_static_module
--with-pcre --with-stream \
--with-stream_ssl_module \
--with-stream_realip_module

[root@Nginx openresty-1.17.8.2]#gmake && gmake install

[root@webserver openresty]# vim ~/.bash_profile
export PATH=$PATH:/apps/openresty/bin

source  ~/.bash_profile


[root@Nginx openresty-1.17.8.2]#openresty -v
nginx version: openresty/1.17.8.2

[root@Nginx openresty-1.17.8.2]#openresty

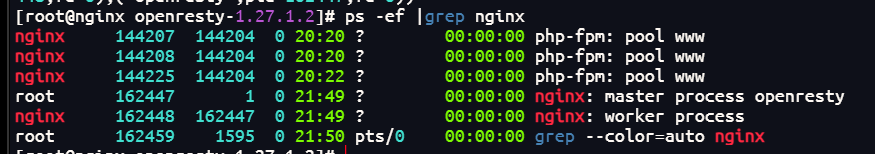
[root@Nginx openresty-1.17.8.2]#ps -ef |grep nginx

[root@webserver openresty]# echo hello test > /usr/local/openresty/nginx/html/index.html
[root@webserver openresty]# curl  172.25.254.200
hello test