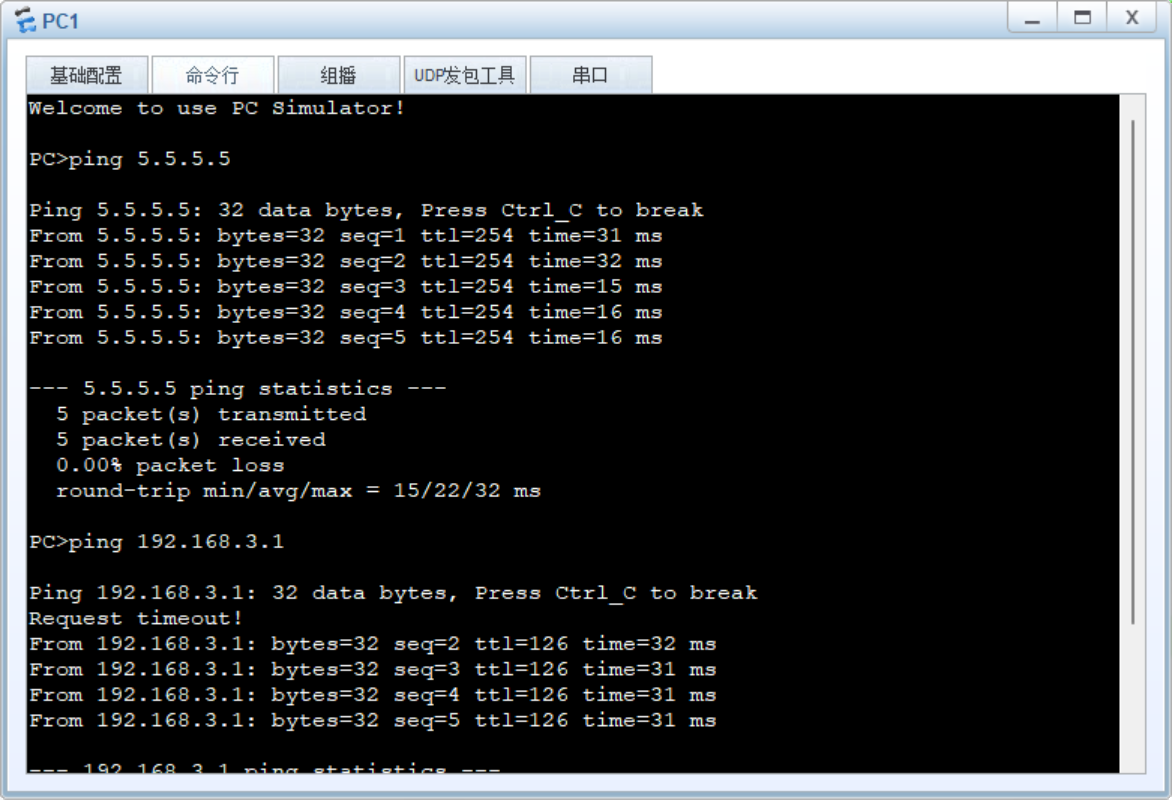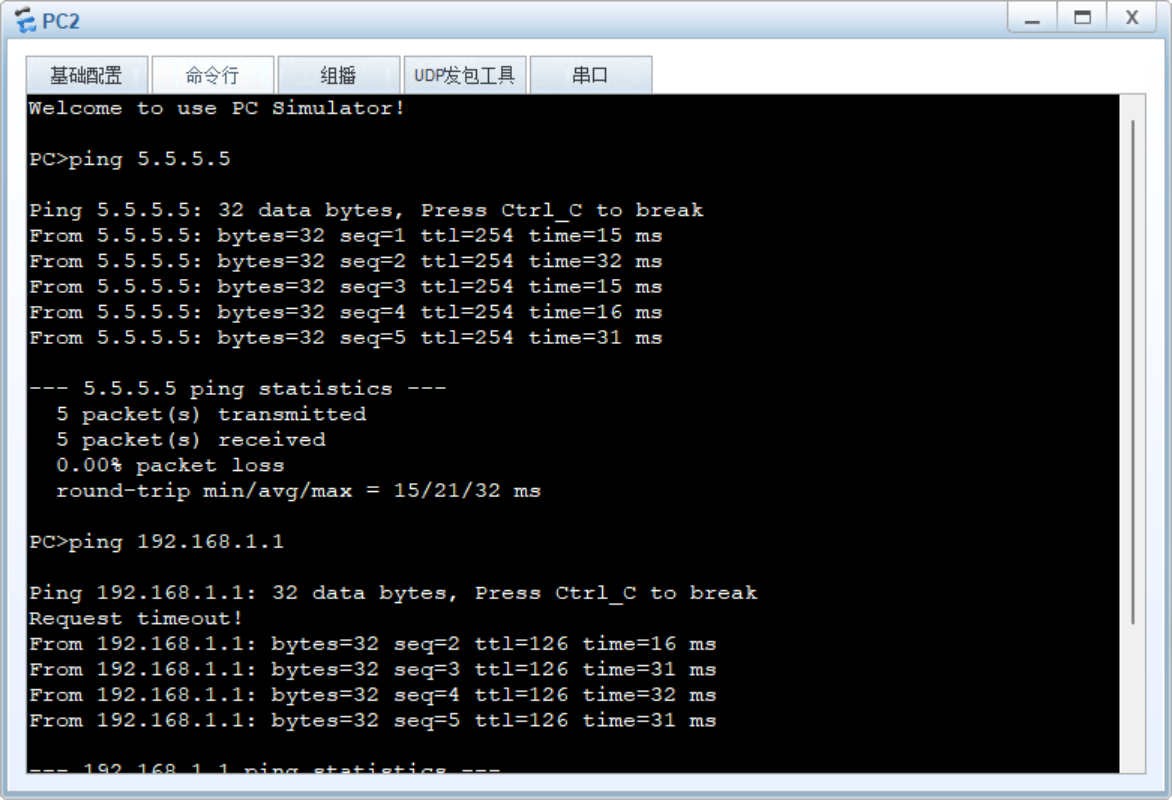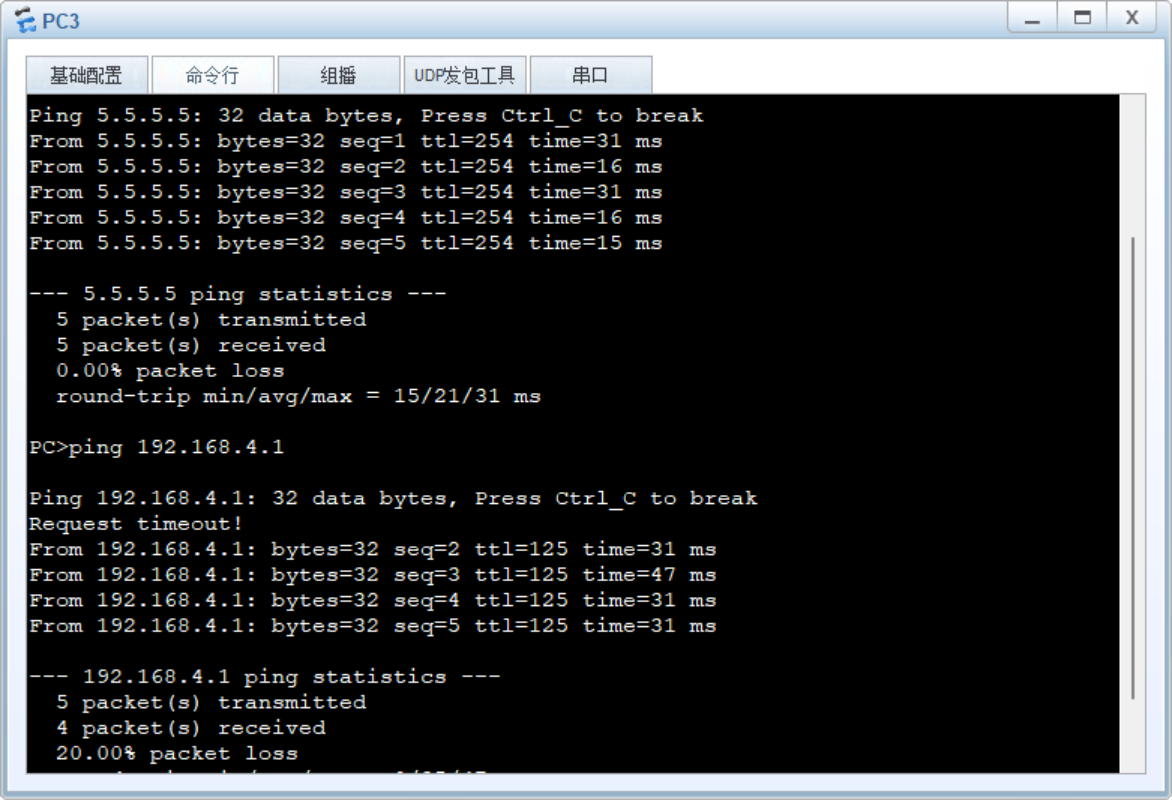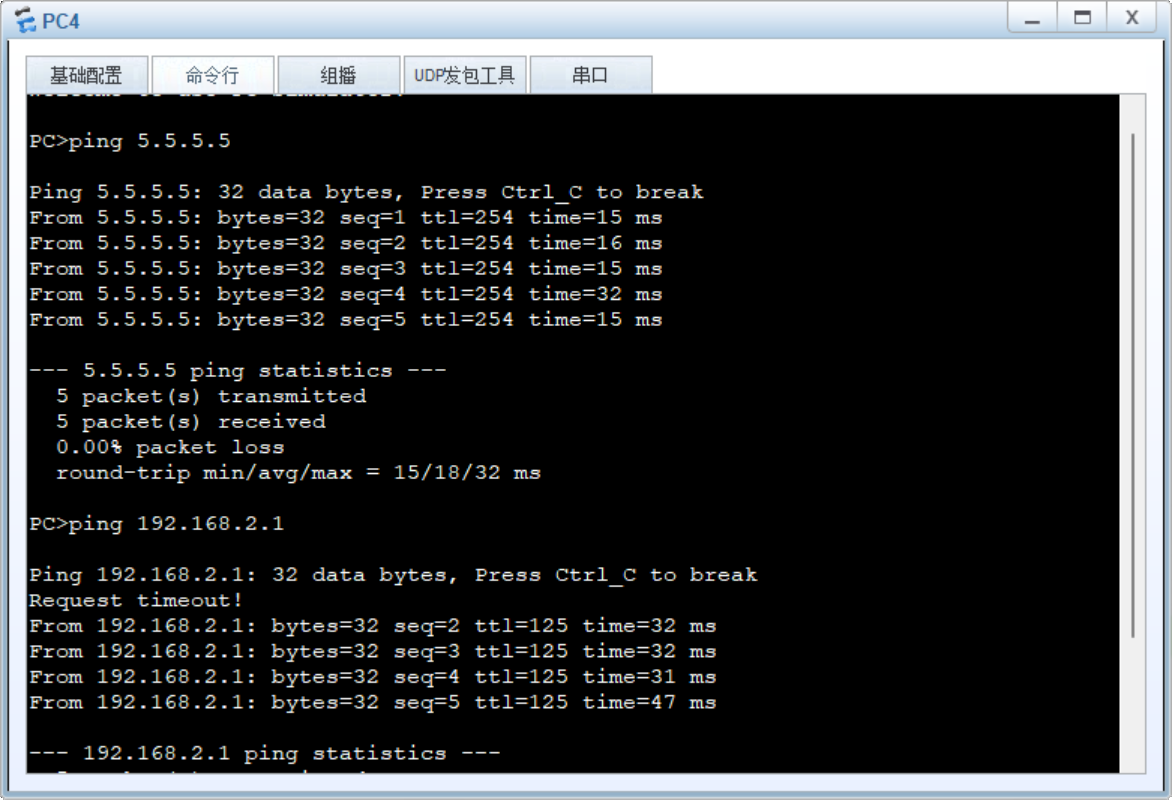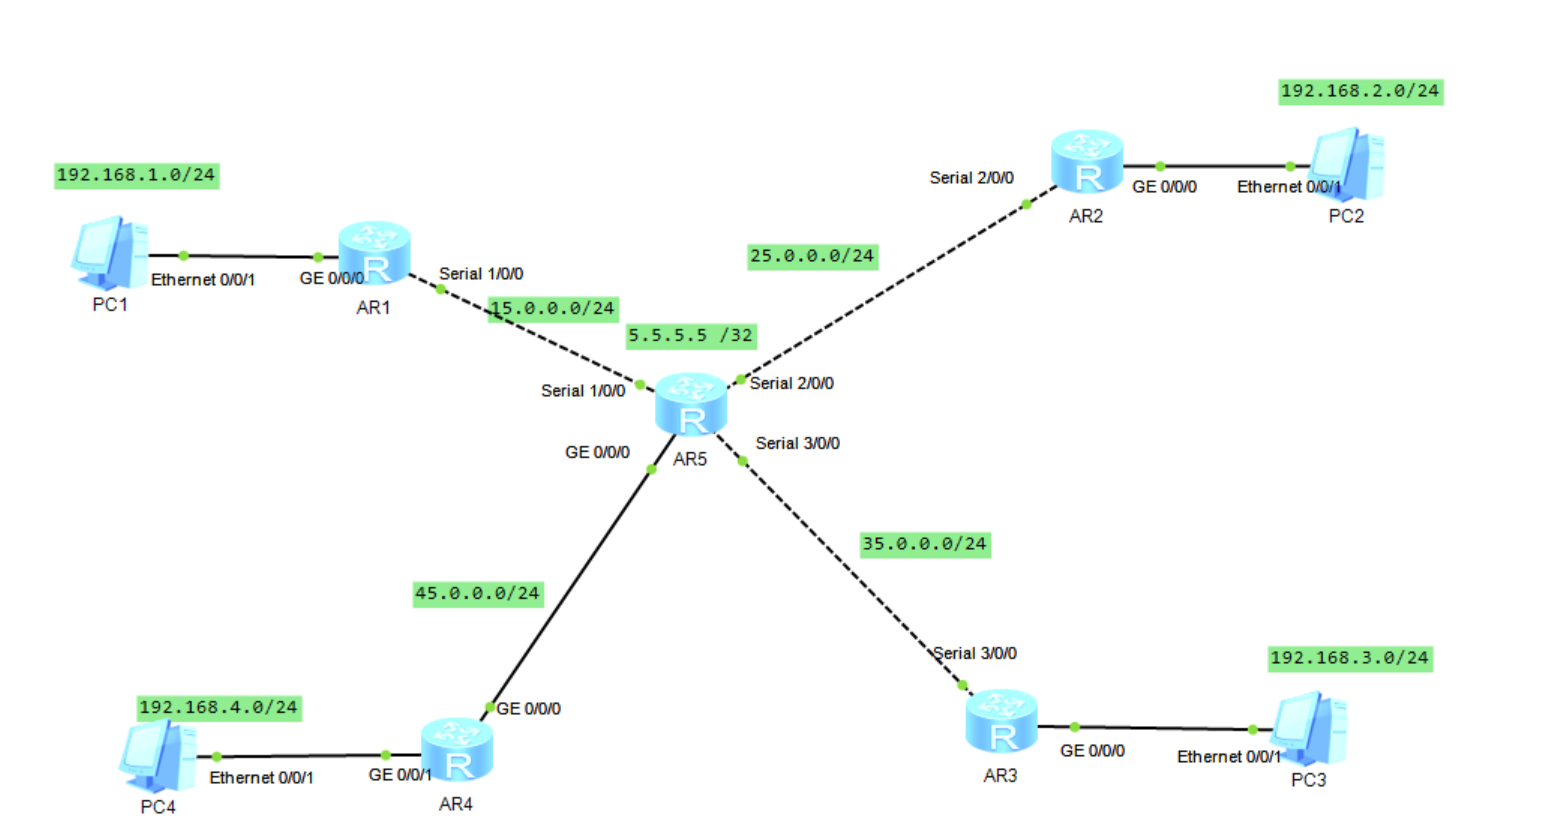
1.R5为ISP,只能进行IP地址配置;其所有的IP地址均为共有IP地址
2.R1和R5之间使用PPP的PAP认证,R5为主认证方
R2和R5之间使用PPP的chap认证,R5为主认证方
R3和R5之间使用HDLC封装
3.R1/R2/R3构建一个MGRE环境,R1为Hub;
R1/R4之间构建一个GRE环境
4.整个私有网络基于RIP全网可达
5.所有PC设置私有IP为源IP,可以访问R5环回
一 、配置IP地址
R1:

[R1]int g 0/0/0

[R1-GigabitEthernet0/0/0]ip address 192.168.1.254 24

[R1]int s 1/0/0

[R1-Serial1/0/0]ip address 15.0.0.1 24


R2:

[R2]int g 0/0/0

[R2-GigabitEthernet0/0/0]ip address 192.168.2.254 24

[R2]int s 2/0/0

[R2-Serial2/0/0]ip address 25.0.0.2 24


R3:

[R3]int g 0/0/0

[R3-GigabitEthernet0/0/0]ip address 192.168.3.254 24

[R3]int s 3/0/0

[R3-Serial3/0/0]ip address 35.0.0.3 24


R4:

[R4]int g 0/0/1

[R4-GigabitEthernet0/0/1]ip address 192.168.4.254 24

[R4]int g 0/0/0

[R4-GigabitEthernet0/0/0]ip address 45.0.0.4 24


R5:

[R5]int s 1/0/0

[R5-Serial1/0/0]ip address 15.0.0.5 24

[R5]int s 2/0/0

[R5-Serial2/0/0]ip address 25.0.0.5 24

[R5]int s 3/0/0

[R5-Serial3/0/0]ip address 35.0.0.5 24

[R5]int g 0/0/0

[R5-GigabitEthernet0/0/0]ip address 45.0.0.5 24

[R5]int LoopBack 0

[R5-LoopBack0]ip address 5.5.5.5 32
二、 配置PAP,CHAP,HDLC封装
(1)R1和R5间使用PPP的PAP认证,R5为主认证方
认证方 R5:

[R5]aaa

[R5-aaa]local-user hcip password cipher 123456

[R5-aaa]local-user hcip service-type ppp

[R5-Serial1/0/0]ppp authentication-mode pap


被认证方 R1:

[R1]int s 1/0/0

[R1-Serial1/0/0]ppp pap local-user hcip password cipher 123456
(2)R2与R5之间使用PPP的CHAP认证,R5为主认证方
认证方R5:

[R5-aaa]

[R5-aaa]local-user huawei password cipher 654321

[R5-aaa]local-user huawei service-type ppp

[R5-Serial2/0/0]ppp authentication-mode chap


被认证方R2:

[R2-Serial2/0/0]ppp chap user huawei
[R2-Serial2/0/0]ppp chap password cipher 654321
(3)R3与R5之间使用HDLC封装
R3:

[R3]int s 3/0/0

[R3-Serial3/0/0]link-protocol hdlc


R5:

[R5]int s 3/0/0

[R5-Serial3/0/0]link-protocol hdlc
三、 配置MGRE,GRE
[R1]ip route-static 0.0.0.0 0 15.0.0.5

[R2]ip route-static 0.0.0.0 0 25.0.0.5

[R3]ip route-static 0.0.0.0 0 35.0.0.5

[R4]ip route-static 0.0.0.0 0 45.0.0.5
(1)R1/R2/R3构建一个MGRE环境,R1为Hub
Hub R1:

[R1]int Tunnel 0/0/0

[R1-Tunnel0/0/0]ip address 192.168.5.1 24

[R1-Tunnel0/0/0]tunnel-protocol gre p2mp

[R1-Tunnel0/0/0]source 15.0.0.1


Spoke R2:

[R2]int Tunnel 0/0/0

[R2-Tunnel0/0/0]ip add 192.168.5.2 24

[R2-Tunnel0/0/0]tunnel-protocol gre p2mp

[R2-Tunnel0/0/0]source Serial 2/0/0

[R2-Tunnel0/0/0]nhrp entry 192.168.5.1 15.0.0.1 register


Spoke R3:

[R3]int Tunnel 0/0/0

[R3-Tunnel0/0/0]ip address 192.168.5.3 24

[R3-Tunnel0/0/0]tunnel-protocol gre p2mp

[R3-Tunnel0/0/0]source Serial 3/0/0

[R3-Tunnel0/0/0]nhrp entry 192.168.5.1 15.0.0.1 register
(2)R1/R4之间构建一个GRE环境
R1:

[R1]int Tunnel 0/0/1

[R1-Tunnel0/0/1]ip address 192.168.6.1 24

[R1-Tunnel0/0/1]tunnel-protocol gre

[R1-Tunnel0/0/1]source 15.0.0.1

[R1-Tunnel0/0/1]destination 45.0.0.4


R4:

[R4]int Tunnel 0/0/1

[R4-Tunnel0/0/1]ip address 192.168.6.4 24

[R4-Tunnel0/0/1]tunnel-protocol gre

[R4-Tunnel0/0/1]source 45.0.0.4

[R4-Tunnel0/0/1]destination 15.0.0.1
四、 配置RIP协议
R1:

rip 1
 version 2
 network 192.168.1.0
 network 192.168.5.0
 network 192.168.6.0

[R1-Tunnel0/0/0]nhrp entry multicast dynamic

[R1-Tunnel0/0/0]undo rip split-horizon

[R1-Tunnel0/0/1]undo rip split-horizon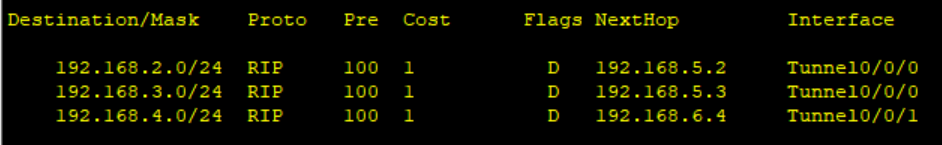
R2:

rip 1
 version 2
 network 192.168.2.0
 network 192.168.5.0

[R2-Tunnel0/0/1]undo rip split-horizon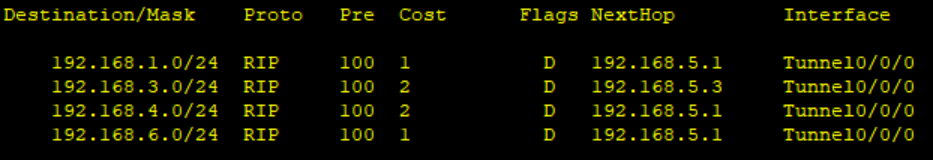
R3:

rip 1
 version 2
 network 192.168.3.0
 network 192.168.5.0

[R3-Tunnel0/0/1]undo rip split-horizon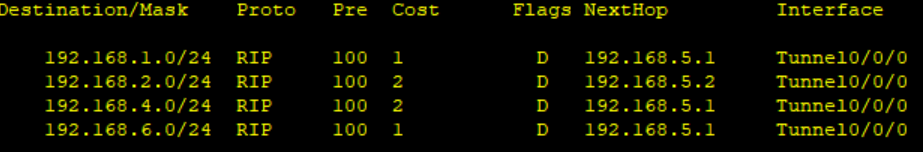
R4:

rip 1
 version 2
 network 192.168.4.0
 network 192.168.6.0

[R4-Tunnel0/0/1]undo rip split-horizon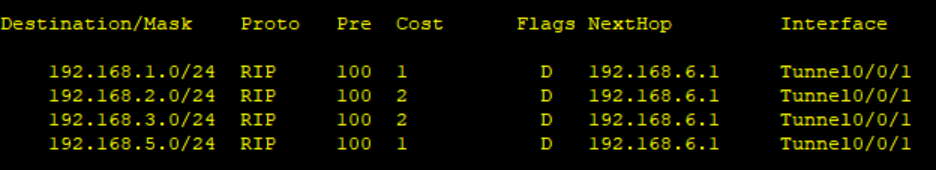
五、 配置NAT
R1:

[R1]acl number 2000

[R1-acl-basic-2000]rule permit source 192.168.1.0 0.0.0.255

[R1]int Serial 1/0/0

[R1-Serial1/0/0]nat outbound 2000


R2:

[R2]acl 2000

[R2-acl-basic-2000]rule permit source 192.168.2.0 0.0.0.255

[R2]int Serial 2/0/0

[R2-Serial2/0/0]nat outbound 2000


R3:

[R3]acl 2000

[R3-acl-basic-2000]rule permit source 192.168.3.0 0.0.0.255

[R3]int Serial 3/0/0

[R3-Serial3/0/0]nat outbound 2000


R4:

[R4]acl 2000

[R4-acl-basic-2000]rule permit source 192.168.4.0 0.0.0.255

[R4]int g 0/0/0

[R4-GigabitEthernet0/0/0]nat outbound 2000