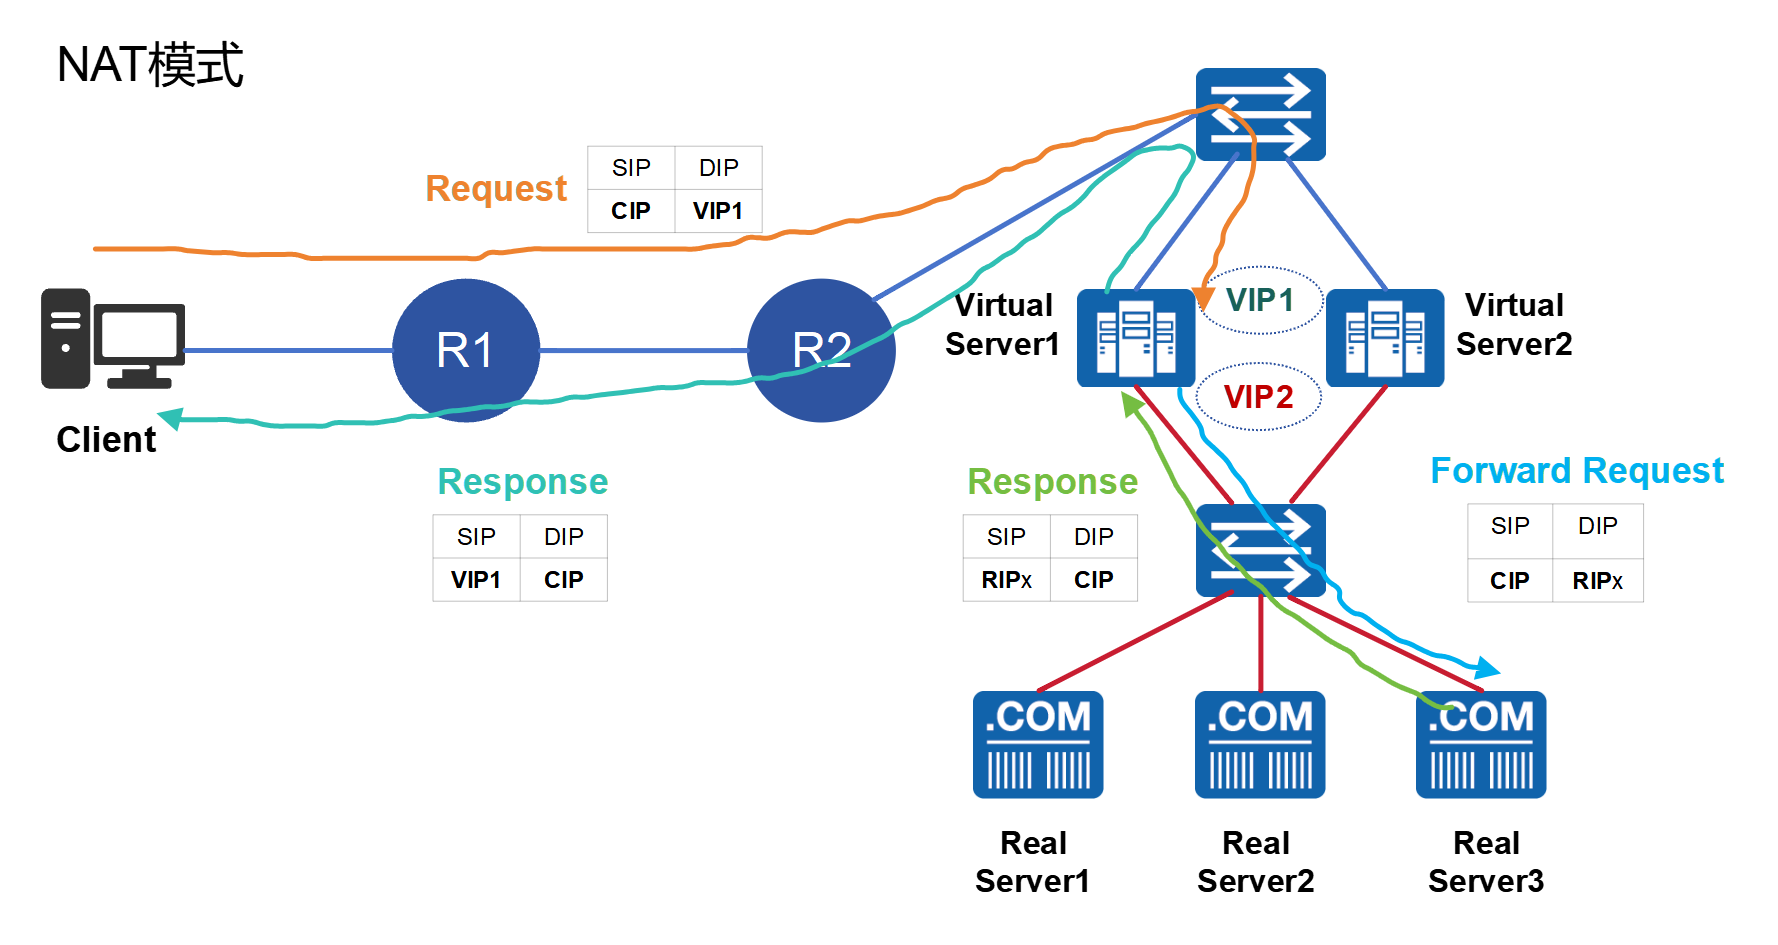
本次实验在之前实验拓扑基础上进行改造
keepalived + LVS DR_172.16.1.21:8000-CSDN博客
一、实验拓扑
二、IP地址规划
|-----------------|------|------------------|--------------|--------------------------------------------|
| | 接口 | IP地址 | 网关 | 虚拟IP |
| Client | - | 192.168.10.20/24 | 192.168.10.1 | |
| Virtual Server1 | 外网 | 123.1.1.101/24 | 123.1.1.1 | VIP1: 123.1.1.100/32 VIP2: 172.16.1.100/32 |
| Virtual Server1 | DIP | 172.16.1.101/24 | - | VIP1: 123.1.1.100/32 VIP2: 172.16.1.100/32 |
| Virtual Server2 | 外网 | 123.1.1.102/24 | 123.1.1.1 | VIP1: 123.1.1.100/32 VIP2: 172.16.1.100/32 |
| Virtual Server2 | DIP | 172.16.1.102/24 | - | VIP1: 123.1.1.100/32 VIP2: 172.16.1.100/32 |
| Real Server1 | RIP1 | 172.16.1.201/24 | 172.16.1.100 | |
| Real Server2 | RIP2 | 172.16.1.202/24 | 172.16.1.100 | |
| Real Server3 | RIP3 | 172.16.1.203/24 | 172.16.1.100 | |
三、关键点
virtual server上要配置两个虚拟IP,一个VIP1用户客户端的业务访问,另一个VIP2用于做real server的虚拟网关。
要做两个网卡间的联动,否则单个网卡故障后,此网卡绑定的虚拟IP切换到另一台机器上,但另一个网卡绑定的虚拟地址仍留在原来的机器上,导致通讯故障。
3.1 virtual server1和virtual server2
开启路转发
root@localhost \~# echo 'net.ipv4.ip_forward = 1' >> /etc/sysctl.conf
root@localhost \~# sysctl -p
3.1.1 keepalived配置文件
virtual server1
root@localhost \~# cat /etc/keepalived/keepalived.conf
! Configuration File for keepalived
global_defs {
notification_email {
acassen@firewall.loc
failover@firewall.loc
sysadmin@firewall.loc
}
notification_email_from Alexandre.Cassen@firewall.loc
smtp_server 192.168.200.1
smtp_connect_timeout 30
router_id LVS_Master
vrrp_skip_check_adv_addr
! vrrp_strict
vrrp_garp_interval 0
vrrp_gna_interval 0
}
vrrp_instance VI_1 {
state MASTER
interface ens160
interface ens192
virtual_router_id 111
priority 150
advert_int 1
authentication {
auth_type PASS
auth_pass 3690
}
virtual_ipaddress {
123.1.1.100 dev ens160
172.16.1.100 dev ens192
}
track_interface {
ens160
ens192
}
}
virtual_server 123.1.1.100 80 {
delay_loop 6
lb_algo rr
lb_kind NAT
persistence_timeout 0
protocol TCP
real_server 172.16.1.201 80 {
weight 1
HTTP_GET {
url {
path /index.html
status_code 200
}
connect_timeout 1
retry 3
delay_before_retry 1
}
}
real_server 172.16.1.202 80 {
weight 1
HTTP_GET {
url {
path /index.html
status_code 200
}
connect_timeout 1
retry 3
delay_before_retry 1
}
}
real_server 172.16.1.203 80 {
weight 1
HTTP_GET {
url {
path /index.html
status_code 200
}
connect_timeout 1
retry 3
delay_before_retry 1
}
}
}
virtual server2
root@localhost \~# cat /etc/keepalived/keepalived.conf
! Configuration File for keepalived
global_defs {
notification_email {
acassen@firewall.loc
failover@firewall.loc
sysadmin@firewall.loc
}
notification_email_from Alexandre.Cassen@firewall.loc
smtp_server 192.168.200.1
smtp_connect_timeout 30
router_id LVS_Backup
vrrp_skip_check_adv_addr
! vrrp_strict
vrrp_garp_interval 0
vrrp_gna_interval 0
}
vrrp_instance VI_1 {
state BACKUP
interface ens160
interface ens192
virtual_router_id 111
priority 100
advert_int 1
authentication {
auth_type PASS
auth_pass 3690
}
virtual_ipaddress {
123.1.1.100 dev ens160
172.16.1.100 dev ens192
}
track_interface {
ens160
ens192
}
}
virtual_server 123.1.1.100 80 {
delay_loop 6
lb_algo rr
lb_kind NAT
persistence_timeout 0
protocol TCP
real_server 172.16.1.201 80 {
weight 1
HTTP_GET {
url {
path /index.html
status_code 200
}
connect_timeout 1
retry 3
delay_before_retry 1
}
}
real_server 172.16.1.202 80 {
weight 1
HTTP_GET {
url {
path /index.html
status_code 200
}
connect_timeout 1
retry 3
delay_before_retry 1
}
}
real_server 172.16.1.203 80 {
weight 1
HTTP_GET {
url {
path /index.html
status_code 200
}
connect_timeout 1
retry 3
delay_before_retry 1
}
}
}
3.2其余配置略
如启动keepalived服务、nginx页面准备等。
四、效果验证
正常情况下访问自动轮询
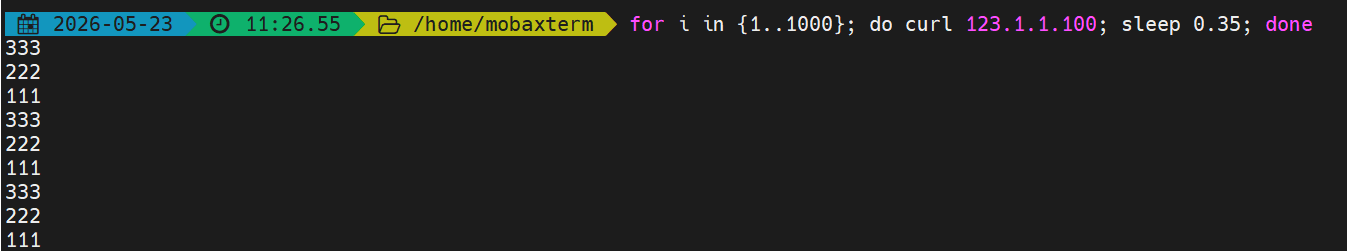
断开master上的任意关联网卡,两个虚拟IP均转至服务器2上,服务仍正常
恢复master上的网卡,两个虚拟IP均转至服务器1上,服务仍正常
另外,配置了健康检查,real server故障后,超时后会自动踢除故障服务器继续提供服务