一.网站需求:
1.基于域名www.openlab.com可以访问网站内容为 welcome to openlab!!!
#关闭防火墙 SElinux
systemctl stop firewalld

setenforce 0
#安装服务
dnf install -y nginx

vim /etc/nginx/conf.d/test_name.conf
#添加
server{
        listen 192.168.190.131:80;
        root /www/openlab;
        server_name www.openlab.com;
        location / {

        }
}

#添加配置文件
vim /etc/hosts

192.168.190.131    www.openlab.com
#创建目录
mkdir -p /www/openlab
#写入内容
echo 'welcome openlab!!!' > /www/openlab/index.htm
#重启服务
systemctl restart nginx.service

#验证服务
curl www.openlab.com
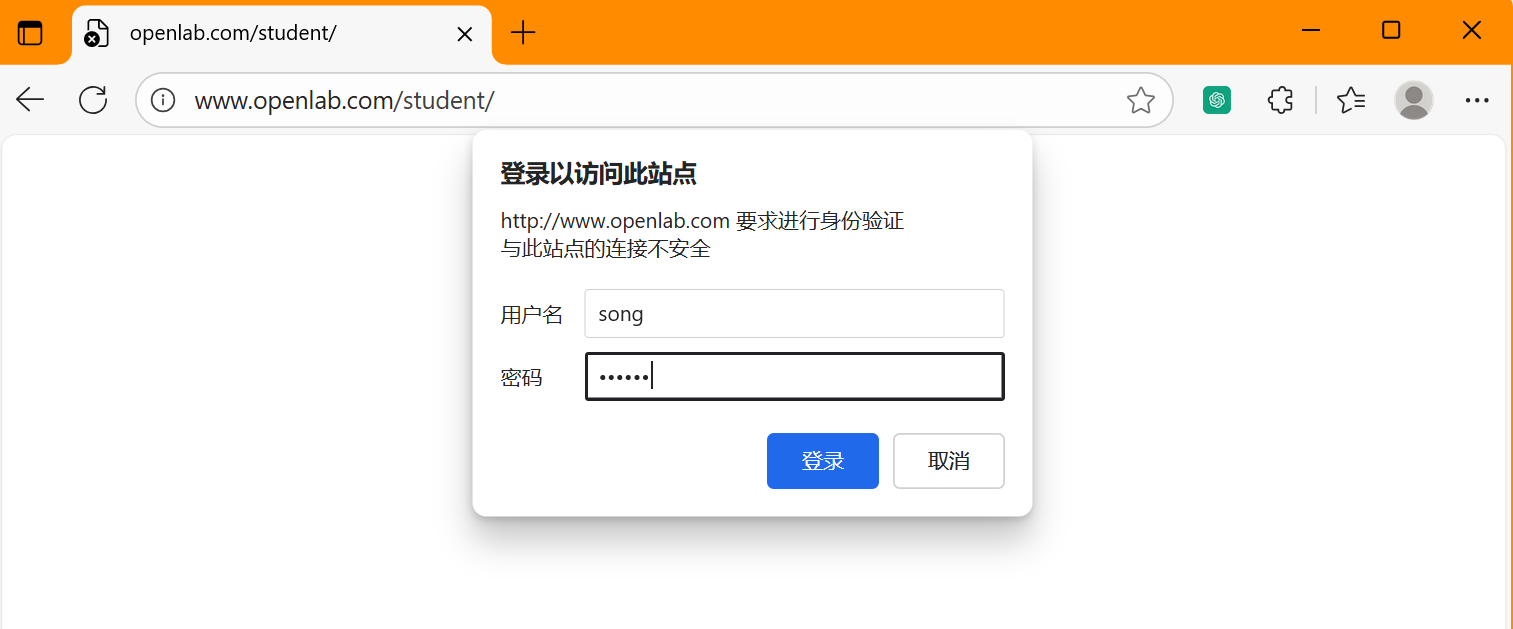
2.给该公司创建三个子界面分别显示学生信息,教学资料和缴费网站,基于www.openlab.com/student 网站访问学生信息,www.openlab.com/data网站访问教学资料
vim /etc/nginx/conf.d/test_alias.conf

server{
        listen 192.168.190.131:80;
        root /www/openlab;
        server_name www.openlab.com;
        location /student{
                alias /www/openlab/student/;
                auth_basic on;
                auth_basic_user_file /etc/nginx/users;
        }
        location /date{
                alias /www/openlab/date/;
        }
        location /money{
                alias /www/openlab/money/;
        }
}
#创建目录写入内容
[root@localhost ~]# mkdir /www/openlab/student
[root@localhost ~]# echo student > /www/openlab/student/index.html
[root@localhost ~]# mkdir /www/openlab/date
[root@localhost ~]# echo date > /www/openlab/date/index.html
[root@localhost ~]# mkdir /www/openlab/money
[root@localhost ~]# echo money > /www/openlab/money/index.html
#重启服务
systemctl restart nginx.service

#验证
curl http://www.openlab.com/date/
3.要求
(1)访问该网站http请求都通过https响应。
(2)学生信息网站只有song和tian两人可以访问,其他用户不能访问
[root@localhost ~]# htpasswd -c /etc/nginx/users song
New password:
Re-type new password:
Adding password for user song
[root@localhost ~]# htpasswd /etc/nginx/users tian
New password:
Re-type new password:
Adding password for user tian

#添加配置文件
vim /etc/nginx/conf.d/test_httpd.conf

server{
        listen 192.168.190.131:443 ssl;
        root /www/openlab/money/;
        ssl_certificate /etc/pki/tls/certs/openlab.crt;
        ssl_certificate_key /etc/pki/tls/private/openlab.key;
        location /{
                index index.html;
        }
}

#证书
[root@localhost ~]# openssl req -utf8 -new -key /etc/pki/tls/private/openlab.key -x509 -days 365 -out /etc/pki/tls/certs/openlab.crt

You are about to be asked to enter information that will be incorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Name or a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [XX]:86
State or Province Name (full name) []:jiangsu
Locality Name (eg, city) [Default City]:nanjin
Organization Name (eg, company) [Default Company Ltd]:rhce
Organizational Unit Name (eg, section) []:server
Common Name (eg, your name or your server's hostname) []:server
Email Address []:andy@qq.com

#重启服务
systemctl restart nginx.service

#验证
curl https://www.openlab.com -k